
gtfobins-cli
 t0thkr1s/gtfobins-cli
Search for Unix binaries that can be exploited to bypass system security restrictions.
binary-exploitationinformation-gatheringpenetration-testing+2
145
t0thkr1s/gtfobins-cliSearch for Unix binaries that can be exploited to bypass system security restrictions.

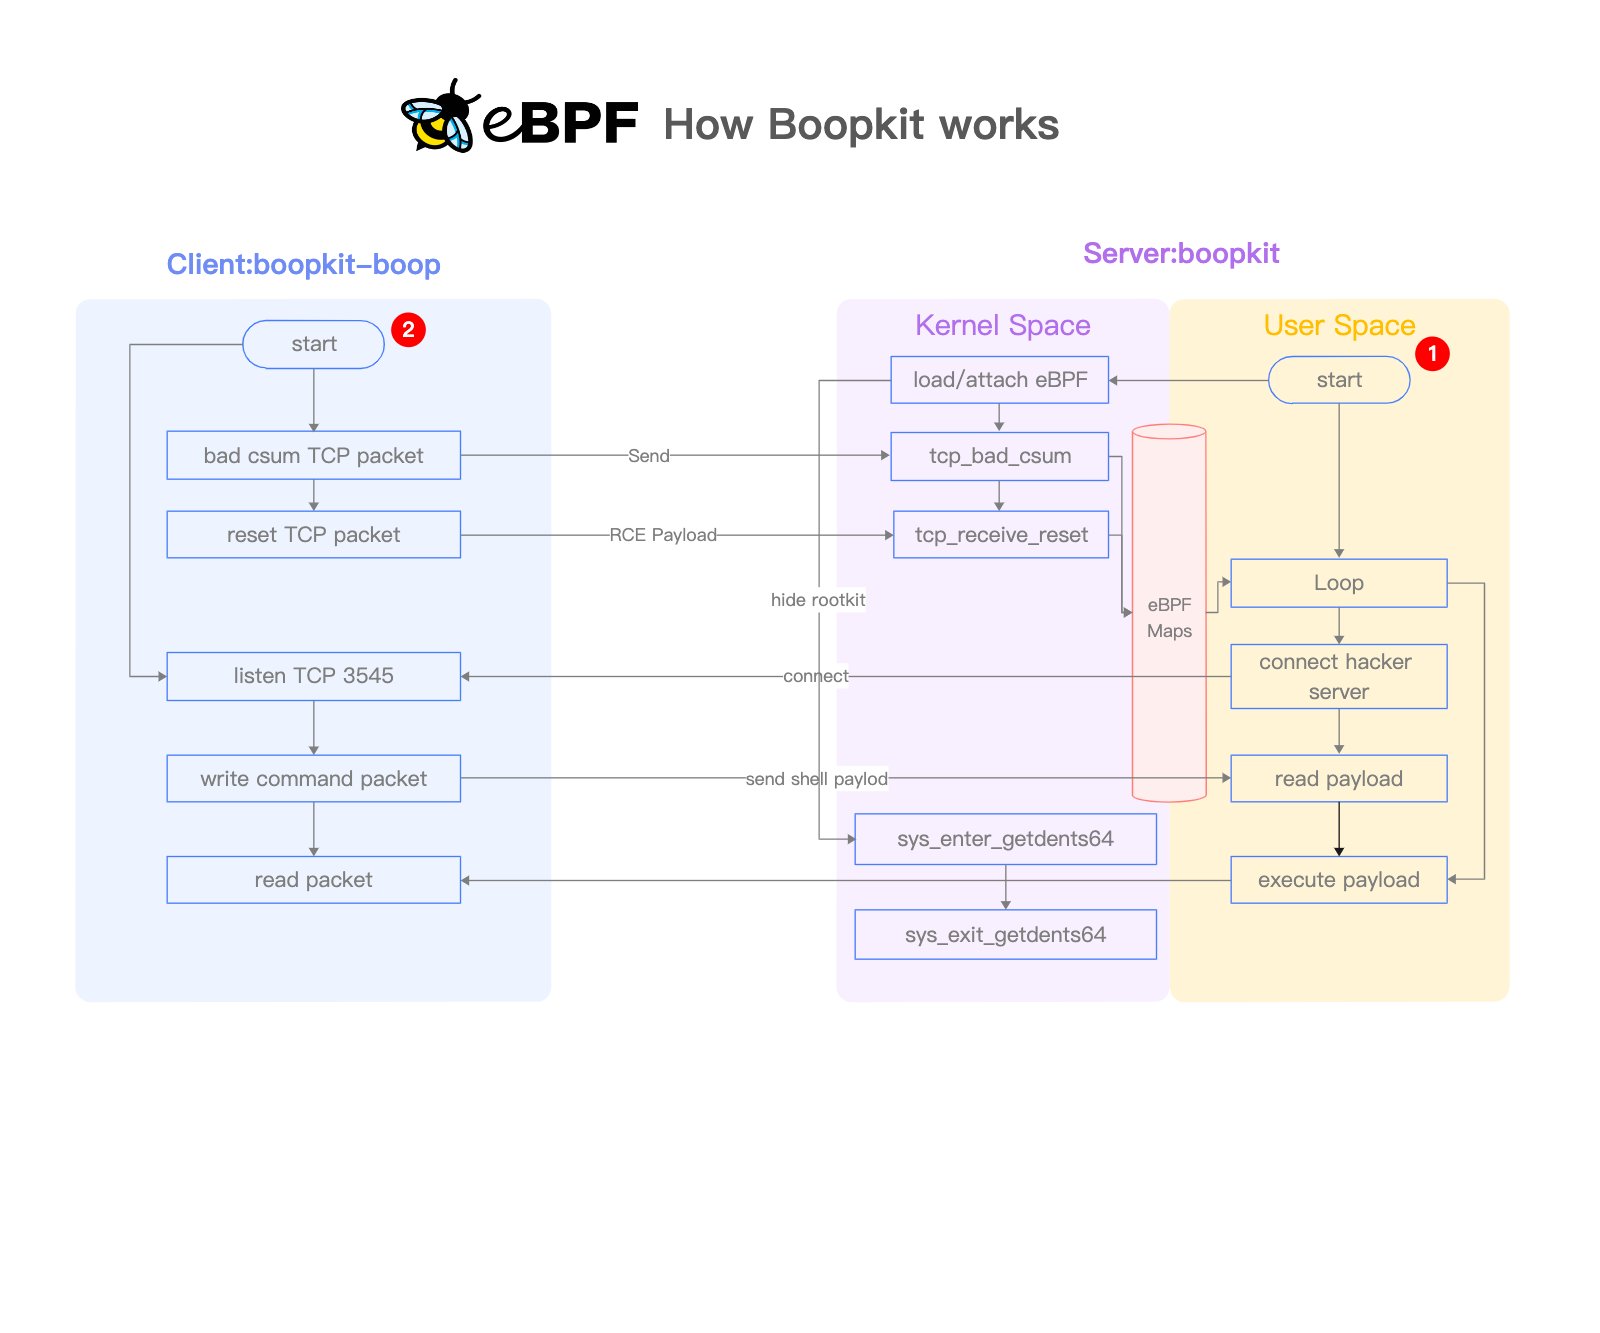 krisnova/boopkit
Linux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.
 netero1010/edrsilencer
A tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.
 m00nrise/processhider
Post-exploitation tool for hiding processes from monitoring applications
 nccgroup/socksoverrdp
Socks5/4/4a Proxy support for Remote Desktop Protocol / Terminal Services / Citrix / XenApp / XenDesktop
 beetlechunks/redsails
RedSails is a Python based post-exploitation project aimed at bypassing host based security monitoring and logging. DerbyCon 2017 Talk:…
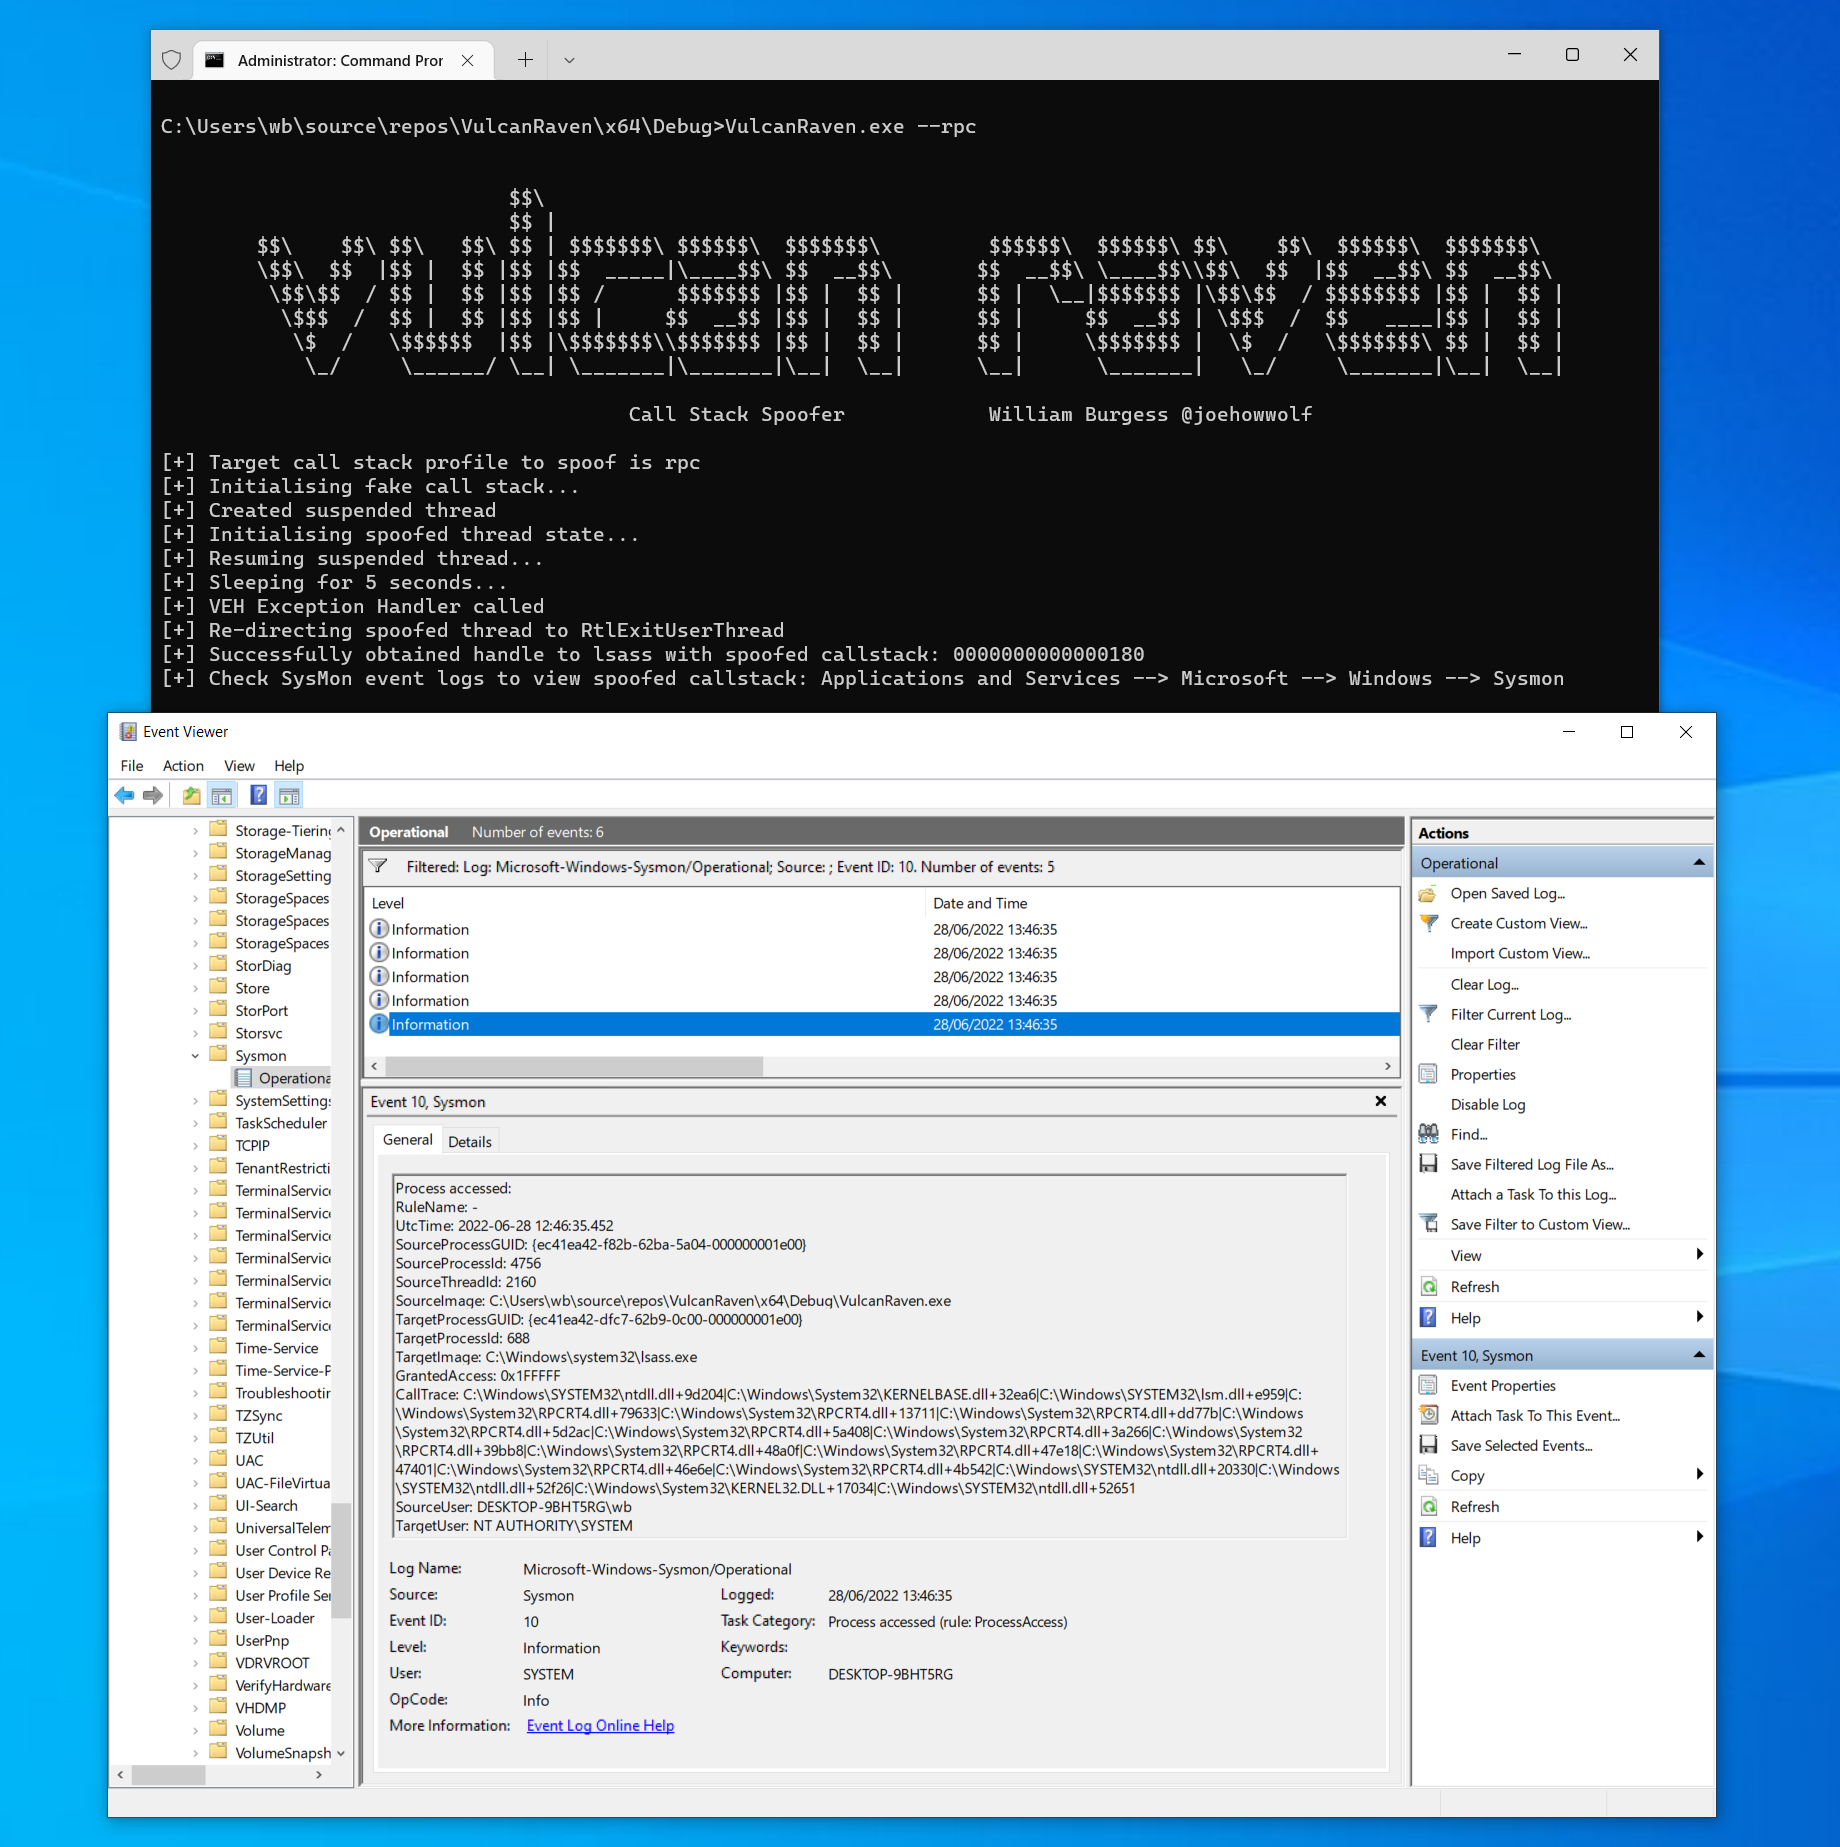 withsecurelabs/callstackspoofer
A PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)
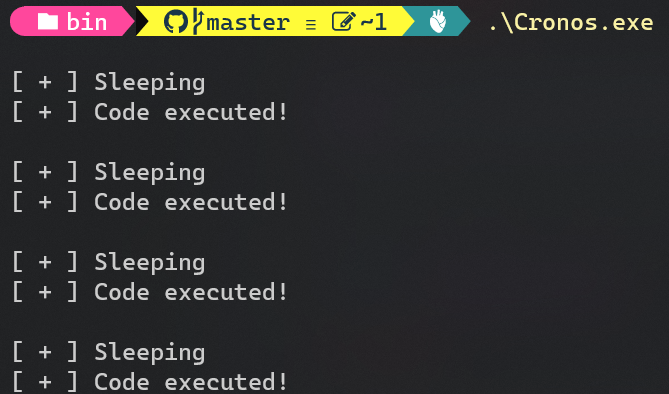 idov31/cronos
PoC for a sleep obfuscation technique leveraging waitable timers to evade memory scanners.
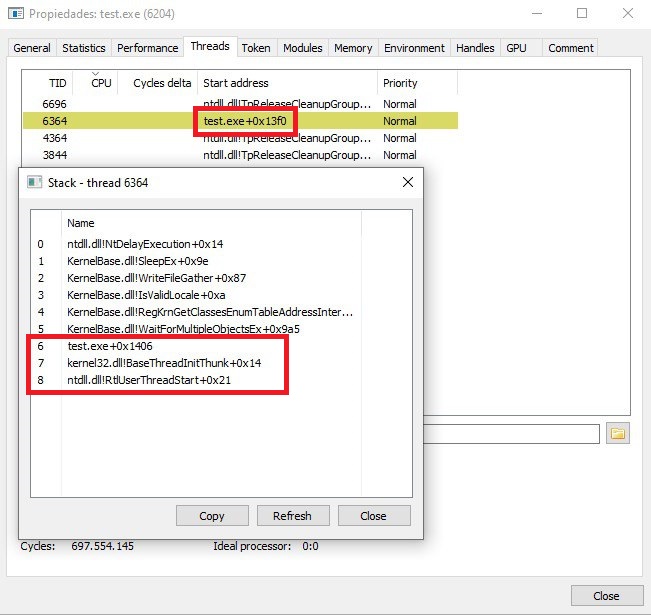 kudaes/unwinder
Call stack spoofing for Rust
 rasta-mouse/crystal-loaders
A small collection of Crystal Palace PIC loaders designed for use with Cobalt Strike
 janoglezcampos/rust_syscalls
Single stub direct and indirect syscalling with runtime SSN resolving for windows.
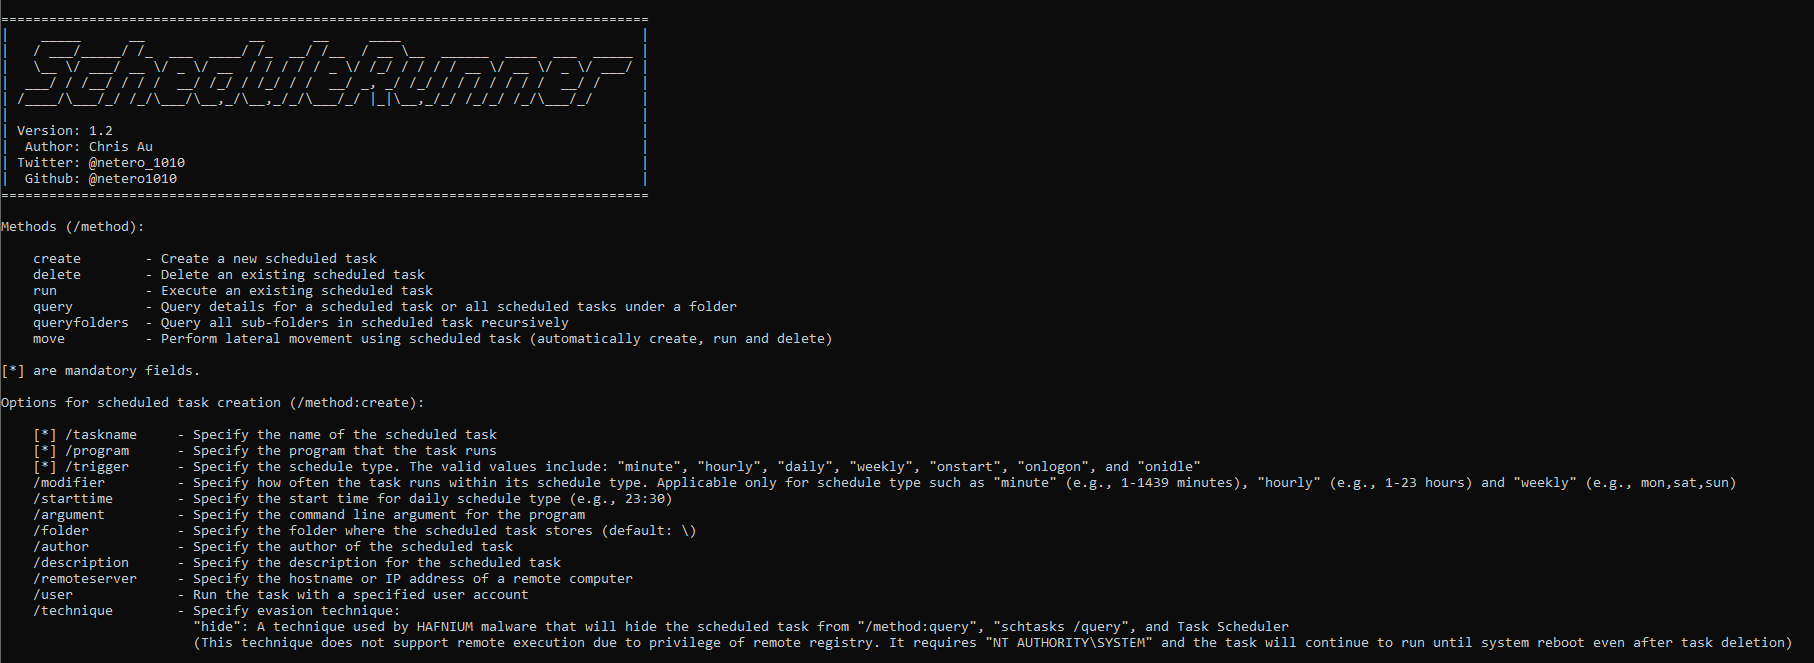 netero1010/schedulerunner
A C# tool with more flexibility to customize scheduled task for both persistence and lateral movement in red team operation
 lloydlabs/ntqueueapcthreadex-ntdll-gadget-injection
This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
 faisal-p27/wareed-dns-c2
DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
 secforce/sharpwhispers
C# porting of SysWhispers2. It uses SharpASM to find the code caves for executing the system call stub.
 rasta-mouse/libtp
Crystal Palace library for proxying Nt API calls via the Threadpool
 waawaa/breakcyserver
Red-team EDR evasion utility that terminates security services by abusing Process Explorer driver functionality to bypass PPL and ObRegisterCallbacks.