

NetExec
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
command-and-controldatabase-securityexploitation+14
5.9k
pennyw0rth/netexecPost-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 bishopfox/sliver
Adversary Emulation Framework
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
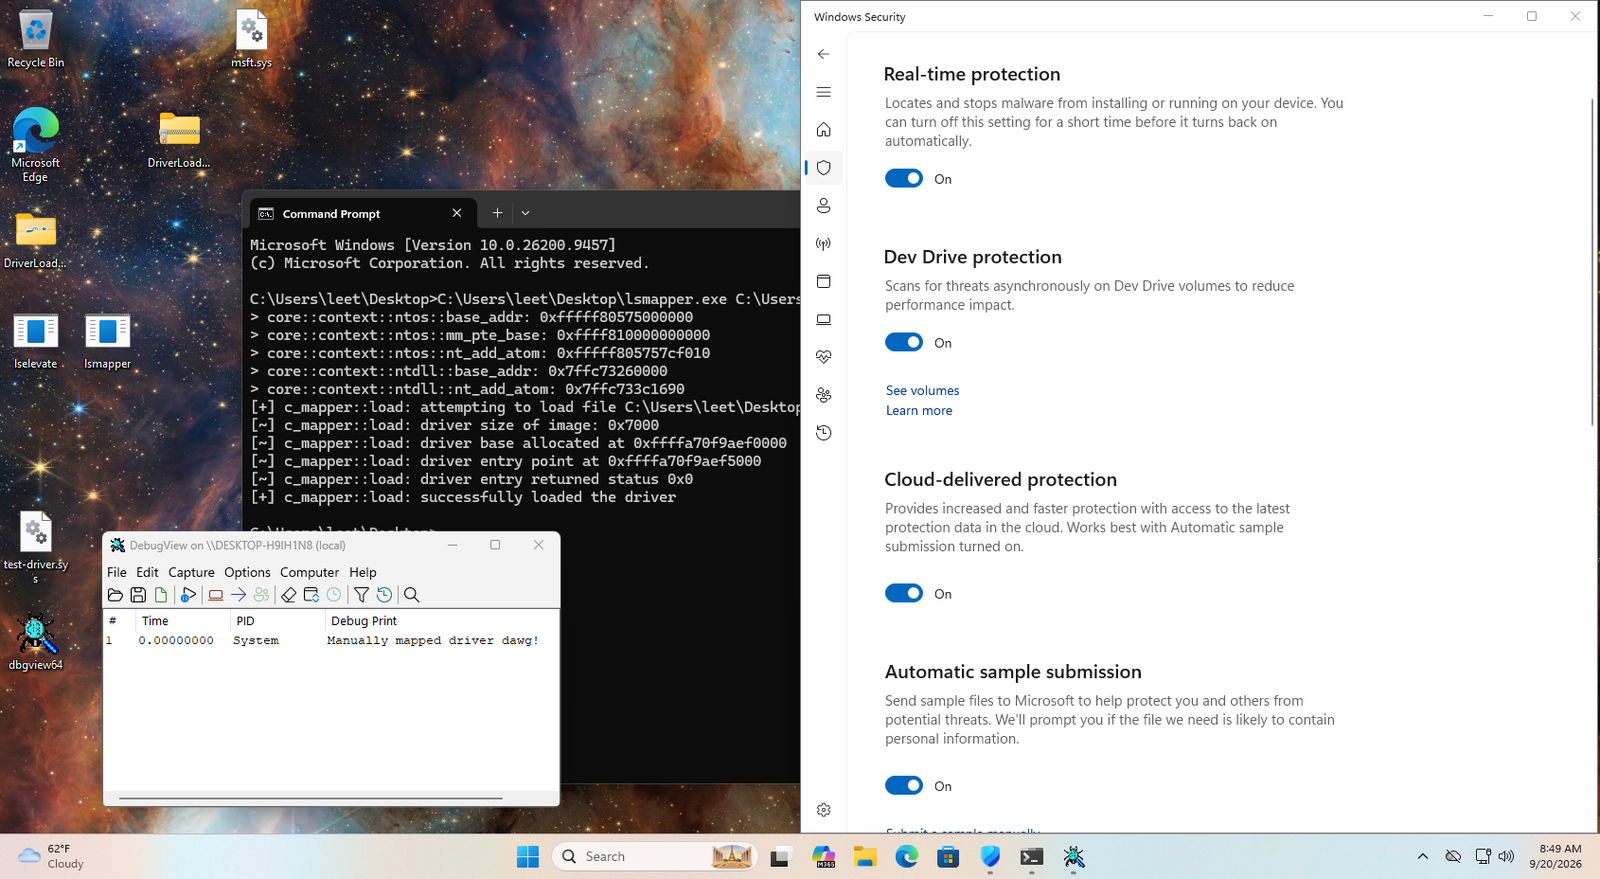 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
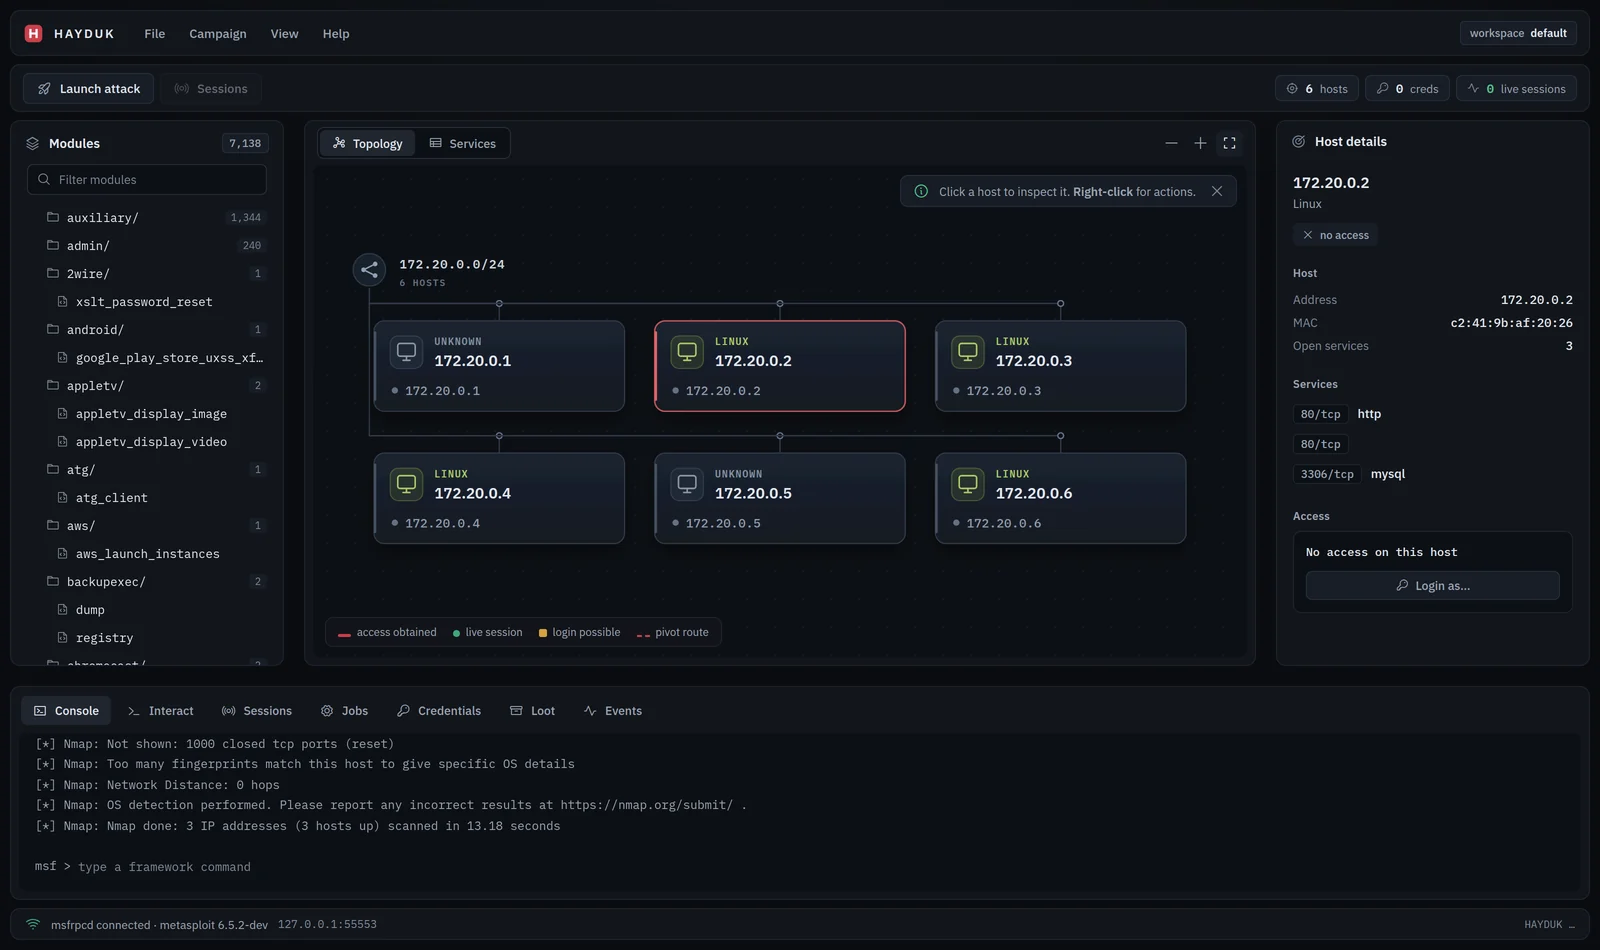 jolovicdev/hayduk
Graphical attack management console for Metasploit: the lineage of Armitage as a single Go binary with a browser UI. Live network topology, campaign…
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 attackercan/wp2shell-poc2
CVE-2026-63030
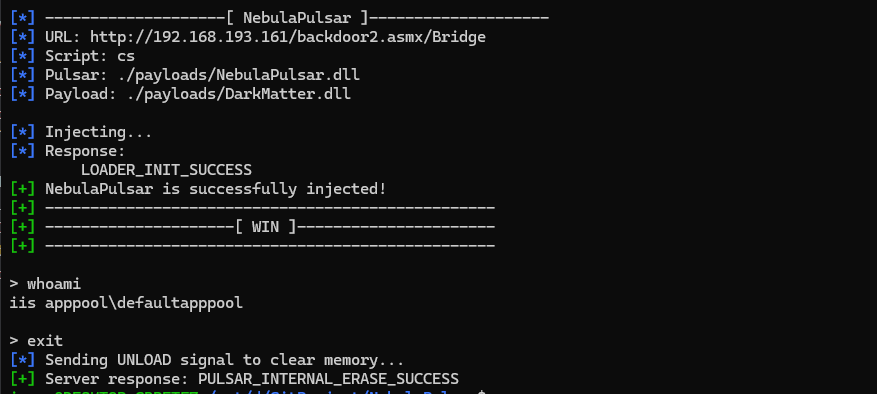 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 alexlinov/miniplasma-runner
CVE-2020-17103 adapted for C2 with split-binary SYSTEM callback
 danimrtzp/cve-2026-31431-revshell
Weaponized Python exploit for CVE-2026-31431, chaining Linux kernel privilege escalation to a daemonized root reverse shell with full PTY, patching…
 malwarekid/cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel AF_ALG memory corruption vulnerability. Uses splice to patch /usr/bin/su in page cache,…
 xm0kht4r/phoenix-framework
Post-exploitation framework that abuses trusted sites like Telegram and Discord for C2.
 devianntsec/cve-2025-55182
Master's thesis research on CVE-2025-55182 (React2Shell). Modular exploitation framework with 6 attack scenarios (RCE, exfiltration, defacement),…
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 sobri3195/-pegasus-suite
A comprehensive security toolkit with 1000+ penetration testing and security assessment tools.
 reverseclabs/c3
Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…