

CVE-2026-77647
 nxploited/cve-2026-77647
SPIP before 4.4.20 allows unauthenticated remote attackers to execute arbitrary code
exploitationpayload-generationpenetration-testing+5
nxploited/cve-2026-77647SPIP before 4.4.20 allows unauthenticated remote attackers to execute arbitrary code
 baguette168/nmg
Generates parameterized .NET memory-shell payloads (VPP, MVC route, HttpListener) compatible with Godzilla, Behinder, and AntSword clients for red…
 fl0ydsec/cve-2026-15989
Mass scanner and exploit for CVE-2026-15989, the unauthenticated privilege escalation in Super Forms <= 6.3.316 that creates administrator accounts…
 winrarzipsexploit/cve-2026-87930
Joomla multi-CVE RCE suite with seven exploit modules for Balbooa Forms, Page Builder CK, SP Page Builder, JCE, iCagenda, Helix3, and SP LMS, plus…
 mrdebora/cups-2.4.16-lpe
CUPS 2.4.16 Local Privilege Escalation via Local Admin Token Leak and file:// Arbitrary File Write (CVE-2026-34990)
 hackspeak/cve-2026-17566
pgAdmin 4 Import/Export RCE (CVE-2026-17566) PoC - TO PROGRAM injection via backslash-escape mismatch
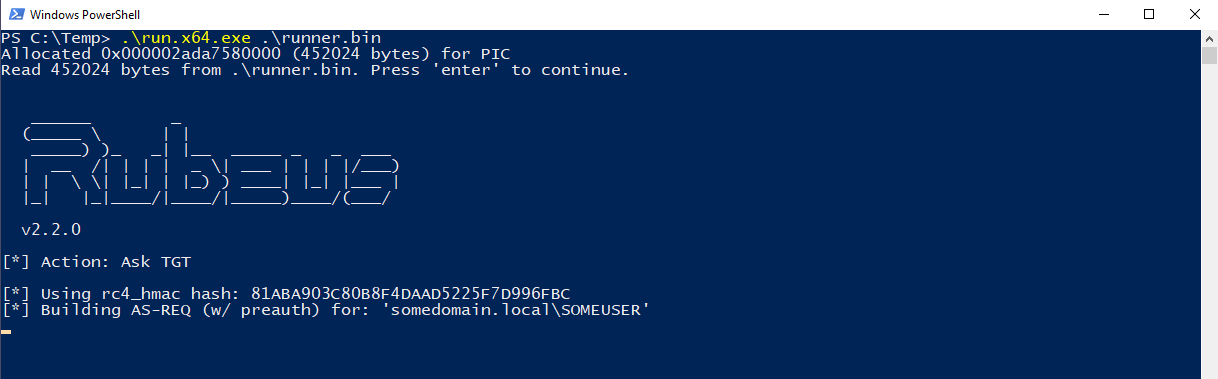 ofasgard/execute-assembly-pico
A PICO for Crystal Palace that implements CLR hosting to execute a .NET assembly in memory.
 gbuyssens/cve-2026-39987
Marimo exploit prior to 0.23.0. Pre-Auth RCE vulnerability via websocket endpoint : /terminal/ws.
 prodigiousmind/revshell
Pentestmonkeys' PHP reverse shell with dynamic host and port passing through GET request parameters
 horizon3ai/vrealizeloginsightrce
POC for RCE using vulnerabilities described in VMSA-2023-0001
 h3x0v3rl0rd/nodejsshell
Node.js reverse shell payload generator for penetration testing. Creates bind and reverse shells in JavaScript.
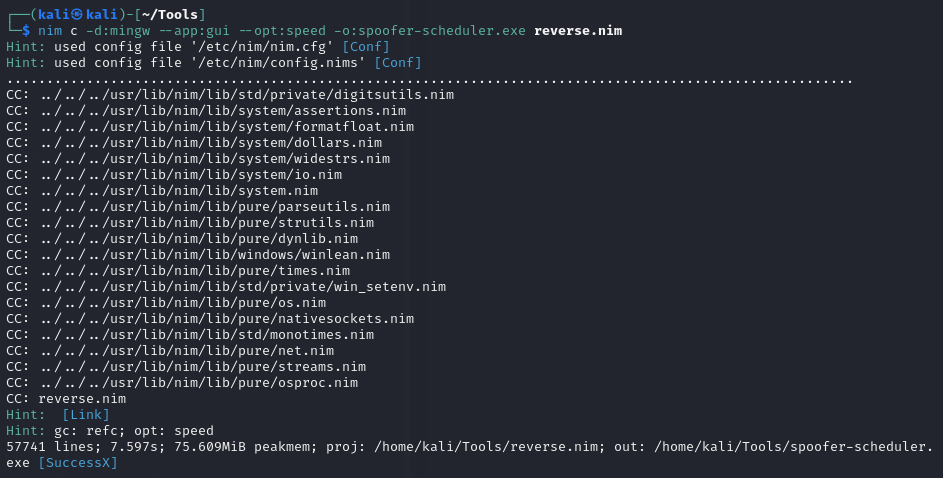 h3x0v3rl0rd/nim-reverse-shell
nim-reverse-shell
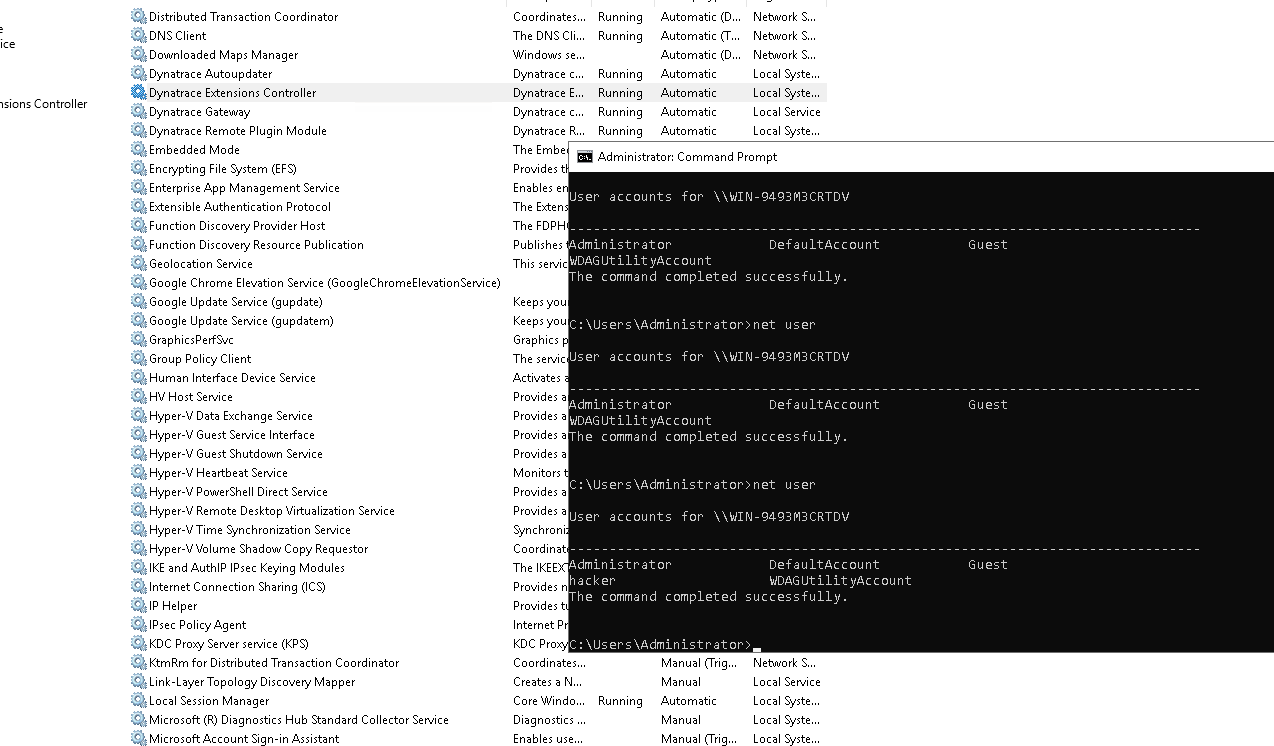 pentastic-be/cve-2025-61304
OS command injection vulnerability in Dynatrace ActiveGate ping extension up to 1.016 via crafted ip address
 blackarch/webshells
Various webshells. We accept pull requests for additions to this collection.
 lennertdefauw/cve-2025-8088
WinRAR < 7.13 path traversal for persistency
 t3l3machus/hoaxshell
A Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.
 tuhinshubhra/shellstack
A PHP Based Tool That Helps You To Manage All Your Backdoored Websites Efficiently.
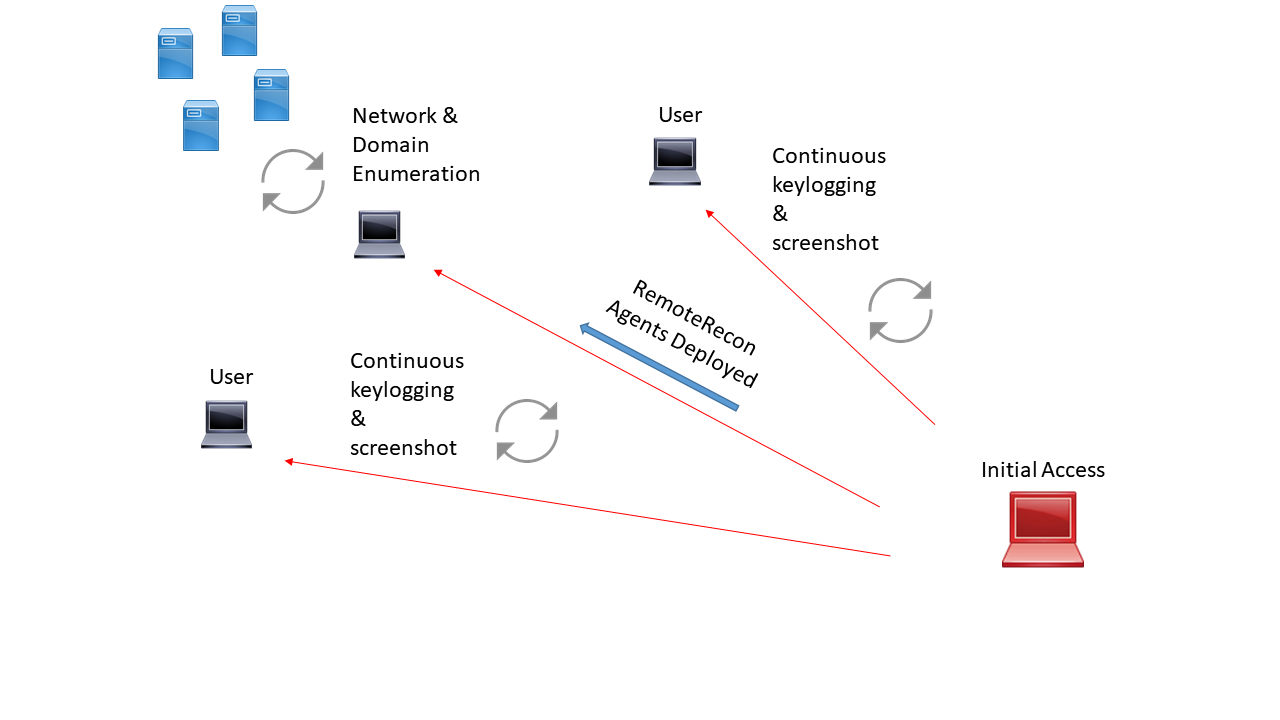 xorrior/remoterecon
Remote Recon and Collection