
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
RemoteRecon — Remote Recon and Collection | Kitploit
Tools/GitHubGitHub/xorrior/remoterecon
Payload GenerationPost-ExploitationPenetration TestingRed TeamingRemote Access Tool
GitHubxorrior/remoterecon

RemoteRecon

Remote Recon and Collection

View Repository
46196358 years agoReviewed by Kitploit
Share

RemoteRecon

Remote Recon and Collection

RemoteRecon provides the ability to execute post-exploitation capabilities against a remote host, without having to expose your complete toolkit/agent. Often times as operator's we need to compromise a host, just so we can keylog or screenshot (or some other miniscule task) against a person/host of interest. Why should you have to push over beacon, empire, innuendo, meterpreter, or a custom RAT to the target? This increases the footprint that you have in the target environment, exposes functionality in your agent, and most likely your C2 infrastructure. An alternative would be to deploy a secondary agent to targets of interest and collect intelligence. Then store this data for retrieval at your discretion. If these compromised endpoints are discovered by IR teams, you lose those endpoints and the information you've collected, but nothing more. Below is a visual representation of how I imagine an adversary would utilize this.
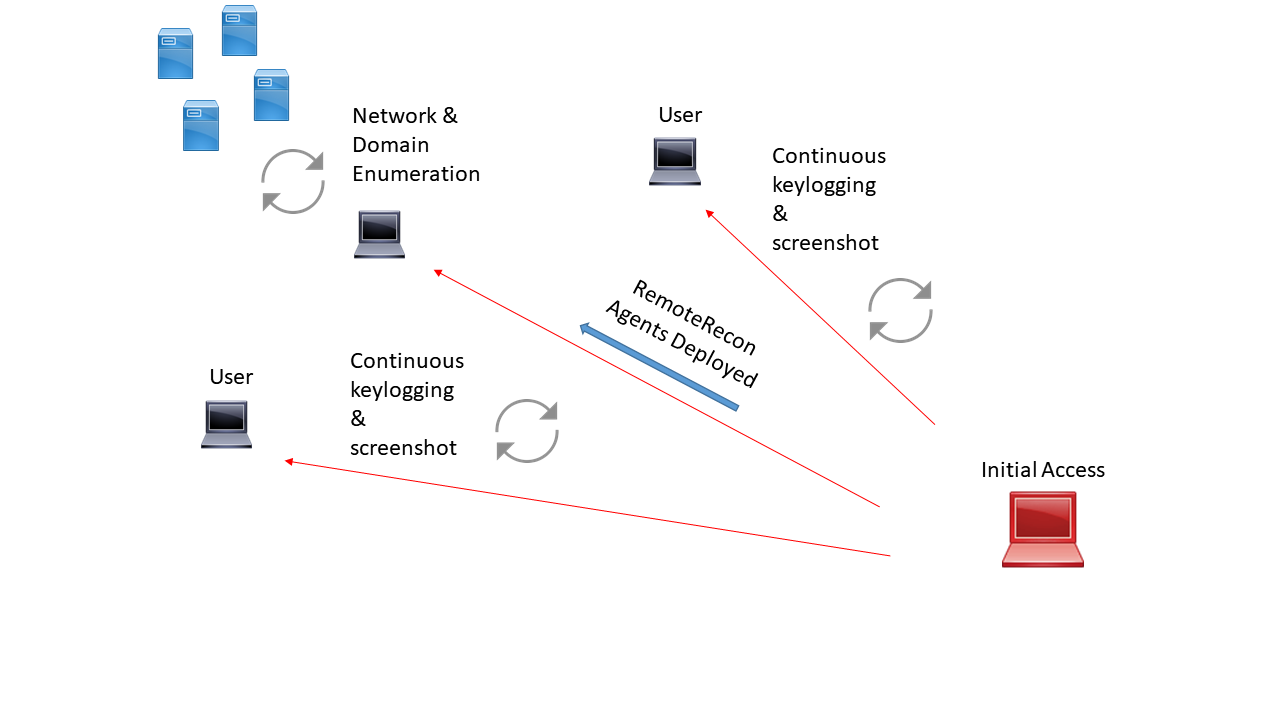
Remote Recon

RemoteRecon utilizes the registry for data storage, with WMI as an internal C2 channel. All commands are executed in a asynchronous, push and pull manner. Meaning that you will send commands via the powershell controller and then retrieve the results of that command via the registry. All results will be displayed in the local console.

Current Capabilities

PowerShell

Screenshot

Token Impersonation

Inject ReflectiveDll (Must Export the ReflectiveLoader function from Stephen Fewer)

Inject Shellcode

Keylog

Improvements, Additions, ToDo's:

Dynamically Load and execute .NET assemblies

Support non reflective dll's for injection

Build Dependecies

The RemoteRecon.ps1 script already contains a fully weaponized JS payload for the Agent. The payload will only be updated as the code base changes.

If you wish to make changes to the codebase on your own, there are a few depencies required.

  1. Visual Studio 2015+
  2. Windows 7 and .NET SDK
  3. Windows 8.1 SDK
  4. mscorlib.tlh (This is included in the project but there are instances where intellisense can't seem to find it [shrug])
  5. .NET 3.5 & 4
  6. James Forshaw's DotNetToJScript project
  7. Fody/Costura Nuget package. Package and embed any extra dependencies in .NET.

Credit

Thanks to these individuals for their contributions via code or knowledge :)

ambray

tifkin

mattifestation

subtee

harmj0y

For a short setup guide, please visit the wiki

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →






