

ARTEX
 trhhubsd/artex
Multi-agent LLM system for autonomous penetration testing in isolated labs: planner/worker agents share asset and exploration graphs, with MITM…
ai-securityexploitationinformation-gathering+7
2.1k
trhhubsd/artexMulti-agent LLM system for autonomous penetration testing in isolated labs: planner/worker agents share asset and exploration graphs, with MITM…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
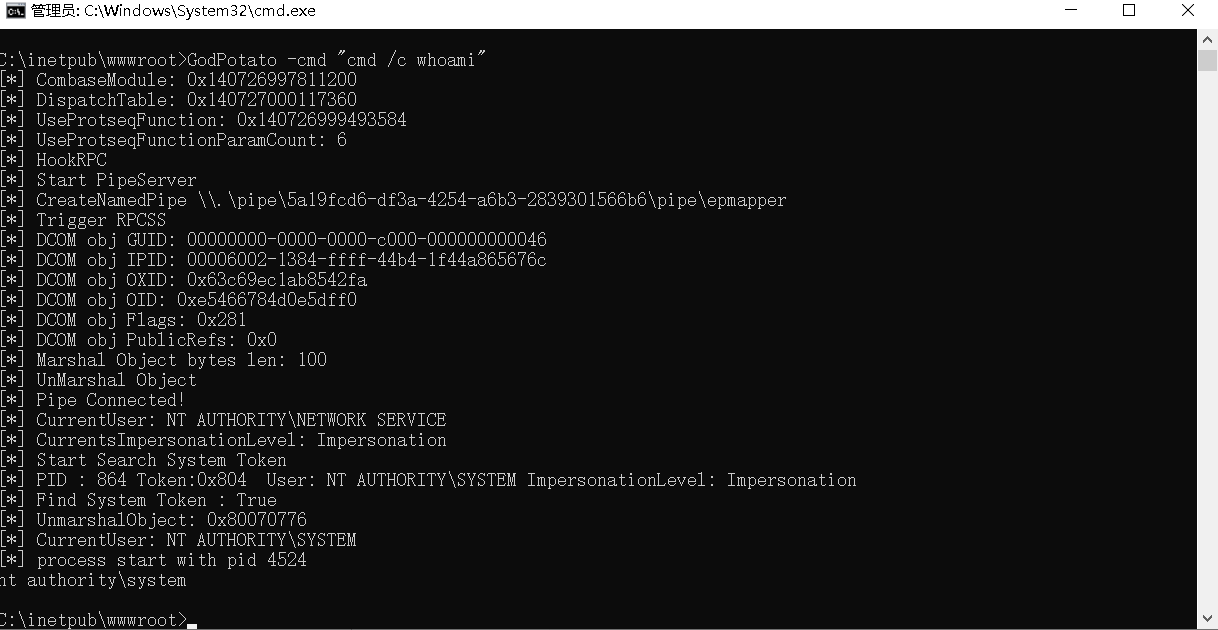 beichendream/godpotato
DCOM-based privilege escalation tool for Windows Server 2012-2022 and Windows 8-11, elevating users with ImpersonatePrivilege to NT AUTHORITY\SYSTEM…
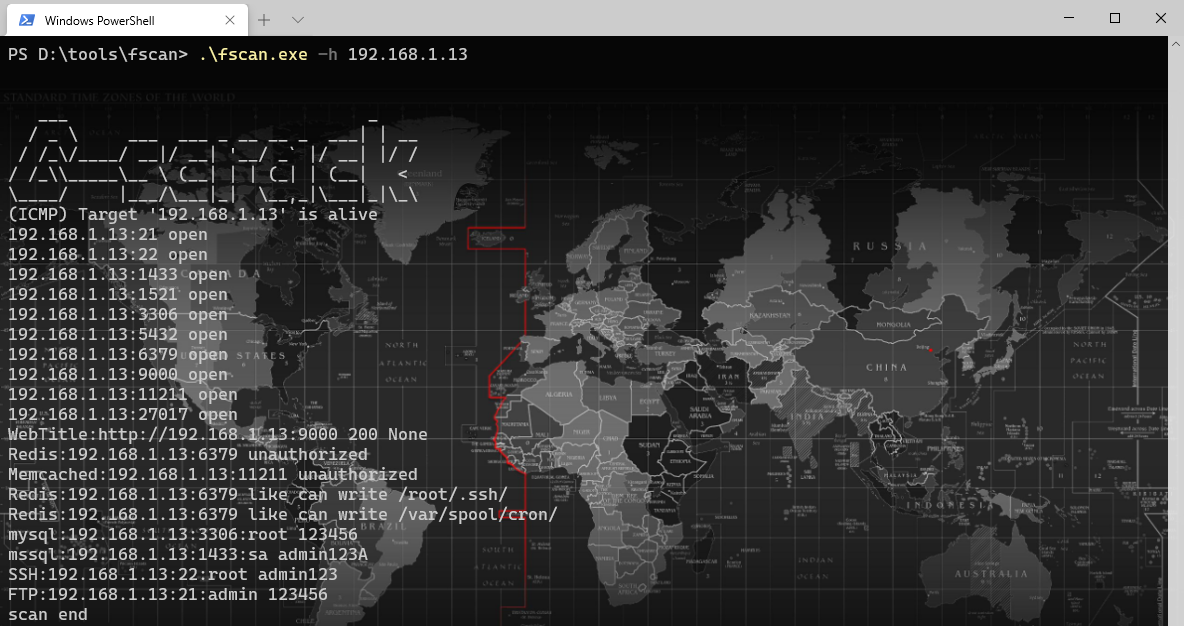 shadow1ng/fscan
一款内网综合扫描工具,方便一键自动化、全方位漏扫扫描。(An intranet comprehensive scanning tool, enabling one-click automated, all-round vulnerability scanning)
 0xtatsuki/cve-2026-31857
Craft CMS RCE via relational conditionals in the control panel
 f4r3sx0/ios-bluetooth-ethernet-exploit
iOS Bluetooth PAN vulnerability that opens USB port 62078 and displays Ethernet icon without any adapter (€0). Apple sells a €89.95 adapter for the…
 scumfrog/fiberbreak
React2Shell Exploitation Tool (CVE-2025-55182)
 7h30th3r0n3/cve-2026-53625-glpi-poc
GLPI Privilege Escalation via authtype Manipulation PoC - CVE-2026-53625. Ethical PoC for the GLPI vulnerability allowing a Technician to take full…
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 deimosc2/deimosc2
DeimosC2 is a Golang command and control framework for post-exploitation.
 j4ck3lsyn-gen2/cve-2026-63030-wp2r00t
A fully red-team(offensive security) weaponized variant of wp2shell, built for authorized penetration testing & educational purposes.
 horizon3ai/vrealizeloginsightrce
POC for RCE using vulnerabilities described in VMSA-2023-0001
 tc4dy/cve-2026-87902-toolkit
WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…
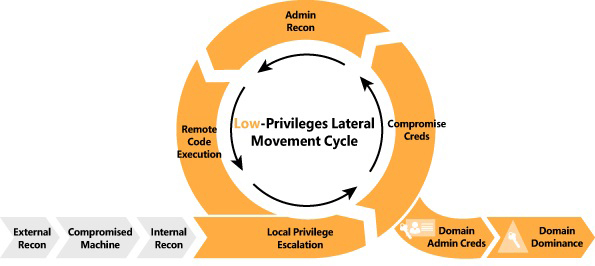 ihebski/a-red-teamer-diaries
RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.
 nicetop1027/cve-2026-termius
Vulnerability disclosure with PoCs for three critical Termius macOS flaws: Remote Code Execution via exposed Node modules, Local Privilege Escalation…
 super-meuw/cve-2026-86218
Python 3 proof-of-concept exploit for CVE-2026-86218, a pre-auth RCE in N-able N-central via a Struts multipart race condition, with command…
 anonymous941/zygote-injection-toolkit
A command-line utility to exploit Android Zygote injection (CVE-2024-31317)