

ARES
 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
cloud-securitycommand-and-controldefensive-tools+5
478
mafifrizi/aresAutonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 hyd3sec/azur3alph4
PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
 nurupo/rootkit
Linux kernel module that grants root privileges, hides processes/files, and protects itself from unloading, designed for educational purposes on…
 wayang1337/cve-2026-80099
Newfold plugins (wp-module-data <= 2.9.7) Unauthenticated
 gloxec/crossc2
generate CobaltStrike's cross-platform payload
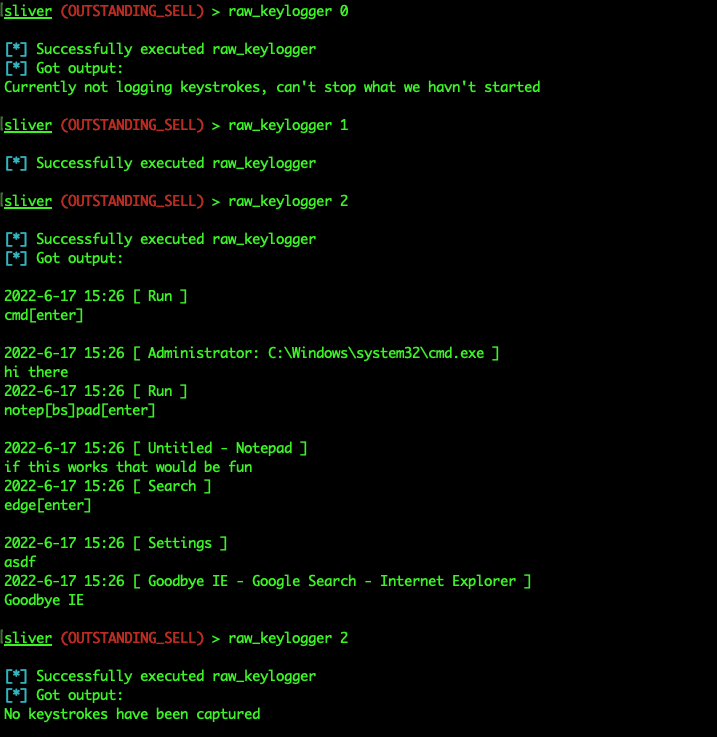 trustedsec/sliverkeylogger
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…
 mncoppola/rpef
Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers
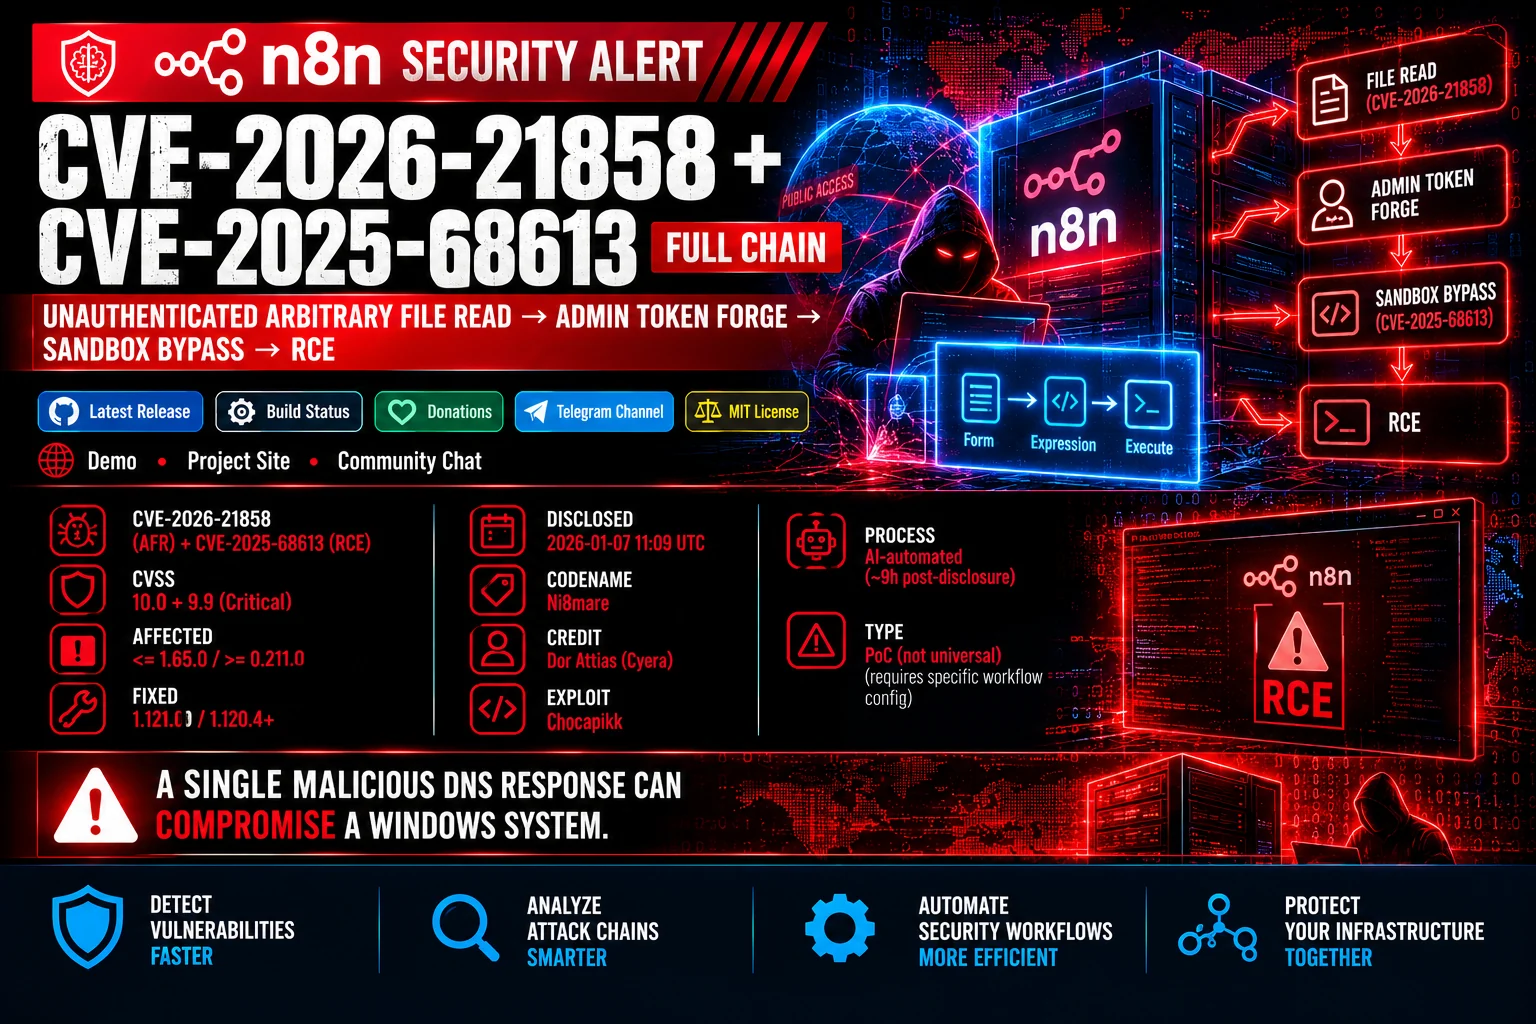 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
 riskydissonance/sharpcookiemonster
C# tool to dump all cookies from Chrome/Edge browsers, including httpOnly and secure flags, for session hijacking and post-exploitation credential…
 zyn3rgy/smbtakeover
BOF and Python3 implementation of technique to unbind 445/tcp on Windows via SCM interactions
 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 zedeldi/cve-2025-47827
PoC and vulnerability report for CVE-2025-47827.