
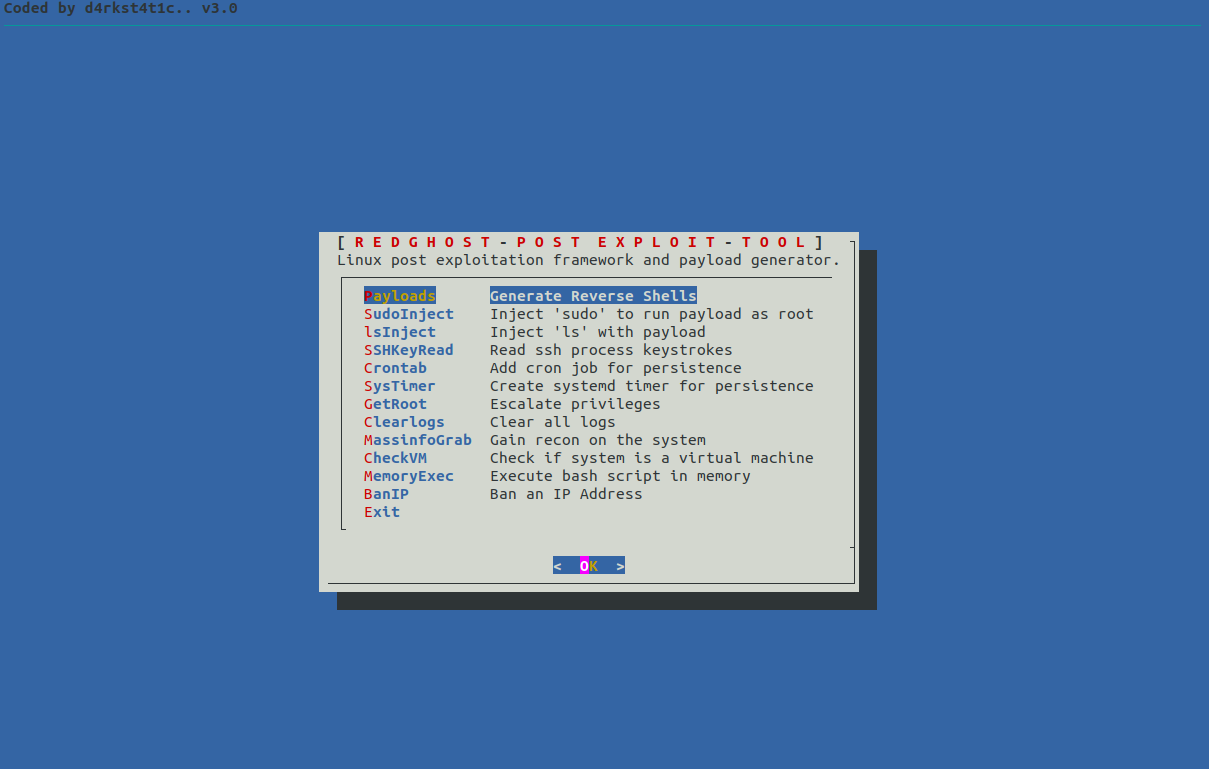
RedGhost
 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
command-and-controllateral-movementpayload-generation+5
541
d4rk007/redghostLinux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
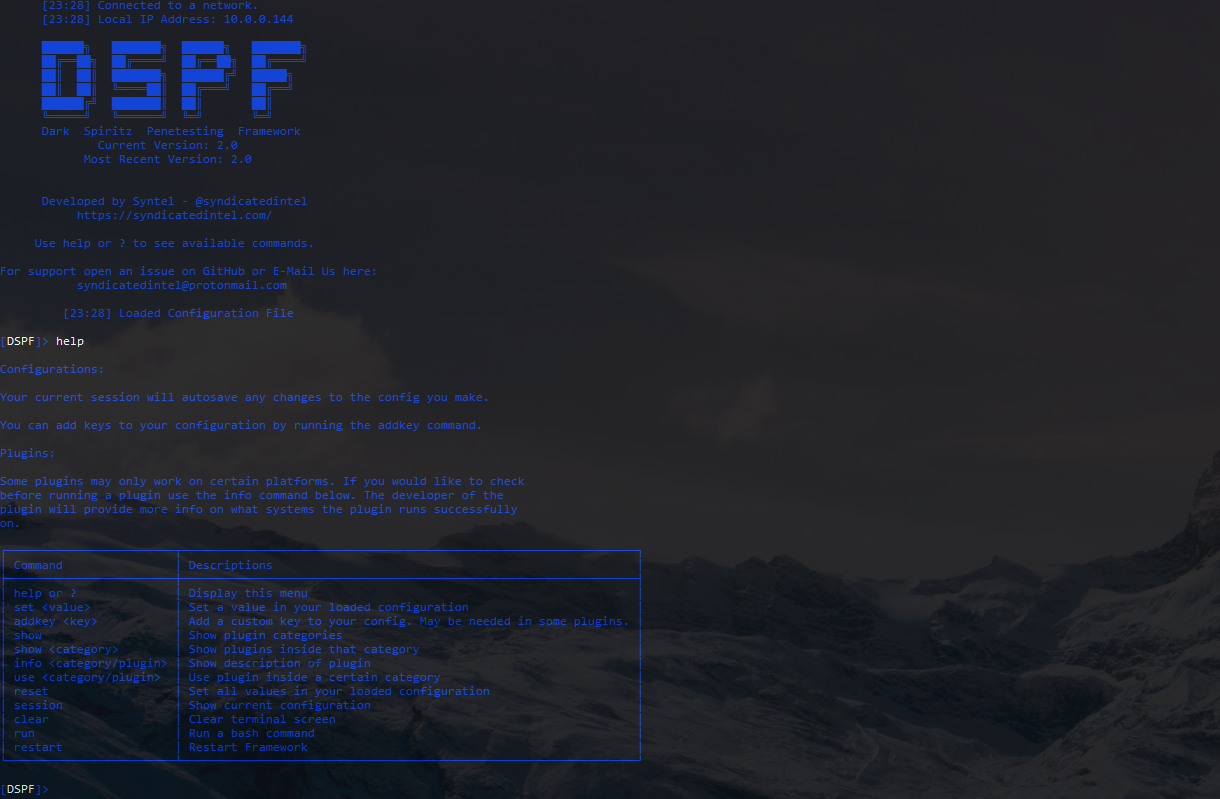 m4cs/darkspiritz
🌔 Official Repository for DarkSpiritz Penetration Framework | Written in Python 🐍
 erarnitox/malvexc2
A simple C2 Framework written in modern C++
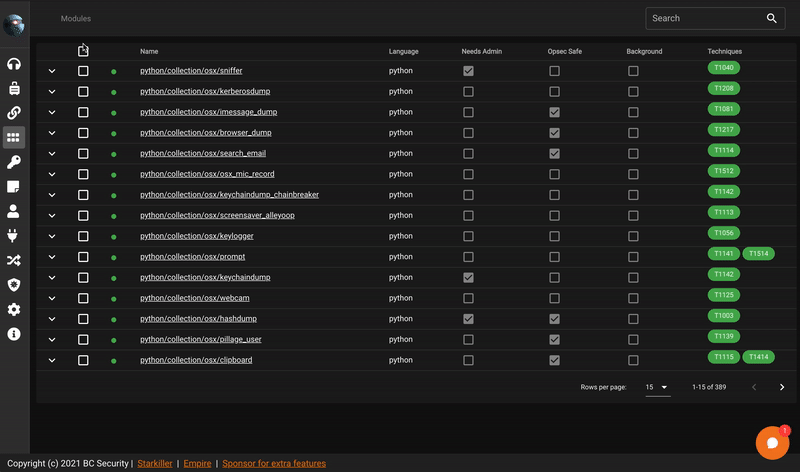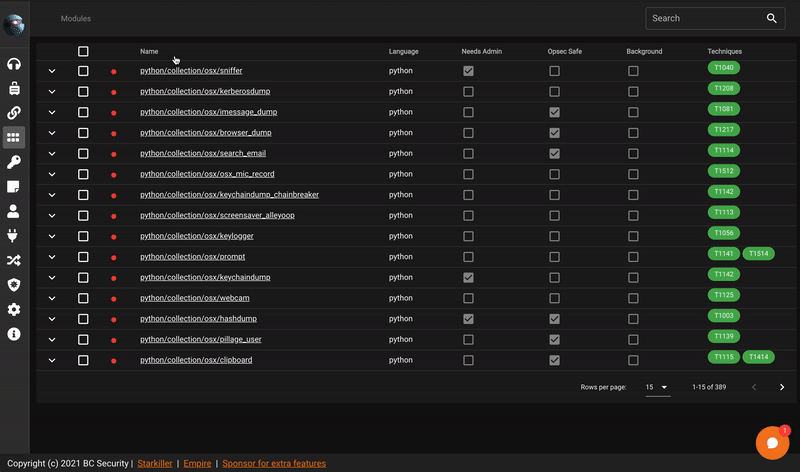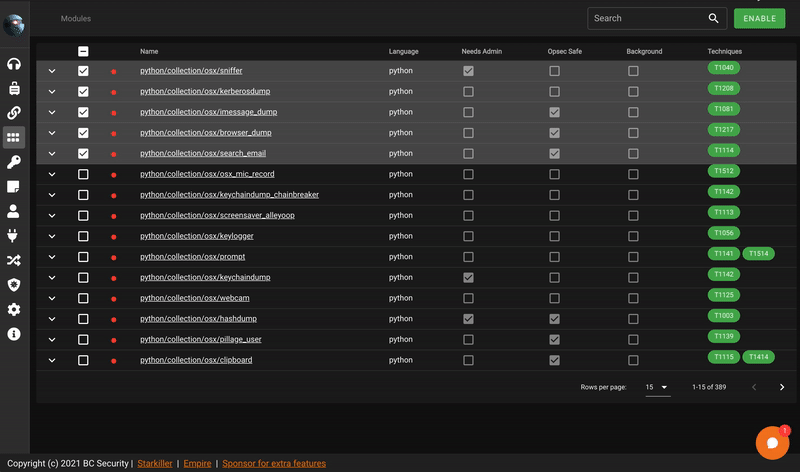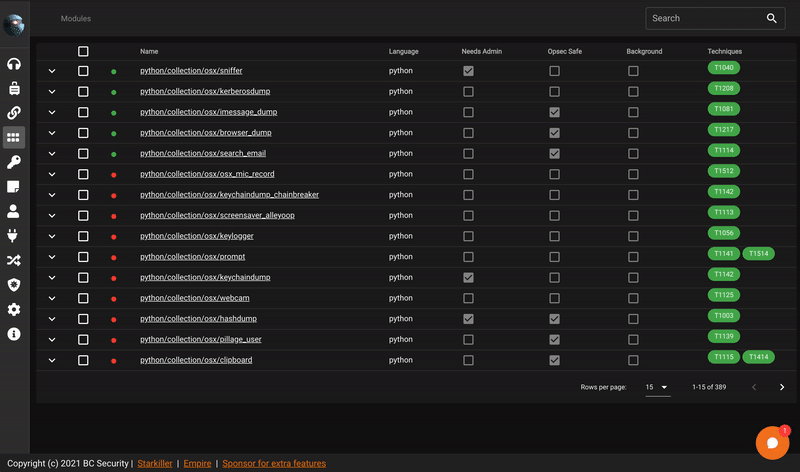 bc-security/starkiller
Starkiller is a Frontend for PowerShell Empire.
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 dobin/antnium
A C2 framework for initial access in Go
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 cn33liz/p0wnedshell
PowerShell Runspace Post Exploitation Toolkit
 0xtriboulet/revenant
Revenant - A 3rd party agent for Havoc that demonstrates evasion techniques in the context of a C2 framework
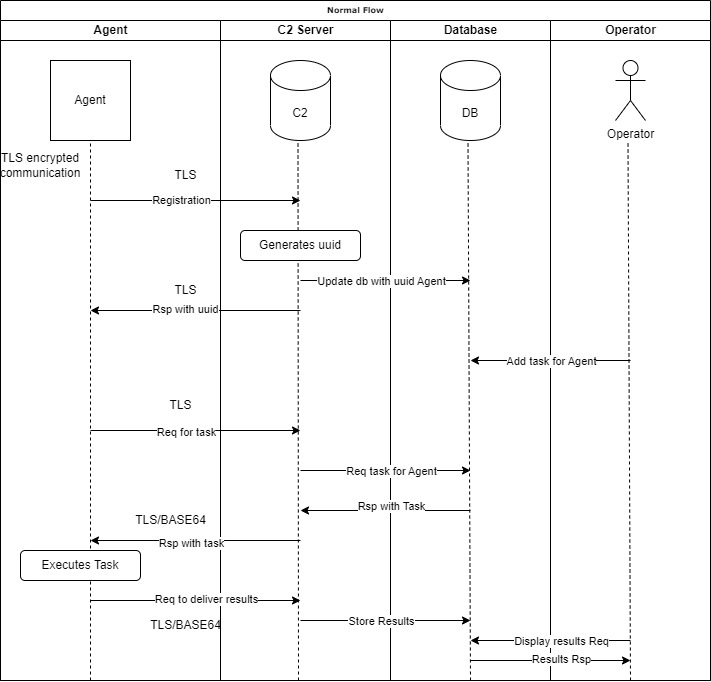 voukatas/commander
Python-based command and control framework with encrypted TLS communication, multiple agent support (Python/C), interactive sessions, file transfer,…
 trustedsec/tap
The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.
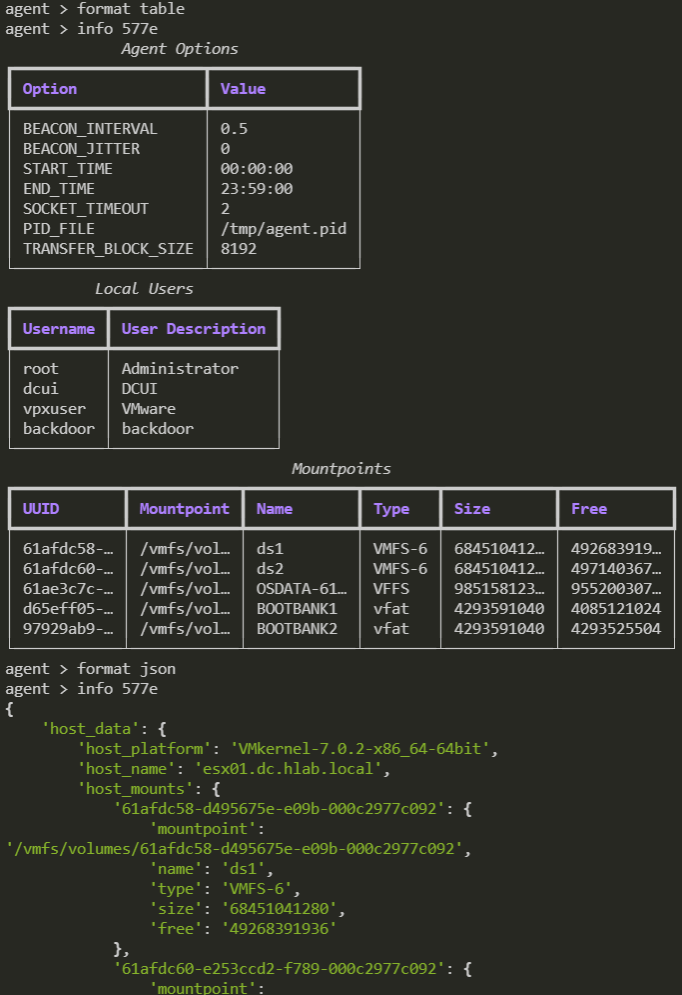 psmths/reave
WIP Post-exploitation framework tailored for hypervisors.
 phoenixc2/phoenixc2
Command & Control-Framework created for collaboration in python3
 esskumar/phantomevasion
Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…
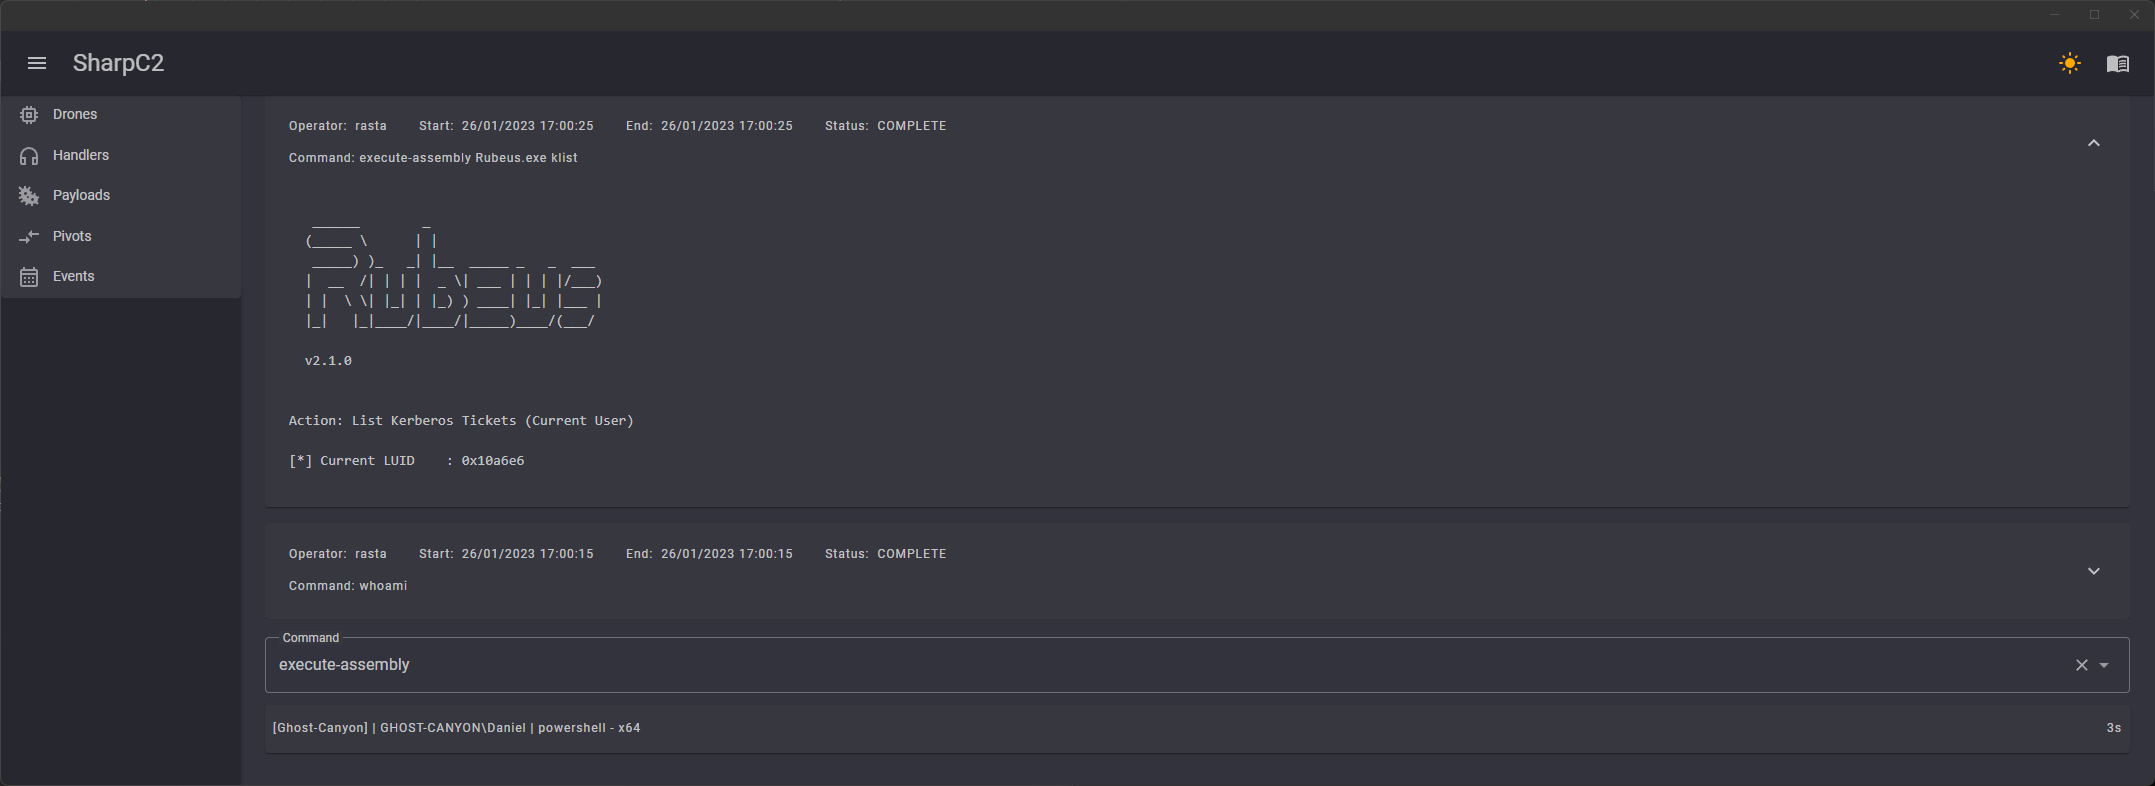 rasta-mouse/sharpc2
Command and Control Framework written in C#