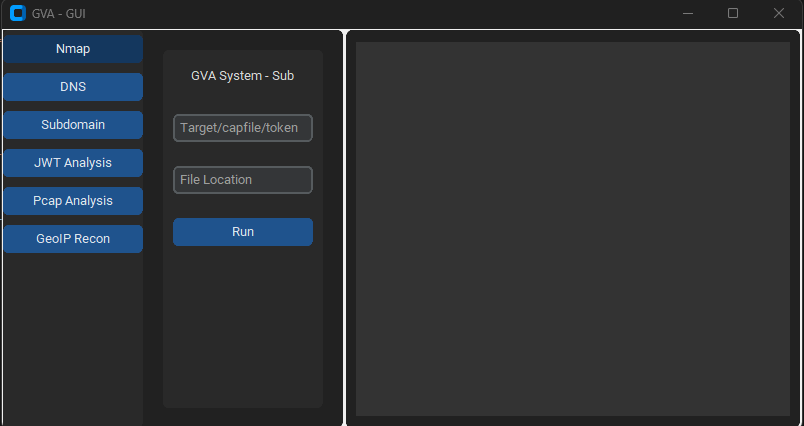

GPT_Vuln-analyzer
Uses ChatGPT API, Bard API, and Llama2, Python-Nmap, DNS Recon, PCAP and JWT recon modules and uses the GPT3 model to create vulnerability reports…

Uses ChatGPT API, Bard API, and Llama2, Python-Nmap, DNS Recon, PCAP and JWT recon modules and uses the GPT3 model to create vulnerability reports…

Pentest/BugBounty progress control with scanning modules

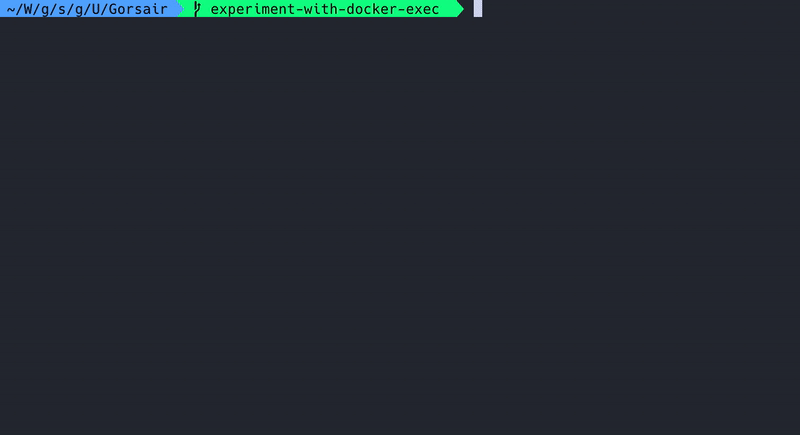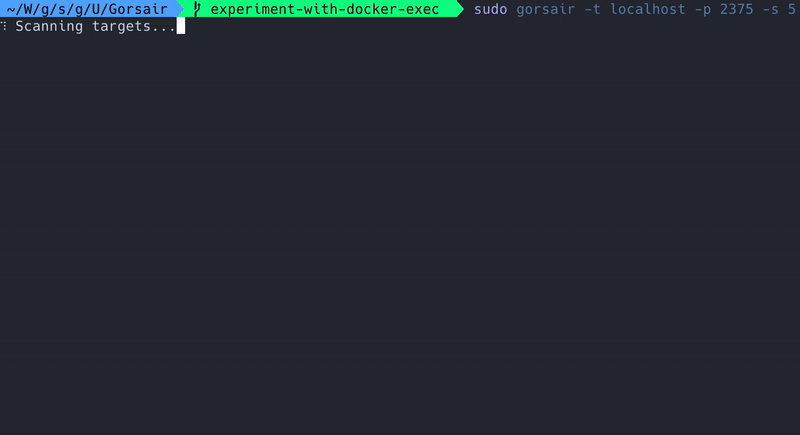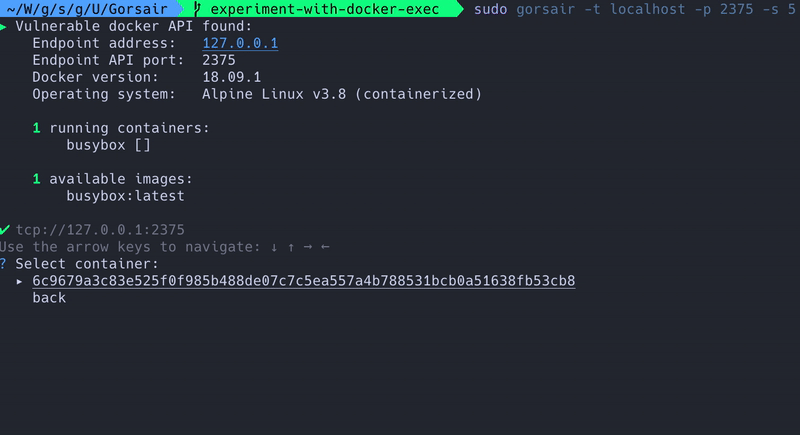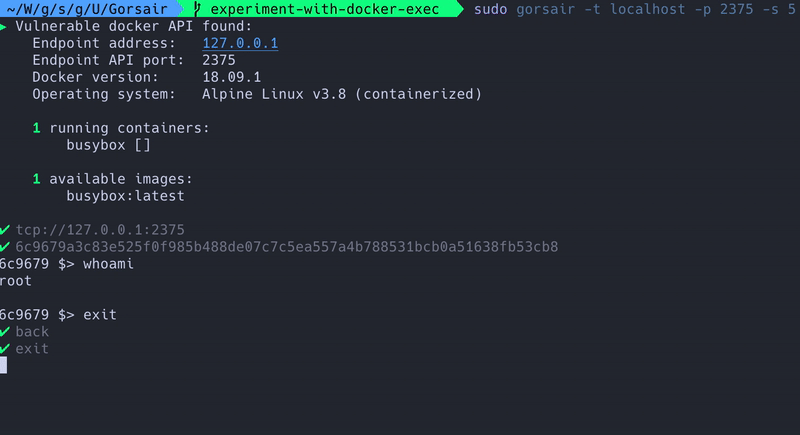
Gorsair gives root access on remote docker containers that expose their APIs

Recon is a script to perform a full recon on a target with the main tools to search for vulnerabilities. Created based on @ofjaaah and @Jhaddix…

A personal tool in GO for my usual first enumeration steps on a target

Manual black-box penetration test of MagnoHost and MeteorCloud infrastructure, documenting exposed MariaDB, default credentials, CVE-2024-27102, and…

Take a list of domains and probe for working HTTP and HTTPS servers

Pentesting suite for Maltego based on data in a Metasploit database

Scan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.

CLI tool for inspecting and managing services listening on localhost ports

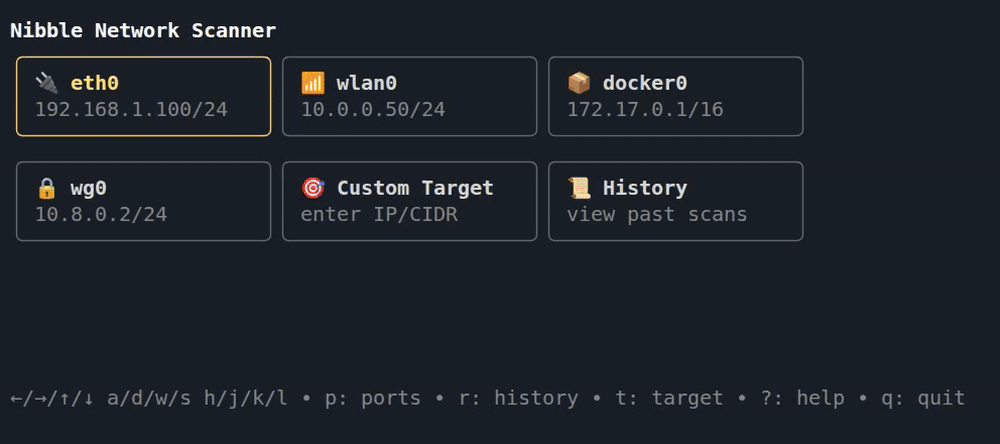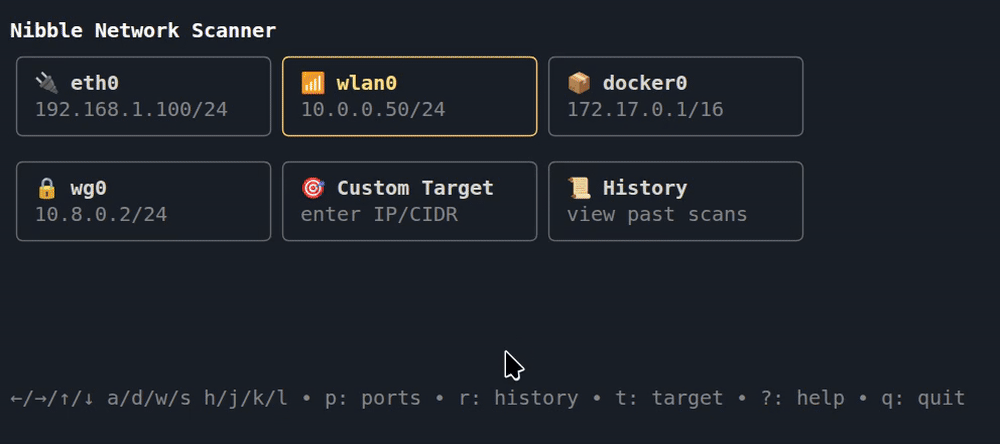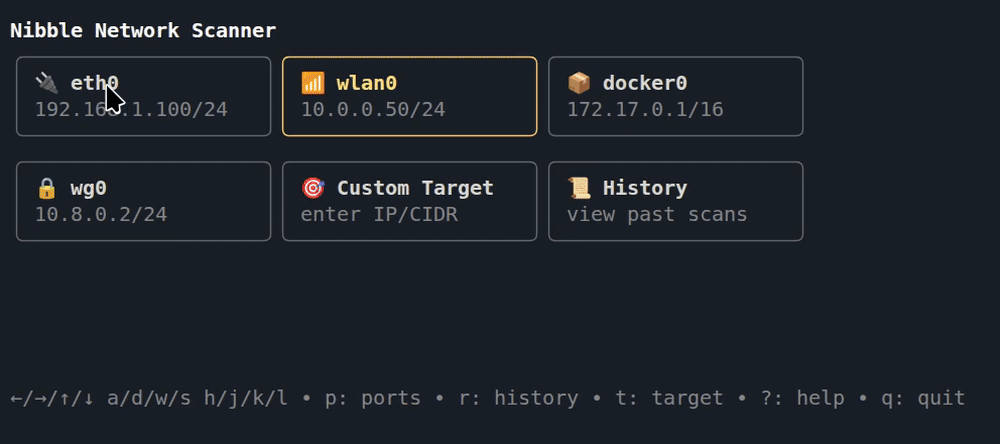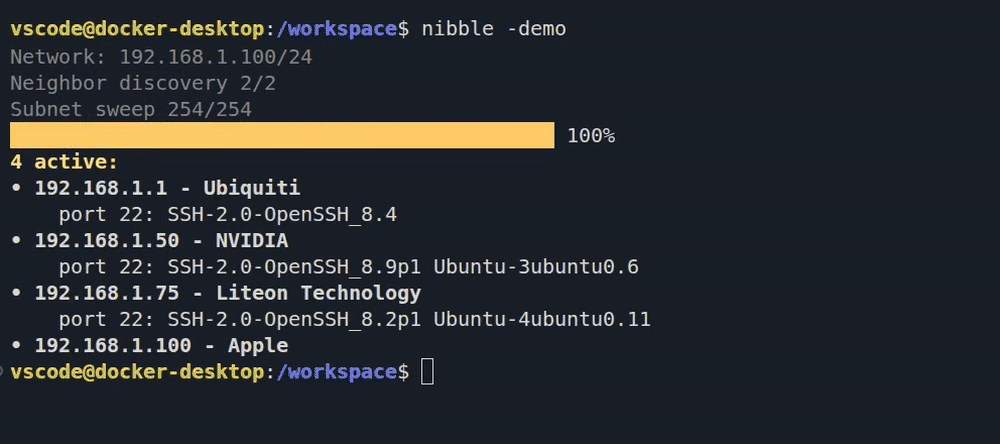
easy to use network scanner, with a clickable tui interface

Multi-threaded, reliable scanner for CVE-2018-10933.

Multi-protocol port scanner with fingerprint recognition, service detection, and brute-force authentication testing. Supports 1200+ protocols, 10000+…

A tool to perform port scanning using vulnerable Request-Baskets

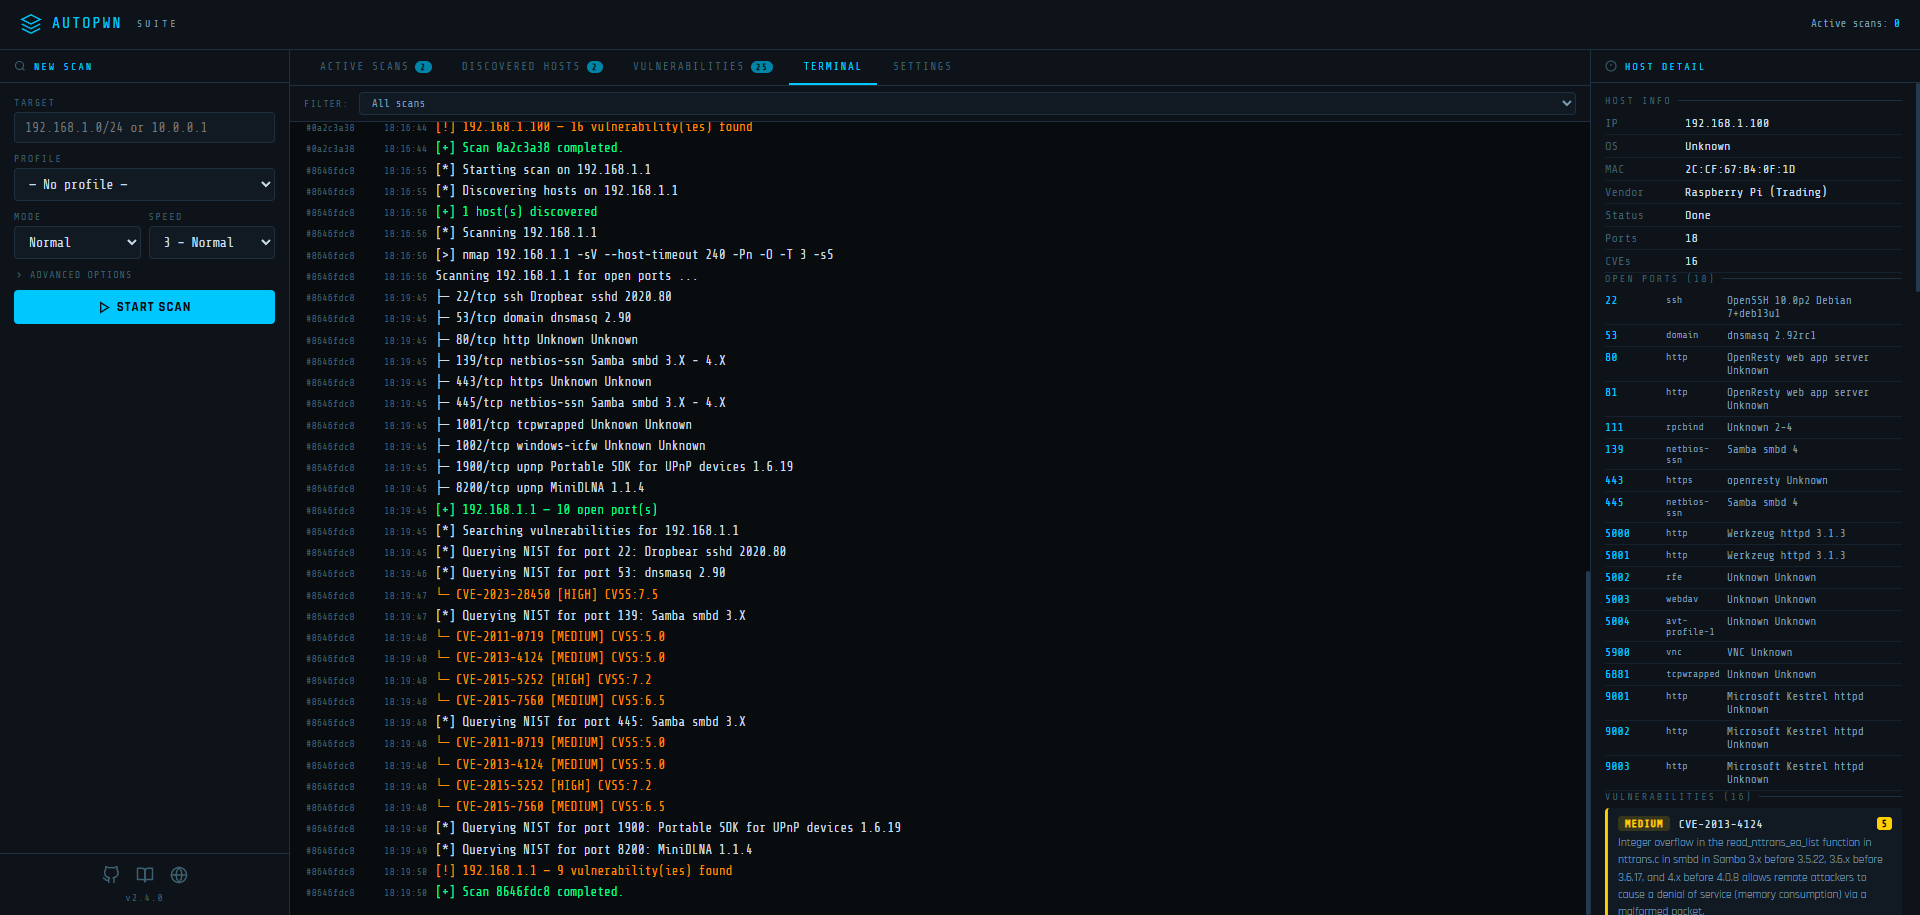
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.

Self-hosted network discovery and search engine with continuous port scanning, deep protocol probing across ~100 services, local CVE matching, and…

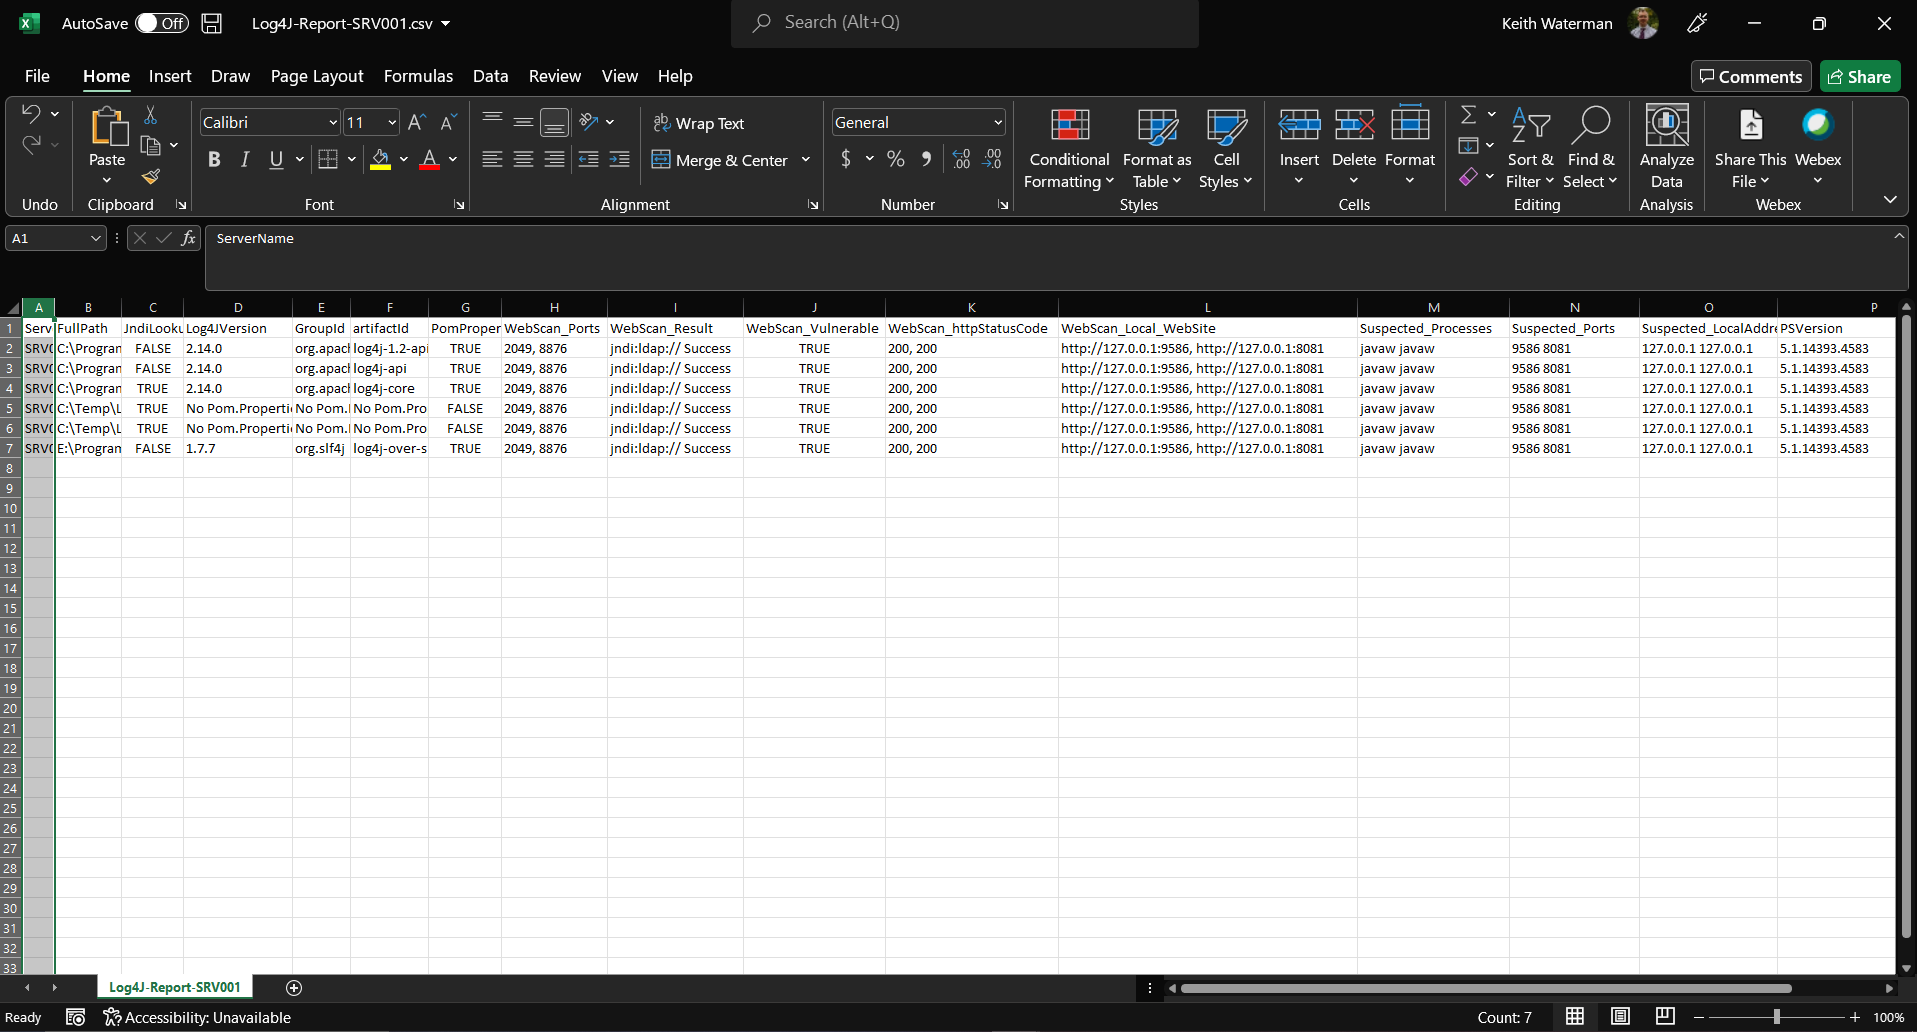
Identifying all log4j components across on local windows servers. CVE-2021-44228