RED_HAWK
 tuhinshubhra/red_hawk
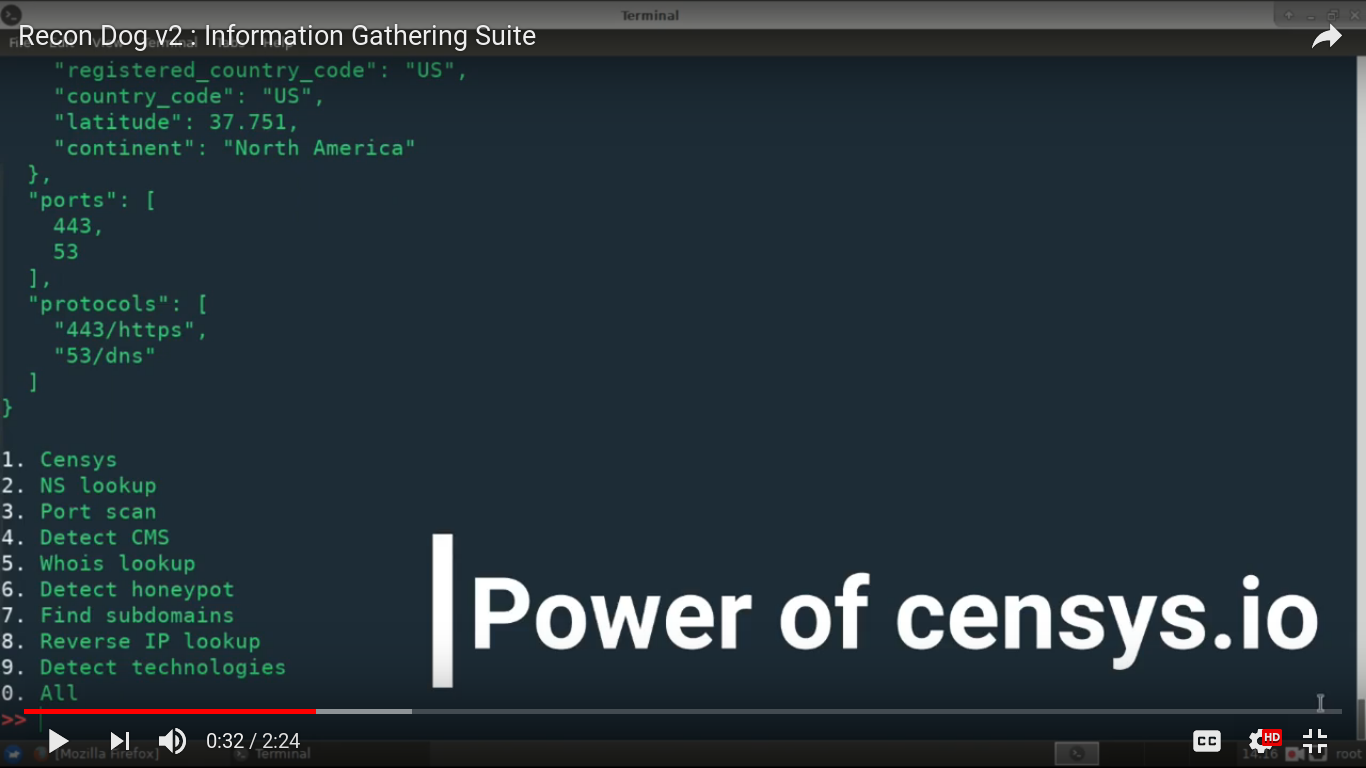
All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
crawlerdns-analysisinformation-gathering+5
3.8k
tuhinshubhra/red_hawkAll in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 besimorhino/powercat
netshell features all in version 2 powershell
 eldraco/domain_analyzer
Analyze the security of any domain by finding all the information possible. Made in python.
 devxprite/infoooze
A OSINT tool which helps you to quickly find information effectively. All you need is to input and it will take take care of rest.
 robotshell/magicrecon
MagicRecon is a powerful shell script to maximize the recon and data collection process of an objective and finding common vulnerabilities, all this…
 silverpoision/rock-on
Rock-On is a all in one Recon tool that will just get a single entry of the Domain name and do all of the work alone.
 rpranshu/eternalview
EternalView is an all in one basic information gathering and vulnerability assessment tool
 cappricio-securities/ghostrecon
gh0str3con is a All in one cloud based web Recon tool.
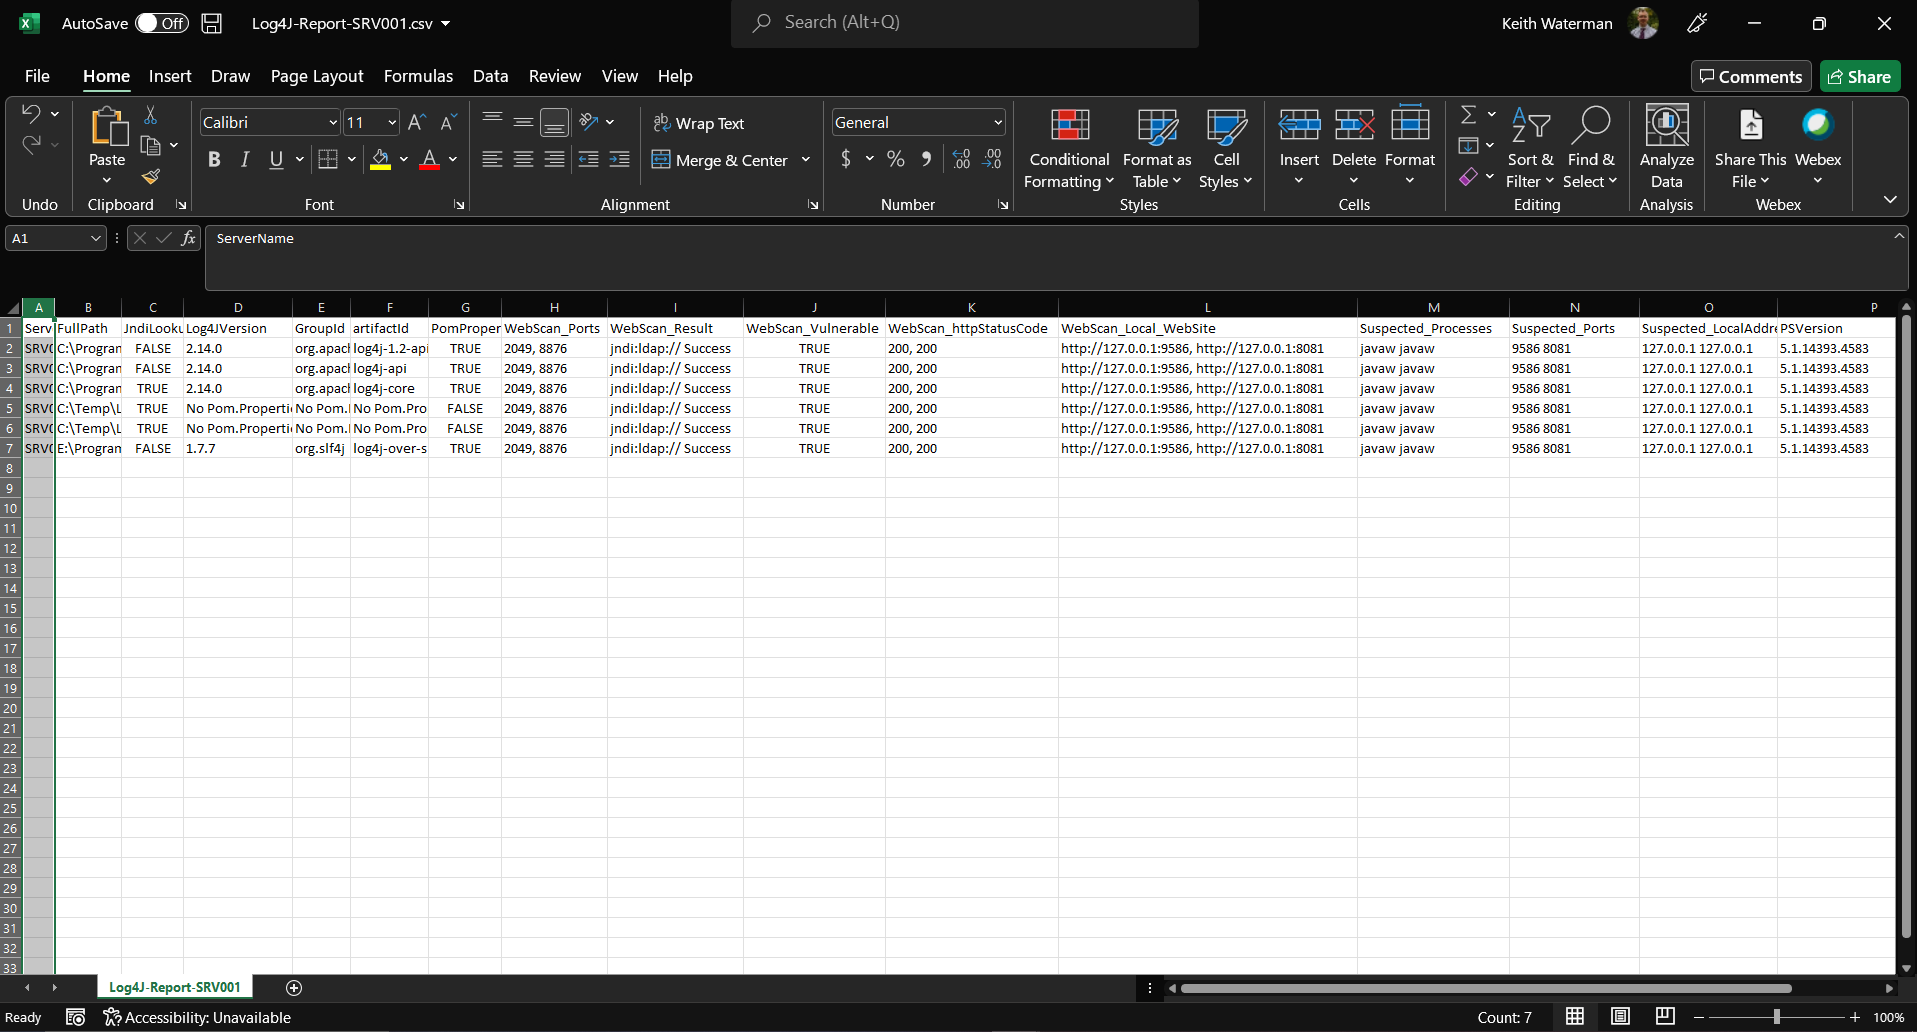 keysau/get-log4j-windows-local
Identifying all log4j components across on local windows servers. CVE-2021-44228
 parbatzone/reconvault
🔍 Recon notes organizer for bug bounty hunters and CTF players — subdomains, ports, endpoints, vulns, all in one place.
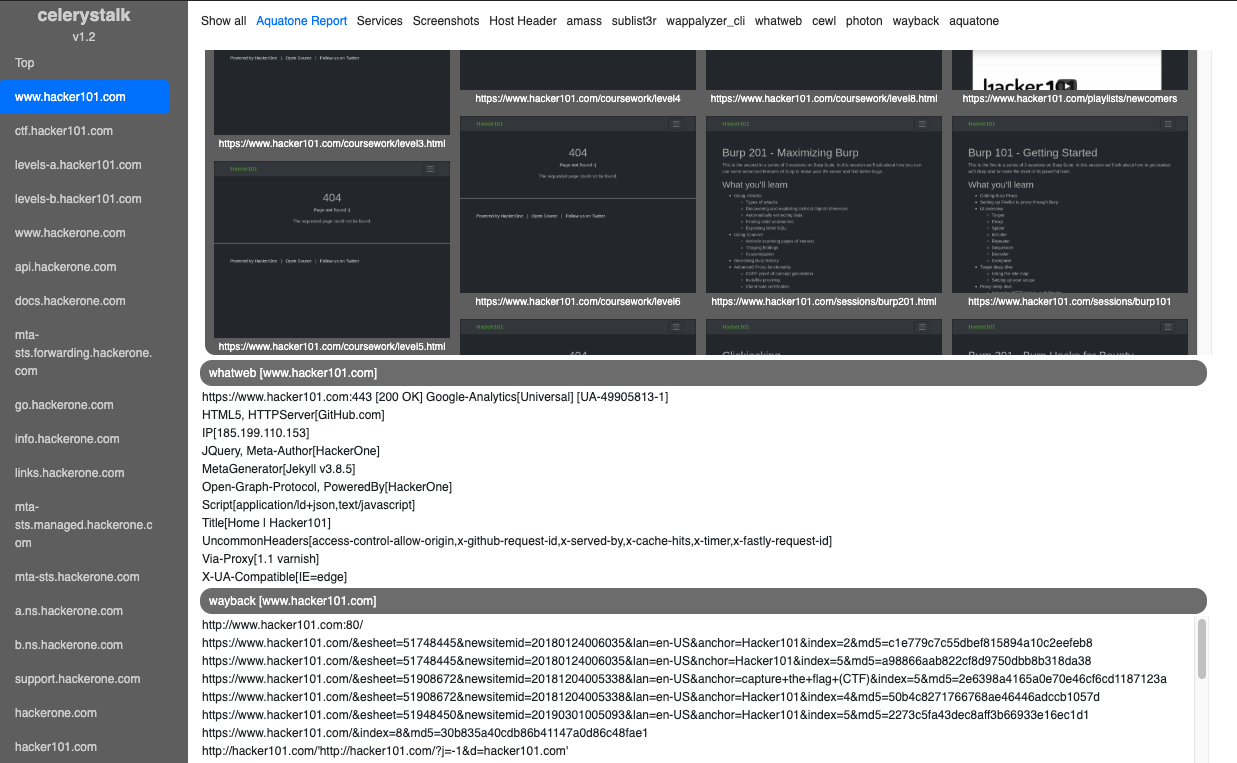 sethsec/celerystalk
An asynchronous enumeration & vulnerability scanner. Run all the tools on all the hosts.
 eslam3kl/3klcon
Automation Recon tool which works with Large & Medium scopes. It performs a lot of tasks and gets back all the results in separated files.
 ritvikb99/dark-fantasy-hack-tool
DDOS Tool: To take down small websites with HTTP FLOOD. Port scanner: To know the open ports of a site. FTP Password Cracker: To hack file system of…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 divinelabio/argus
The Ultimate Information Gathering Toolkit
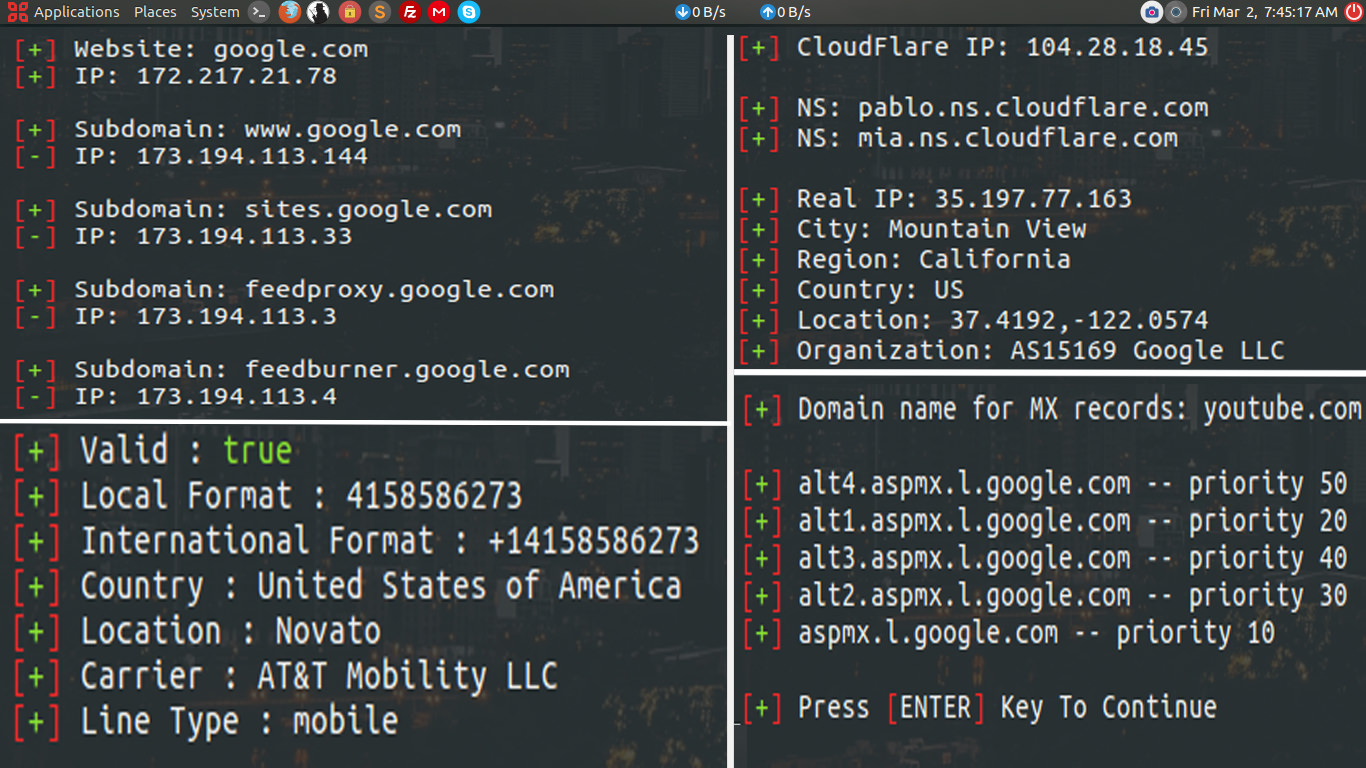 moham3driahi/th3inspector
Th3Inspector 🕵️ Best Tool For Information Gathering 🔎
 thewhiteh4t/finalrecon
Automated web reconnaissance tool providing header analysis, DNS enumeration, subdomain discovery, directory scanning, SSL inspection, and port…