

nmap
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
bluetooth-securitydatabase-securitydata-exfiltration+18
13.7k
nmap/nmapHigh-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
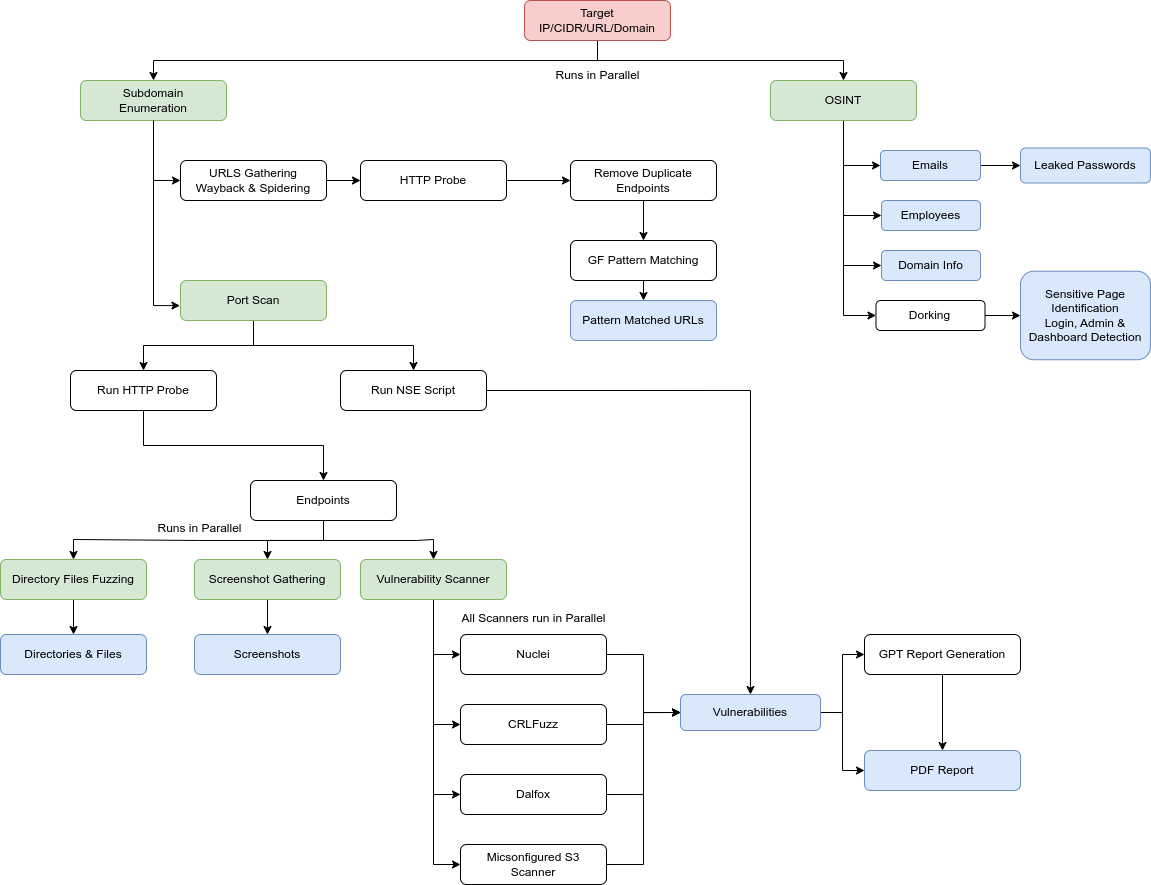 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 gwen001/pentest-tools
A collection of custom security tools for quick needs.
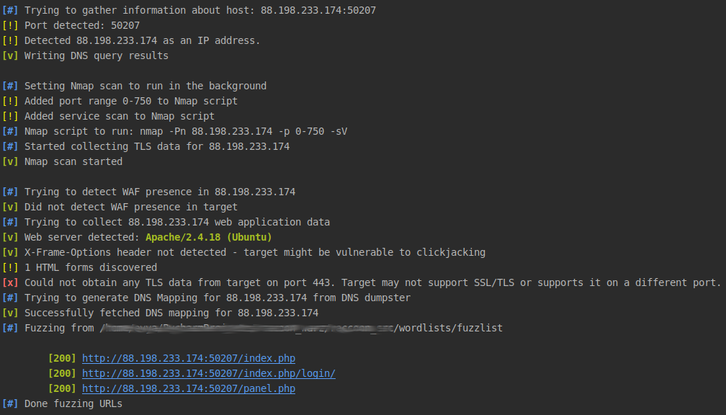 evyatarmeged/raccoon
A high performance offensive security tool for reconnaissance and vulnerability scanning
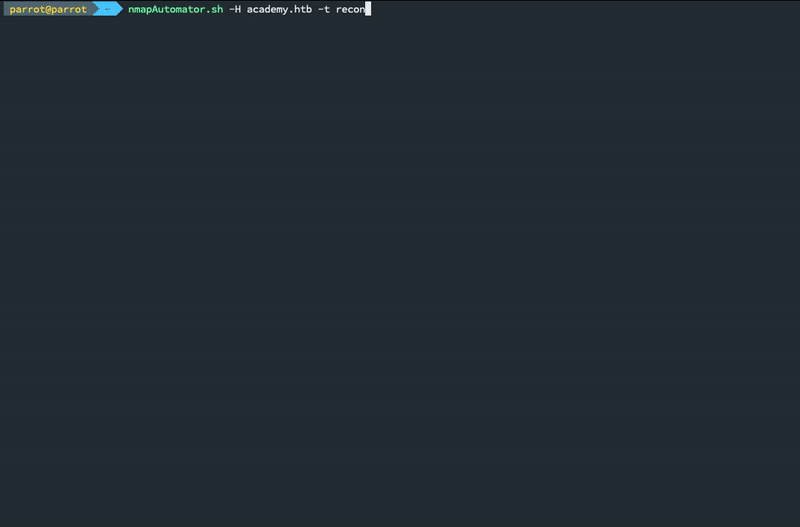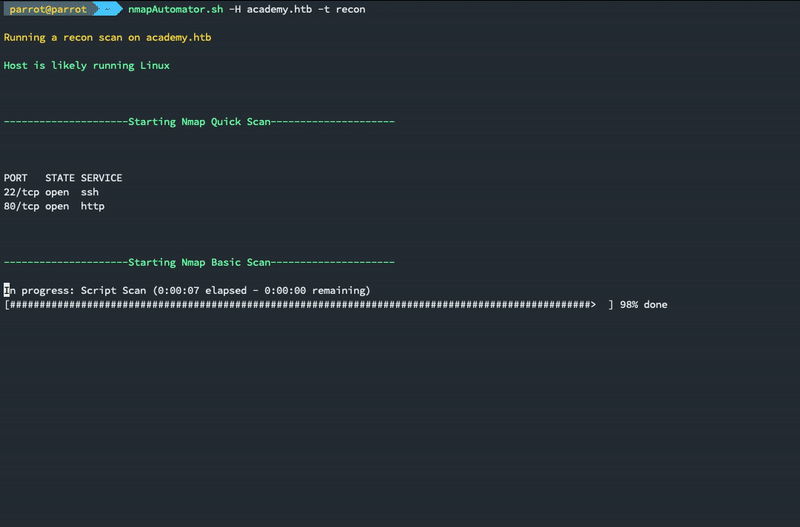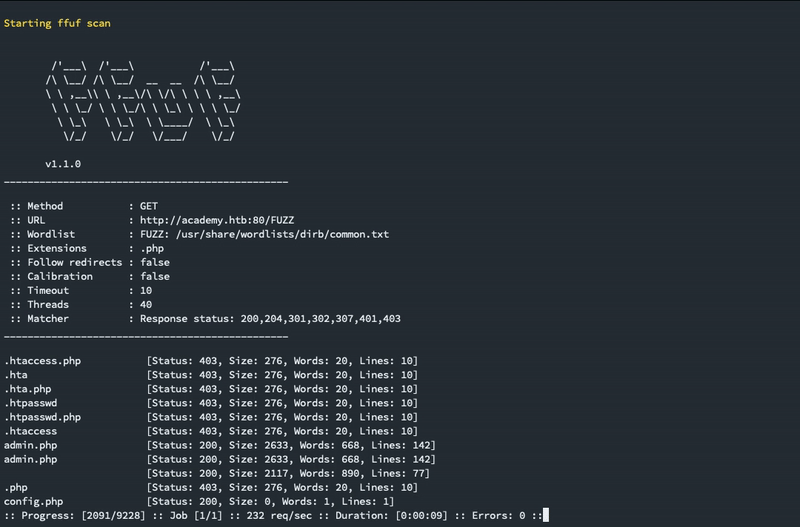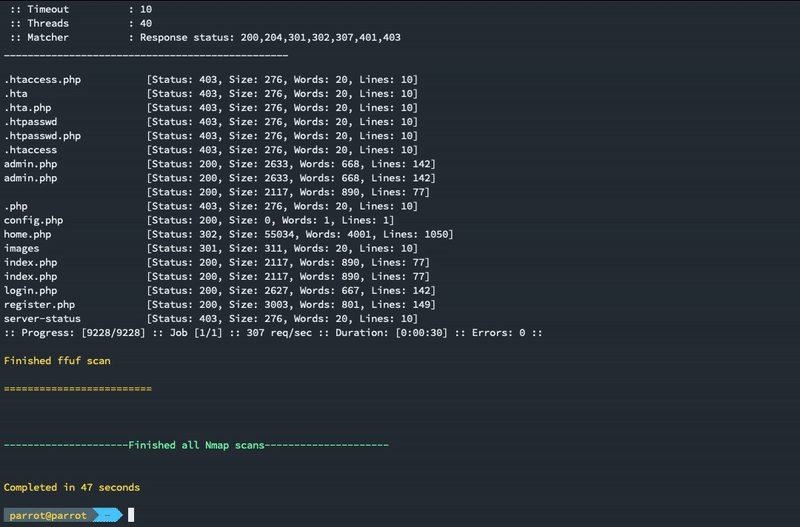 21y4d/nmapautomator
A script that you can run in the background!
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 0xinfection/tidos-framework
The Offensive Manual Web Application Penetration Testing Framework.
 bahaabdelwahed/killshot
A Penetration Testing Framework, Information gathering tool & Website Vulnerability Scanner
 pepelux/sippts
Set of tools to audit SIP based VoIP Systems
 0xinfection/logmepwn
A fully automated, reliable, super-fast, scanning and validation toolkit for the Log4J RCE CVE-2021-44228 vulnerability.
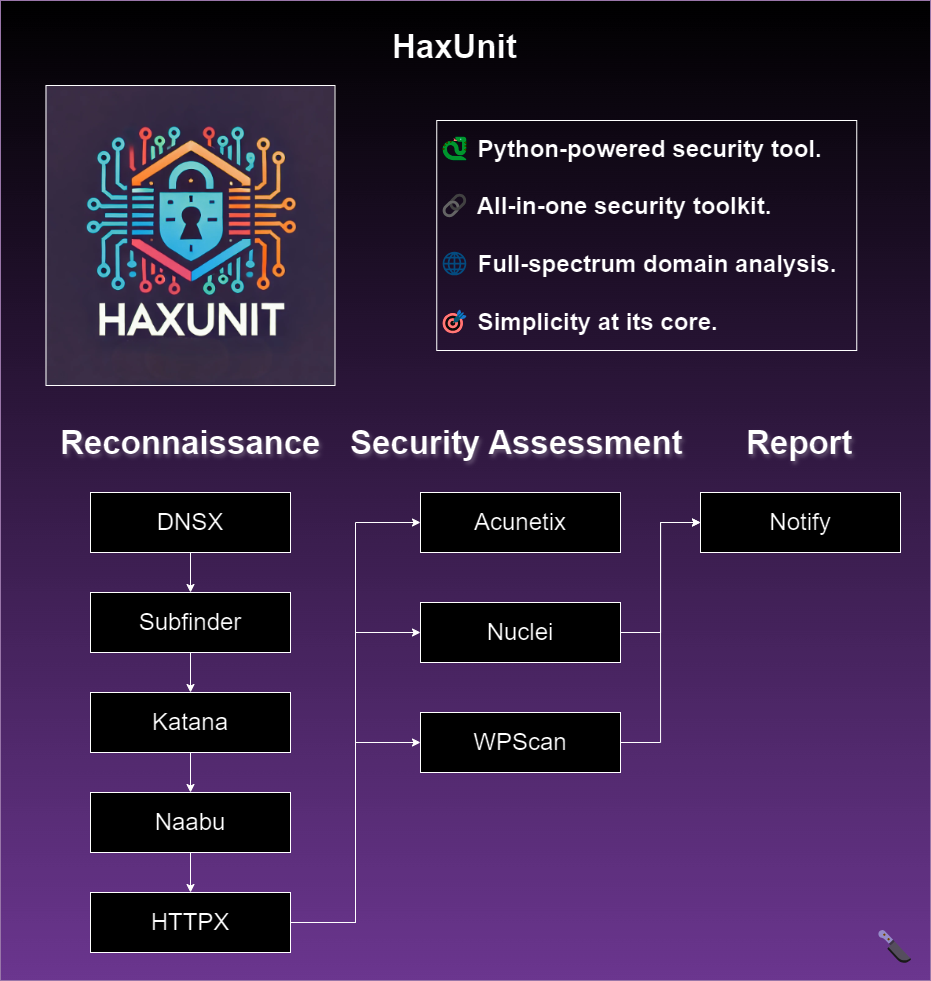 bandit-haxunit/haxunit
Automated web domain reconnaissance and security assessment tool integrating subdomain enumeration, port scanning, vulnerability scanning, and…
 dirsoooo/recon
Recon is a script to perform a full recon on a target with the main tools to search for vulnerabilities. Created based on @ofjaaah and @Jhaddix…