Metasploitable2-Reconnaissance-and-UnrealIRCd-Backdoor-Exploitation

End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.

End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.

A third-party Gopher Assassin for the Havoc Framework.

Quick network scanner library. https://crates.io/crates/qscan

System Vulnerability Checklist & Network Security Hardening project featuring reconnaissance, vsFTPd backdoor analysis (CVE-2011-2523), and active…

IPv6 analysis tool: the other side

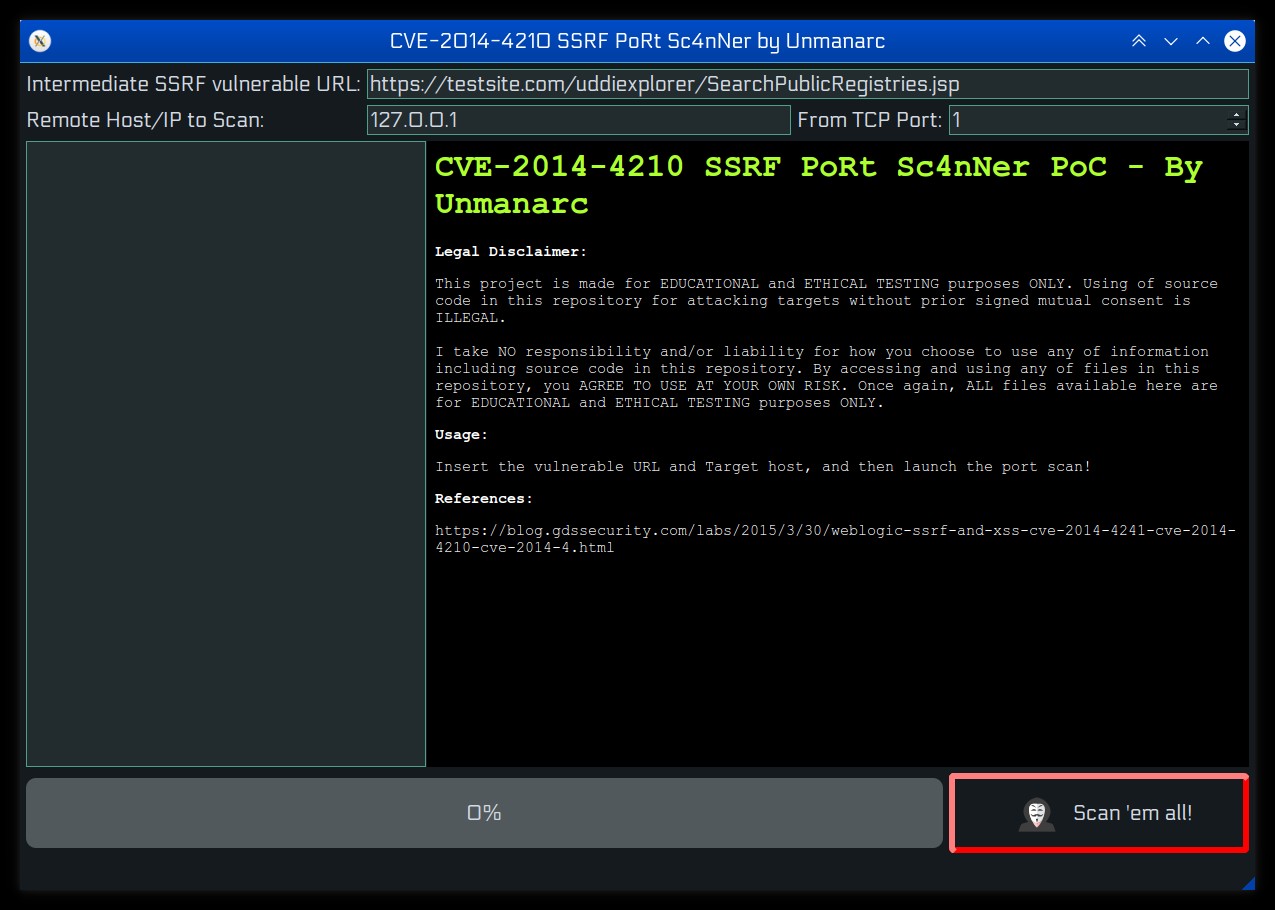
CVE-2014-4210 SSRF PORTSCANNER PoC

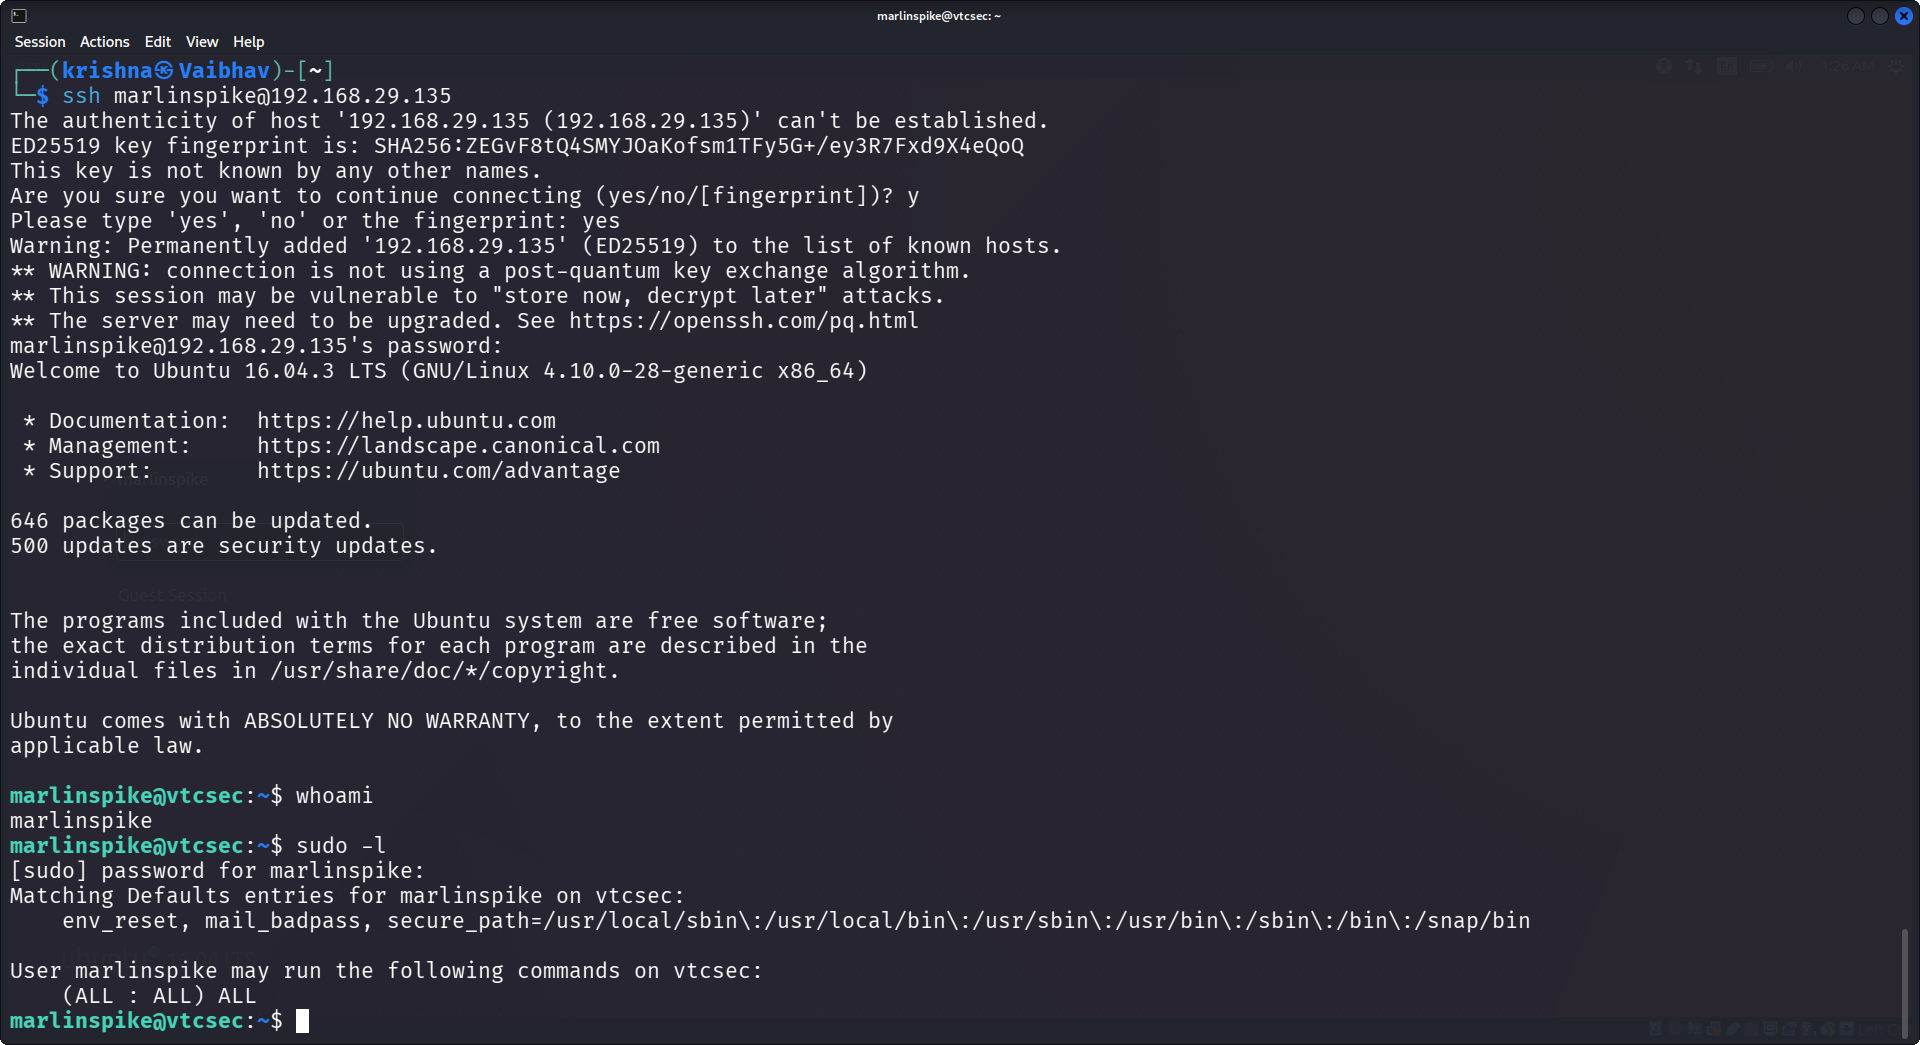
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)

Script of Network Security Project - Attack on CVE-2021-22555

AlienTec-Recon-Tool

Project: vsFTPd 2.3.4 backdoor exploitation (CVE-2011-2523) on Metasploitable 2.

The hackers tool belt

Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.

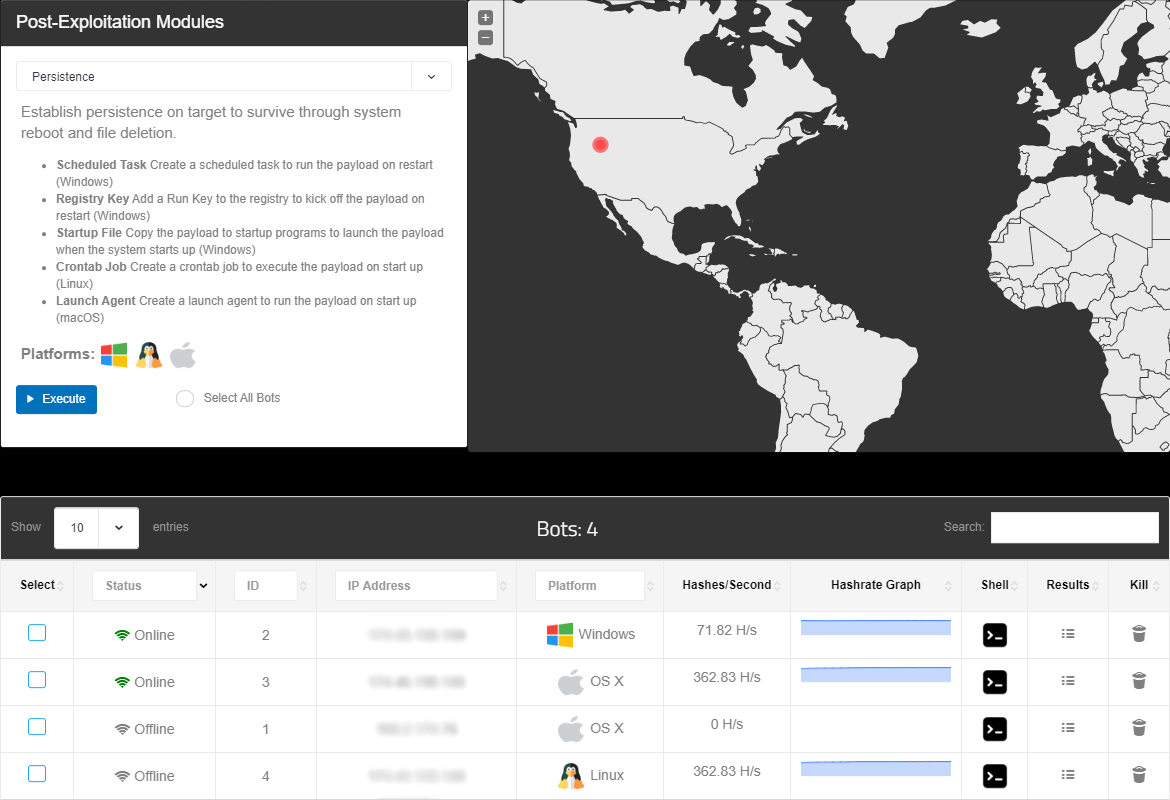
An open-source post-exploitation framework for students, researchers and developers.

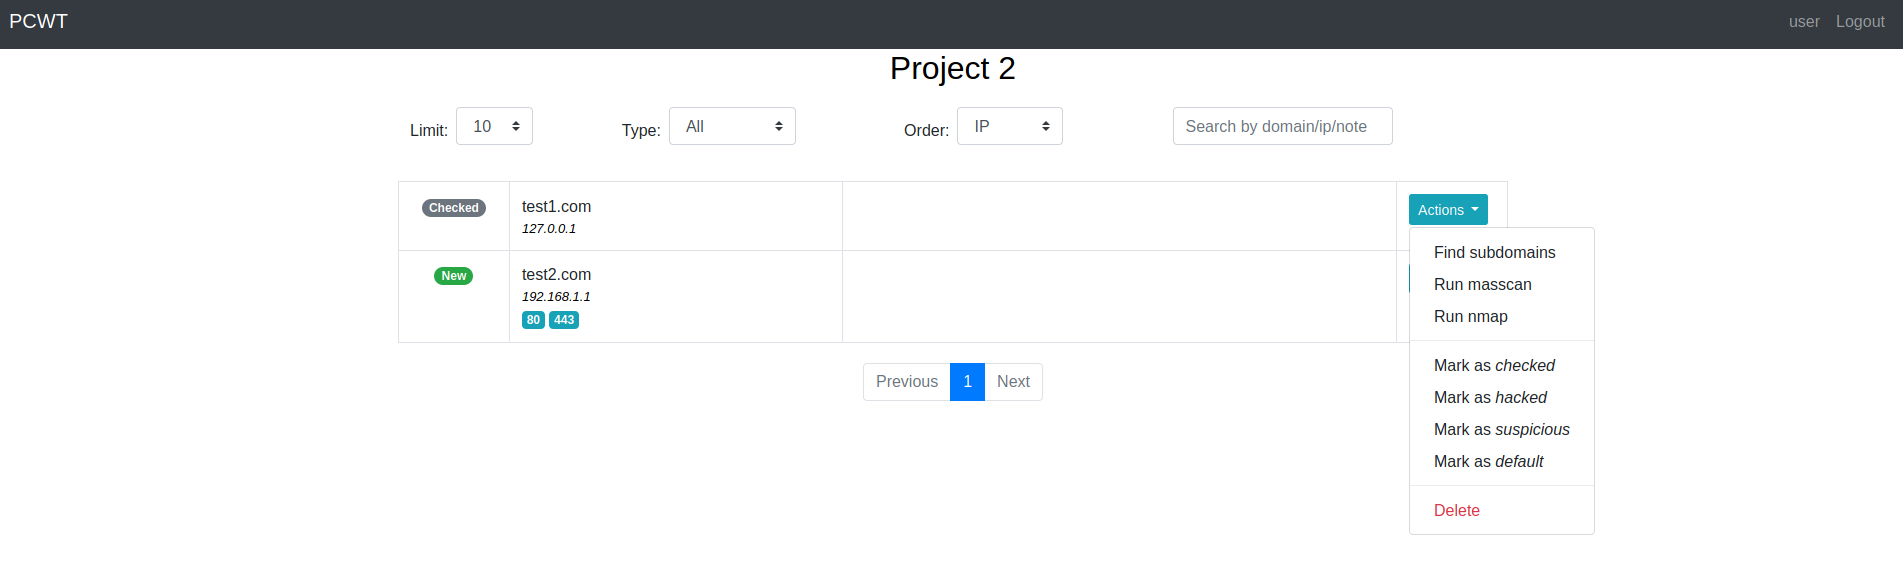
Web-based project management interface for penetration testing and bug bounty workflows, automating port scanning with Nmap/Masscan and subdomain…

This project is part of a school work focusing on network security.

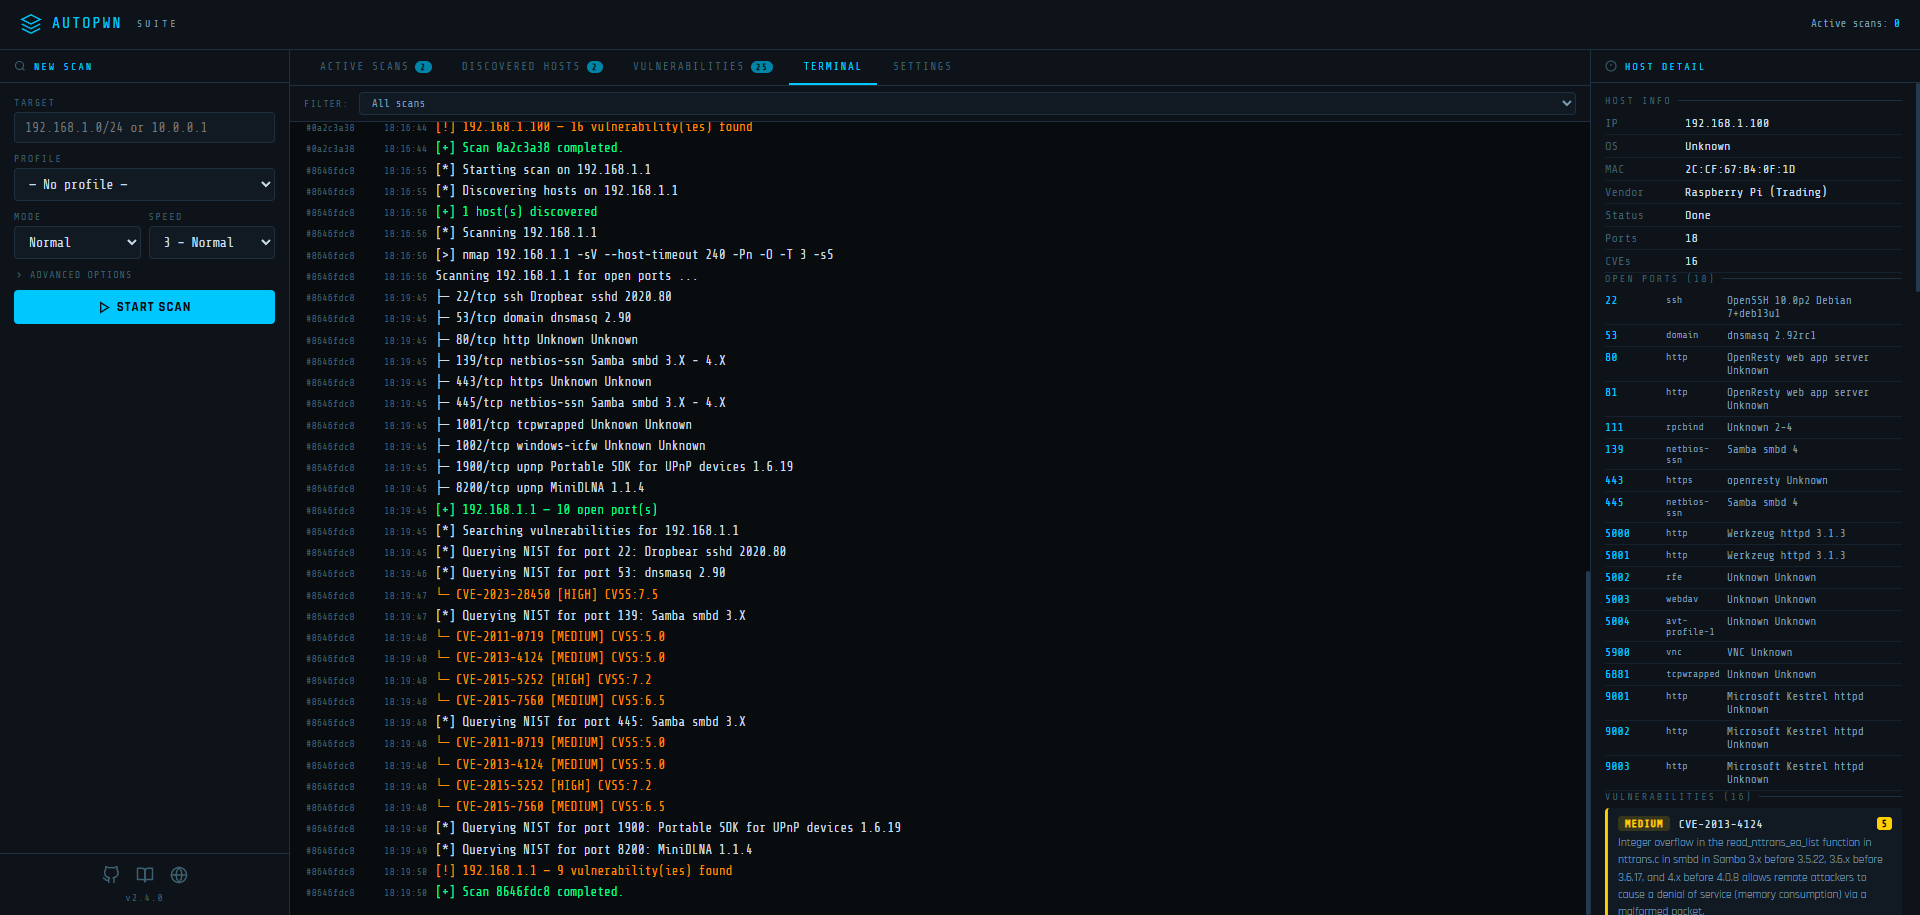
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.

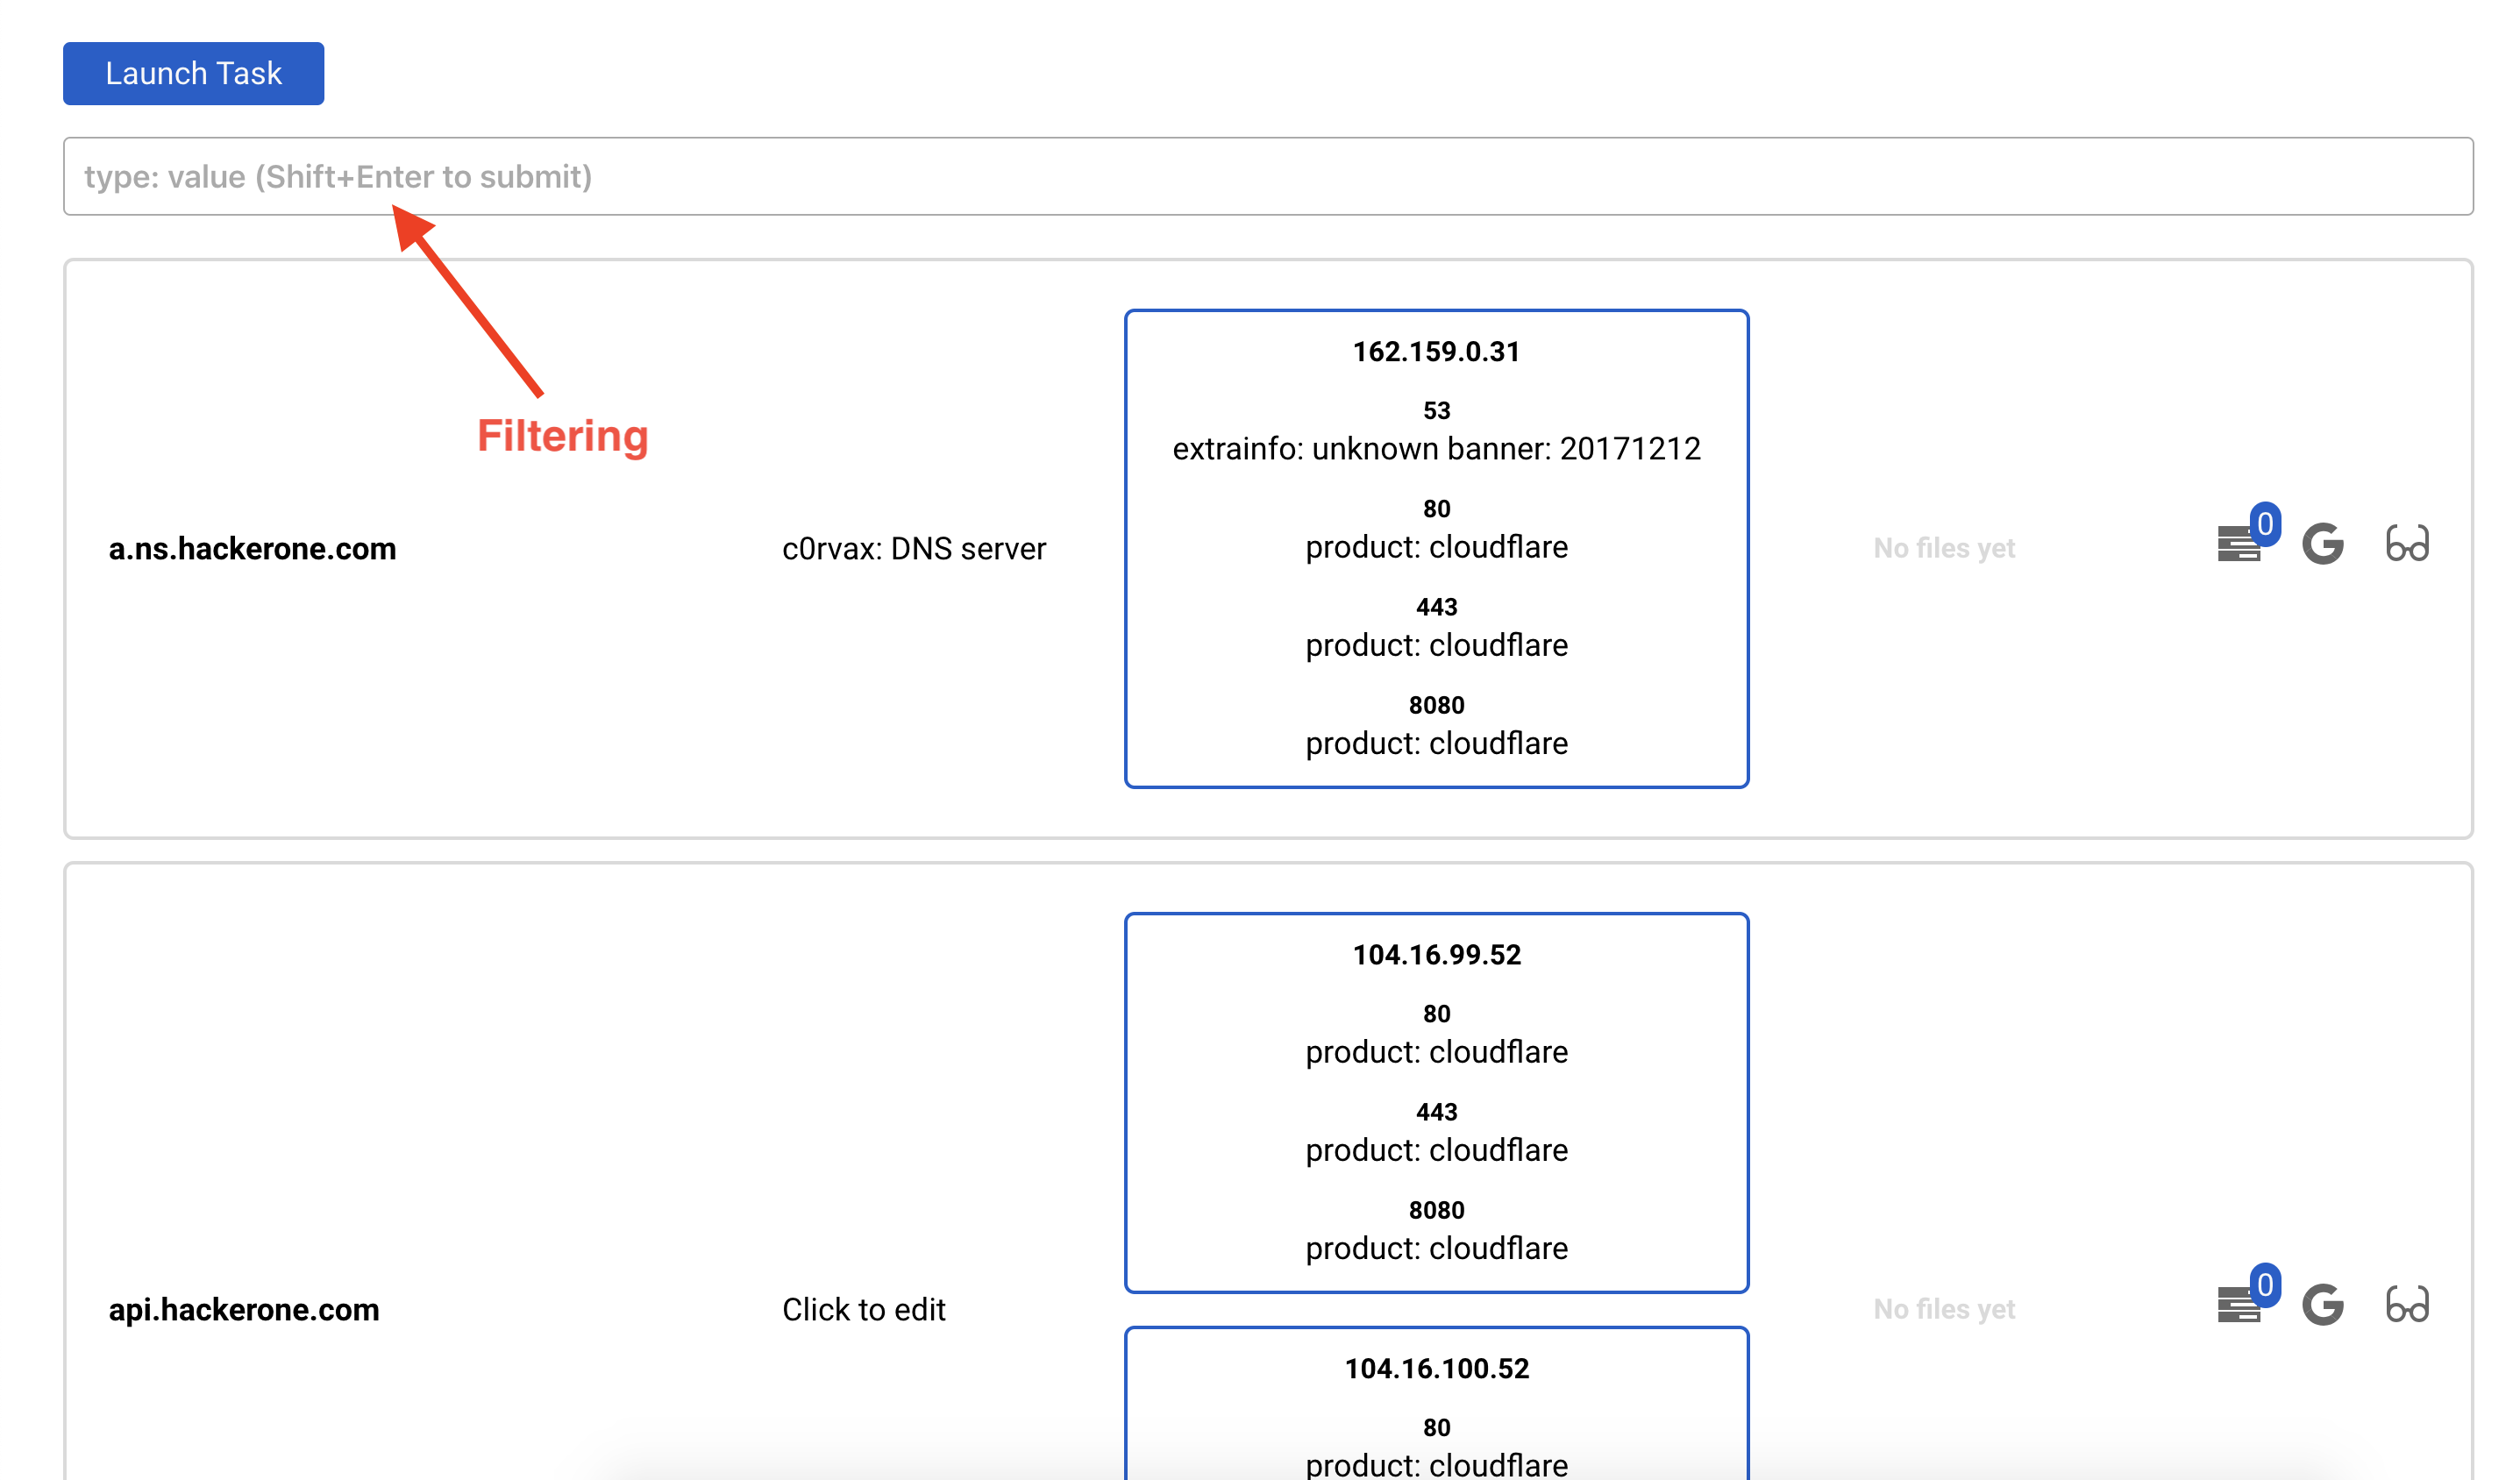
Pentest/BugBounty progress control with scanning modules

Automated, reproducible network security testing framework using Ansible and BATS to verify DNS, host availability, open ports, and TLS configuration…