
NtlmRelayToEWS
 arno0x/ntlmrelaytoews
ntlm relay attack to Exchange Web Services
email-securityexploitationinformation-gathering+4
arno0x/ntlmrelaytoewsntlm relay attack to Exchange Web Services
 mr-un1k0d3r/azureredops
Azure RedOps is a offensive security toolkit for assessing the security posture of Microsoft Entra ID
 tkcert/mail-security-tester
A testing framework for mail security and filtering solutions.
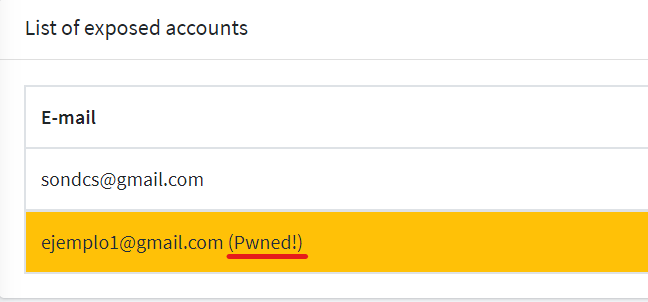 micro-joan/zphisher-gui-back_office
Real-time phishing campaign back-office plugin for Zphisher, capturing credentials, checking account exposure via haveibeenpwned, and evaluating…
 puliczek/cve-2021-21123-poc-google-chrome
🐱💻 👍 Google Chrome - File System Access API - vulnerabilities reported by Maciej Pulikowski | Total Bug Bounty Reward: $5.000 | CVE-2021-21123…
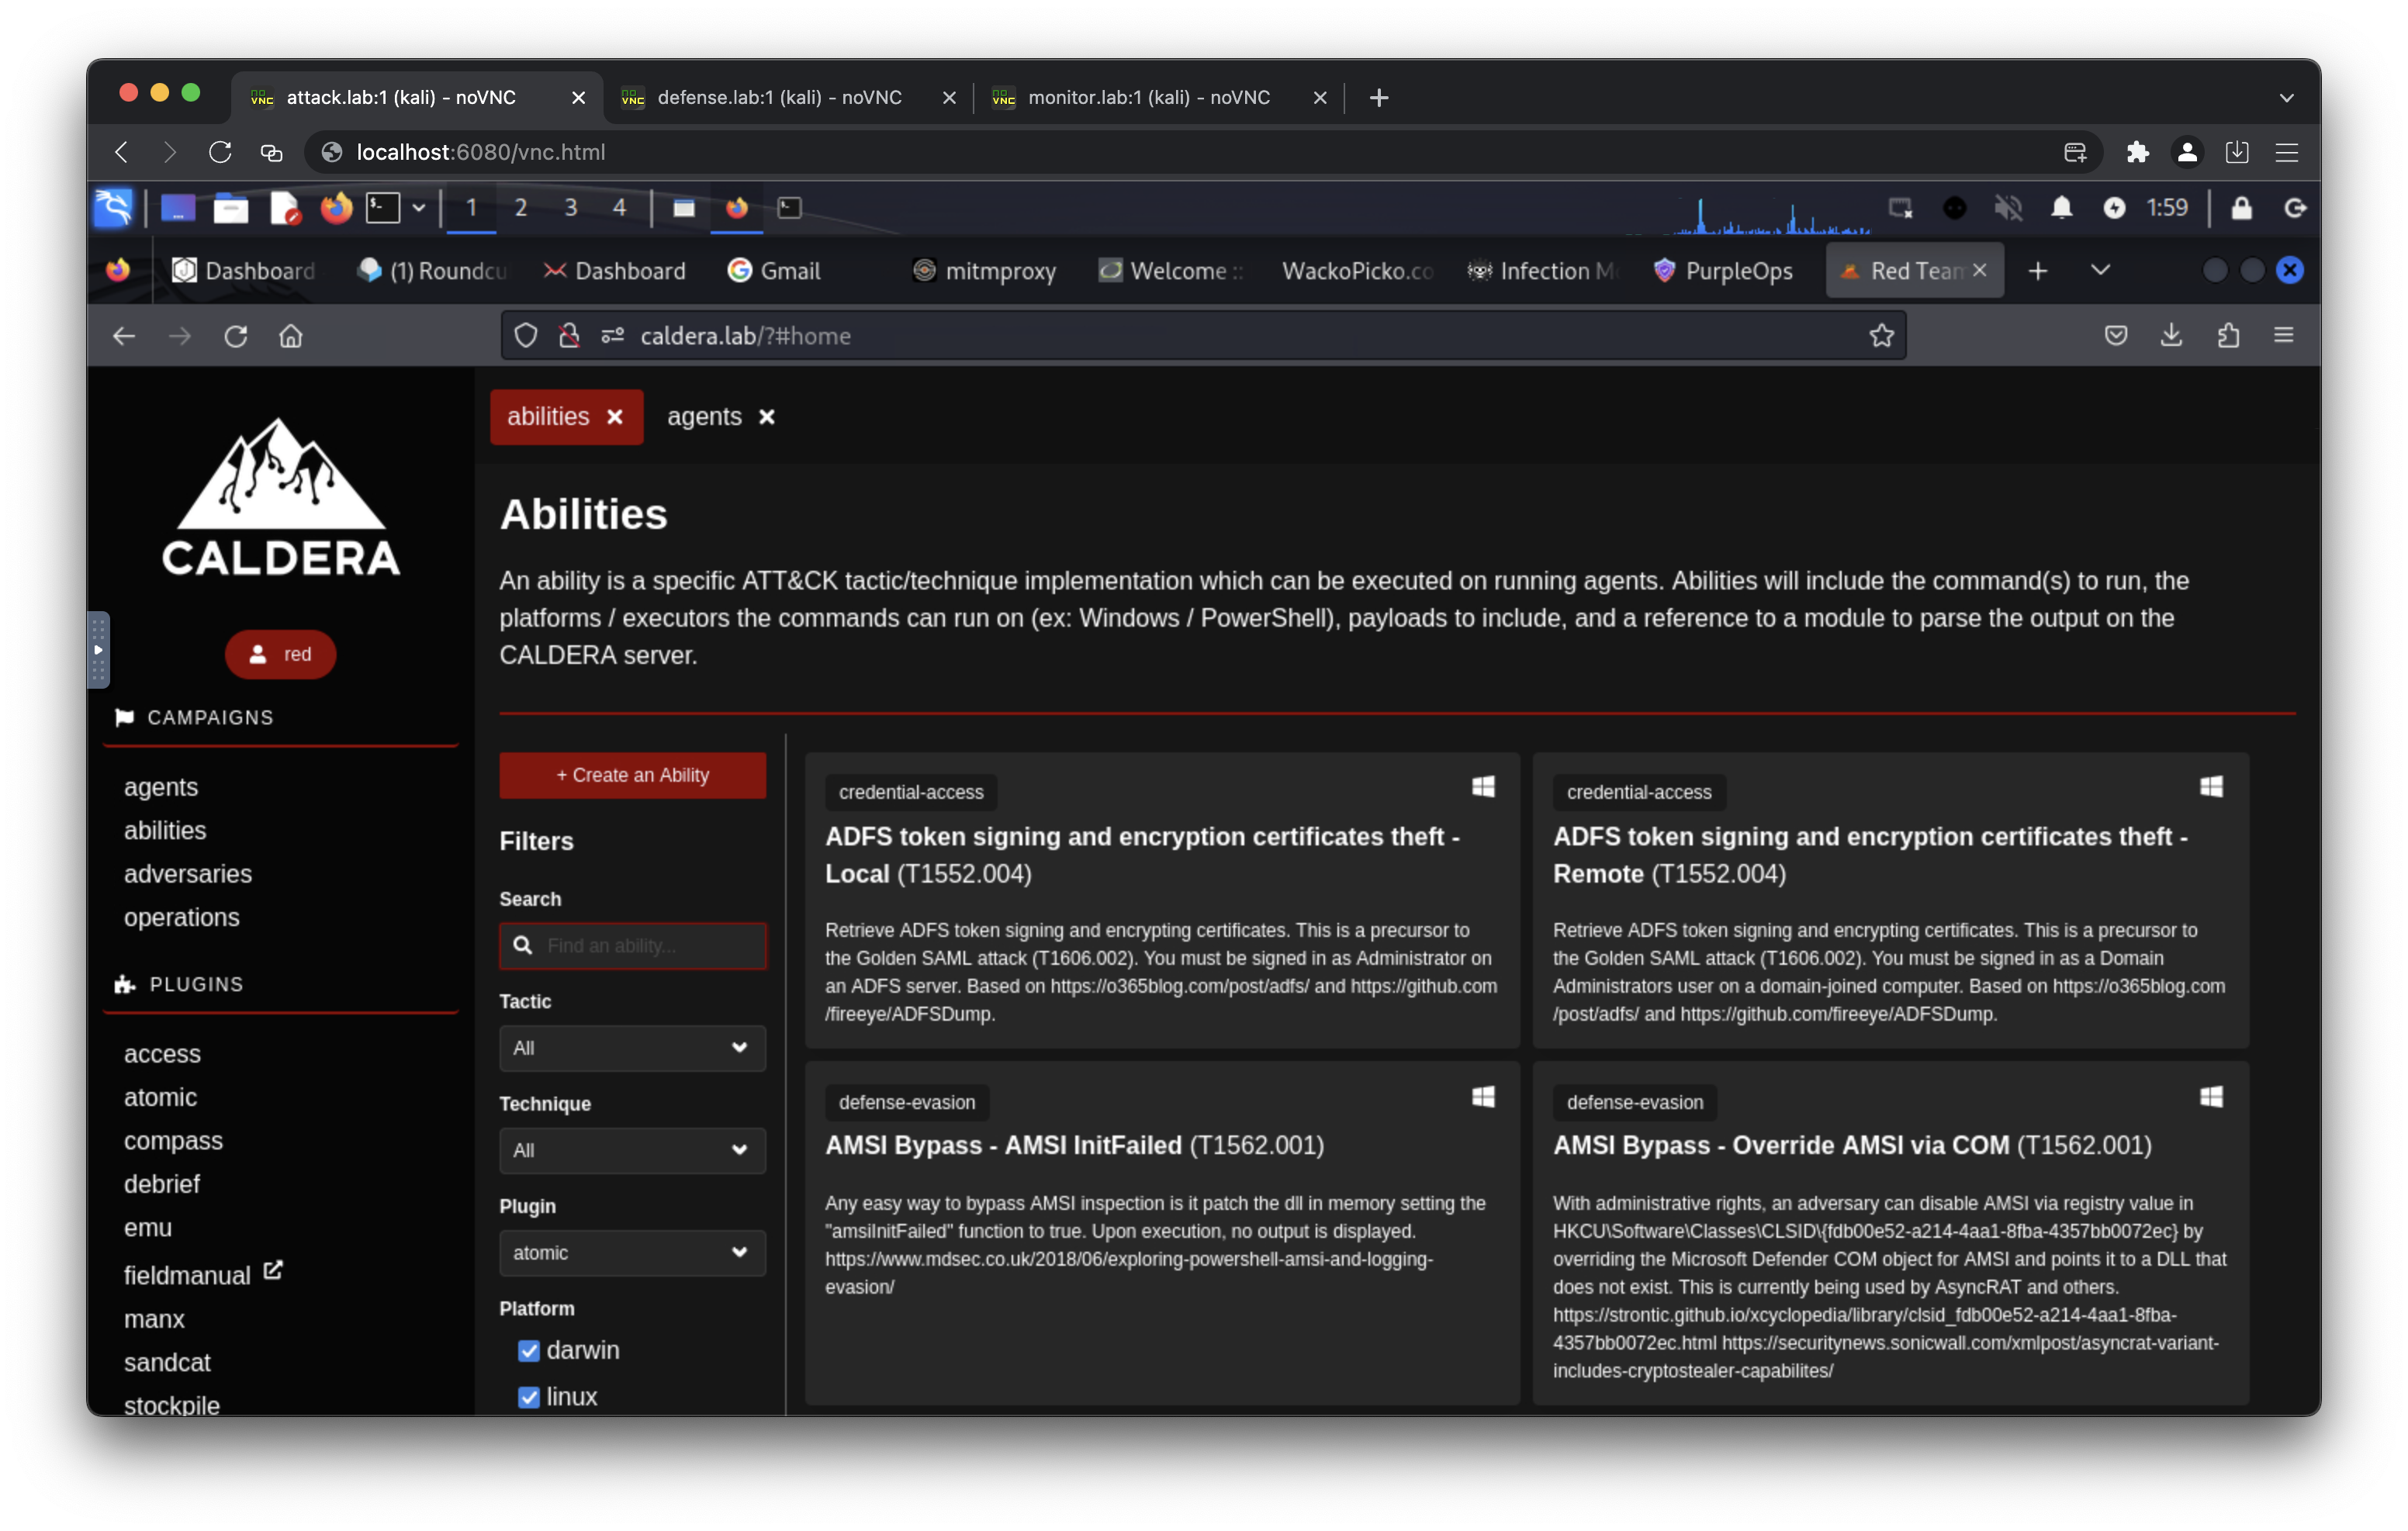
 g4lb1t/pstf2
Passive Security Tools Fingerprinting Framework
 cappricio-securities/camjacking
CamJacking is a tool designed for use in human penetration testing tool. It is intended to simulate potential security threats by testing the…
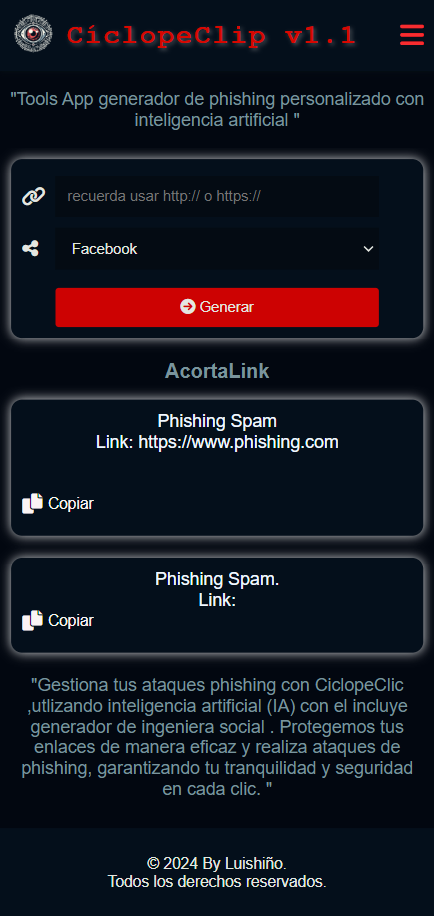 pericena/ciclopeclic
Security awareness training tool for authorized phishing simulations and internal IT audits
 nu11secur1ty/vulnerable-pdf
Educational PDF files demonstrating client-side exploitation techniques, including calculator execution and directory browsing, for security testing…
 dereeqw/web-mitm-lab
Web traffic interception simulation tool for cybersecurity research and defensive learning in isolated lab environments.
 segunakinsoyinu/cve-2024-42009-roundcube-xss
Stored XSS exploit for Roundcube Webmail ≤1.6.6 (CVE-2024-42009) with zero-click email exfiltration via CSS animation event handlers. Includes SMTP…
 dharmstm/cve-2026-30502-openkm-6.3.12-reflected-xss
Documentation and proof-of-concept for CVE-2026-30502, a reflected XSS vulnerability in OpenKM v6.3.12. Includes technical analysis, root cause,…
 asepsaepdin/cve-2010-1240
Educational proof-of-concept demonstrating how to embed a Meterpreter backdoor into a PDF file exploiting CVE-2010-1240, with step-by-step Metasploit…
 shacode/olyx
🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…
 spiderlabs/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 kgretzky/evilginx
PLEASE USE NEW VERSION: https://github.com/kgretzky/evilginx2
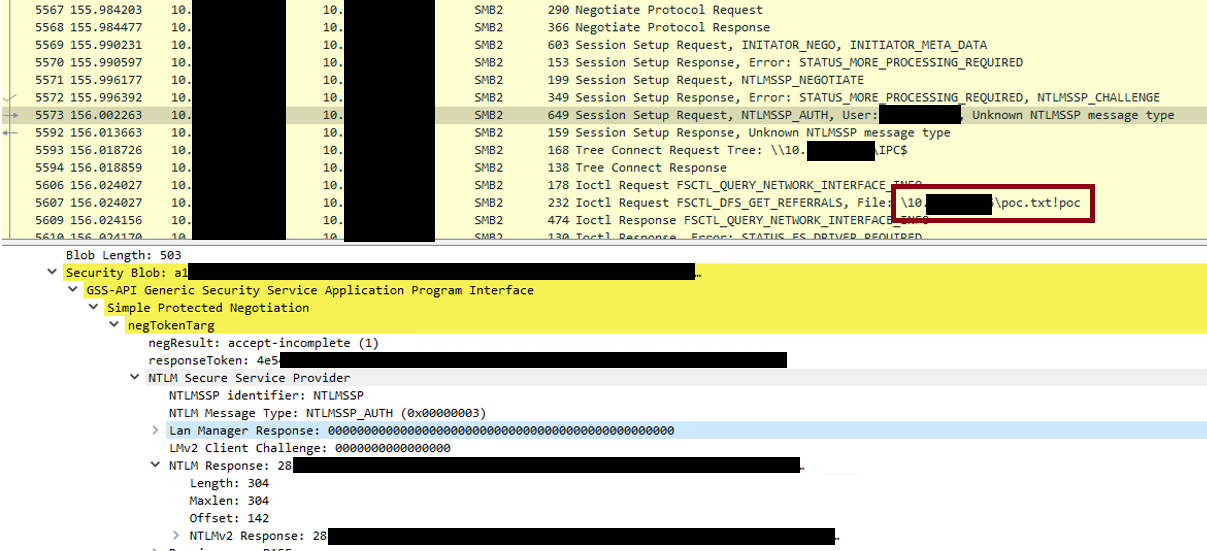 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability