
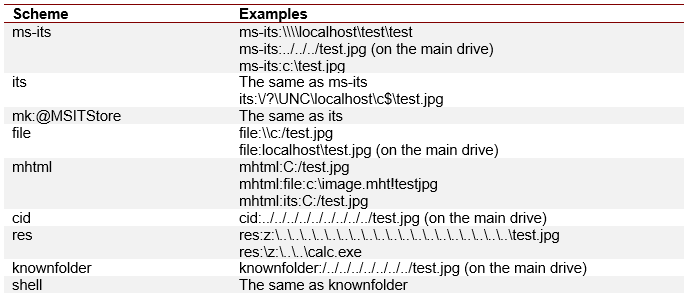
OutlookLeakTest
 nccgroup/outlookleaktest
The Outlook HTML Leak Test Project
data-exfiltrationemail-securityinformation-gathering+5
1298 years ago
nccgroup/outlookleaktestThe Outlook HTML Leak Test Project

 elvira-alec/fracture
FragAttacks WiFi penetration framework — CVE-2020-24586/87/88
 bhanunamikaze/cve-2024-42009
This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…
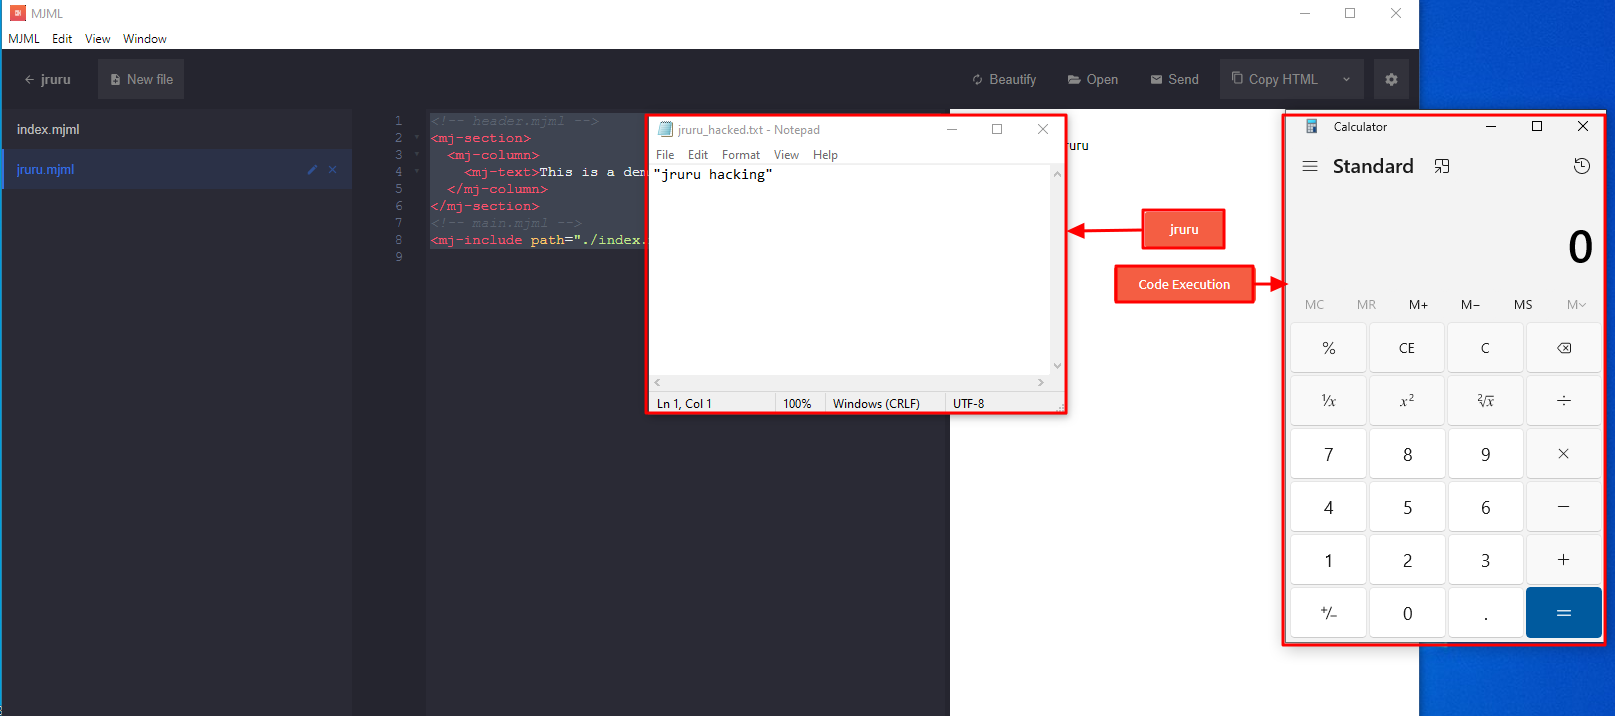 eqstlab/cve-2024-25293
mjml-app v3.0.4 & 3.1.0-beta RCE exploit
 mehulj94/radium
Python logger with multiple features.
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 mrd0x/bitb
HTML/CSS/JS templates for Browser-In-The-Browser phishing attacks, embedding fake login windows with customizable titles, domains, and phishing links…
 ustayready/credsniper
CredSniper is a phishing framework written with the Python micro-framework Flask and Jinja2 templating which supports capturing 2FA tokens.
 arno0x/embedinhtml
Embed and hide any file in an HTML file
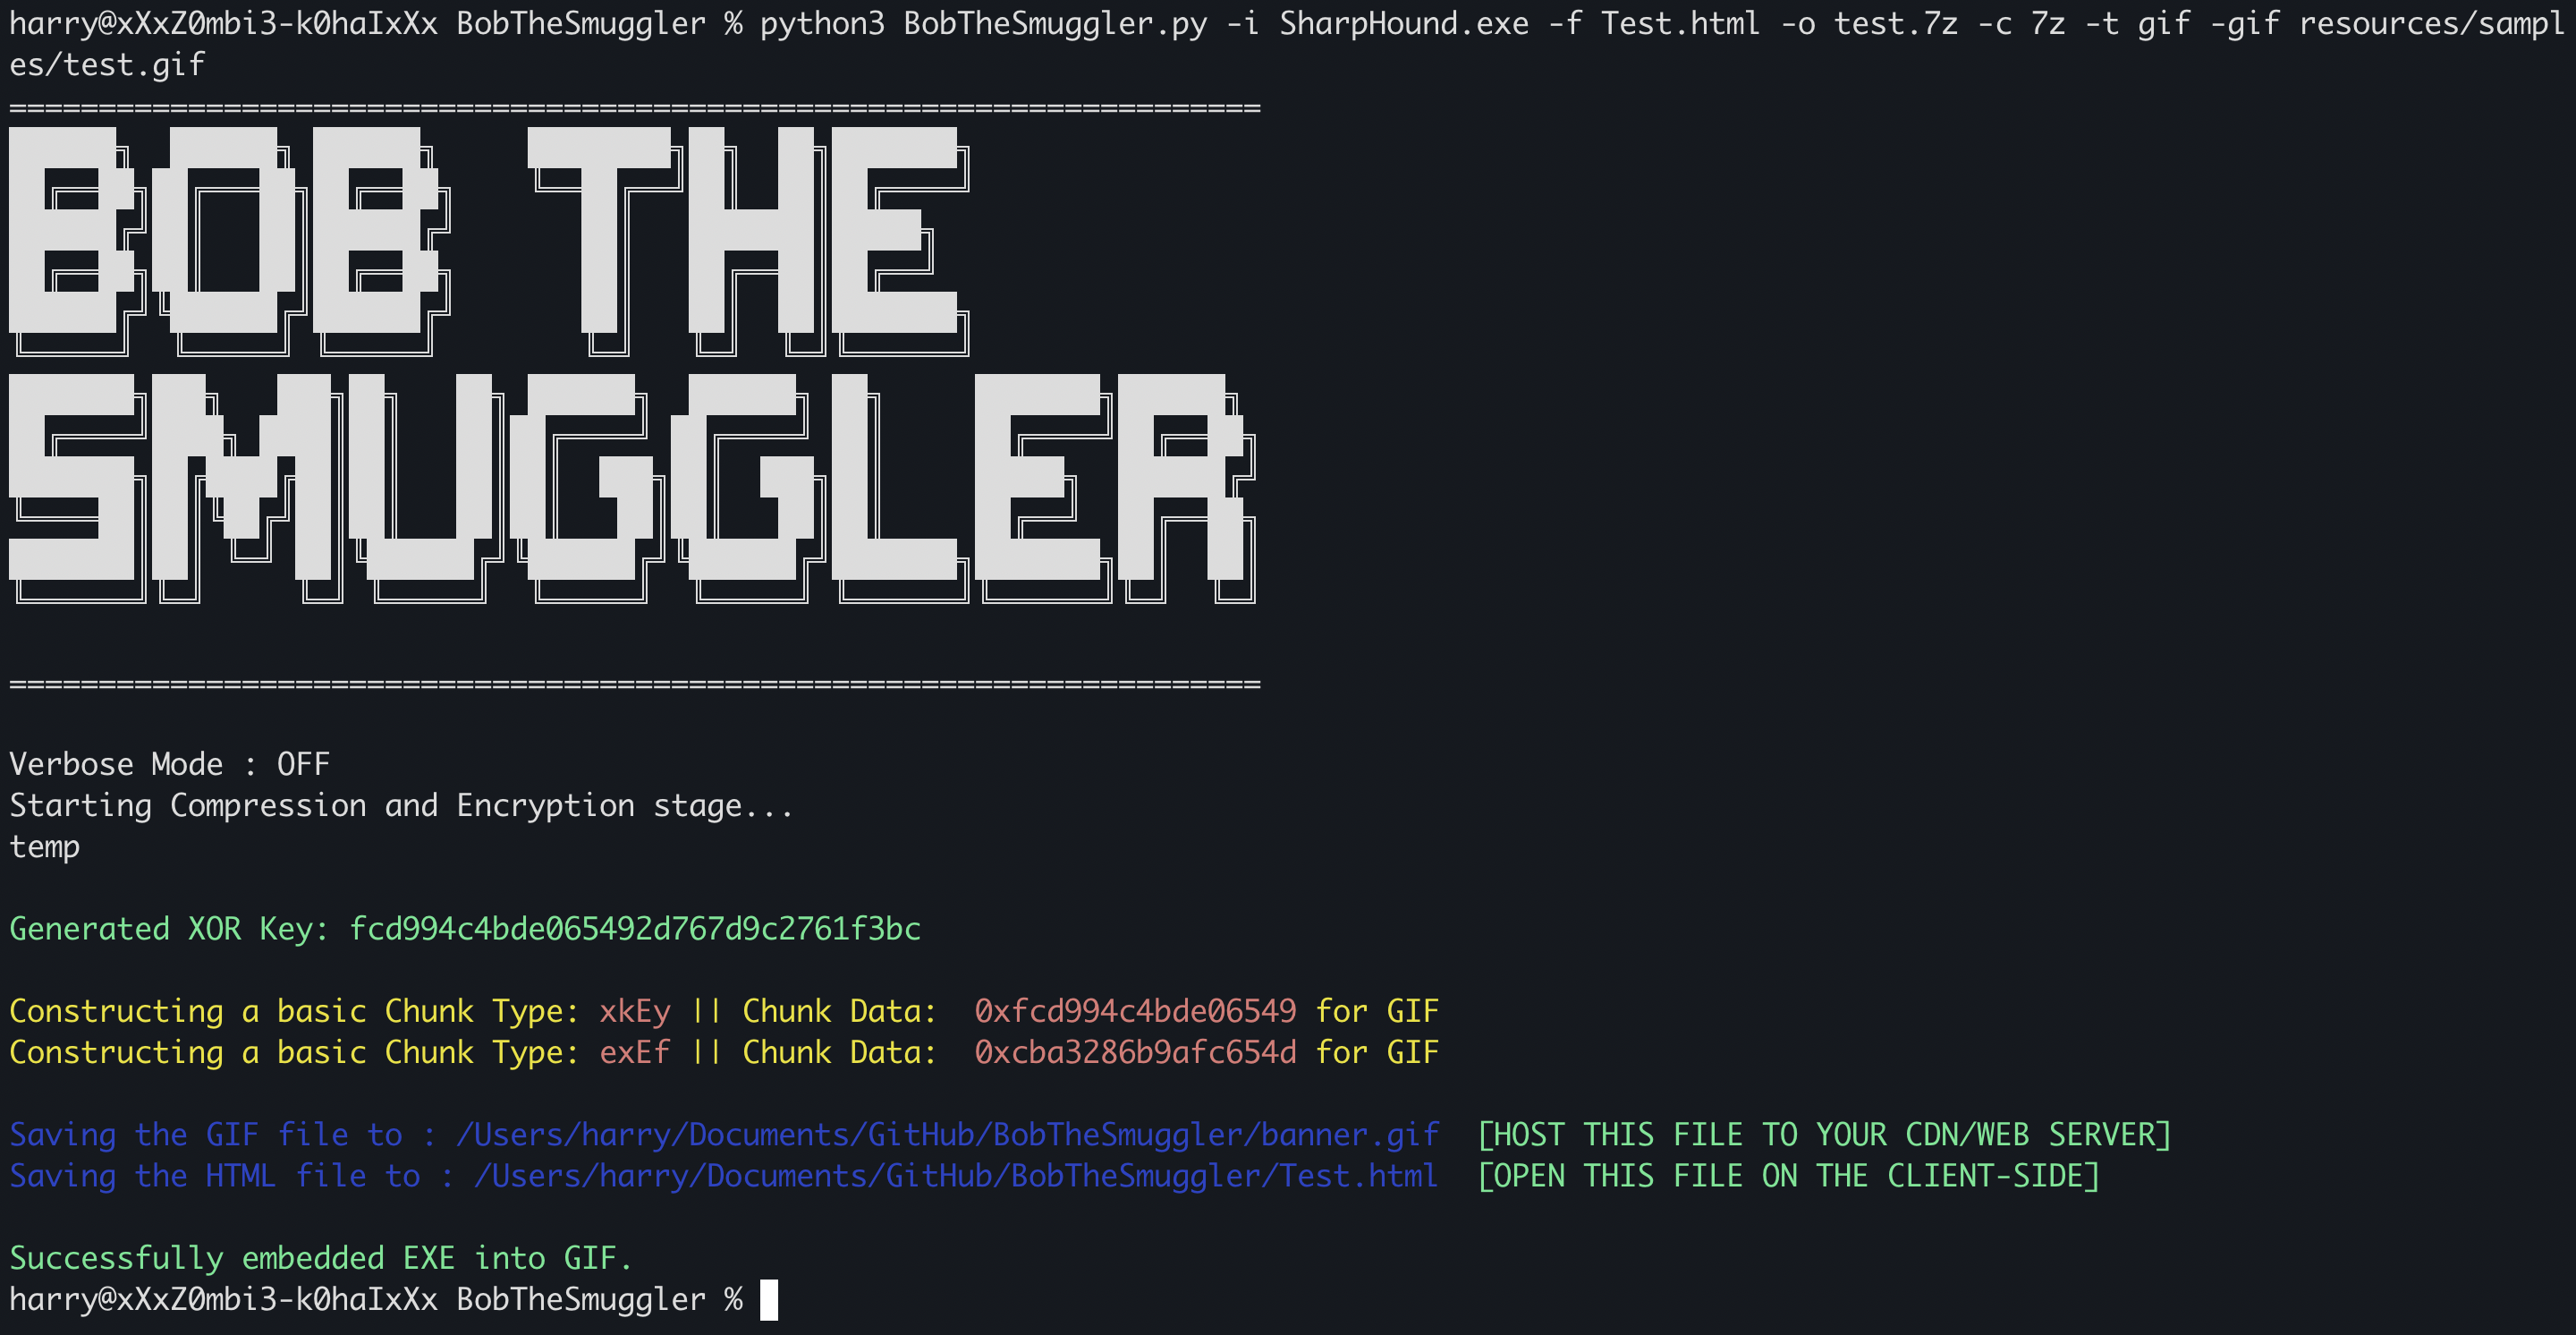 thecyb3ralpha/bobthesmuggler
"Bob the Smuggler": A tool that leverages HTML Smuggling Attack and allows you to create HTML files with embedded 7z/zip archives. The tool would…
 waelmas/frameless-bitb
A new approach to Browser In The Browser (BITB) without the use of iframes, allowing the bypass of traditional framebusters implemented by login…
 komomon/cve-2022-30190-follina-office-msdt-fixed
Modified CVE-2022-30190 exploit tool for MS-MSDT Office RCE with custom docx template support, binary/command execution modes, and embedded HTTP…
 jimywork/cromos
Cromos is a tool for downloading legitimate extensions of the Chrome Web Store and inject codes in the background of the application.
 puliczek/cve-2021-21123-poc-google-chrome
🐱💻 👍 Google Chrome - File System Access API - vulnerabilities reported by Maciej Pulikowski | Total Bug Bounty Reward: $5.000 | CVE-2021-21123…
 reverseclabs/cve-2021-25374_samsung-account-access
This script can be used to gain access to a victim's Samsung Account if they have a specific version of Samsung Members installed on their Samsung…
 jakabakos/cve-2023-36884-ms-office-html-rce
MS Office and Windows HTML RCE (CVE-2023-36884) - PoC and exploit