
CVE-2025-1306
 nxploited/cve-2025-1306
Newscrunch <= 1.8.4 - Cross-Site Request Forgery to Arbitrary File Upload
educationexploitationpayload-generation+2
51 year ago
nxploited/cve-2025-1306Newscrunch <= 1.8.4 - Cross-Site Request Forgery to Arbitrary File Upload
 mnqazi/cve-2023-33977
Read more at Medium
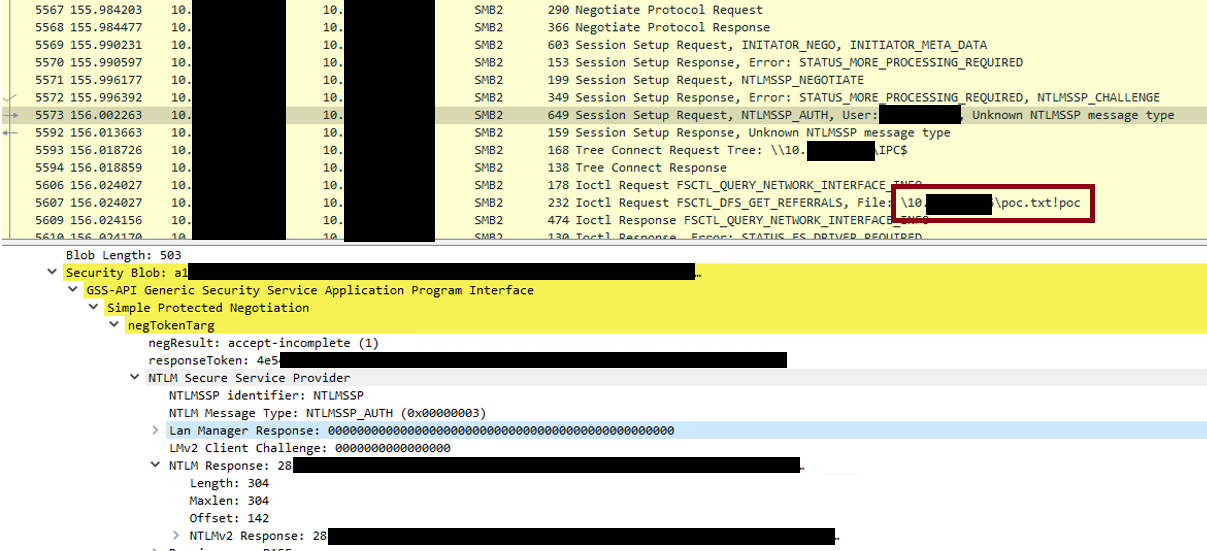 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability
 trackflaw/cve-2023-23397
Simple PoC of the CVE-2023-23397 vulnerability with the payload sent by email.
 0xflagplz/ms-msdt-office-rce-follina
CVE-2022-30190 | MS-MSDT Follina One Click
 absholi7ly/microsoft-edge-information-disclosure
CVE-2024-30056 Microsoft Edge (Chromium-based) Information Disclosure Vulnerability
 bartfroklage/cve-2024-37383-poc
Proof of concept for CVE-2024-37383
 minhhk68/cve-2026-13156
CVE-2026-13156 Vulnerability Advisory & PoC — Discovered by Huynh Kien Minh (MinhHK).
 exfil0/weaponizing-cve-2024-4367
CVE-2024-4367 is a critical vulnerability (CVSS 9.8) in PDF.js, allowing arbitrary JavaScript code execution due to insufficient type checks on the…
 dharmstm/cve-2026-30502-openkm-6.3.12-reflected-xss
Documentation and proof-of-concept for CVE-2026-30502, a reflected XSS vulnerability in OpenKM v6.3.12. Includes technical analysis, root cause,…
 lewis-ricardo/amaranth-project
CVE-2025-8088 exploitation chain + Quasar C2 multi-stage payload delivery
 moneertv/cve-2023-23397
CVE-2023-23397 C# PoC
 zzn1nj4/cve-2025-22131-poc
PoC for CVE-2025-22131
 roj1py/cve-2024-47875-phpspreadsheet-xss-poc
This is a PoC/Exploit for the CVE-2024-47875 PhpSpreadsheet XSS Vuln
 b0marek/cve-2023-4549
Repository for CVE-2023-4549 vulnerability.
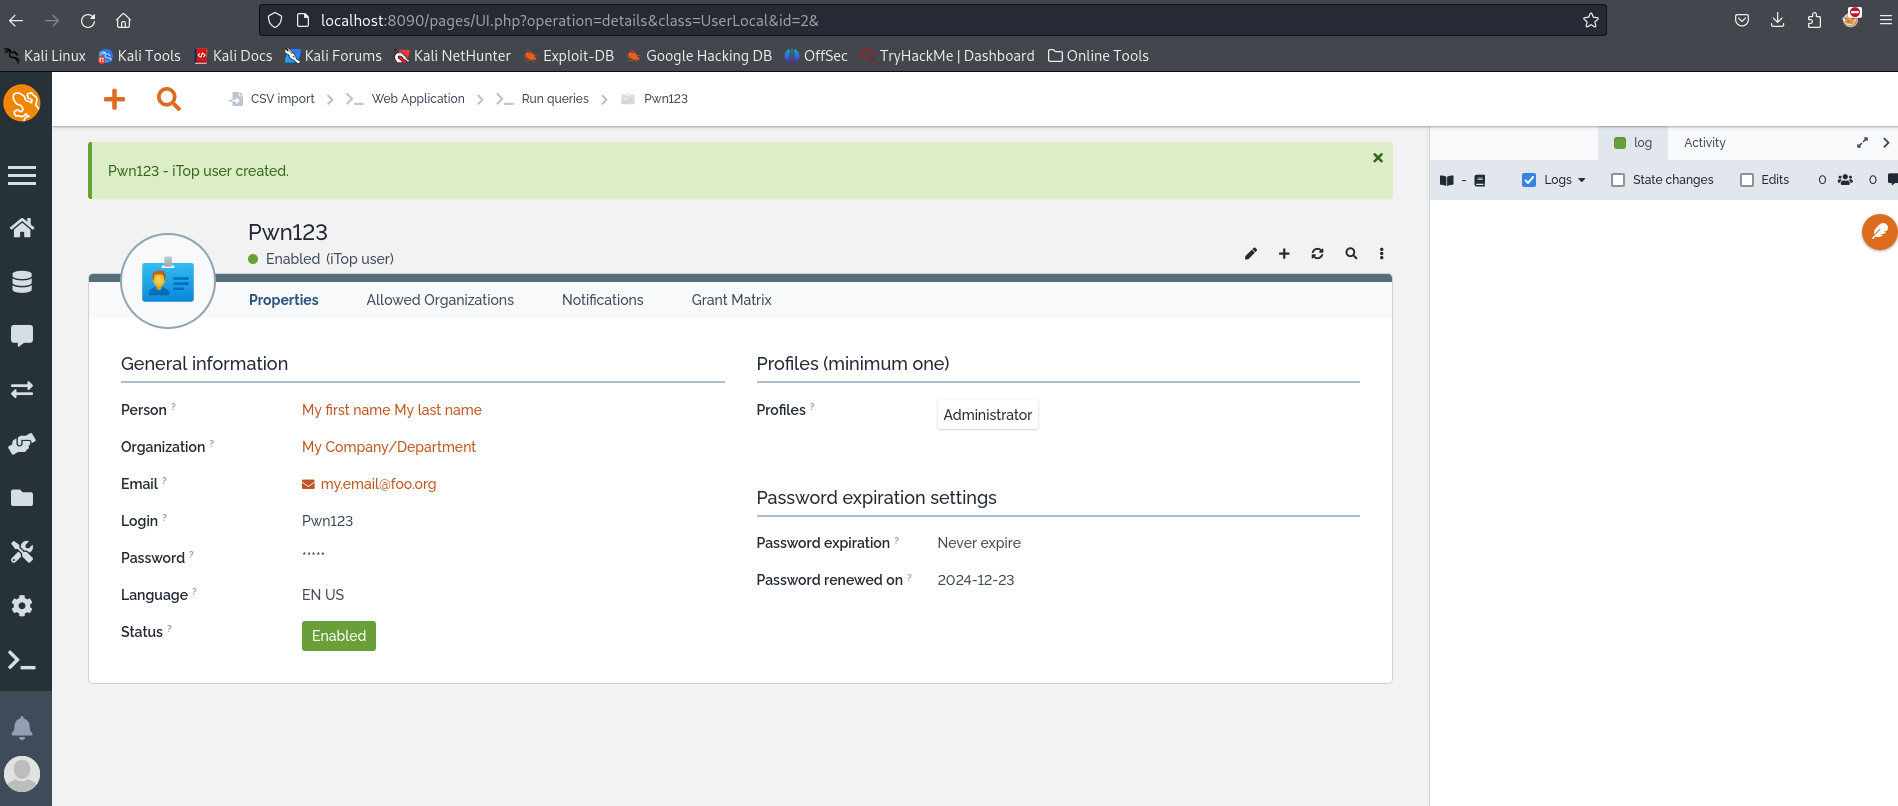 harshit-mashru/itop-cves-exploit
This repository contains exploits for iTOP CVE-2024-52002, 52000, 31998, 31448 that involve CSRF+XSS chaining to get RCE
 jmousqueton/poc-cve-2022-30190
POC CVE-2022-30190 : CVE 0-day MS Offic RCE aka msdt follina
 raffli-dev/cve-2023-41425
Exploit for Wonder CMS XSS to RCE (CVE-2023-41425) with theme upload and reverse shell payloads.