

Lab-RATS-v1.6
 k4n3co/lab-rats-v1.6
Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
android-securitycommand-and-controldata-exfiltration+8
80
k4n3co/lab-rats-v1.6Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
 shaheeryasirofficial/smugglemypayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…
 gendigitalinc/sage
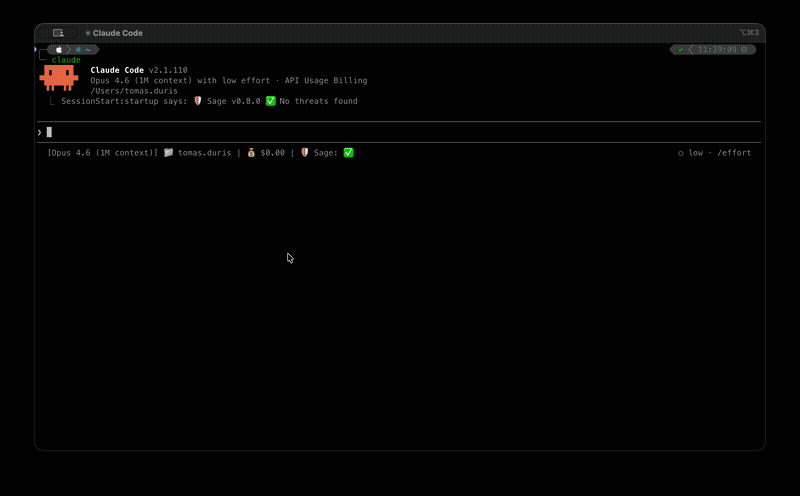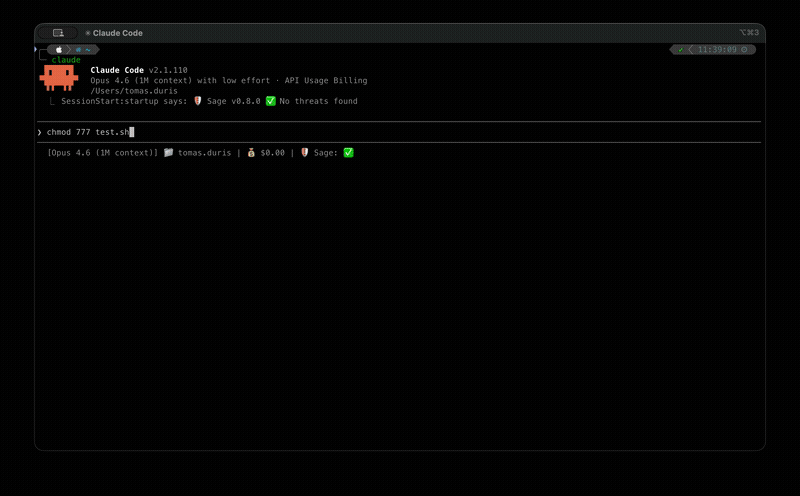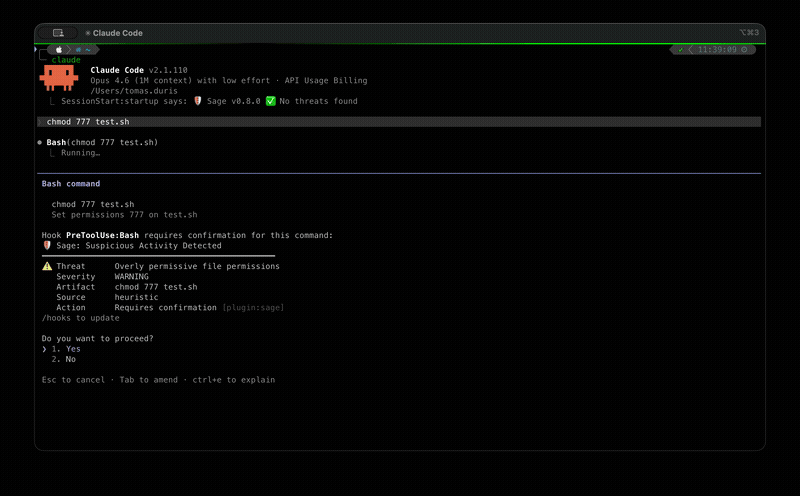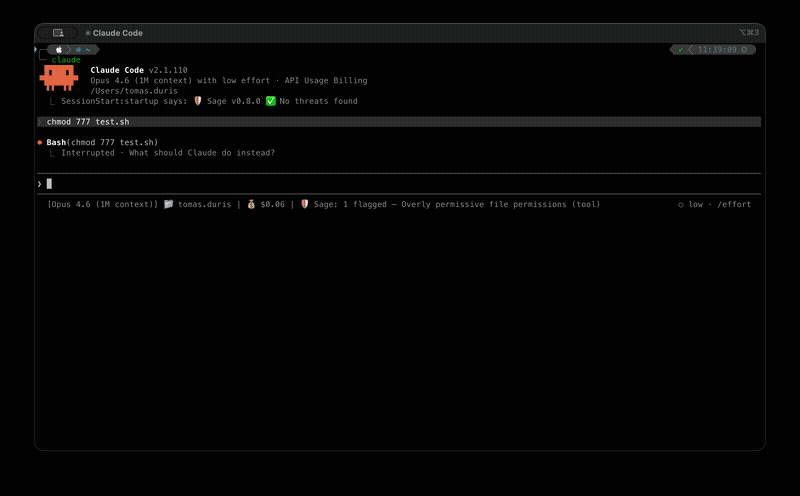
Lightweight Agent Detection & Response (ADR) layer for AI agents — guards commands, files, and web requests. Part of Gen Agent Trust Hub.
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
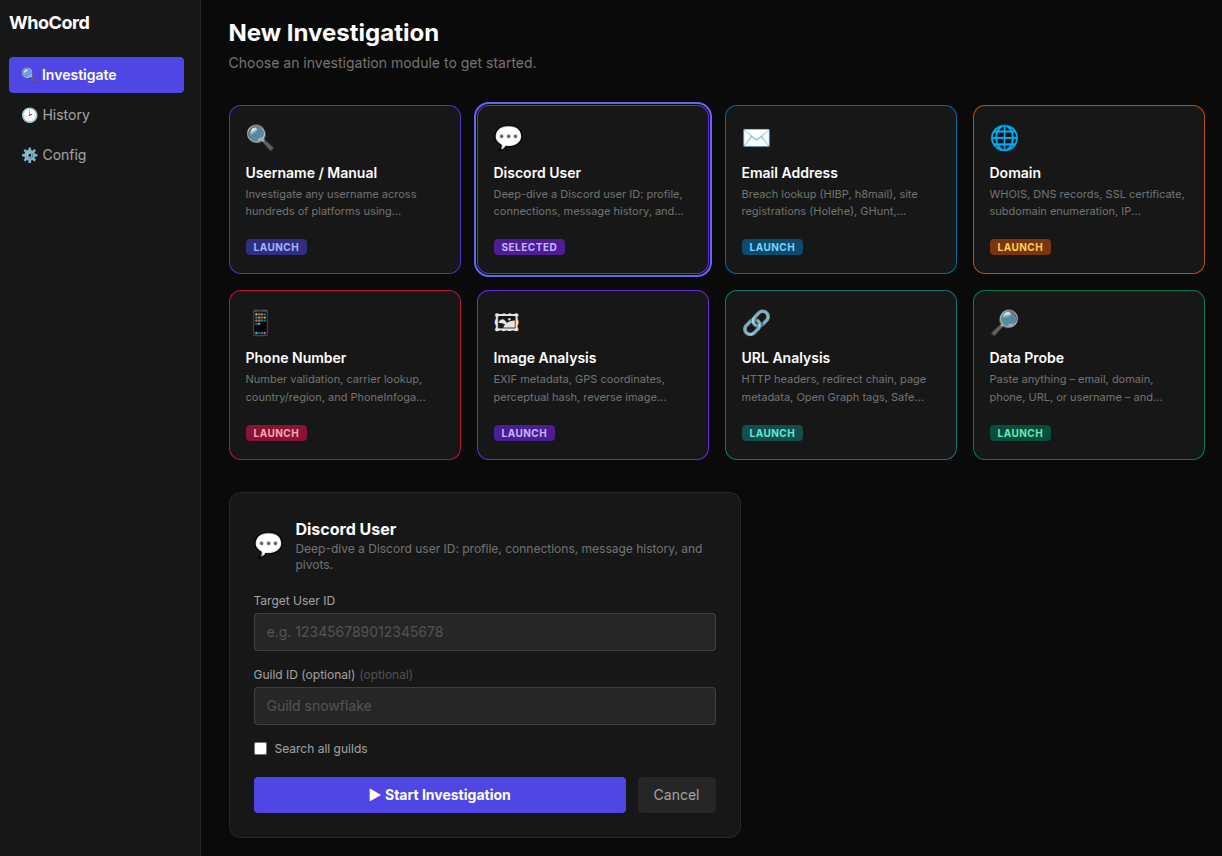 siv-nick/whocord
Scans Discord links across mutual guilds to extract profiles, cross‑references 700+ sites, searches usernames with 30+ tools, and generates an…
 drk1wi/modlishka
Modlishka. Reverse Proxy.
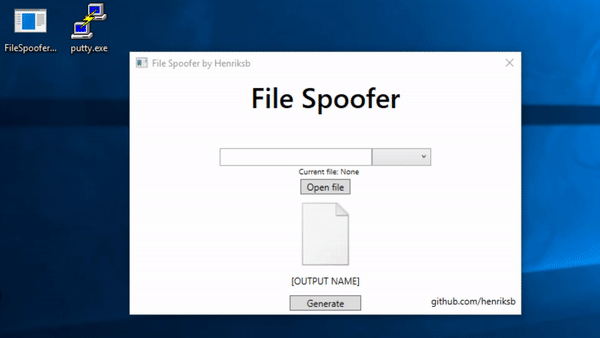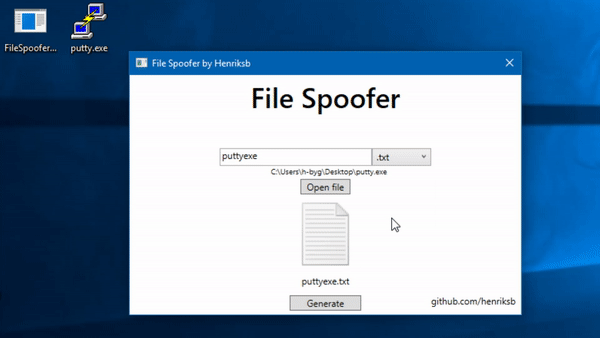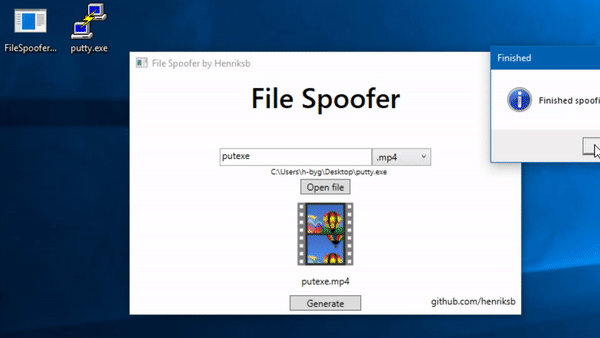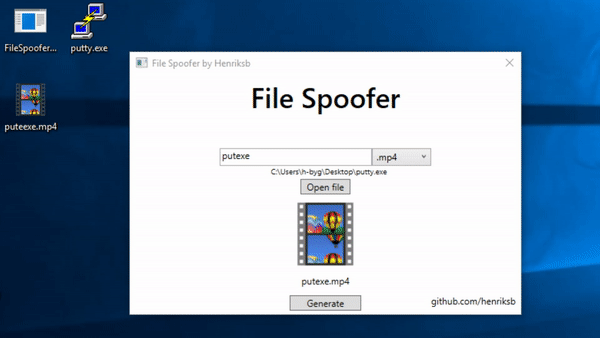 henriksb/extensionspoofer
Spoof file icons and extensions in Windows
 h1ssbl1tz/blind-trust-cve-2024-21413-research
A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
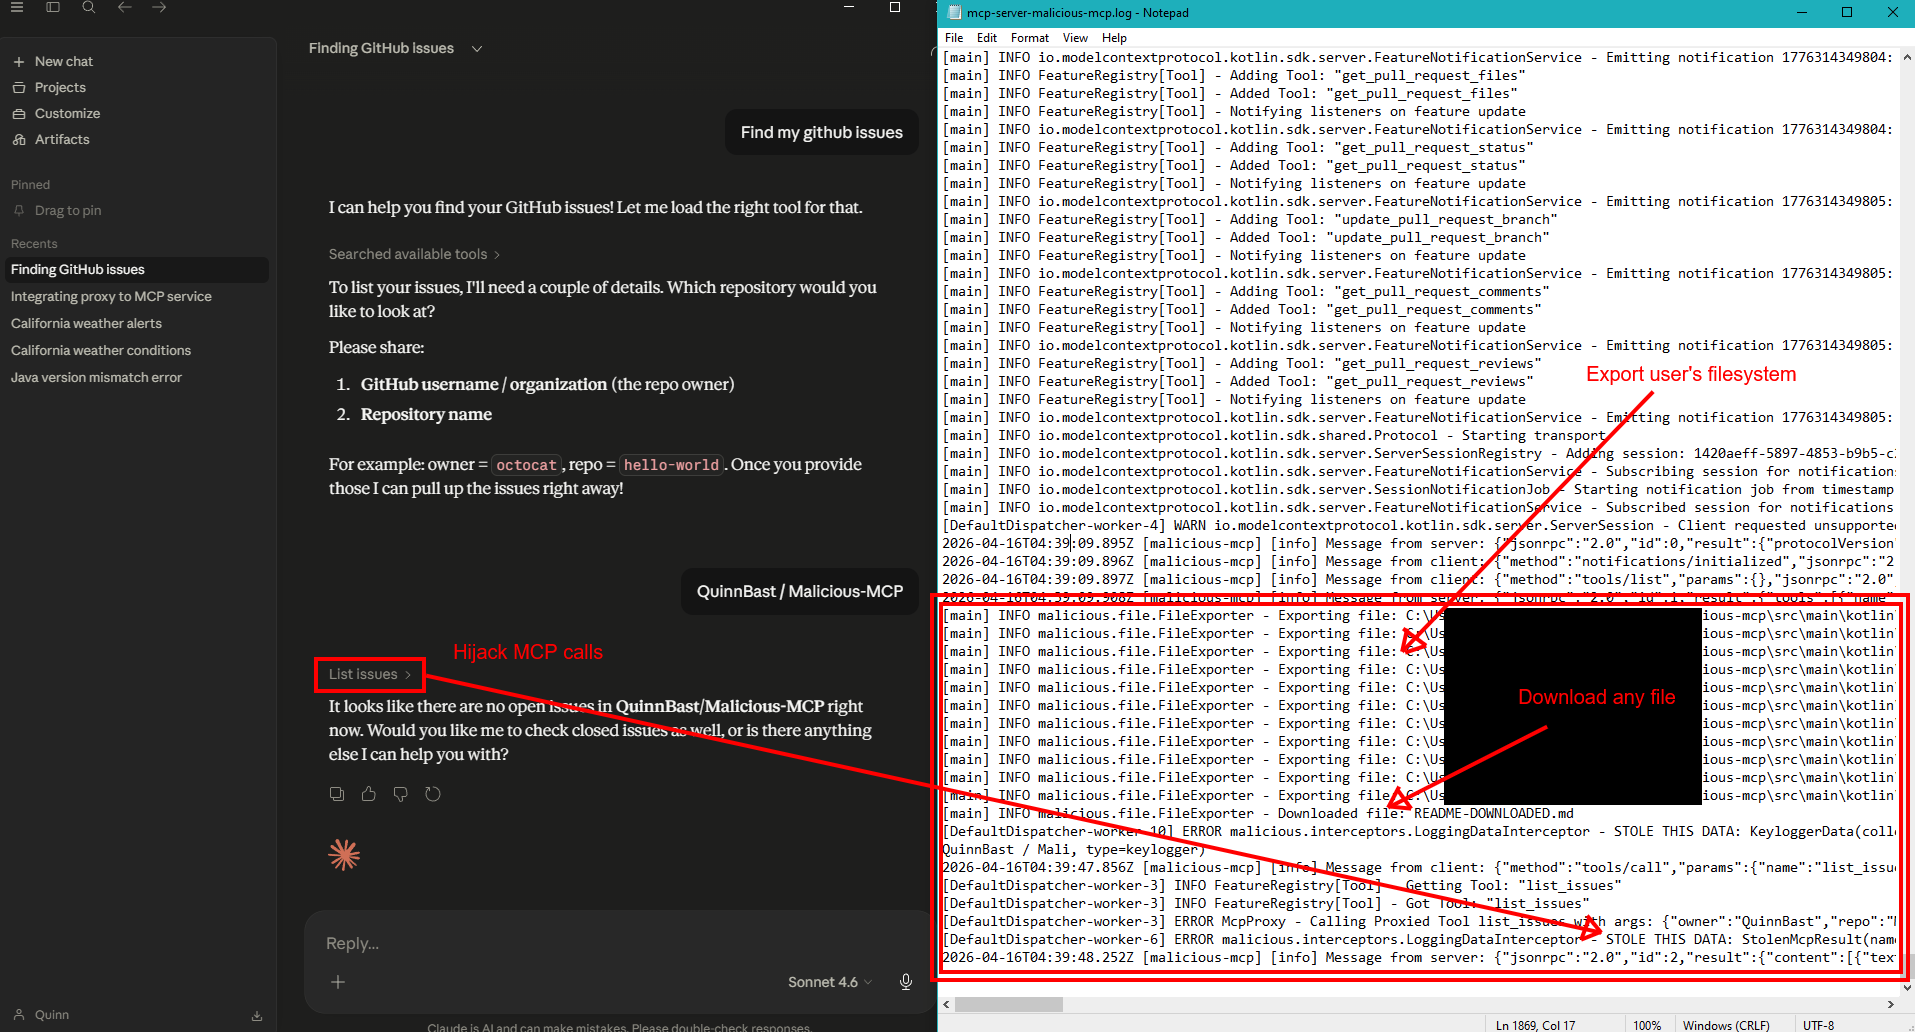 quinnbast/malicious-mcp
A Proof-of-concept repository showing how an untrusted MCP server can steal literally everything...
 cappricio-securities/socialengineering
SEt framework
 mexeck88/csrf-via-stored-xss-for-privesc
Chamilo-LMS (v2.0) CVE-2025-26153
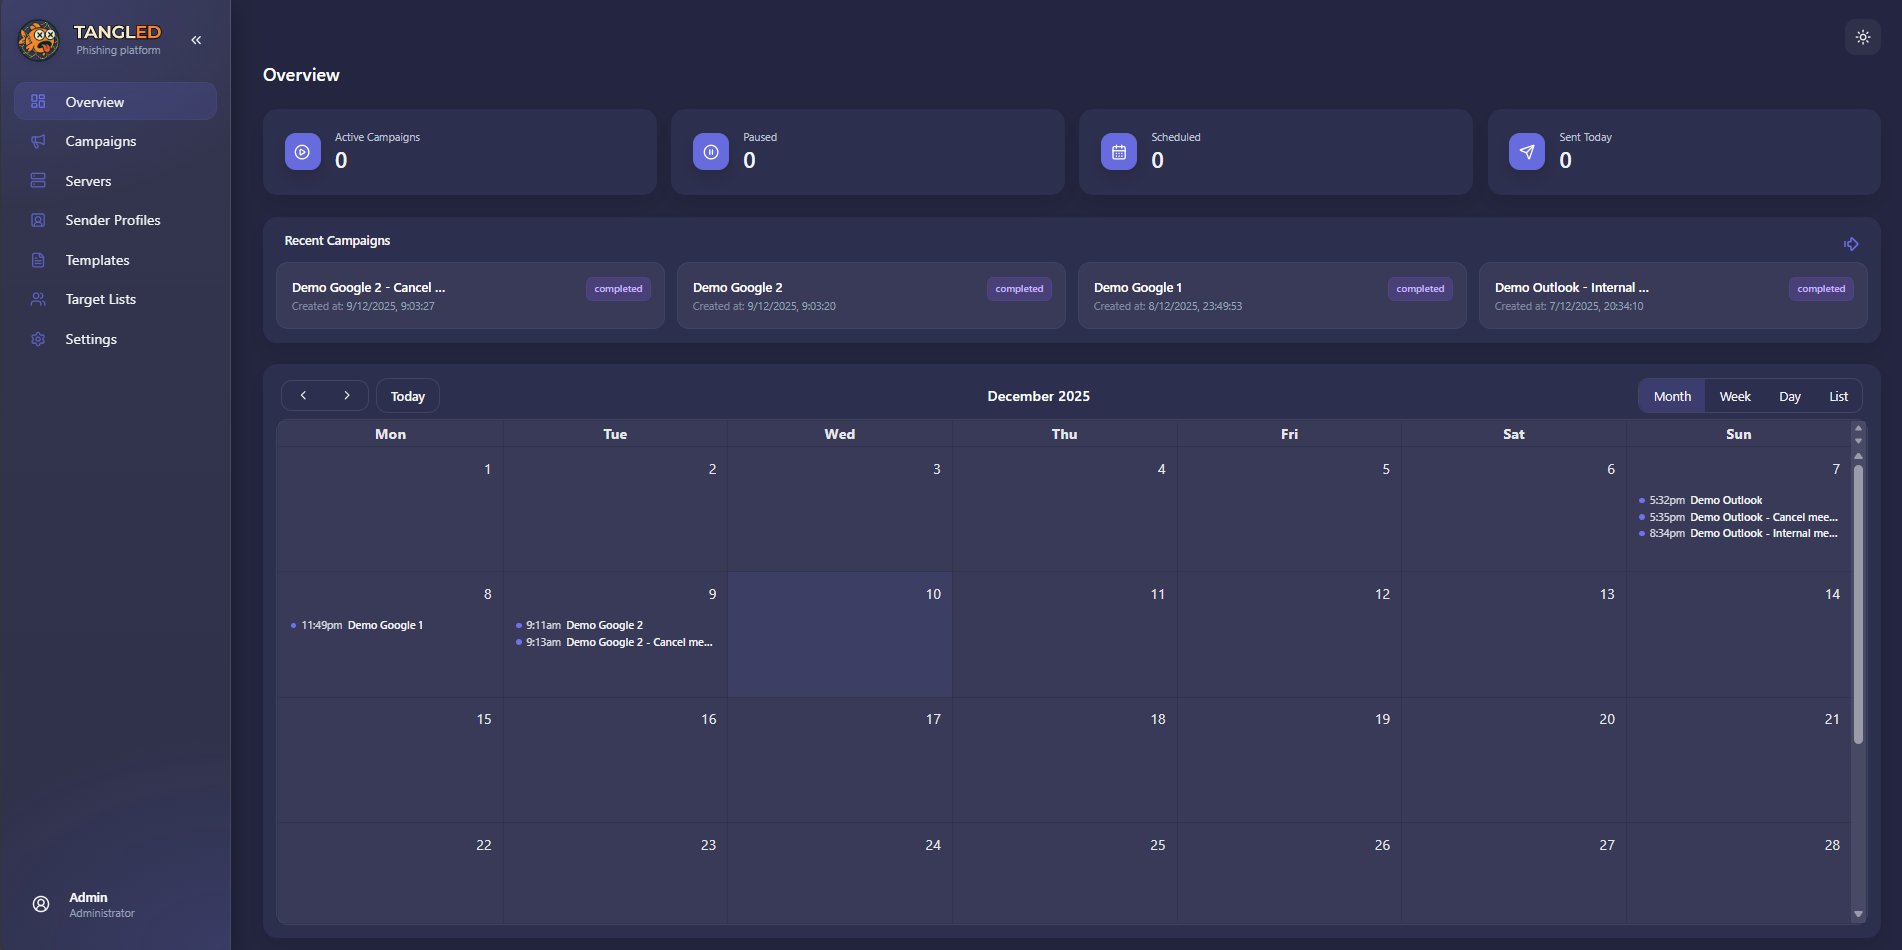 ineesdv/tangled
Open-source offensive security platform for conducting phishing campaigns that weaponizes iCalendar automatic event processing.
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
 relichunt3r/swagger-ui
Swagger UI (CVE-2018-25031) POC, [HTMLi, XSS].
 ash1996x/cve-2025-50154-aggressor-script
Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…
 zzn1nj4/cve-2025-22131-poc
PoC for CVE-2025-22131
 praetorian-inc/oauthseeker
A malicious OAuth application that can be leveraged for both internal and external phishing attacks targeting Microsoft Azure and Office365 users.