
FullscreenBrowserPhishing
 gmh5225/fullscreenbrowserphishing
PoC of the phishing through setting browser in the fullscreen mode
educationphishingphishing-tools+3
gmh5225/fullscreenbrowserphishingPoC of the phishing through setting browser in the fullscreen mode
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 samsayen/jqueryingu
Valid JQuery that profiles the system and returns info to the server in a fake analytics GET request
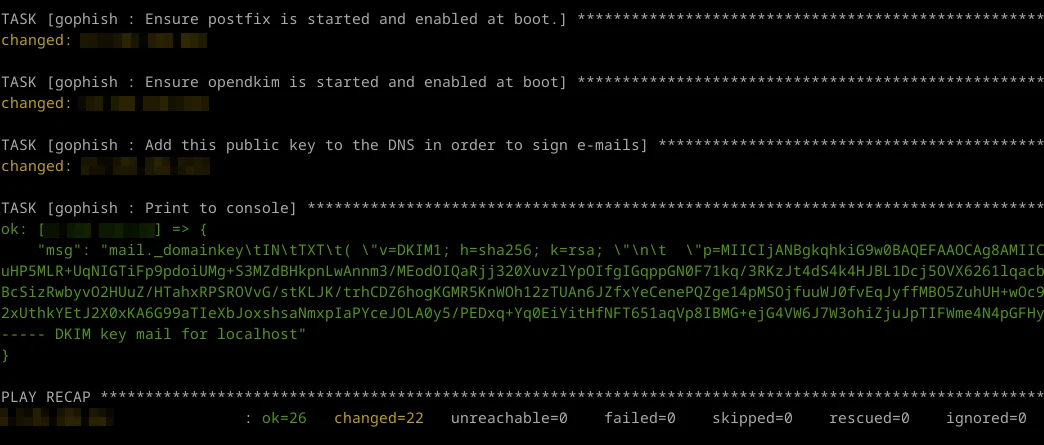 virtualsamuraii/flyphish
Deploy a phishing infrastructure on the fly.
 mbanyamer/cve-2026-27579-collabplatform-appwrite-cors-misconfiguration
Exploit PoC for CVE-2026-27579, a CORS misconfiguration in Appwrite backend, demonstrating credentialed account data theft via malicious phishing…
 exfil0/weaponizing-cve-2024-4367
CVE-2024-4367 is a critical vulnerability (CVSS 9.8) in PDF.js, allowing arbitrary JavaScript code execution due to insufficient type checks on the…
 b1tbit/cve-2026-32201-exploit
Python exploit for CVE-2026-32201, a reflected XSS in Microsoft SharePoint Server, enabling unauthenticated spoofing and data modification via…
 yfelipecruvinel/tryhackme-moniker-link
Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
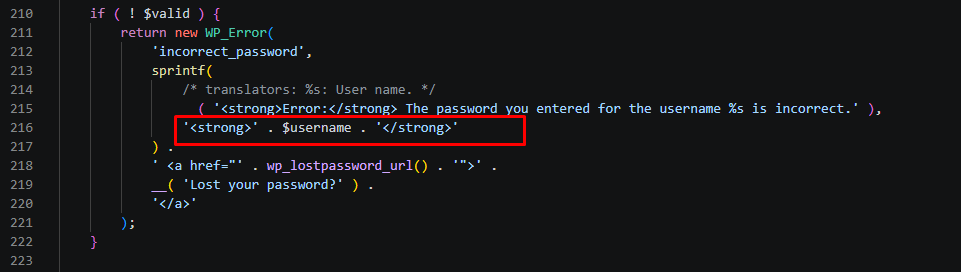 dungsocool/cve-2026-64638
Proof-of-concept exploit for CVE-2026-64638: reflected XSS in WordPress login chained with DOM clobbering to achieve admin account takeover and…
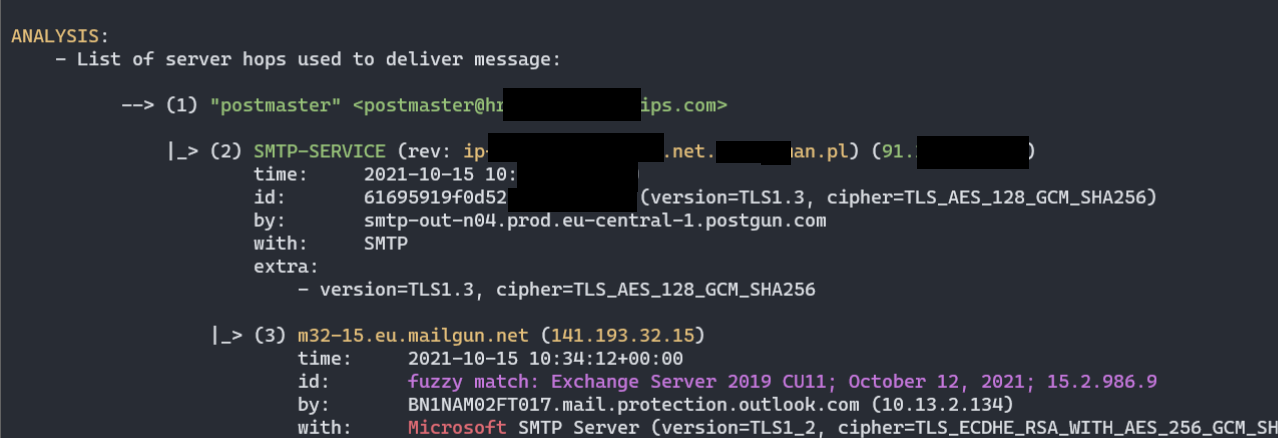 mgeeky/decode-spam-headers
A script that helps you understand why your E-Mail ended up in Spam
 byt3bl33d3r/spamchannel
Spoof emails from any of the +2 Million domains using MailChannels (DEFCON 31 Talk)
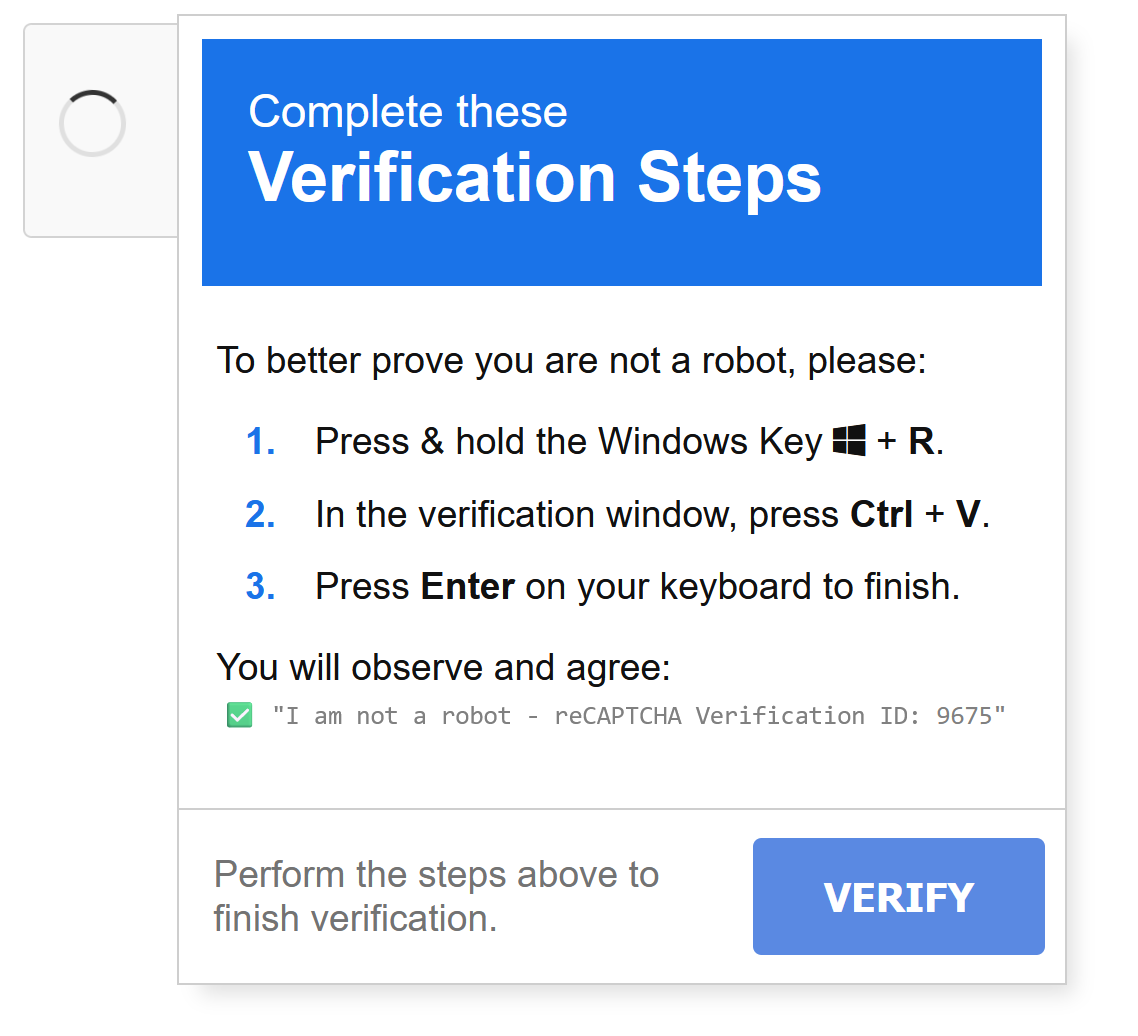 johnhammond/recaptcha-phish
Phishing with a fake reCAPTCHA
 nccgroup/droppedconnection
Emulates a Cisco ASA Anyconnect VPN service for credential harvesting and VBS payload delivery in red team phishing operations.
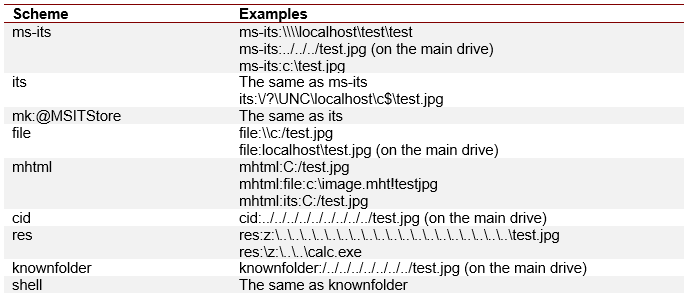 nccgroup/outlookleaktest
The Outlook HTML Leak Test Project
 bishopfox/ca-clone
Scripts to clone CA certificates for use in HTTPS client attacks.
 cappricio-securities/camjacking
CamJacking is a tool designed for use in human penetration testing tool. It is intended to simulate potential security threats by testing the…
 sanupl/letterpress-1.2.1-open-redirection-via-html-injection-vulnerability
In LetterPress plugin <= 1.2.1 is vulnerable to Html Injection Vulnerability which can futher leads to Open Redirection Vulnerabilty.
 minhhk68/cve-2026-13156
CVE-2026-13156 Vulnerability Advisory & PoC — Discovered by Huynh Kien Minh (MinhHK).