
Modlishka
 drk1wi/modlishka
Modlishka. Reverse Proxy.
authenticationimpersonation-toolspenetration-testing+6
drk1wi/modlishkaModlishka. Reverse Proxy.
 sheeki03/tirith
Terminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
 jonaslejon/malicious-pdf
Generate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 phishdestroy/destroylist
Real-time phishing & scam domain blocklist - 205k+ curated threats, 1M+ community, free API, multiple formats
 0x90n/infosec-black-friday
All the deals for InfoSec related software/tools this Black Friday
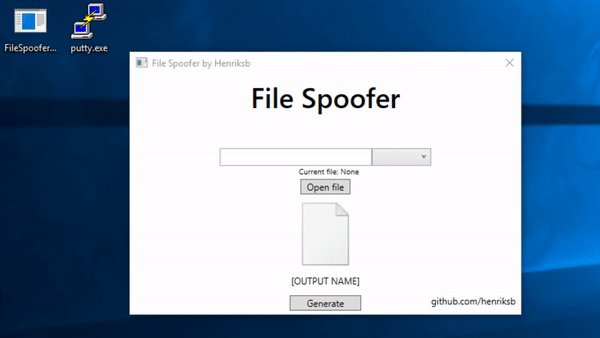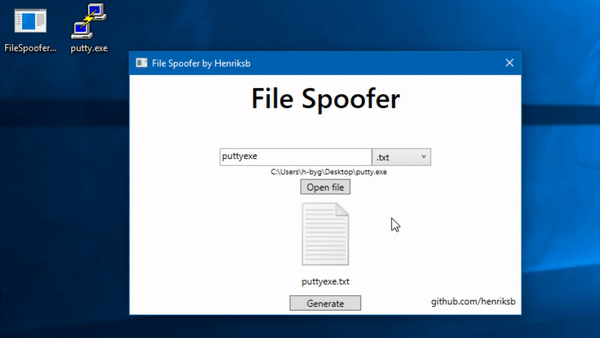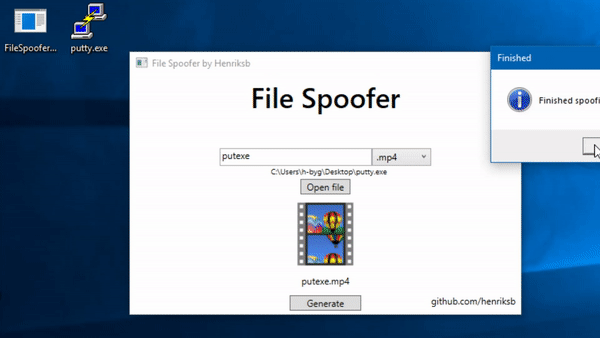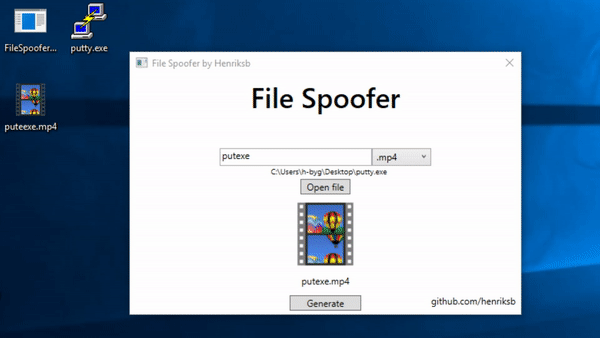 henriksb/extensionspoofer
Spoof file icons and extensions in Windows
 cryst4linqq/turkorat
Fully undetected grabber (grabs wallets, passwords, cookies, modifies discord client etc.)
 ecstatic-nobel/osweep
Don't Just Search OSINT. Sweep It.
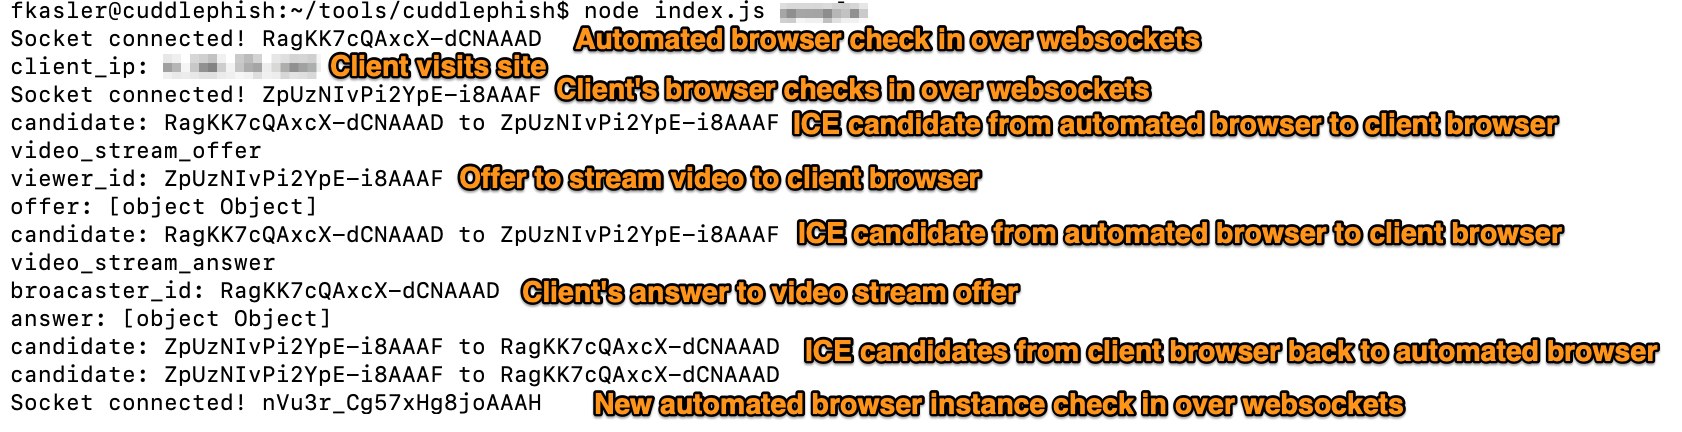 fkasler/cuddlephish
Weaponized Browser-in-the-Middle (BitM) for Penetration Testers
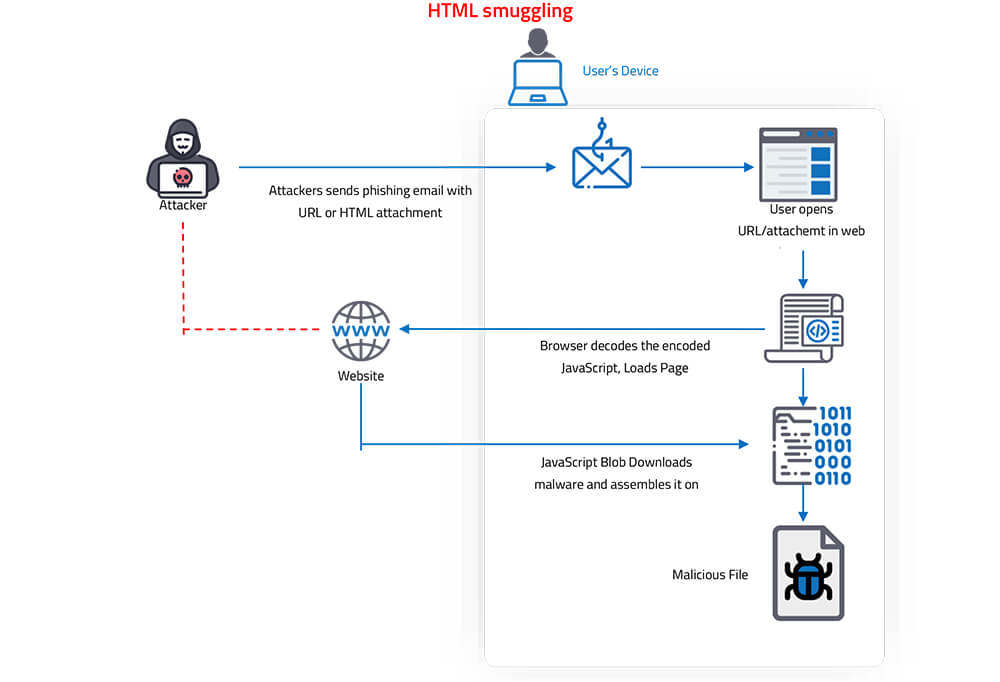 de3vil/htmlsmuggling
it is malicious technique used by hackers to hide malware payloads in an encoded script in a specially crafted HTML attachment or web page
 makdosx/wifi-agent
Rogue access point tool for creating captive portals, phishing credentials via cloned login pages, and injecting malware downloads for educational…
 r00t-3xp10it/trojanizer
Trojanize your payload - WinRAR (SFX) automatization - under Linux distros
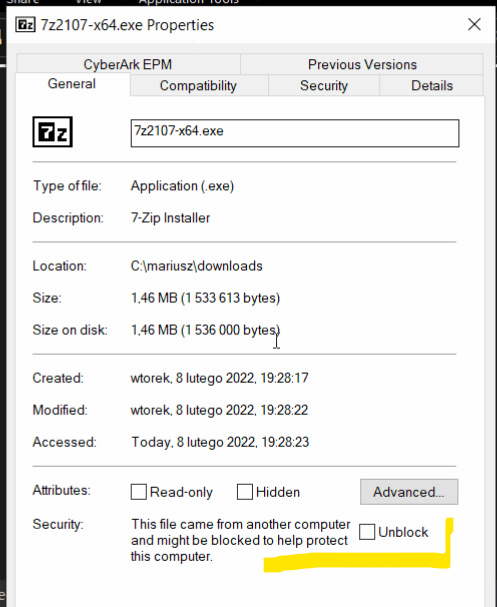 mgeeky/packmypayload
A PoC that packages payloads into output containers to evade Mark-of-the-Web flag & demonstrate risks associated with container file formats.…
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 kira2040k/redbloodc2
Node.js command-and-control server with FUD payload generation, encrypted communication, session management, and modules for data exfiltration and…
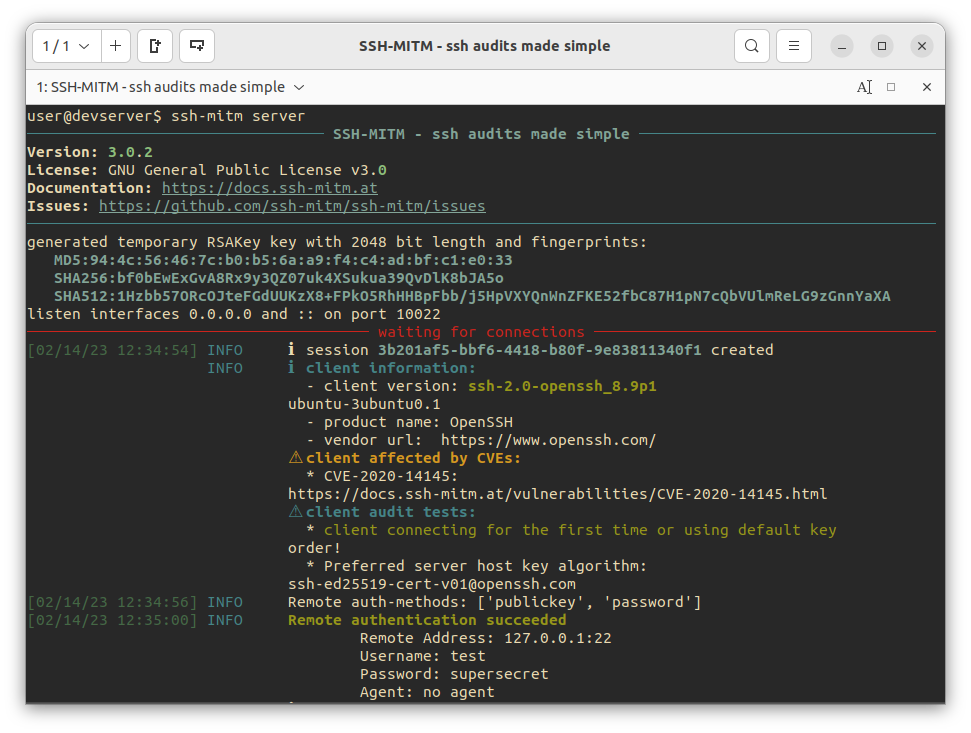 ssh-mitm/ssh-mitm
SSH-MITM - ssh audits made simple
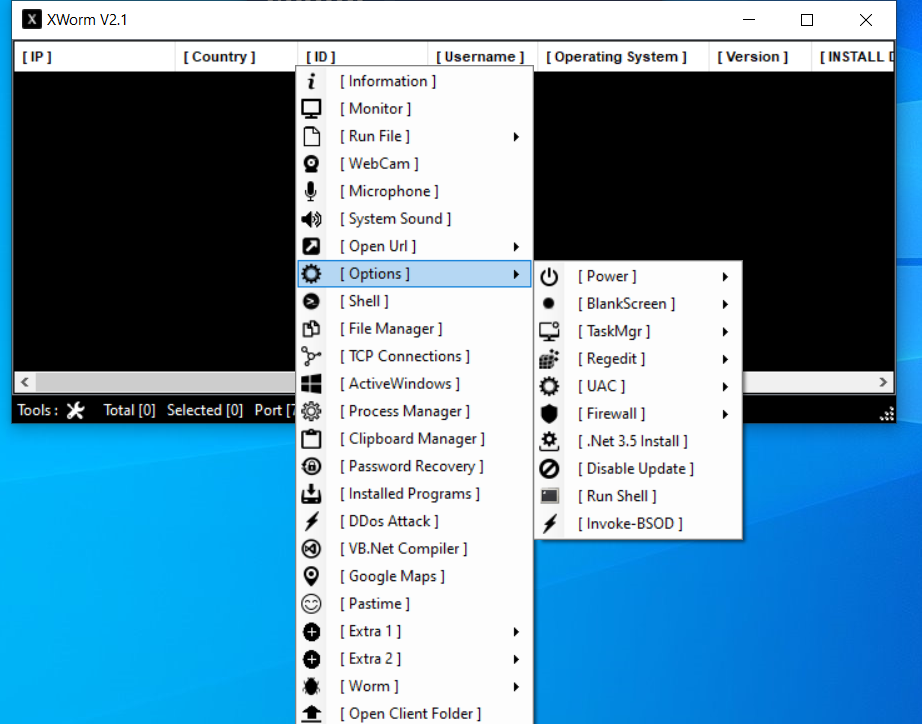
 manturever/xworm-rat
⭐️The famous XWorm RAT, version 2.1. Educational purposes only