
Archived
CVE-2021-46398
 laliea/cve-2021-46398
A Proof of Concept for the CVE-2021-46398 flaw exploitation
educationexploitationlabs-practice+3
laliea/cve-2021-46398A Proof of Concept for the CVE-2021-46398 flaw exploitation
 corvralabs/evilneko
Automated container orchestration tool for Browser-in-the-Browser (BITB) phishing attacks, enabling red teams to scale multi-target infrastructure…
 rub-nds/johnny-you-are-fired
Artifacts for the USENIX publication.
 dev-lu/osint_toolkit
Open source platform for cyber security analysts with many features for threat intelligence and detection engineering.
 lxance-hacker/lxancephisher
Automated phishing simulation tool with 30+ login page templates, URL masking, and multiple tunneling options (Ngrok, Cloudflared, Serveo) for…
 octoberfest7/xll_phishing
XLL Phishing Tradecraft

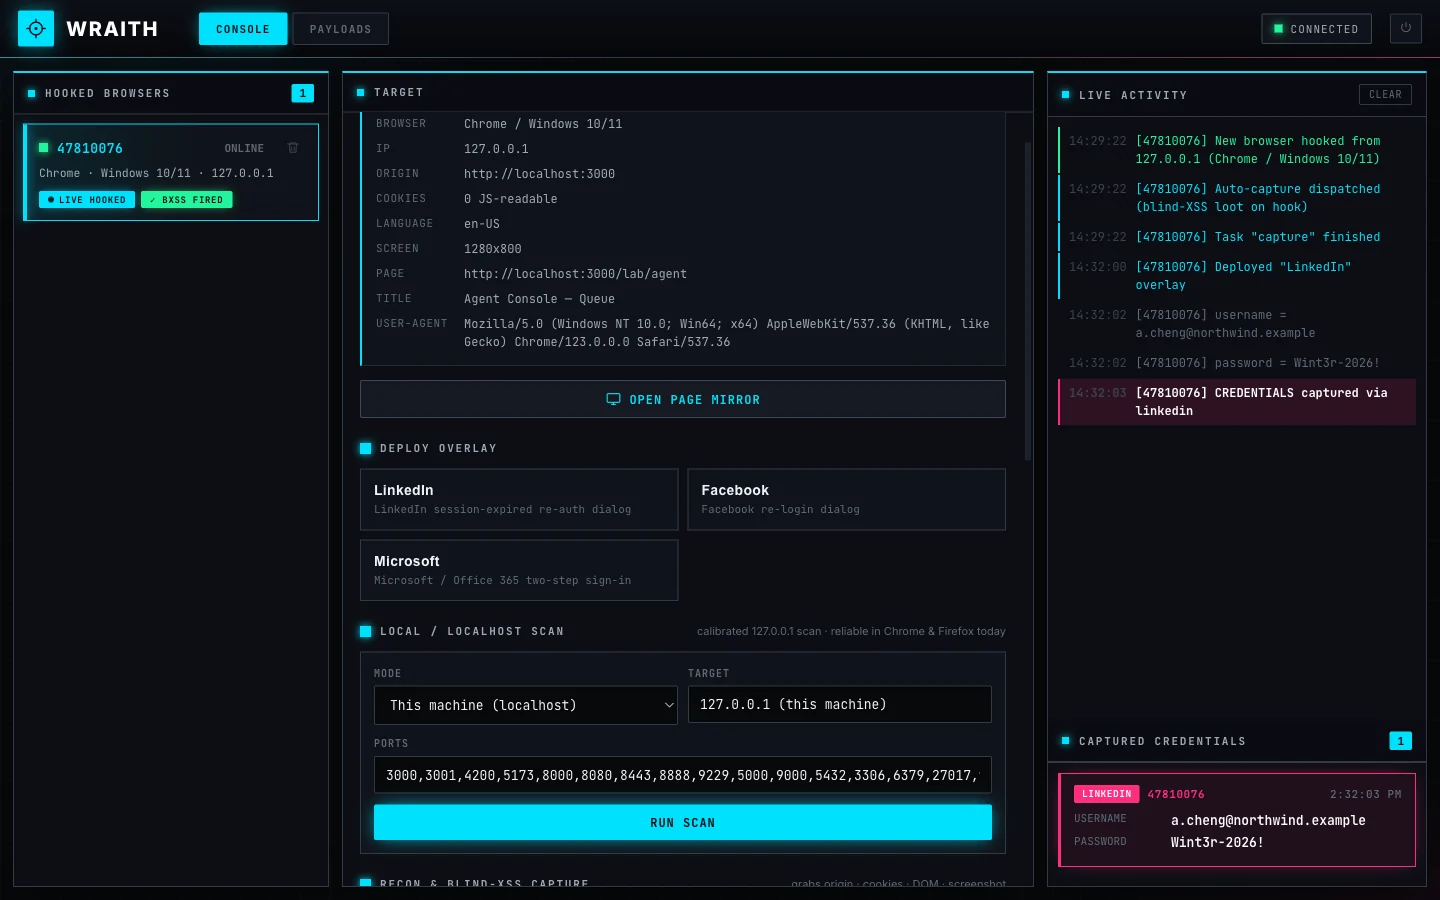 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
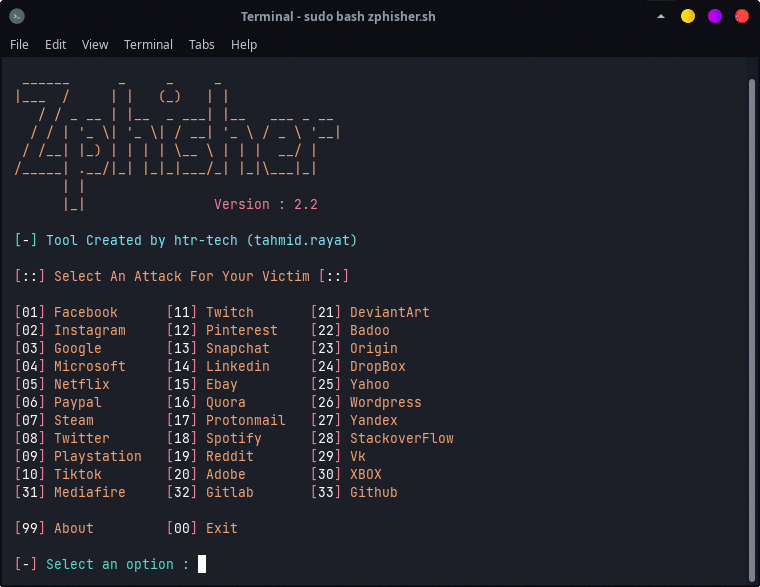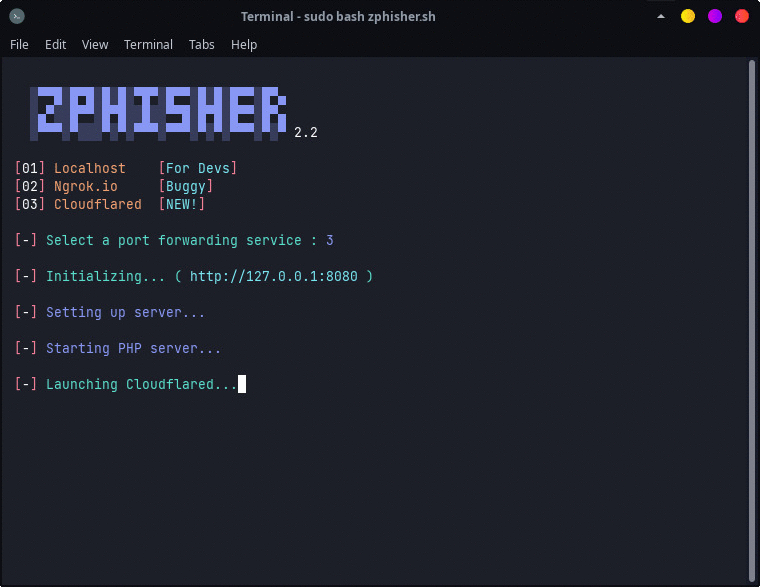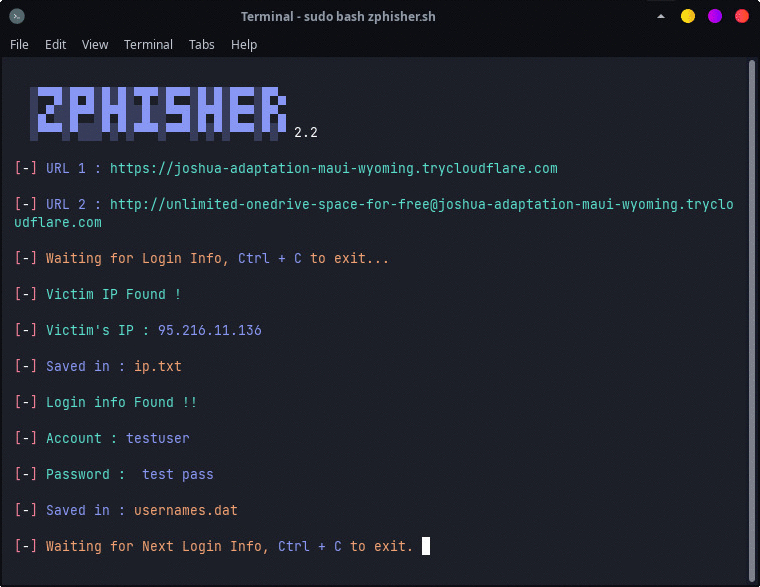 htr-tech/zphisher
An automated phishing tool with 30+ templates. This Tool is made for educational purpose only ! Author will not be responsible for any misuse of this…
 trustedsec/reel
Phishing simulation and awareness framework for node-based campaigns, credential capture, SMTP delivery, CAPTCHA, and optional browser credential…
 secdev02/easytokens
Kali365 - EvilTokens Replica
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…