SmuggleMyPayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

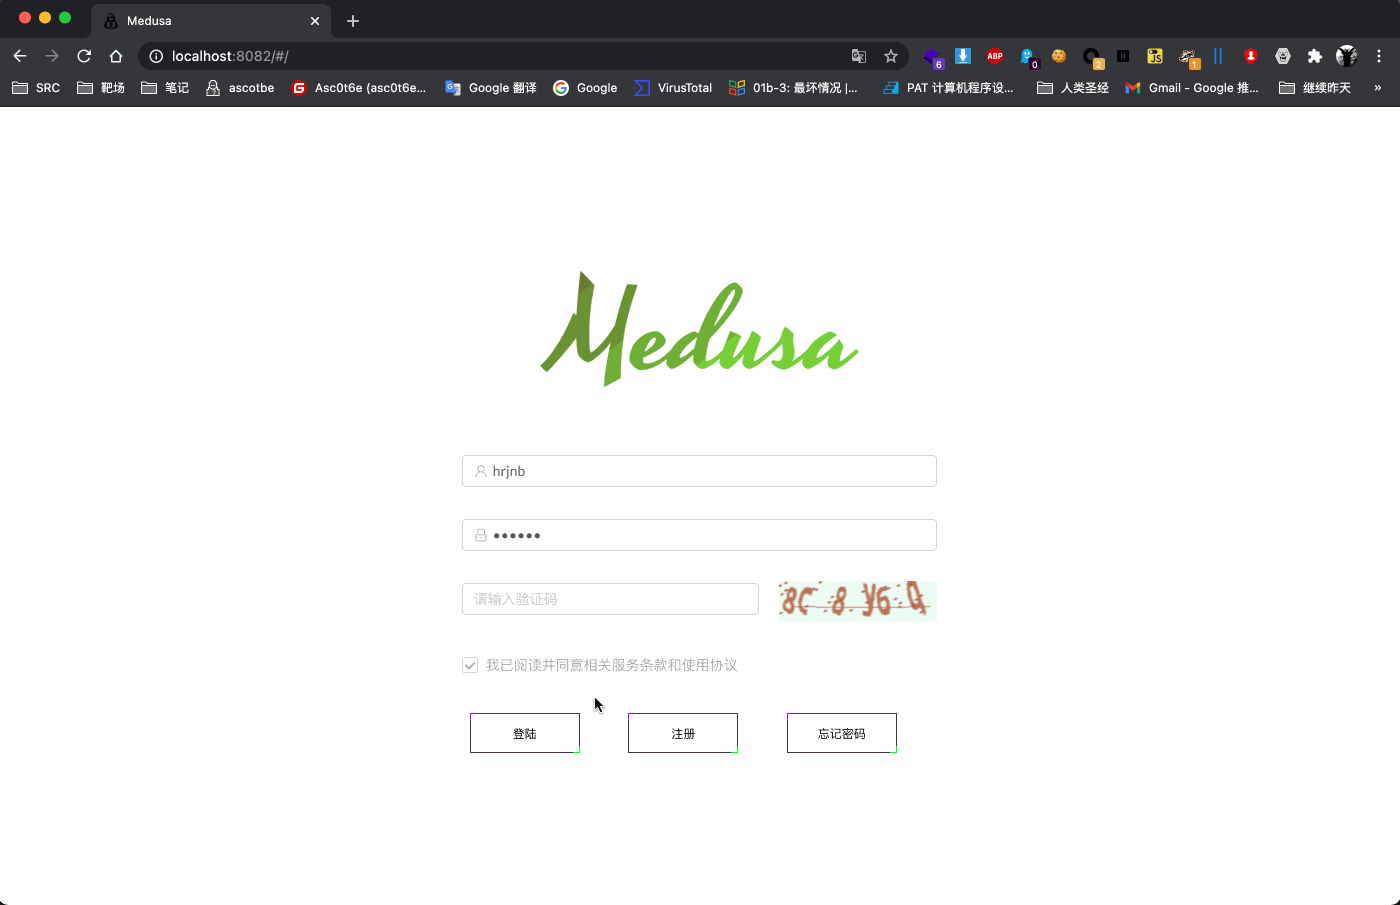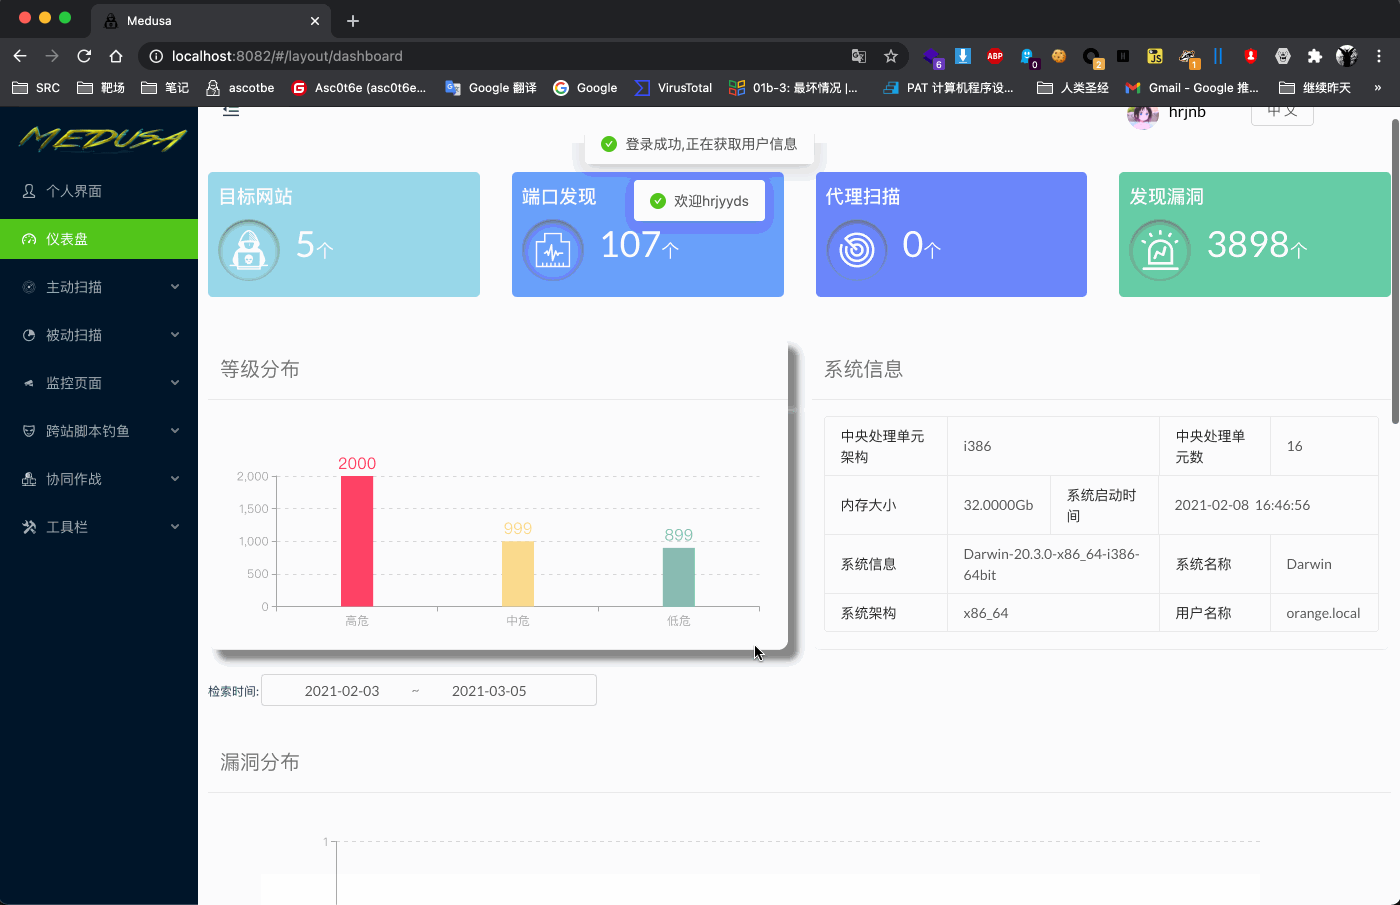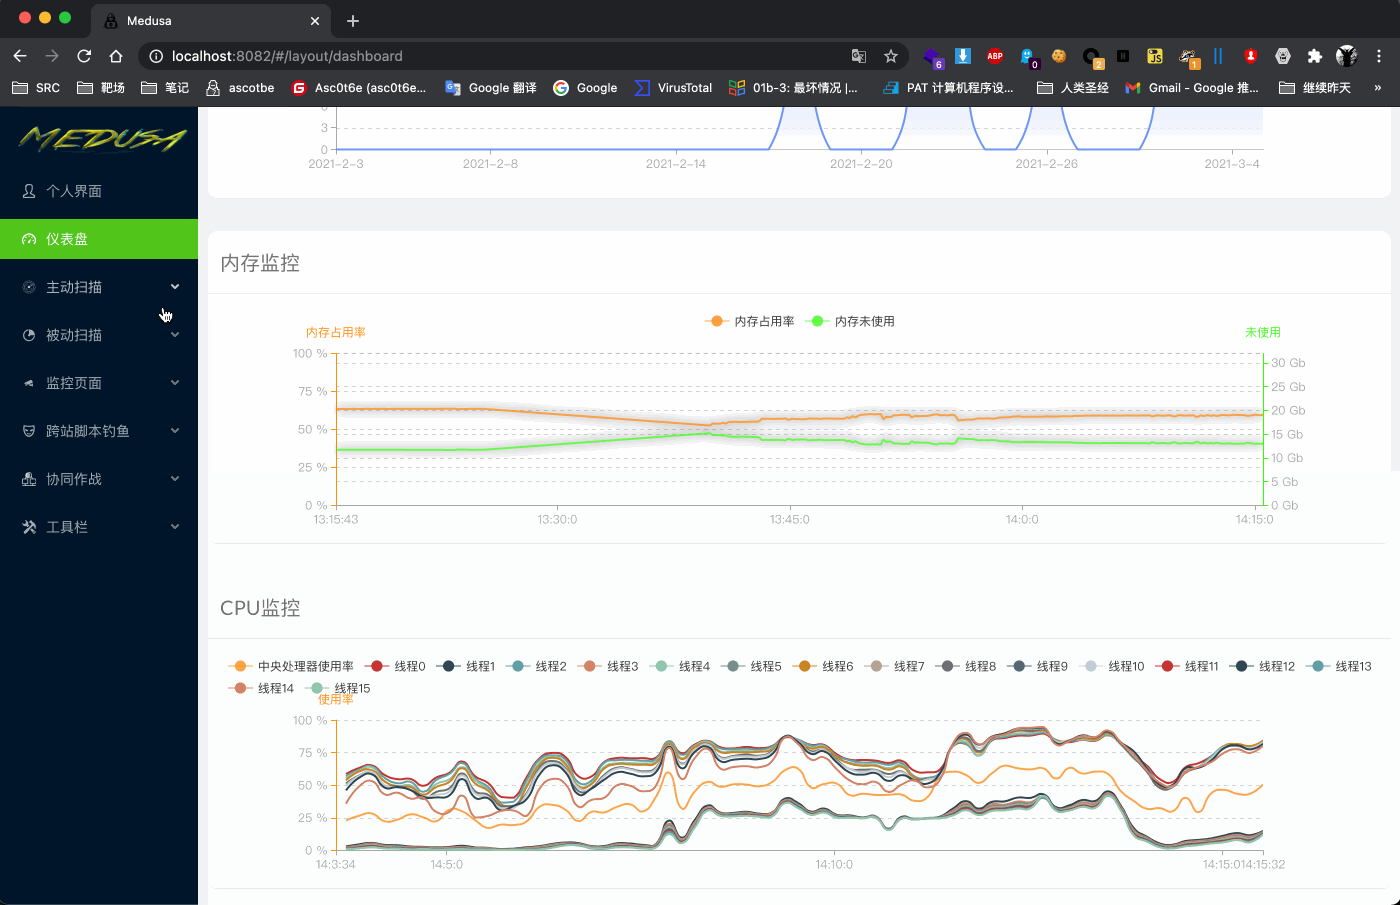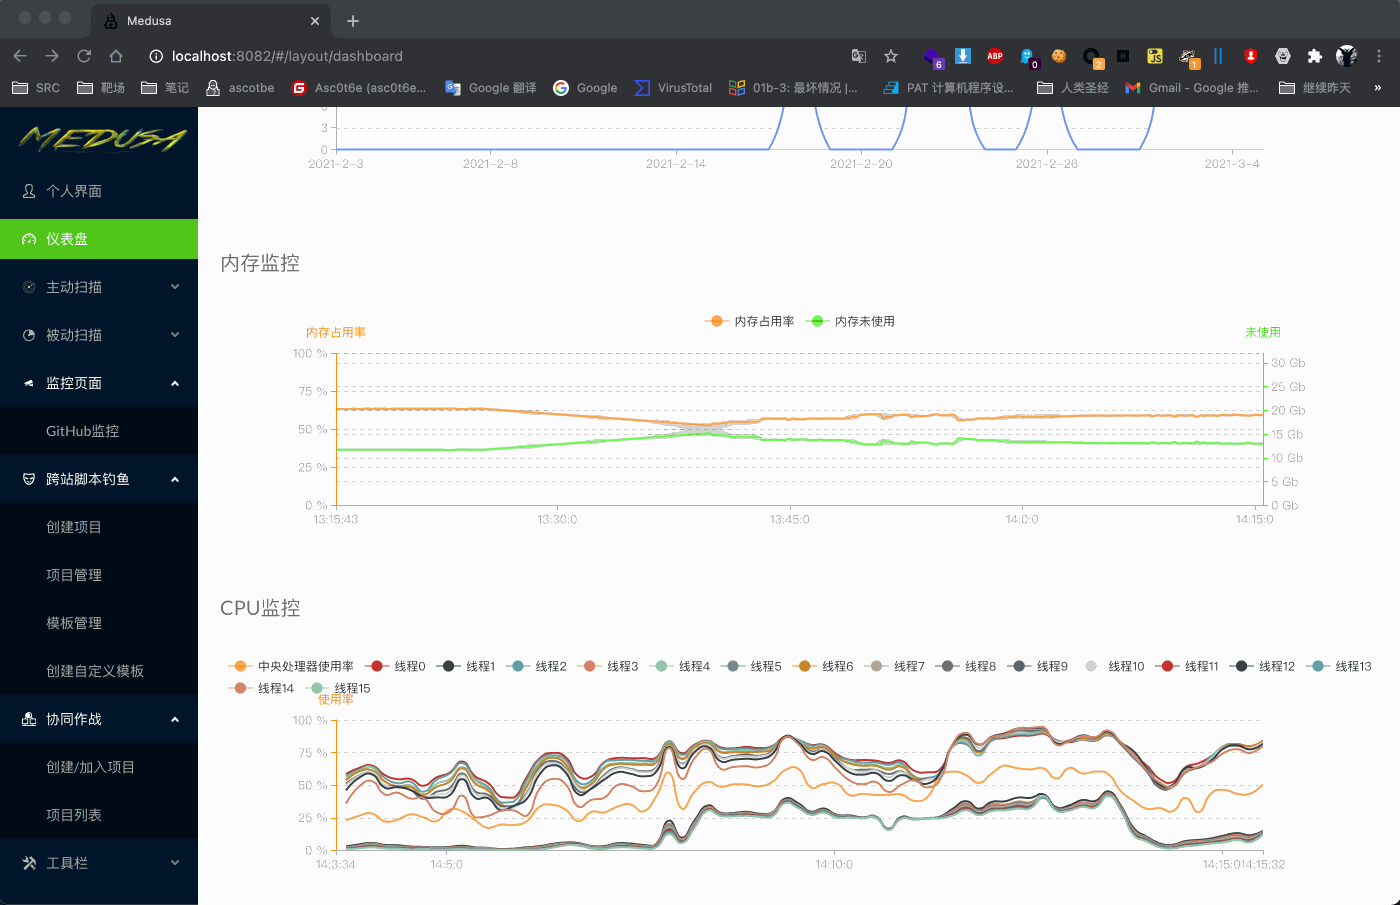
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中

XLL Phishing Tradecraft

A tool to transform Chromium browsers into a C2 Implant

Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.

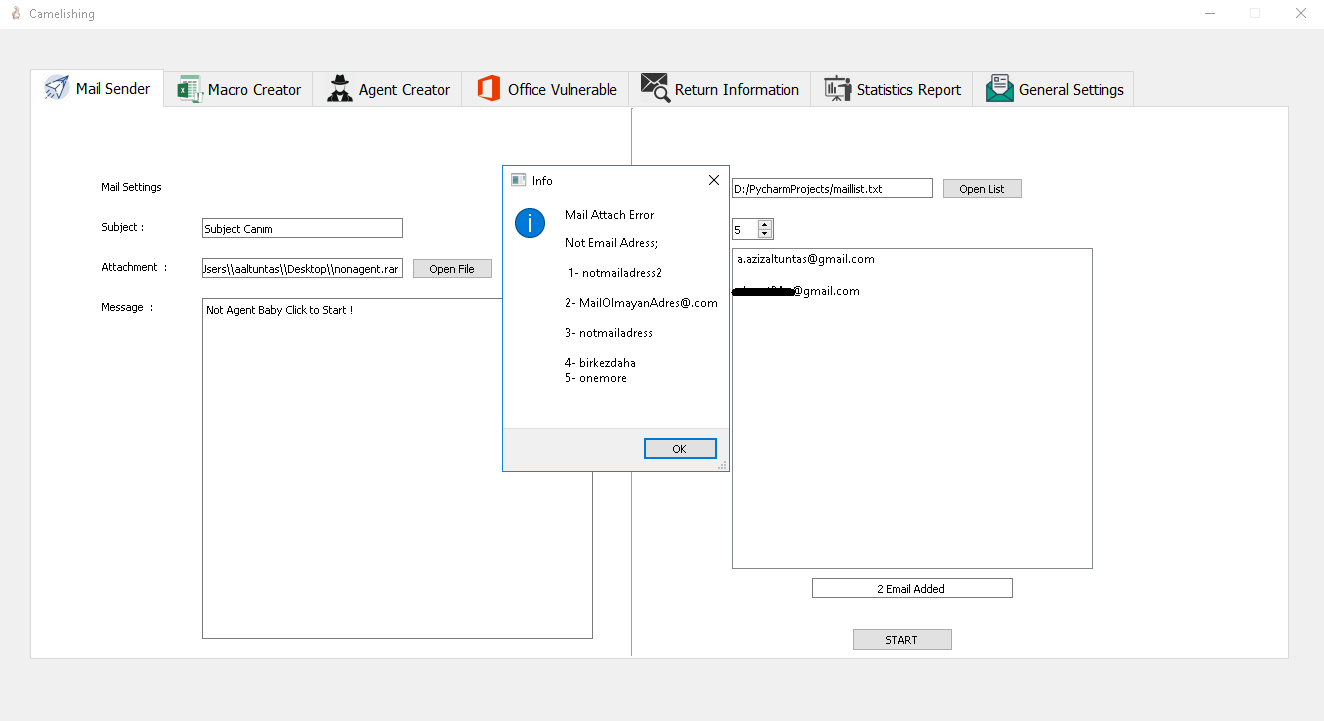
Social Engineering Tool

Excel Macro Document Reader/Writer for Red Teamers & Analysts

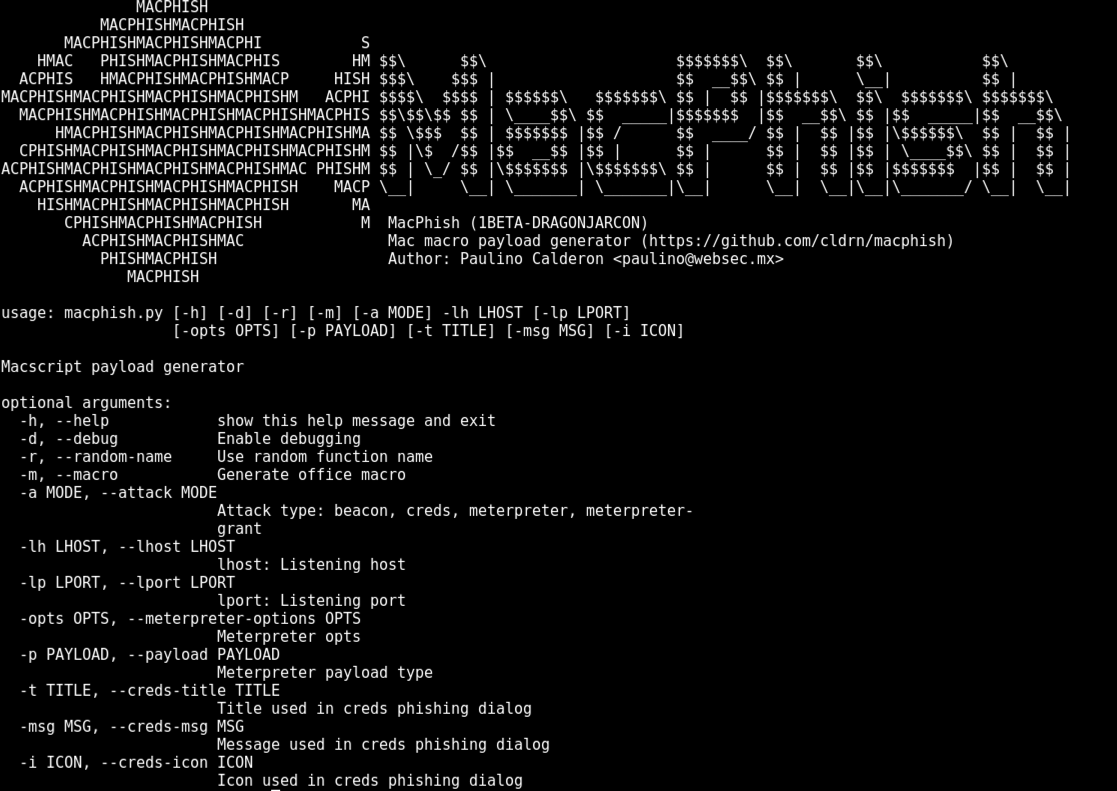
Generates malicious Office for Mac macros with beacon, credential harvesting, and meterpreter payloads for phishing and exploitation testing on macOS.


WonderCMS Authenticated RCE - CVE-2023-41425

Proof-of-concept exploit for Microsoft Office security feature bypass (CVE-2026-21509). Generates malicious DOCX files with embedded OLE objects to…

CVE-2023-23397 PoC

PoC for the "Windows Notepad RCE"

Automated PoC exploit for CVE-2022-30190 (Follina) that generates malicious RTF/DOCX files abusing MSDT protocol to execute arbitrary commands and…

Windows active user credential phishing tool

Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…

XSS-to-RCE exploit for Wonder CMS 3.2.0–3.4.2 with automated payload delivery, reverse shell, and cookie theft via malicious theme installation.

Tools and Techniques for Red Team / Penetration Testing