
URL_CHECKER
 mannansainicyber/url_checker
Hybrid ML and heuristic-based URL phishing detector with real-time analysis, explainable confidence scores, and REST API for programmatic security…
api-security-testingeducationmachine-learning+3
1
mannansainicyber/url_checkerHybrid ML and heuristic-based URL phishing detector with real-time analysis, explainable confidence scores, and REST API for programmatic security…
 octoberfest7/xll_phishing
XLL Phishing Tradecraft
 muraenateam/muraena
Automates phishing and post-phishing activities with an almost-transparent reverse proxy that dynamically mirrors target web apps and interacts with…
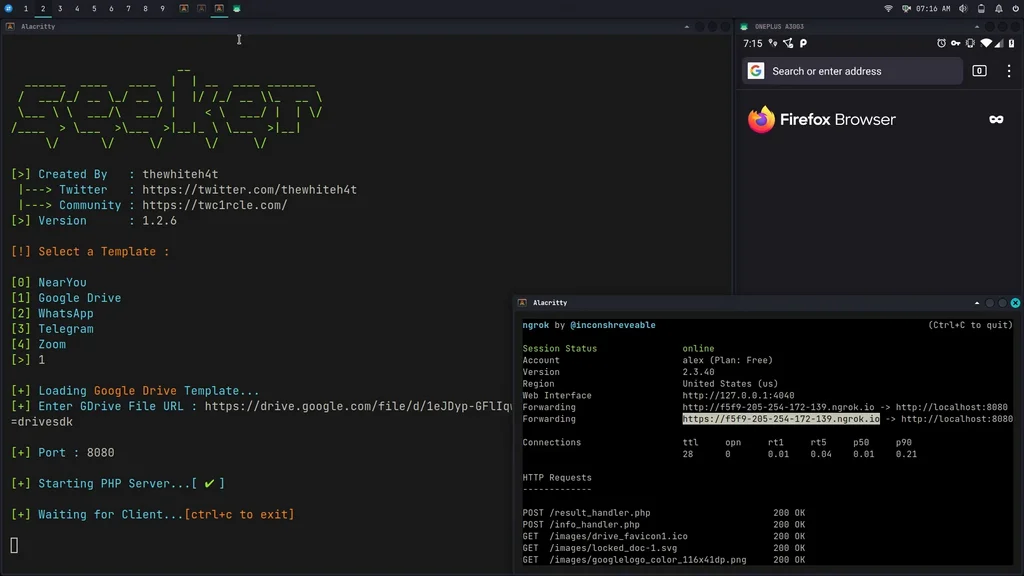 thewhiteh4t/seeker
Accurately Locate Smartphones using Social Engineering
 mattkeeley/spoofy
Bulk domain spoofability checker using authoritative SPF and DMARC record analysis with custom, real-world tested spoof logic and optional DKIM…
 e1tex/cve-2023-48104
Proof-of-concept exploit demonstrating HTML injection in SOGo Web Client before 5.9.1, enabling phishing attacks via malicious forms in email bodies.
 h1ssbl1tz/blind-trust-cve-2024-21413-research
A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).
 fluxionnetwork/fluxion
Automated WPA/WPA2 phishing tool that captures handshakes, spawns a rogue access point, and lures users to a captive portal to harvest credentials…
 mgeeky/penetration-testing-tools
A collection of more than 170+ tools, scripts, cheatsheets and other loots that I've developed over years for Red Teaming/Pentesting/IT Security…
 dionach/phemail
PhEmail is a python open source phishing email tool that automates the process of sending phishing emails as part of a social engineering test
 antisnatchor/phishlulz
Automated phishing campaign toolset that spawns dedicated AWS EC2 instances with integrated PhishingFrenzy and BeEF, plus subdomain discovery and…
 davenisc/thief_raccoon
Educational phishing simulation tool that mimics OS login screens to capture credentials for cybersecurity awareness training. Supports Windows,…
 ilianazz/young-domain-guard
Browser extension that warns users about recently registered domains to prevent phishing attacks. Queries RDAP to check domain age and displays…
 rat5ak/cve-2025-59382-qnap-password-reset-account-takeover
Proof-of-concept and technical writeup for CVE-2025-59382, an unauthenticated password reset URL injection in QNAP NAS that enables a…
 roxanne_ardary/emailxpose
EmailXpose is an open source AI-powered email security system that detects phishing, spam, scams, malware, and social engineering attacks. It goes…
 kaleth4/cve-2022-30190
Automated PoC exploit for CVE-2022-30190 (Follina) that generates malicious RTF/DOCX files abusing MSDT protocol to execute arbitrary commands and…
 filipegaudard/cve-2026-33149-poc
Proof-of-concept exploit for CVE-2026-33149, a Host header injection in Tandoor Recipes that enables invite link poisoning and cache poisoning.…
 mrk336/cve-2021-3456
A practical chain that starts with an innocuous PDF file and ends up in a reverse shell on an AWS EC2 instance