

zaproxy
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
android-securityapi-securityapi-security-testing+15
15.9k
zaproxy/zaproxyOpen-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 lxance-hacker/lxancephisher
Automated phishing simulation tool with 30+ login page templates, URL masking, and multiple tunneling options (Ngrok, Cloudflared, Serveo) for…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 nehkark/cve-2025-40778
Proof-of-concept demonstrating DNS cache poisoning via additional record injection in BIND 9, with tools to validate and exploit CVE-2025-40778 for…
 mannansainicyber/url_checker
Hybrid ML and heuristic-based URL phishing detector with real-time analysis, explainable confidence scores, and REST API for programmatic security…
 hackinglz/ip-obfuscation
Generates obfuscated IP addresses and URLs using DWORD, octal, hex, IPv6-mapped, and fake-domain @ tricks for penetration testing, phishing…
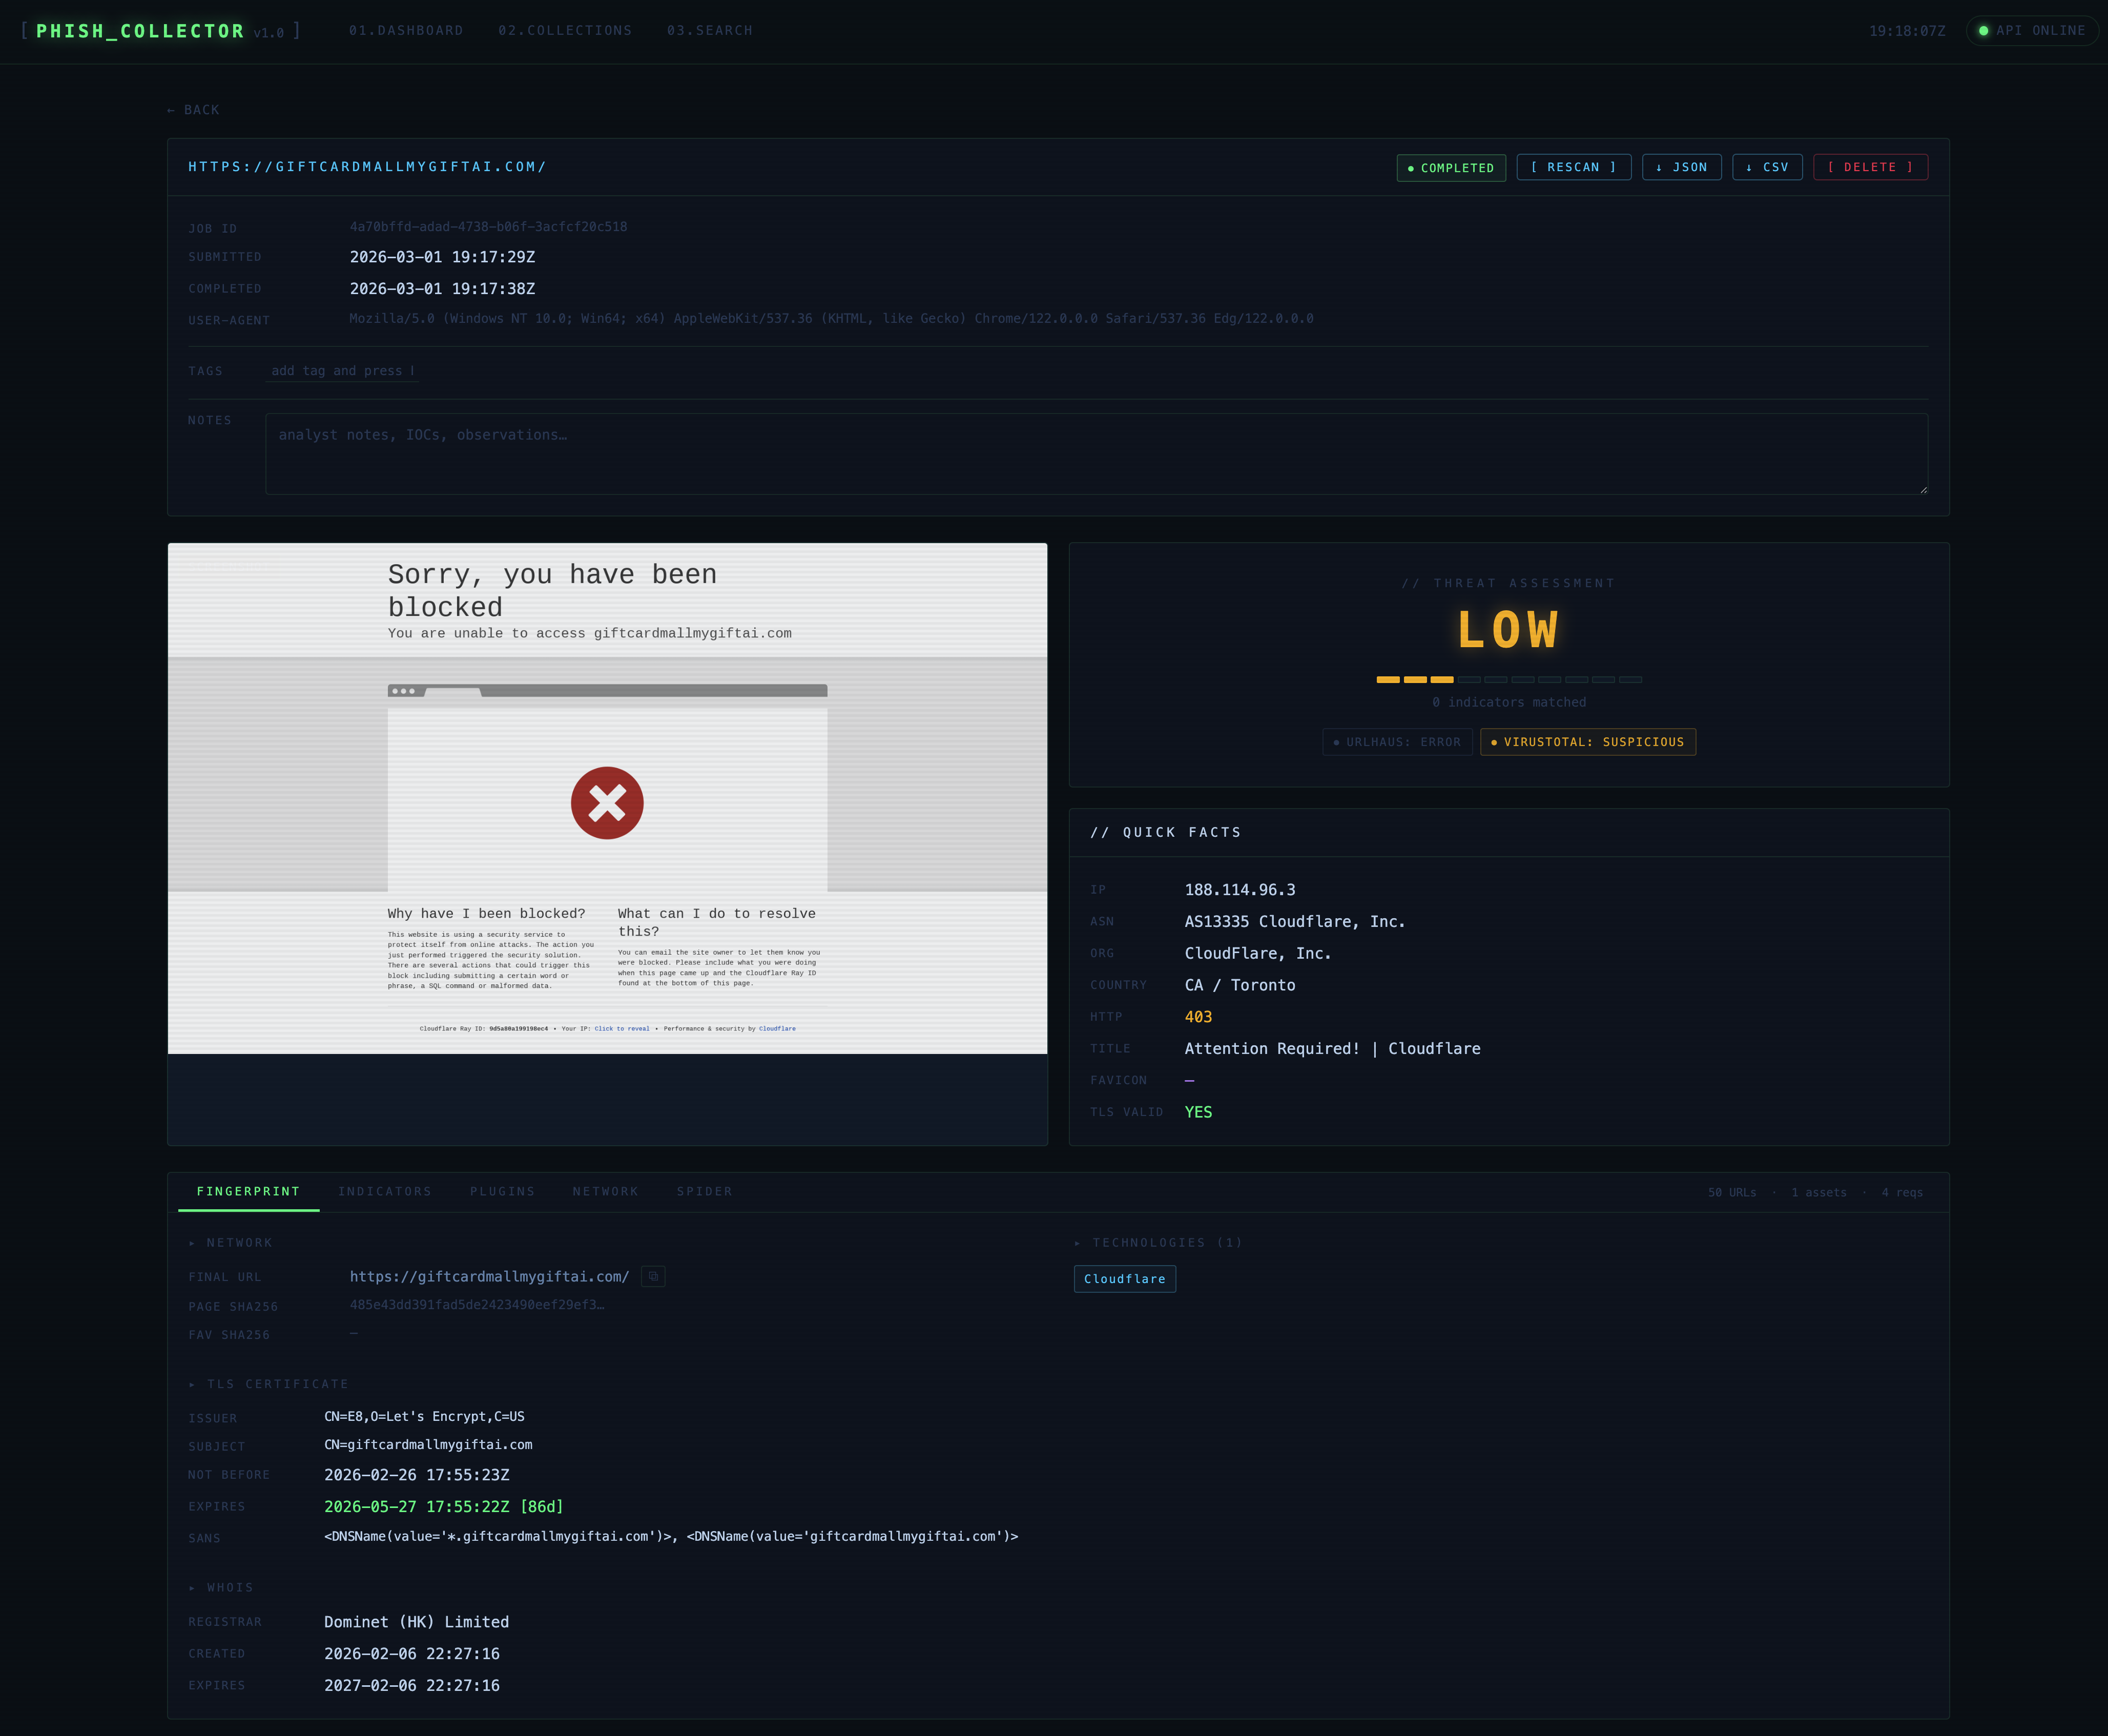 olizimmermann/phishcollector
PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
 sublime-security/ics-phishing-toolkit
Open source tooling to stop ICS phishing (malicious calendar invites)
 sobri3195/pegasus-neo
PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…
 tw-d/wifi-pineapple-mk7_evil-portal
Rogue access point toolkit for WiFi penetration testing, deploying evil portal phishing payloads to capture credentials and perform social…
 fluxionnetwork/fluxion
Automated WPA/WPA2 phishing tool that captures handshakes, spawns a rogue access point, and lures users to a captive portal to harvest credentials…
 pentestgeek/phishing-frenzy
Ruby on Rails Phishing Framework
 4w4k3/umbrella
A Phishing Dropper designed to Pentest.
 paranoidninja/o365-doppelganger
A quick handy script to harvest credentials off of a user during a Red Team and get execution of a file from the user
 649/cve-2017-5415
Addressbar spoofing through blob URL (Firefox browser). An attack can use a blob URL and script to spoof an arbitrary addressbar URL prefaced by…
 atn1ght/fakeauth
Creates Fake Auth prompt to capture users plaintext passwords