SOC336-Windows-OLE-Zero-Click-RCE-Exploitation-Detected-CVE-2025-21298

SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough

SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough

Discovering CVE-2025-22381: Host Header Injection in the Aggie Open-Source Project

Educational Proof-of-Concept for the CVE-2022-30190 (Follina) vulnerability.

A Proof of Concept for the CVE-2021-46398 flaw exploitation

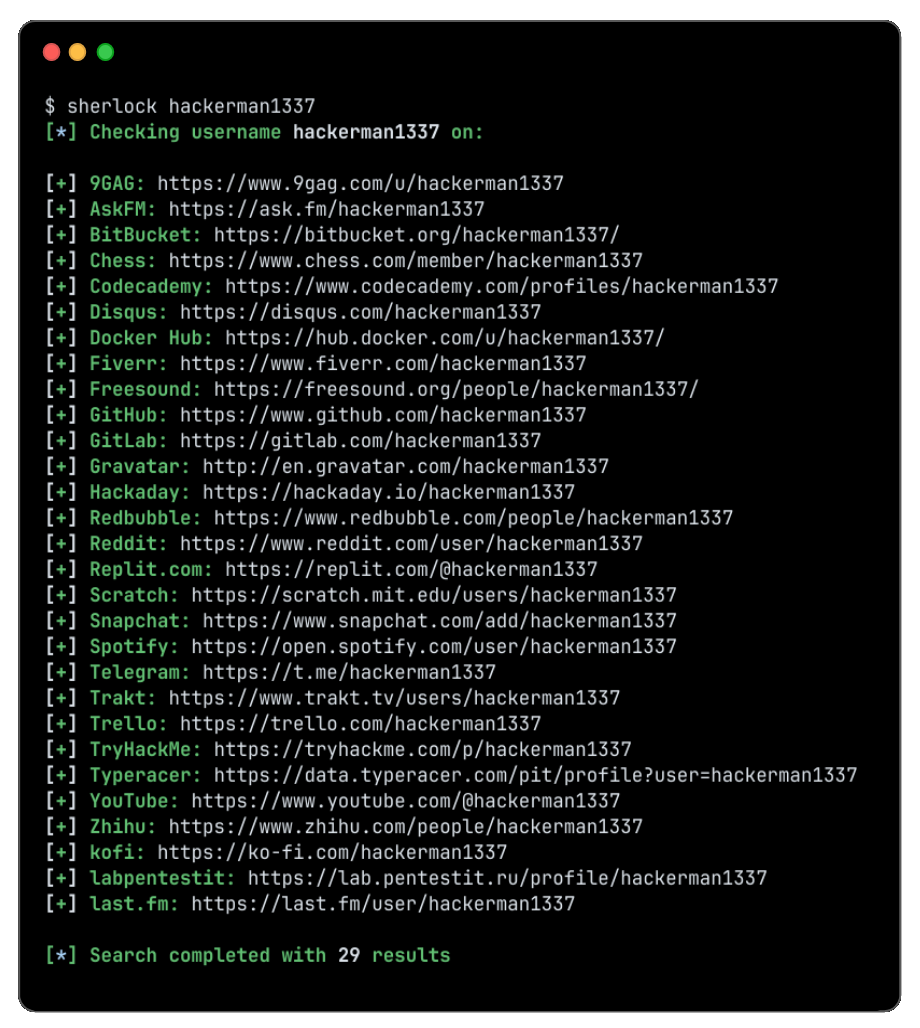
Hunt down social media accounts by username across social networks

Accurately Locate Smartphones using Social Engineering

The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.

This repository contains cutting-edge open-source security tools (OST) for a red teamer and threat hunter.

The Browser Exploitation Framework Project

Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…

The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.

Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…

Tools and Techniques for Red Team / Penetration Testing


Grab cam shots & GPS location from target's phone front camera or PC webcam just sending a link.

Modlishka. Reverse Proxy.

Wiki to collect Red Team infrastructure hardening resources

Modern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…