
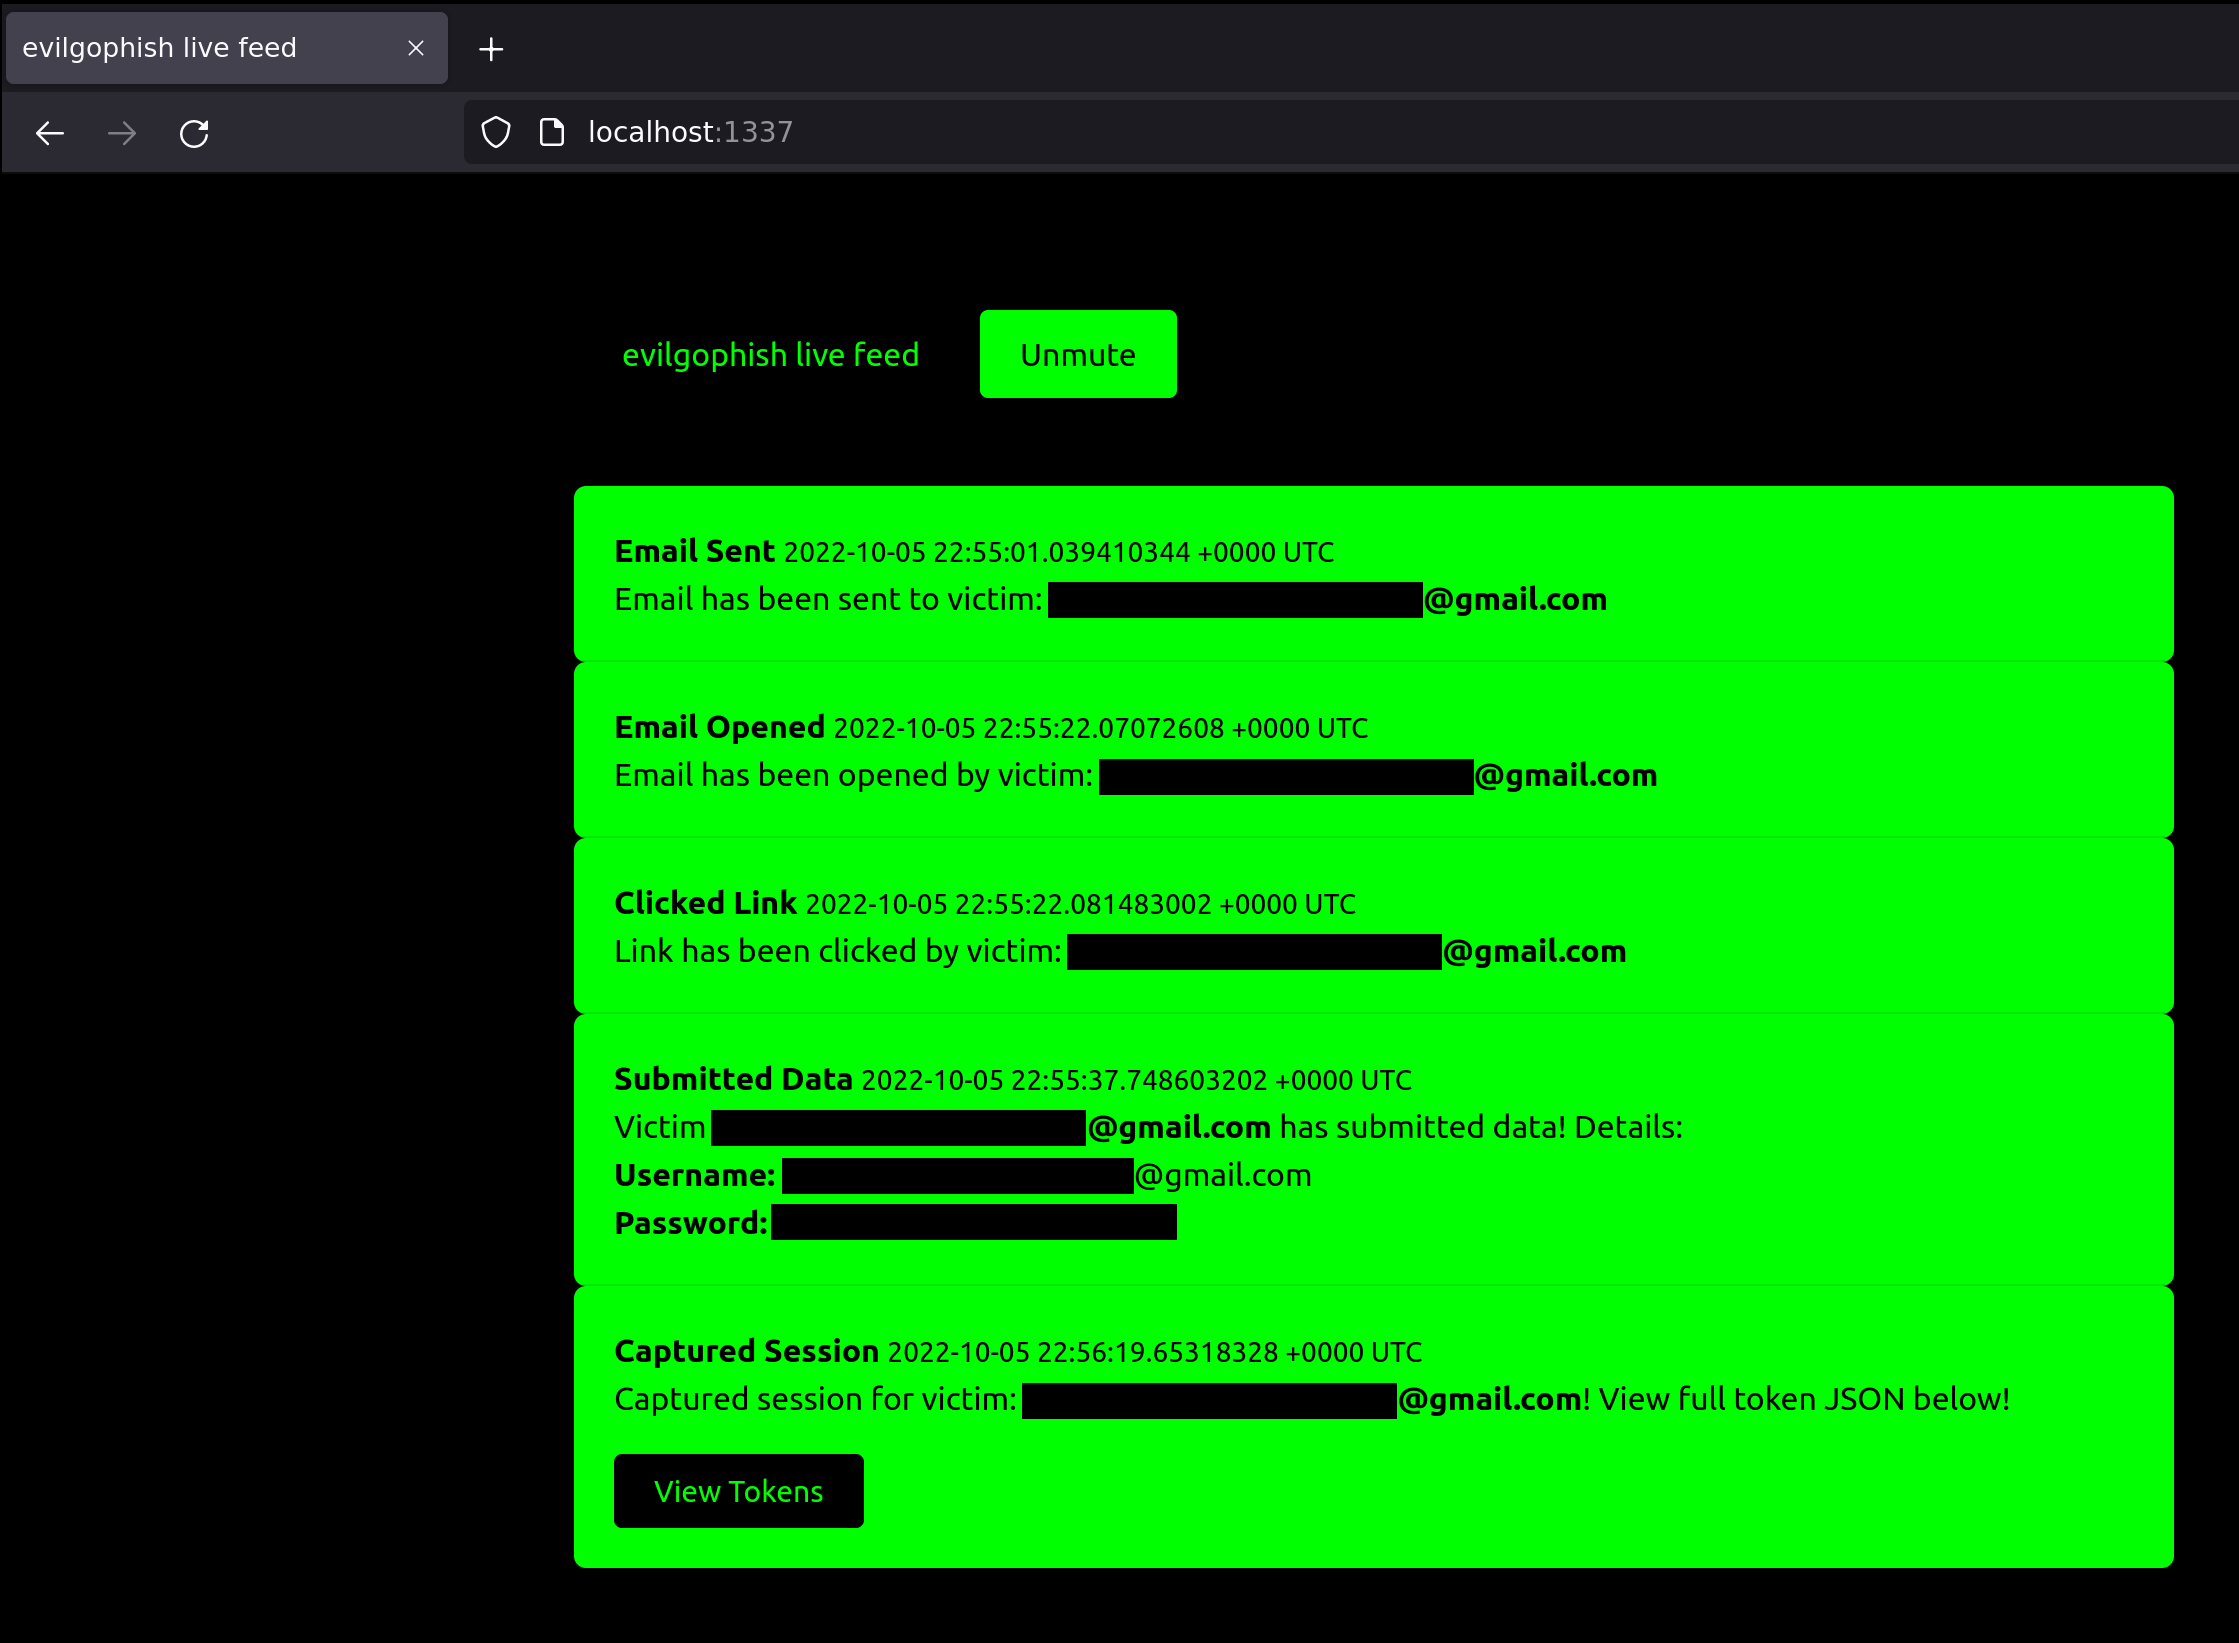
evilgophish
 fin3ss3g0d/evilgophish
evilginx3 + gophish
authenticationcommand-and-controlpenetration-testing+5
fin3ss3g0d/evilgophishevilginx3 + gophish
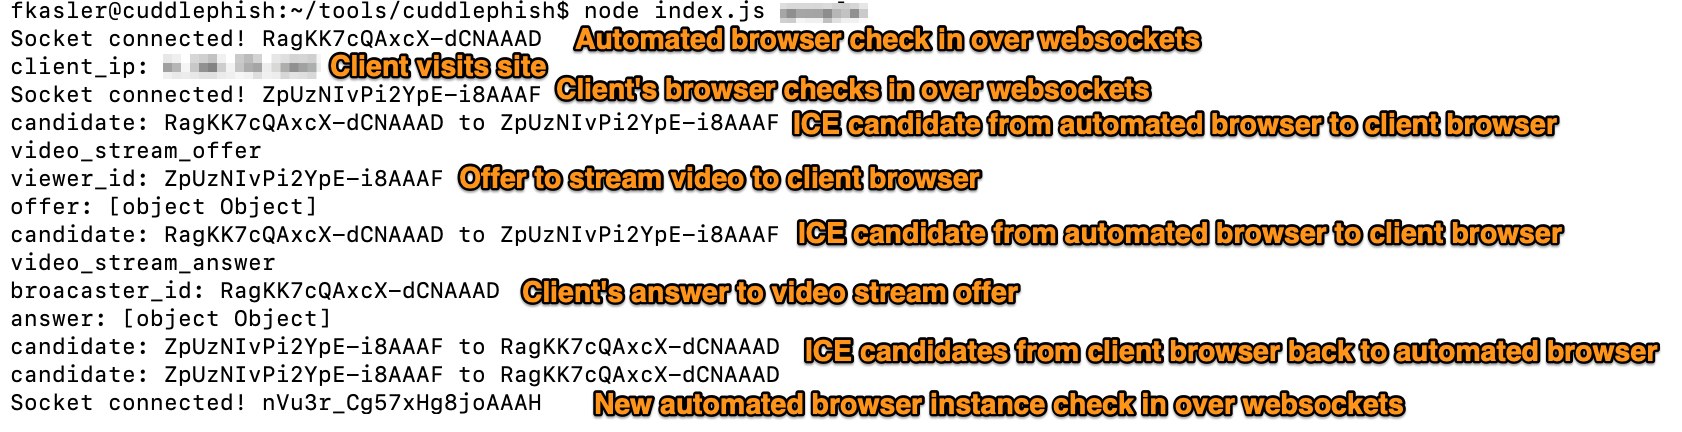 fkasler/cuddlephish
Weaponized Browser-in-the-Middle (BitM) for Penetration Testers
 mdsecactivebreach/o365-attack-toolkit
A toolkit to attack Office365
 ascotbe/medusa
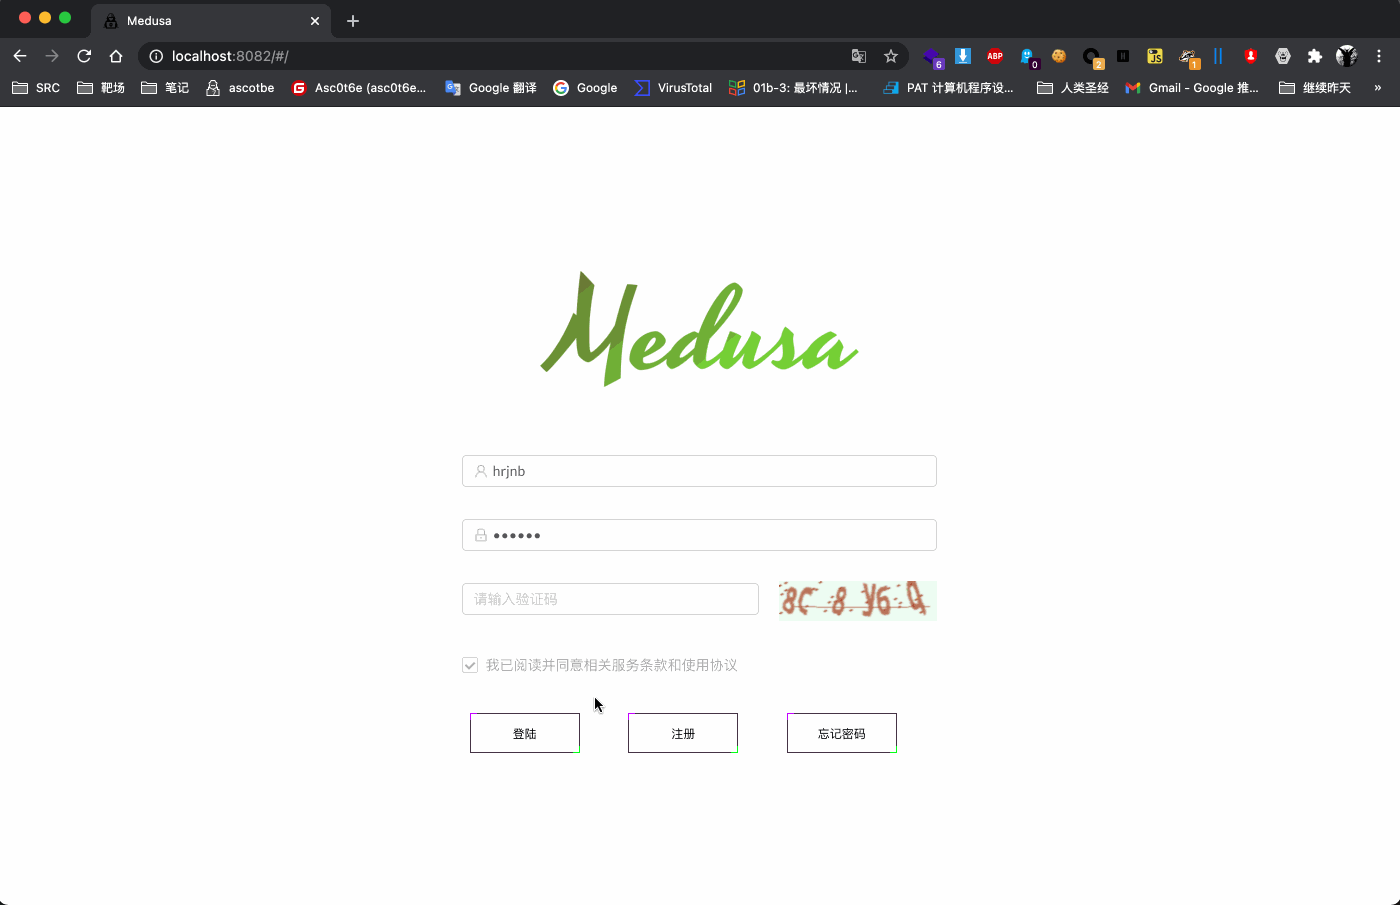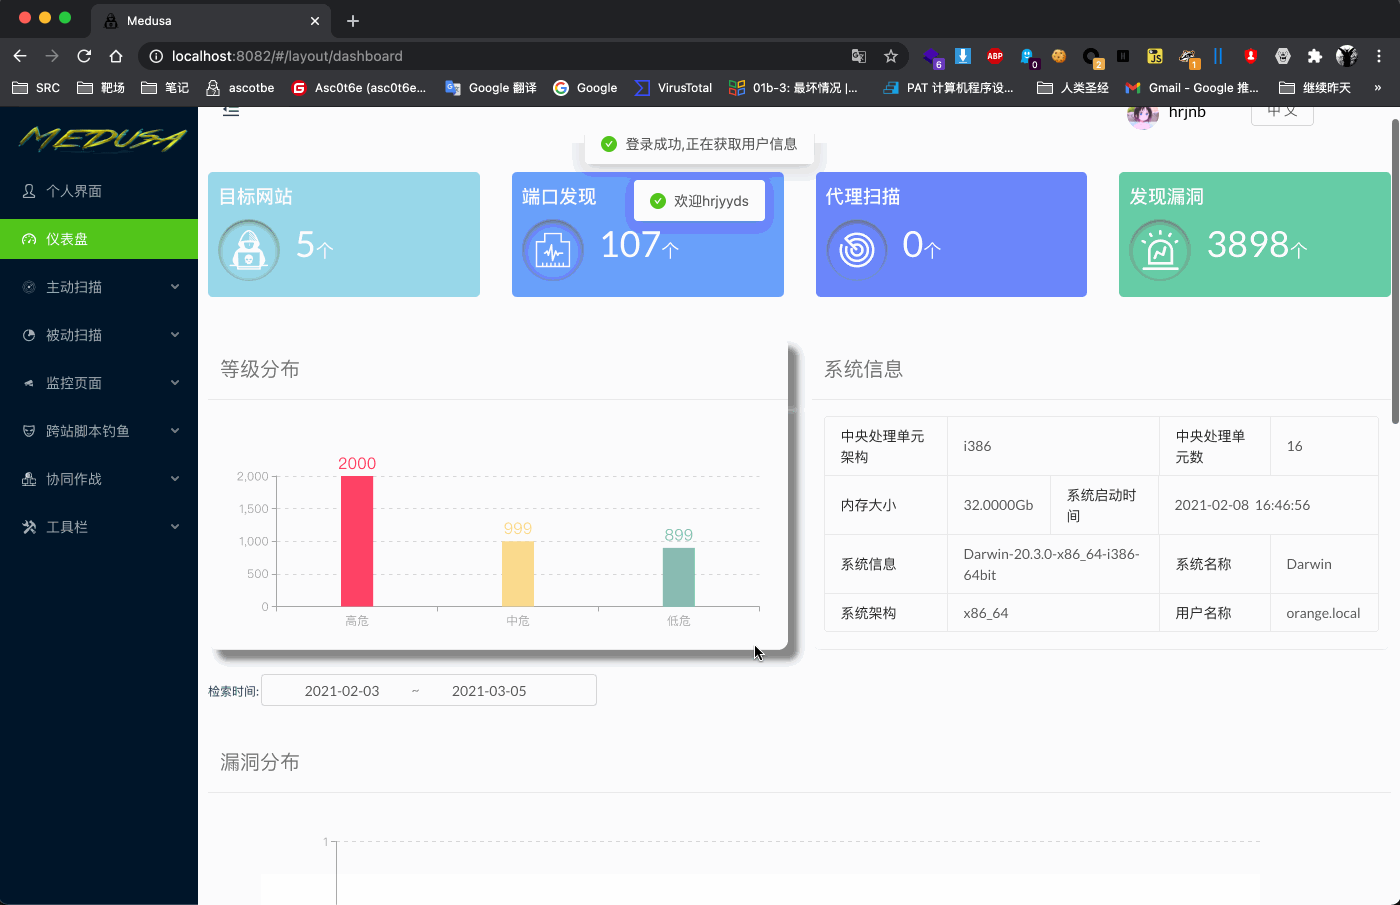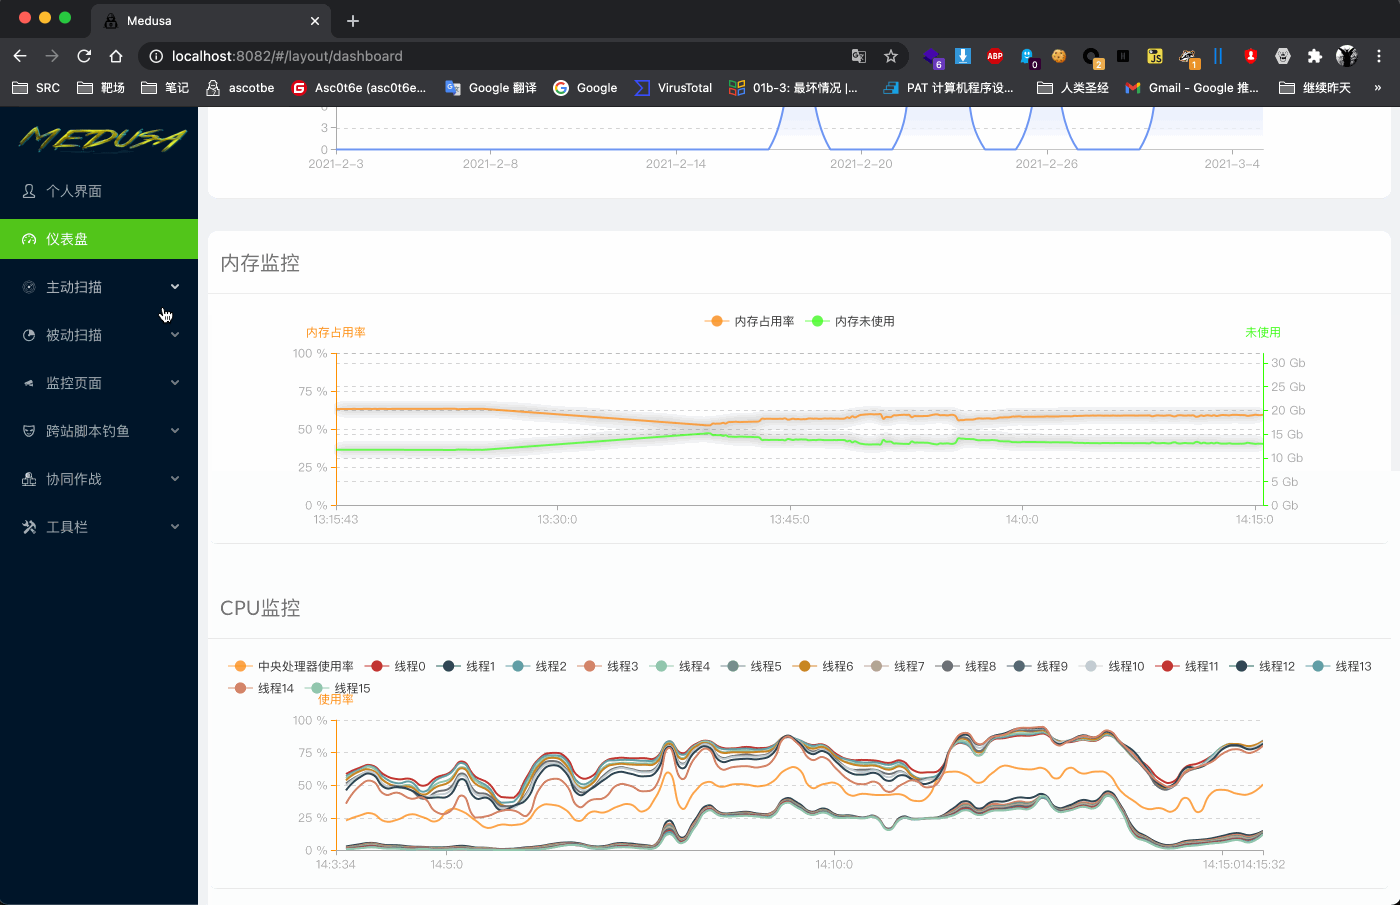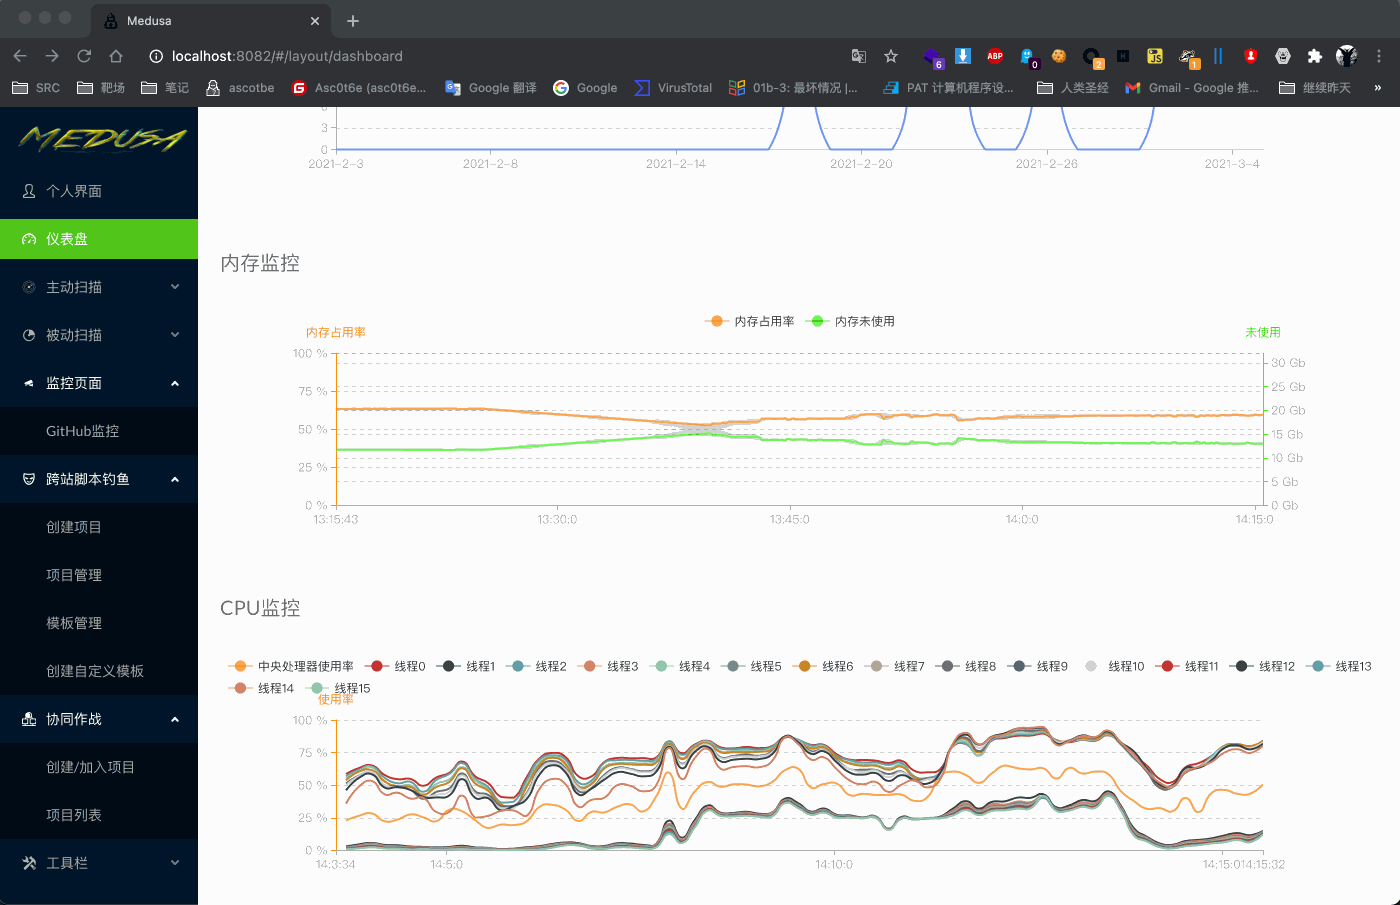
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中
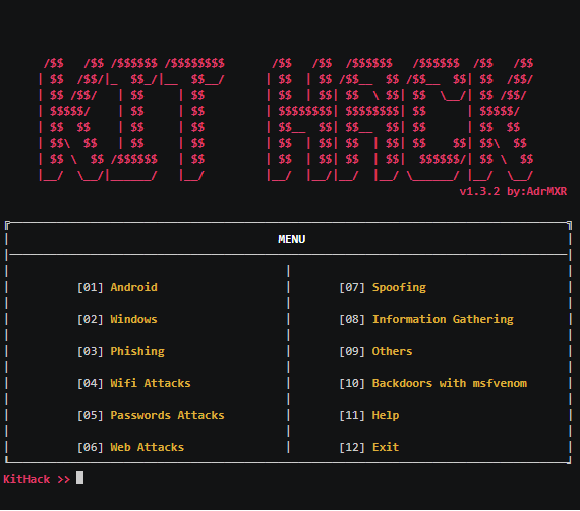 adrmxr/kithack
Hacking tools pack & backdoors generator.
 kgretzky/evilginx
PLEASE USE NEW VERSION: https://github.com/kgretzky/evilginx2
 alteredsecurity/365-stealer
Automates Illicit Consent Grant attacks against Azure/O365 tenants to steal refresh tokens, exfiltrate emails/OneDrive data, and create malicious…
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 s4vitar/eviltrust
Herramienta ideal para el despliegue automatizado de un Rogue AP con capacidad de selección de plantilla + 2FA. No requiere de conexión cableada.
 kgretzky/evilqr
Proof-of-concept to demonstrate dynamic QR swap phishing attacks in practice.
 antisnatchor/phishlulz
Automated phishing campaign toolset that spawns dedicated AWS EC2 instances with integrated PhishingFrenzy and BeEF, plus subdomain discovery and…
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
 jumpseclabs/tokenflare
Serverless AITM Simulation Framework for Entra ID and M365
 redbyte1337/credspy
Entra ID user enumeration and auth method discovery via the public GetCredentialType API
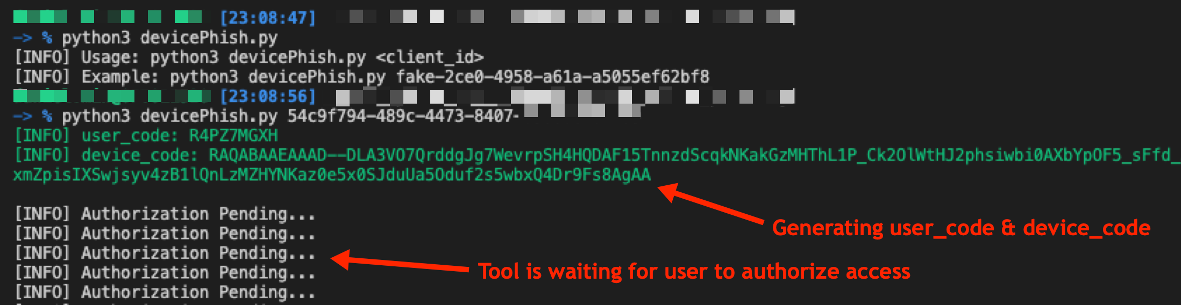 optiv/microsoft365_devicephish
A proof-of-concept script to conduct a phishing attack abusing Microsoft 365 OAuth Authorization Flow
 rnalter/thundercloud
Cloud Exploit Framework
 praetorian-inc/oauthseeker
A malicious OAuth application that can be leveraged for both internal and external phishing attacks targeting Microsoft Azure and Office365 users.
 secdev02/easytokens
Kali365 - EvilTokens Replica