
CVE-2025-40778
 nehkark/cve-2025-40778
Proof-of-concept demonstrating DNS cache poisoning via additional record injection in BIND 9, with tools to validate and exploit CVE-2025-40778 for…
dns-analysiseducationexploitation+3
6
nehkark/cve-2025-40778Proof-of-concept demonstrating DNS cache poisoning via additional record injection in BIND 9, with tools to validate and exploit CVE-2025-40778 for…
 husam212/mitmer
Automated man-in-the-middle attack tool.
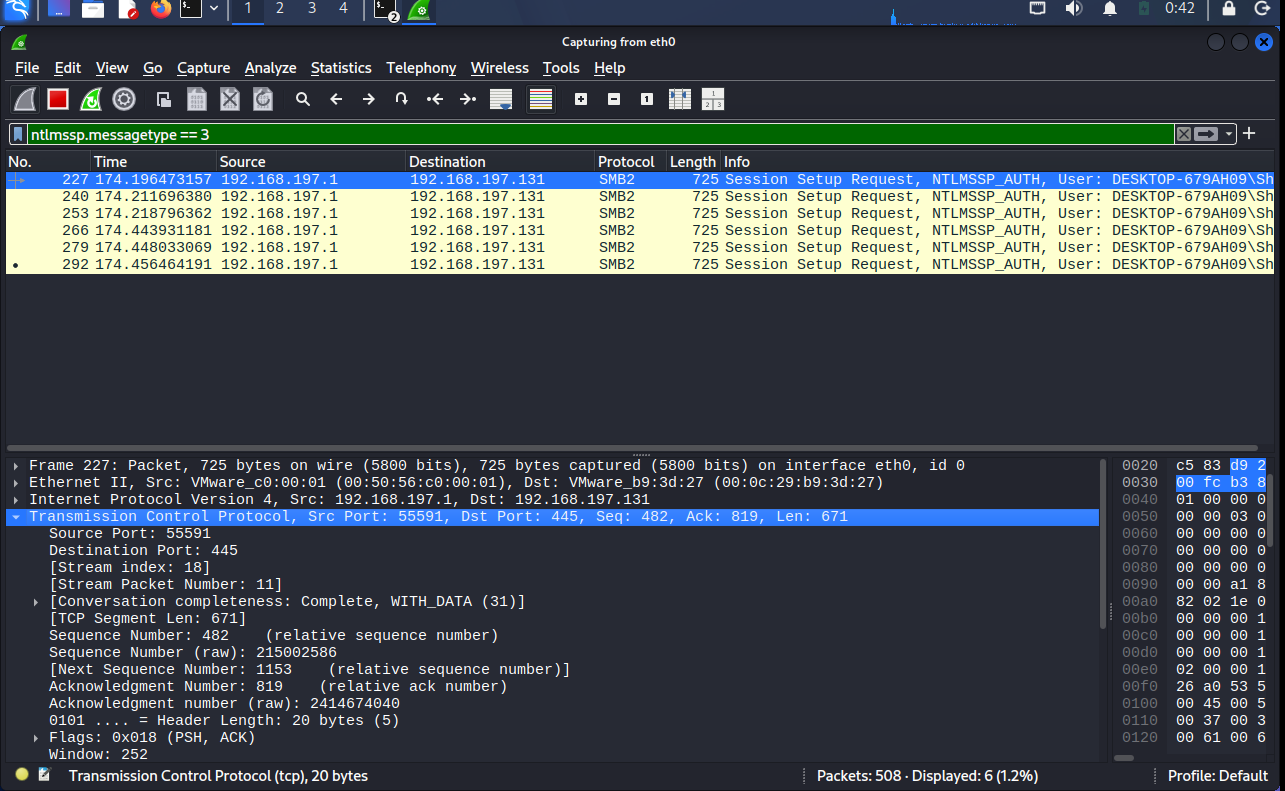 rahultb-sec/cve-2026-33829-writeup
Vulnerability Case Study: CVE-2026-33829 (Windows Snipping Tool NTLM Coercion)
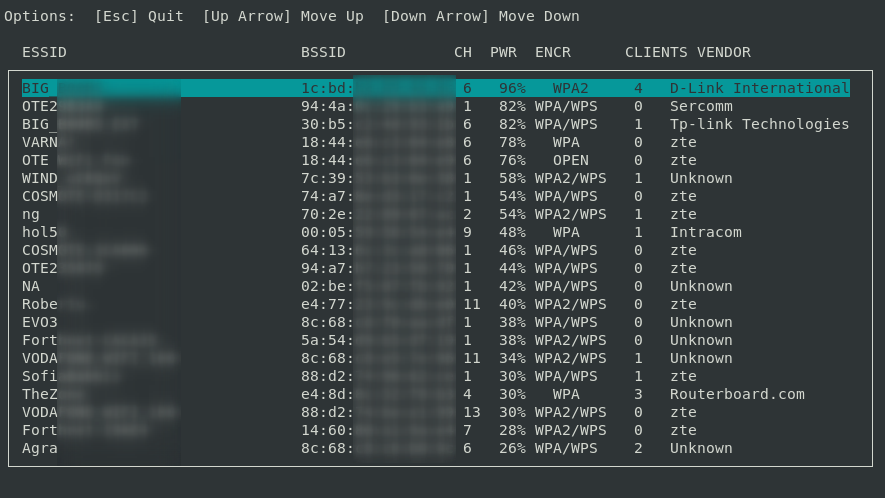 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 jh00nbr/phishruffus
Intelligent threat hunter and phishing servers
 marten4n6/evilosx
An evil RAT (Remote Administration Tool) for macOS / OS X.
 theresafewconors/sooty
The SOC Analysts all-in-one CLI tool to automate and speed up workflow.
 initstring/evil-ssdp
Spoof SSDP replies and create fake UPnP devices to phish for credentials and NetNTLM challenge/response.
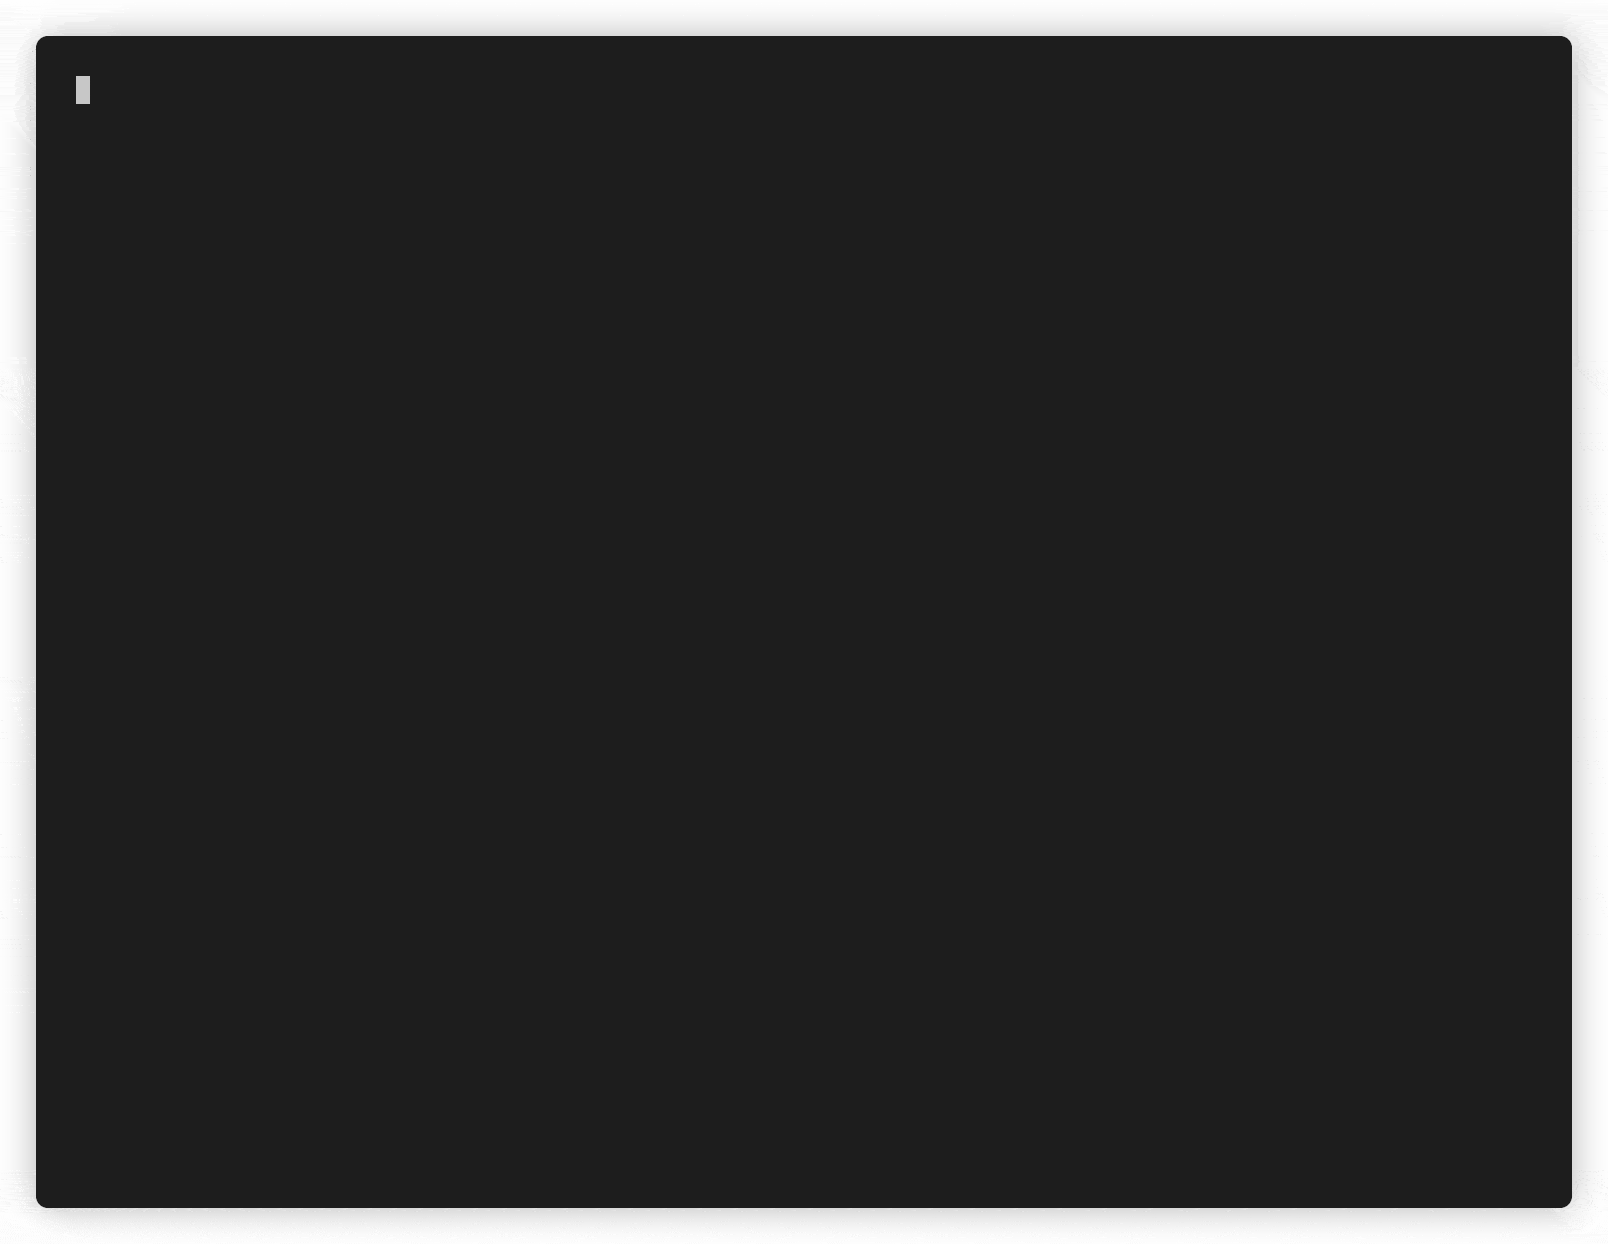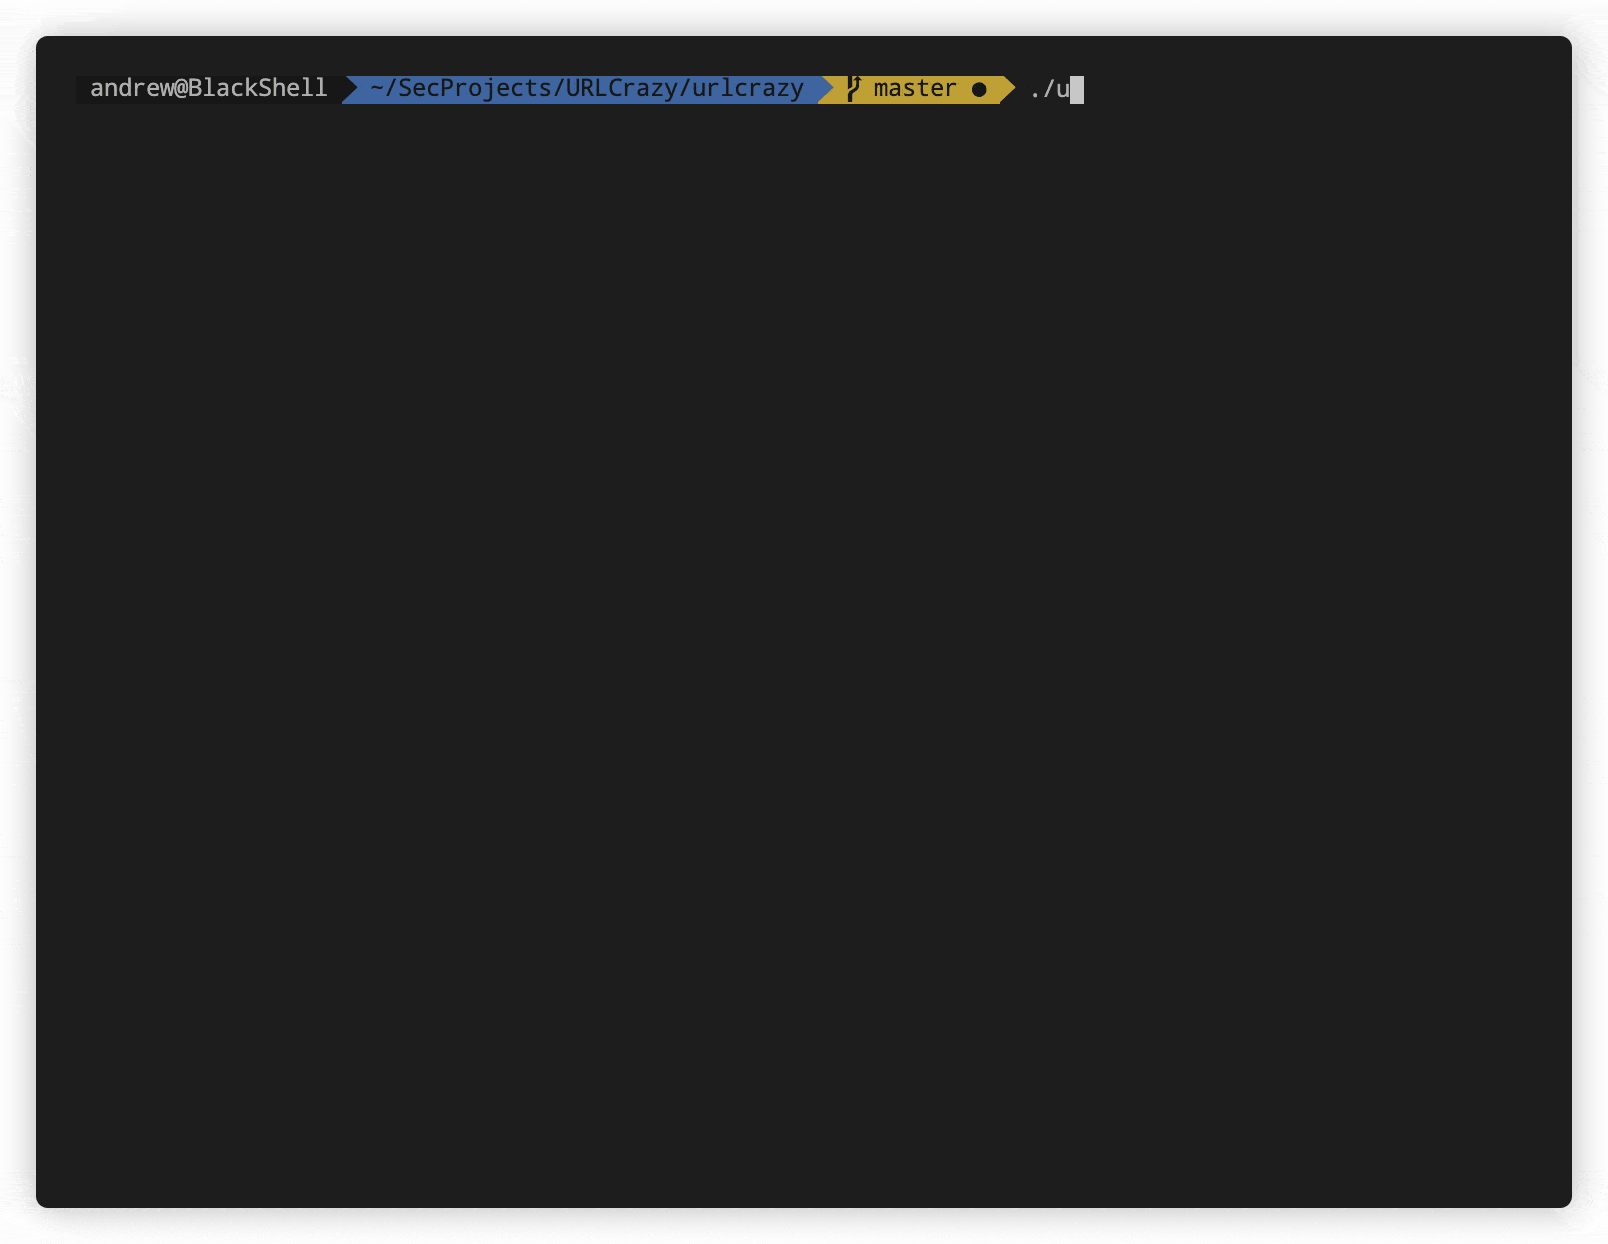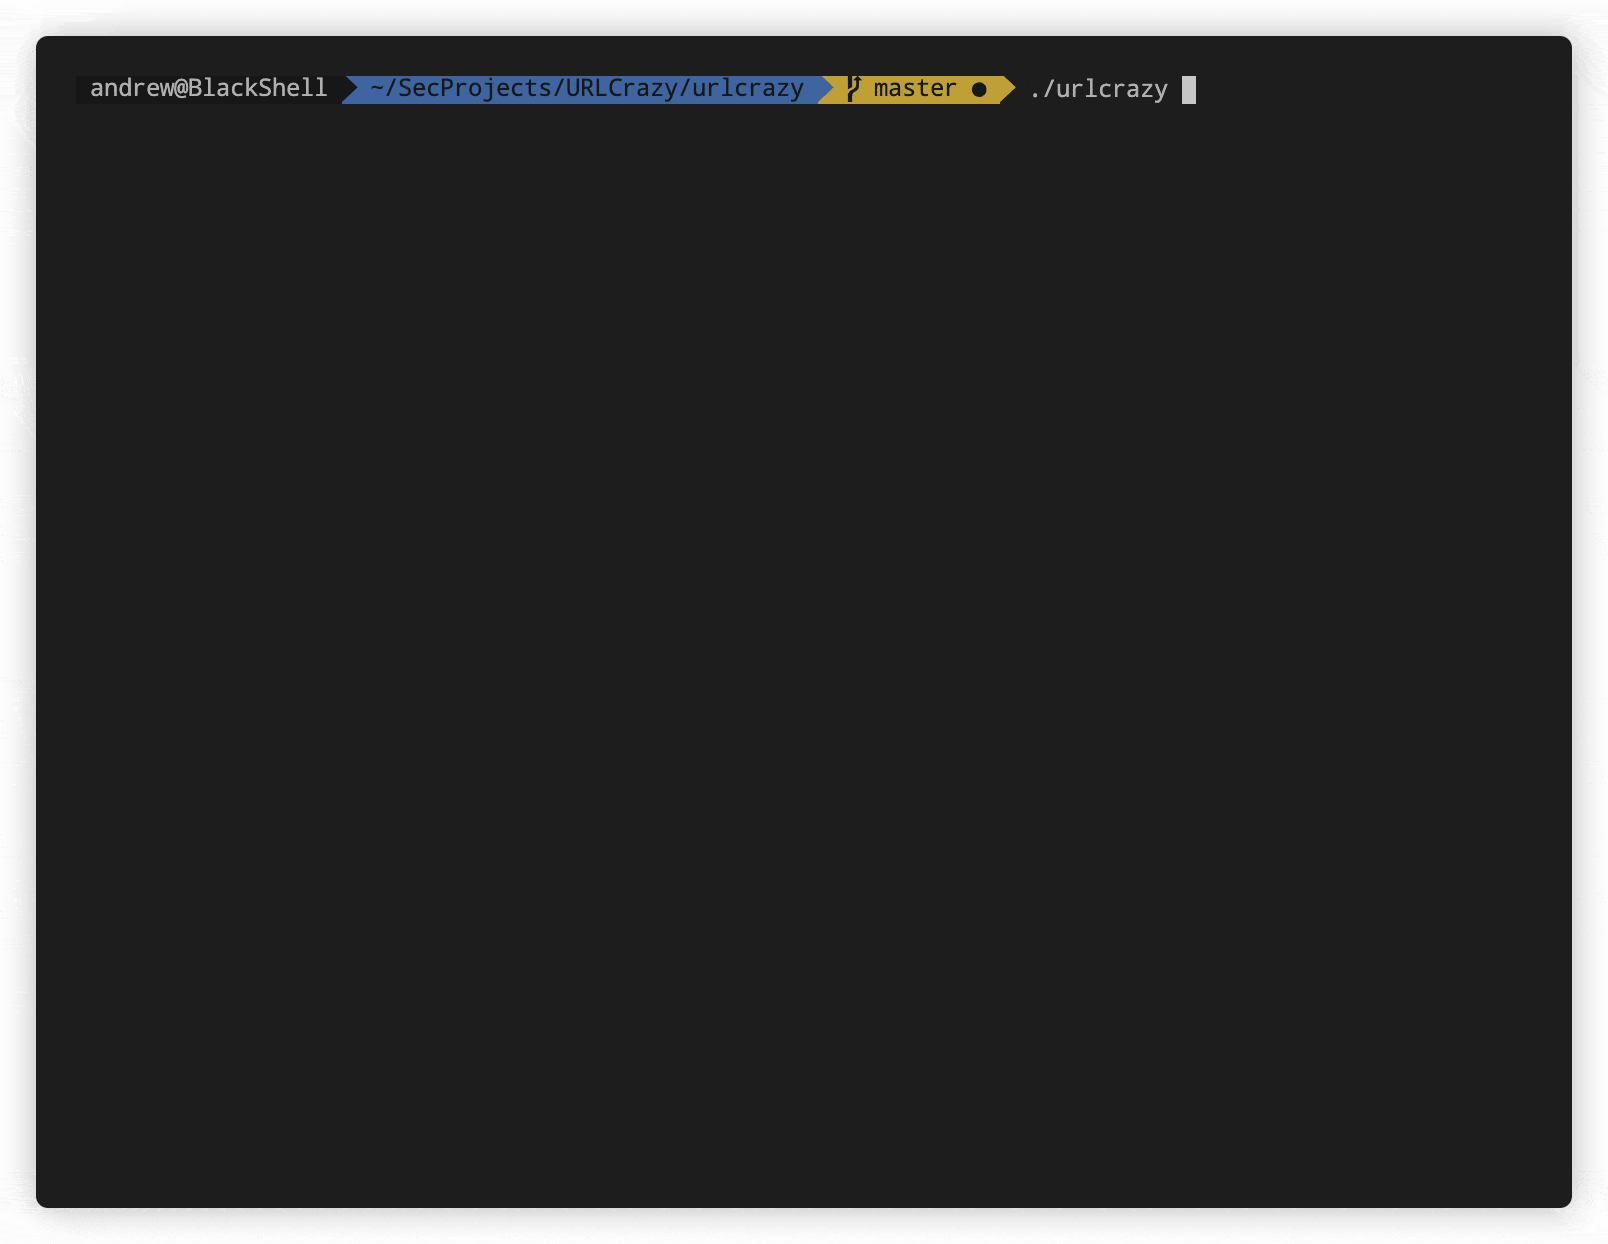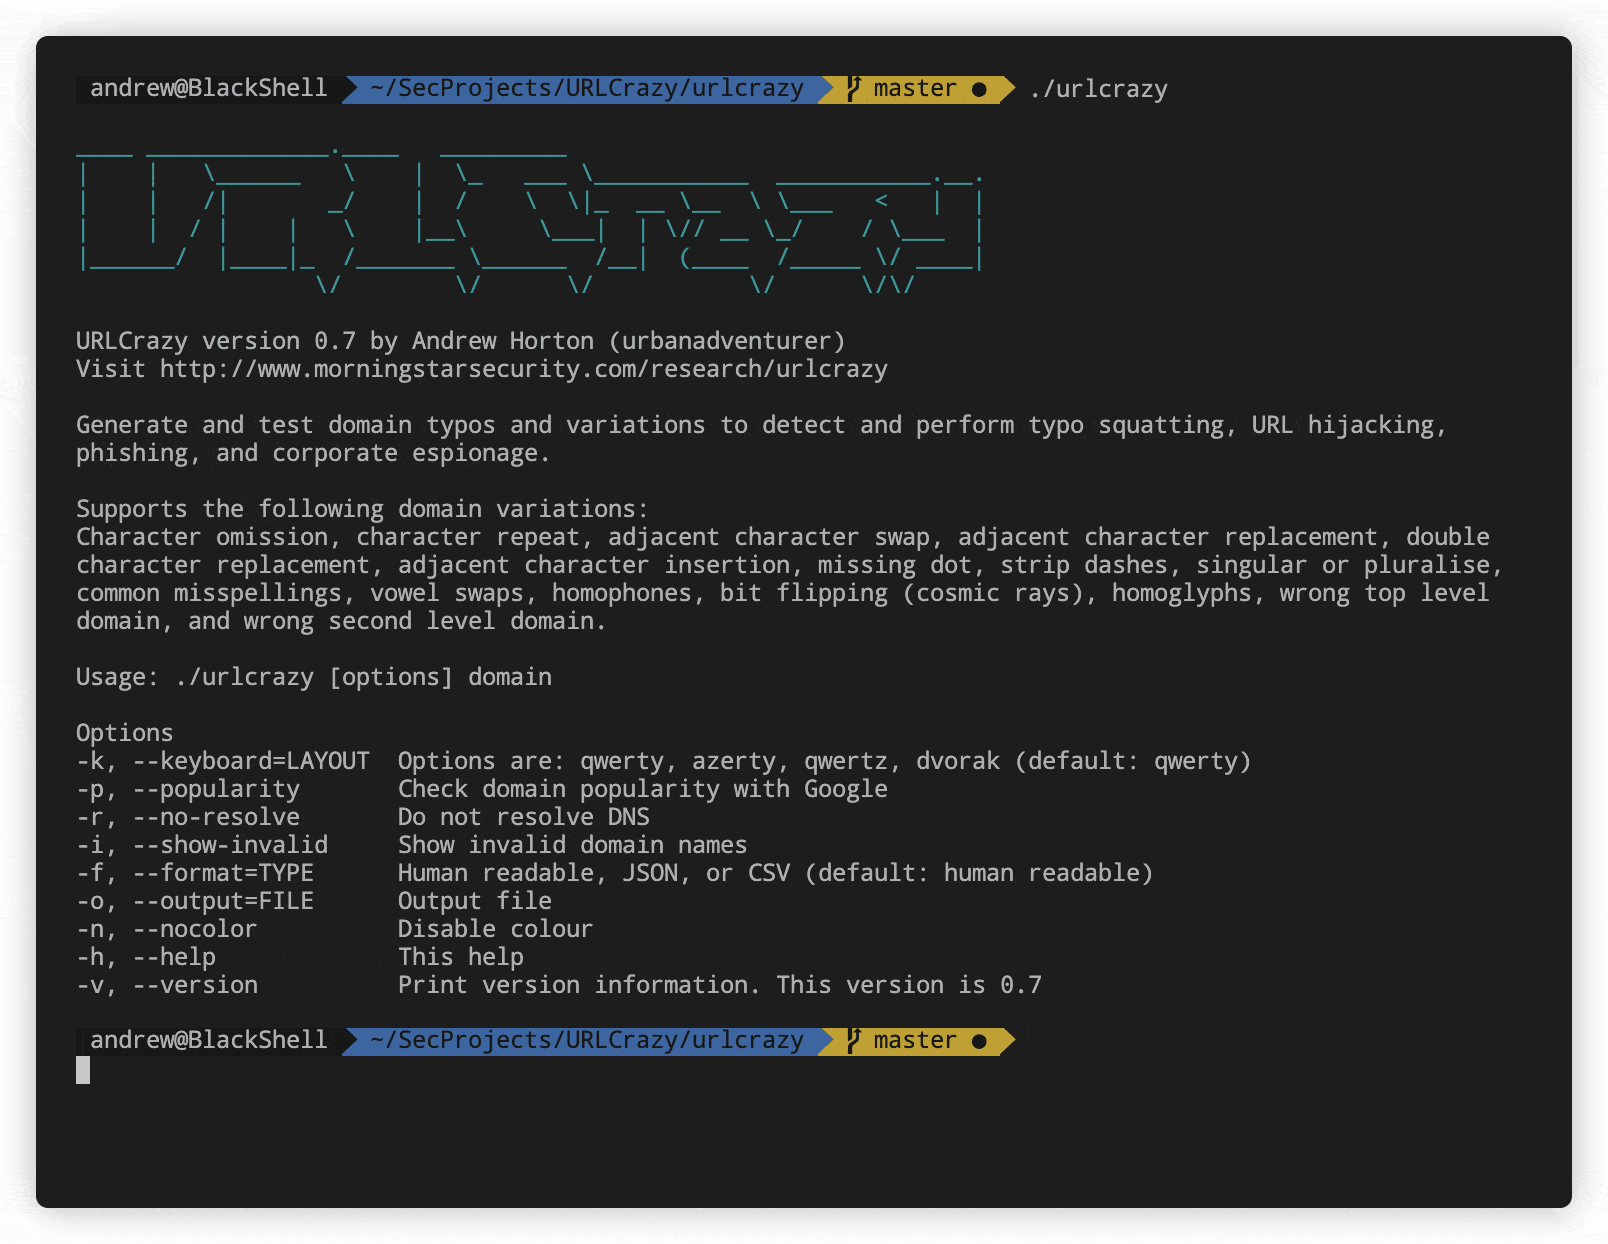 urbanadventurer/urlcrazy
Generate and test domain typos and variations to detect and perform typo squatting, URL hijacking, phishing, and corporate espionage.
 telefonicatc2tech/typodetect
Detects active domain mutations to prevent phishing and smishing. Uses IANA TLDs, blockchain DNS validation, and DoH malware reports. Outputs JSON or…
 atenreiro/opensquat
OSINT tool that detects domain squatting, typosquatting, and phishing look-alikes by monitoring newly registered domains against brand keywords with…
