

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
138 results
impacket preview

impacket

GitHubfortra/impacket

Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…

authenticationcommand-and-controldatabase-security+17
16.1k
12h 37m ago
merlin preview

merlin

GitHubne0nd0g/merlin

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

command-and-controldata-exfiltrationexploit-frameworks+10
5.6k1 year ago
APTs-Adversary-Simulation preview

APTs-Adversary-Simulation

GitHubs3n4t0r-0x0/apts-adversary-simulation

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…

adversarial-attackcommand-and-controleducation+9
1.1k10 days ago
SharpGPOAbuse preview

SharpGPOAbuse

GitHubreverseclabs/sharpgpoabuse

SharpGPOAbuse is a .NET application written in C# that can be used to take advantage of a user's edit rights on a Group Policy Object (GPO) in order…
exploitationlateral-movementpenetration-testing+4
1.4k5 years ago
SharpSploit preview

SharpSploit

GitHubcobbr/sharpsploit

SharpSploit is a .NET post-exploitation library written in C#
command-and-controlexploitationinformation-gathering+9
1.9k5 years ago
OffensiveVBA preview

OffensiveVBA

GitHubs3cur3th1ssh1t/offensivevba

This repo covers some code execution and AV Evasion methods for Macros in Office documents
curated-resourceseducationids-ips-evasion+7
1.3k4 years ago
PersistenceSniper preview

PersistenceSniper

GitHublast-byte/persistencesniper

Powershell module that can be used by Blue Teams, Incident Responders and System Administrators to hunt persistences implanted in Windows machines.…
defensive-toolsforensicsincident-response+1
2.1k1 year ago
Awesome-RedTeam-Cheatsheet preview

Awesome-RedTeam-Cheatsheet

GitHubristbs/awesome-redteam-cheatsheet

Red Team Cheatsheet in constant expansion.

curated-resourceseducationlateral-movement+4
1.3k3 years ago
BEAR-C2 preview

BEAR-C2

GitHubs3n4t0r-0x0/bear-c2

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
6879 days ago
Vegile preview

Vegile

GitHubscreetsec/vegile

This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…
exploit-frameworkslateral-movementpayload-generation+4
7547 years ago
Lilith preview

Lilith

GitHubwerkamsus/lilith

Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++
command-and-controlpayload-generationpenetration-testing+4
7487 years ago
ImpulsiveDLLHijack preview

ImpulsiveDLLHijack

GitHubknight0x07/impulsivedllhijack

C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…

binary-exploitationexploitationpersistence-mechanisms+2
5555 years ago
PurpleSharp preview

PurpleSharp

GitHubmvelazc0/purplesharp

PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…

adversarial-attackeducationlateral-movement+4
8481 year ago
thorse preview

thorse

GitHubpushpenderindia/thorse

THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
anti-botcommand-and-controlexploit-frameworks+6
6143 years ago
botnet-hackpack preview

botnet-hackpack

GitHubtreehacks/botnet-hackpack

Build a basic Command & Control botnet in C
command-and-controleducationmalware-analysis+3
4067 years ago
VEN0m-Ransomware preview

VEN0m-Ransomware

GitHubxm0kht4r/ven0m-ransomware

Fully undetectable and evasive ransomware written in Rust, leveraging a BYOVD technique to disable AV/EDR solutions on the infected systems.
encryption-decryption-toolsexploitationids-ips-evasion+6
3687 months ago
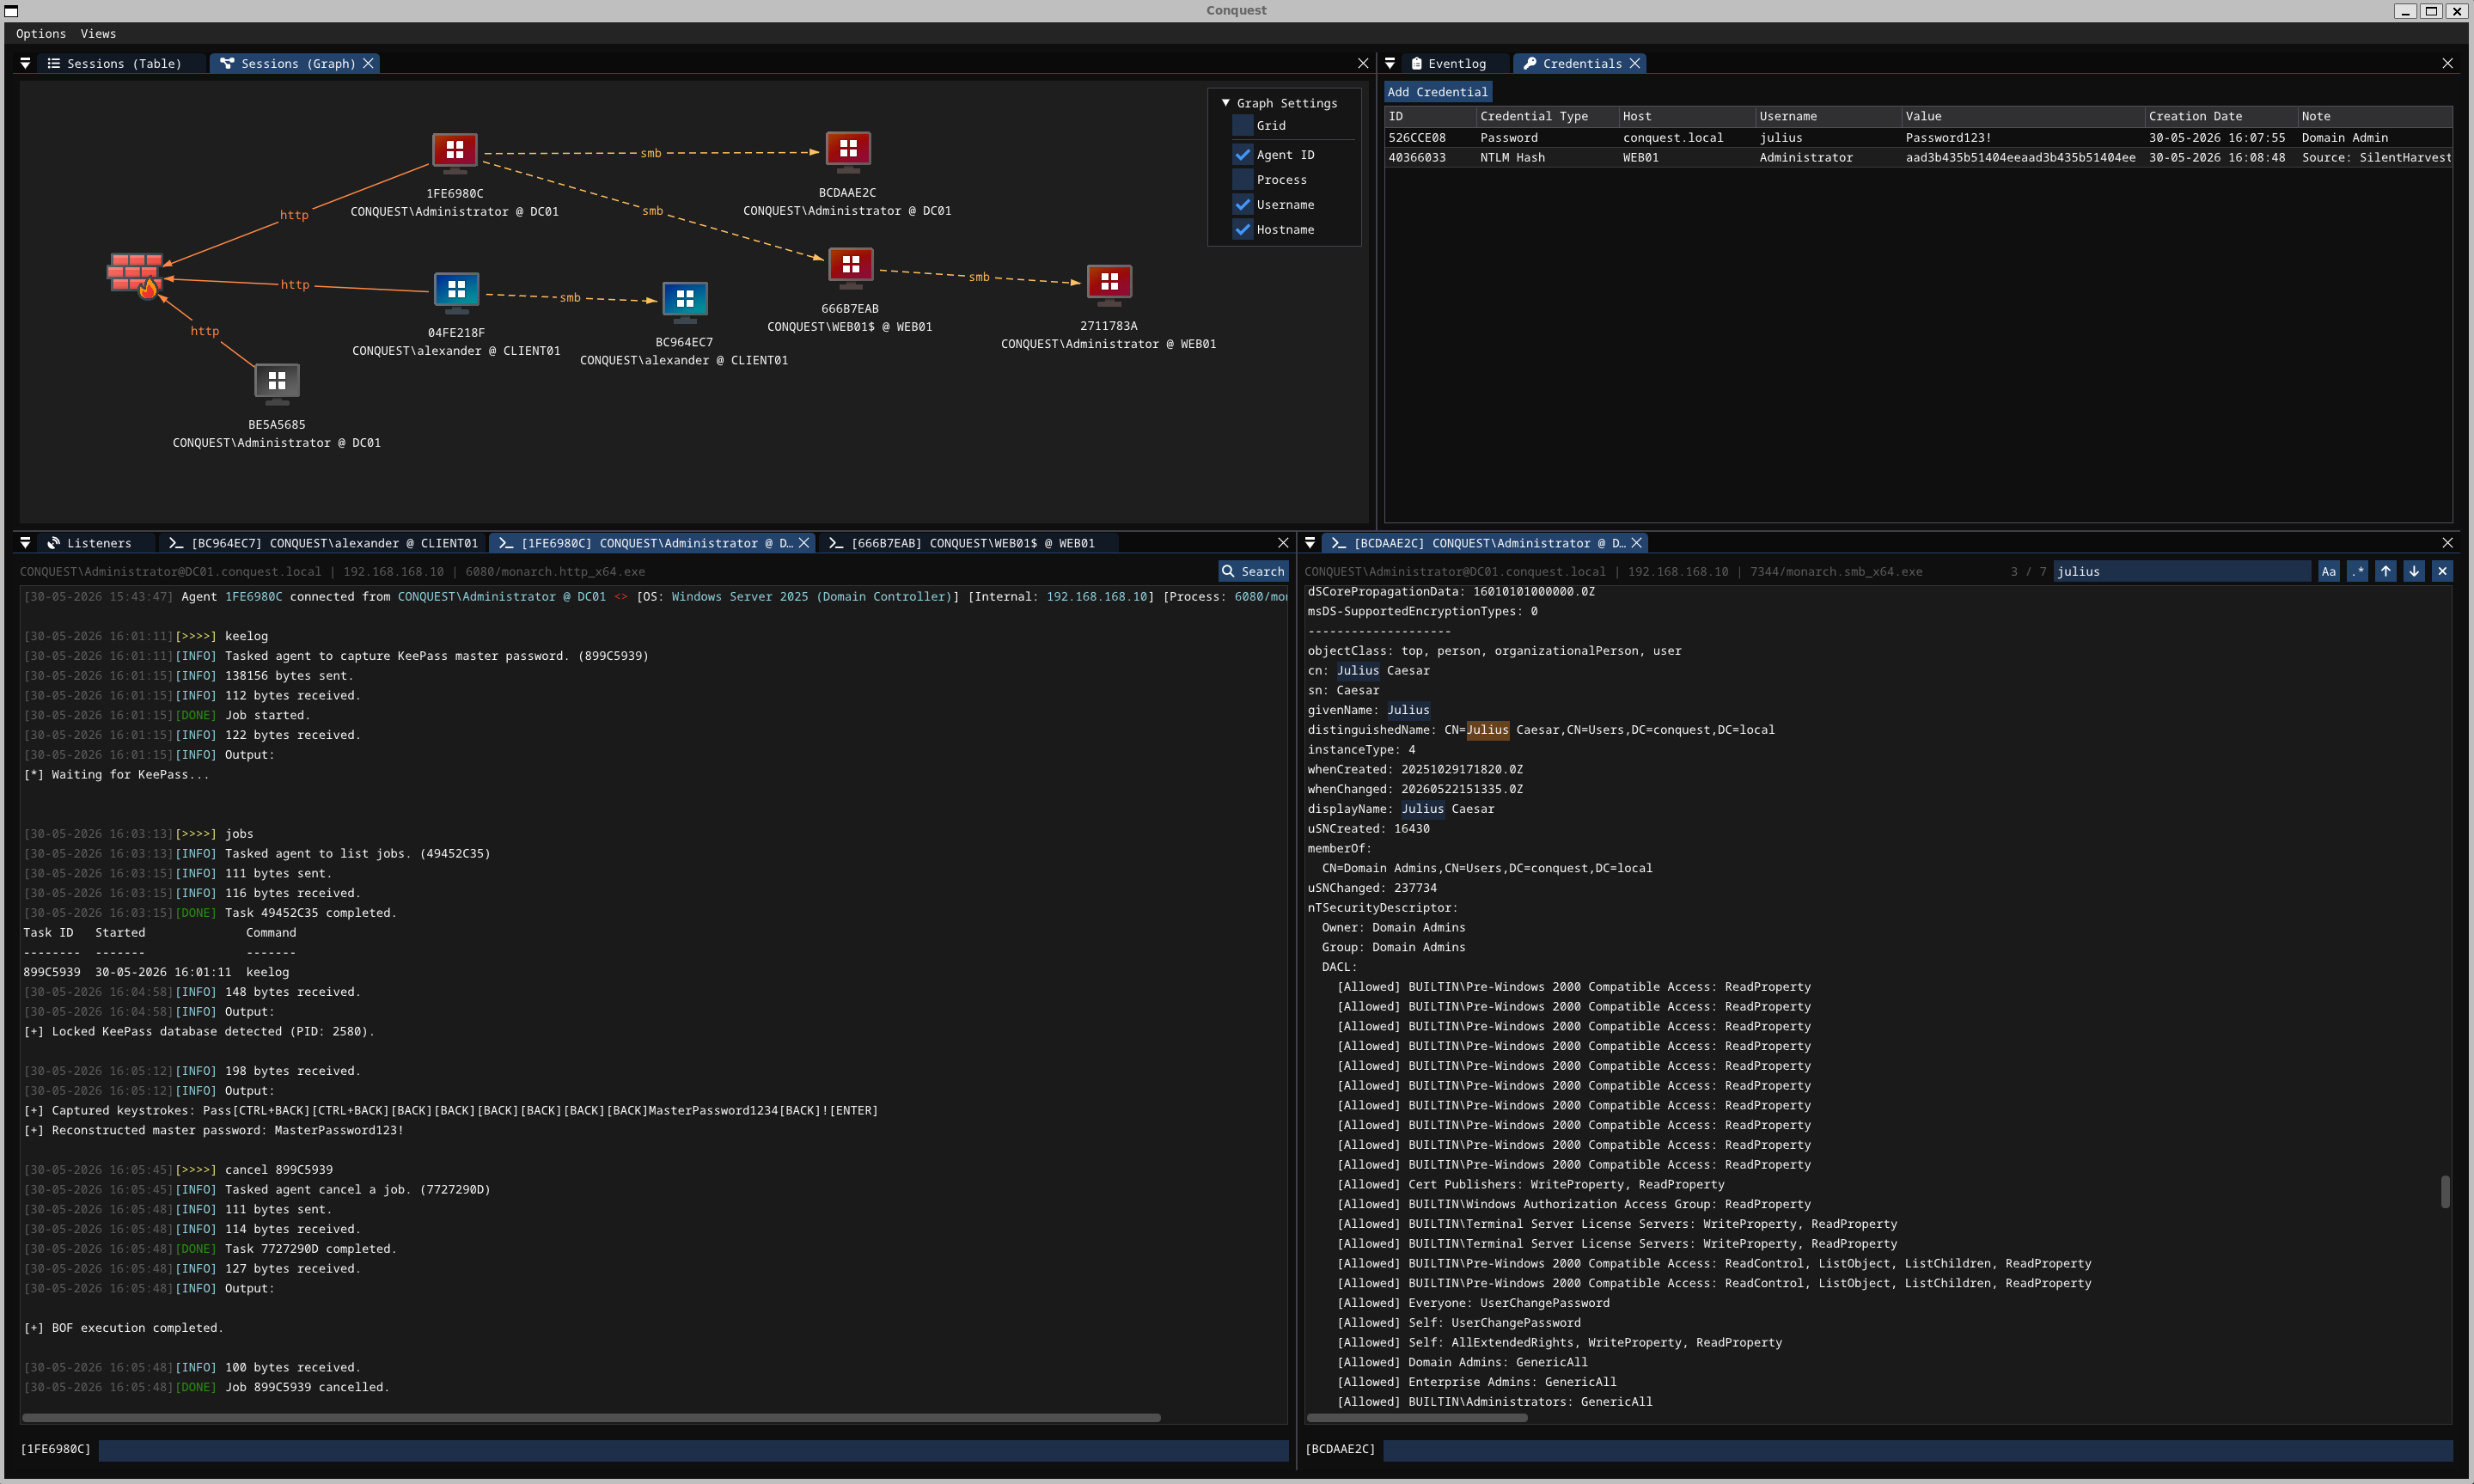
conquest preview

conquest

GitHubjakobfriedl/conquest

Conquest is a feature-rich and malleable command & control/post-exploitation framework developed in Nim.
command-and-controleducationexploit-frameworks+7
4222 months ago
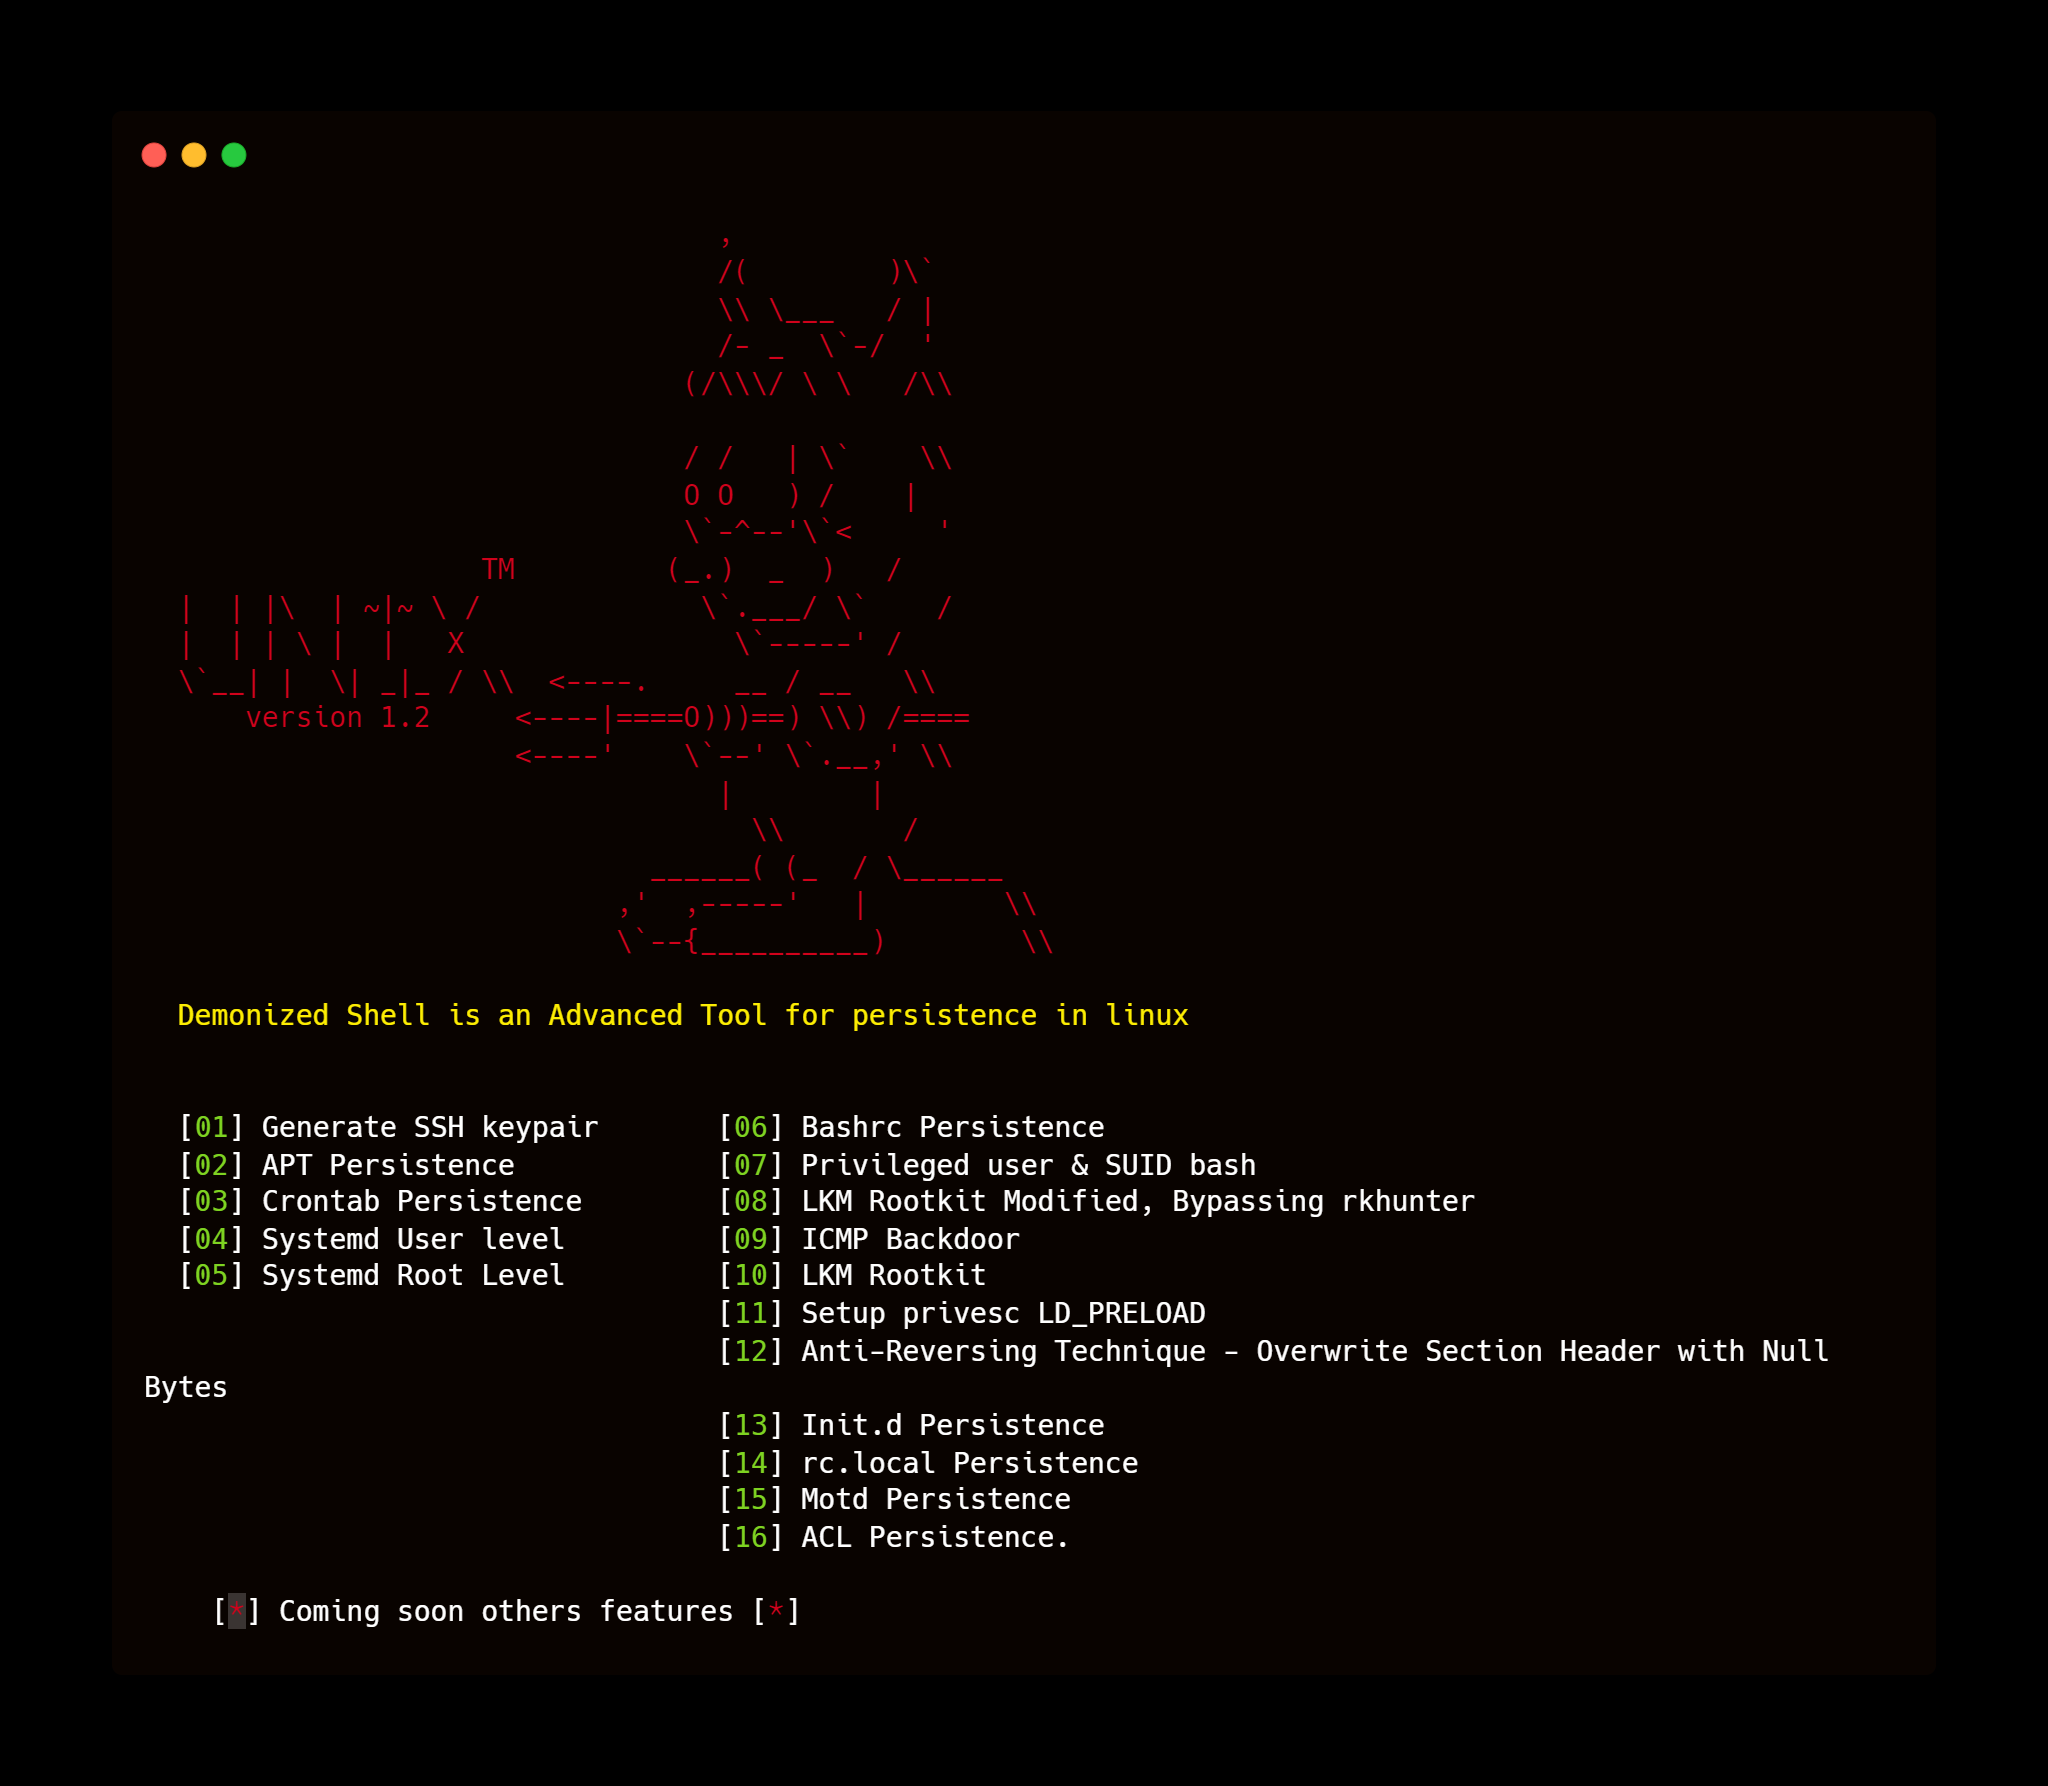
D3m0n1z3dShell preview

D3m0n1z3dShell

GitHubmatheuzsecurity/d3m0n1z3dshell

Demonized Shell is an Advanced Tool for persistence in linux.

persistence-mechanismspost-exploitationprivilege-escalation+1
4591 year ago
Previous12…8Next