

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
19 results
r77-rootkit preview

r77-rootkit

GitHubbytecode77/r77-rootkit

Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
command-and-controldefensive-toolsids-ips-evasion+6
2.2k
2 months ago
SigFlip preview

SigFlip

GitHubmed0x2e/sigflip

SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
binary-analysiscode-analysisdefensive-tools+5
1.3k3 years ago
CS-Remote-OPs-BOF preview

CS-Remote-OPs-BOF

GitHubtrustedsec/cs-remote-ops-bof

Remote operations commands implemented using Beacon Object Files
authenticationencryption-decryption-toolslateral-movement+6
1.2k2 months ago
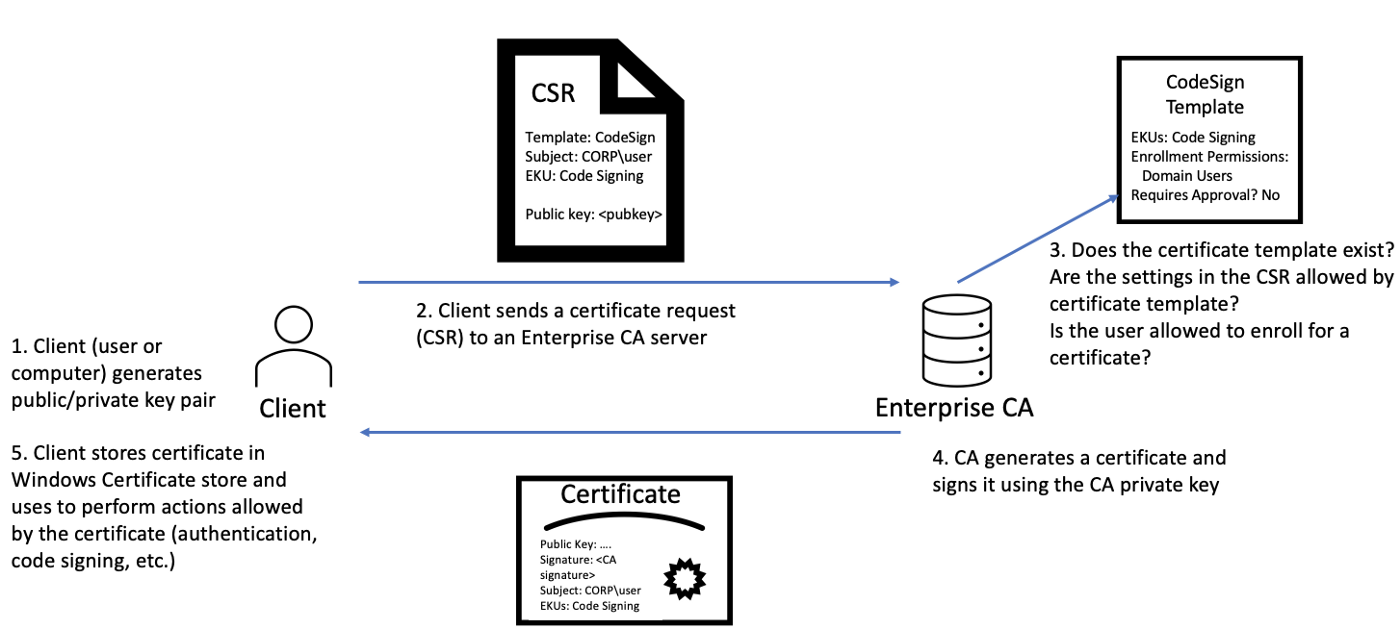
ForgeCert preview

ForgeCert

GitHubghostpack/forgecert

Forge certificates for Active Directory authentication using stolen Certificate Authority private keys, enabling persistent domain access with forged…

authenticationexploitationpayload-generation+1
7133 years ago
NimSyscallPacker preview

NimSyscallPacker

GitHubs3cur3th1ssh1t/nimsyscallpacker

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
binary-exploitationexploitationlateral-movement+7
21710 days ago
CobaltWhispers preview

CobaltWhispers

GitHubnvisosecurity/cobaltwhispers

CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
adversarial-attackcommand-and-controlids-ips-evasion+4
2413 years ago
swarmer preview

swarmer

GitHubpraetorian-inc/swarmer

A tool to convert windows registry export files into windows hive files that can be used to replace NTUSER.MAN

persistence-mechanismspost-exploitationprivilege-escalation+1
1837 months ago
spybrowse preview

spybrowse

GitHub1d8/spybrowse

Code developed to steal certain browser config files (history, preferences, etc)
data-exfiltrationinformation-gatheringmalware-analysis+2
636 years ago
macos_app_structure preview

macos_app_structure

GitHubyo-yo-yo-jbo/macos_app_structure

Educational deep dive into macOS app bundles, plist files, and launchd process behavior, with offensive security notes on packaging payloads as .app…
educationids-ips-evasionpayload-development+2
472 months ago
SkillsGuard preview

SkillsGuard

GitHubteycir/skillsguard

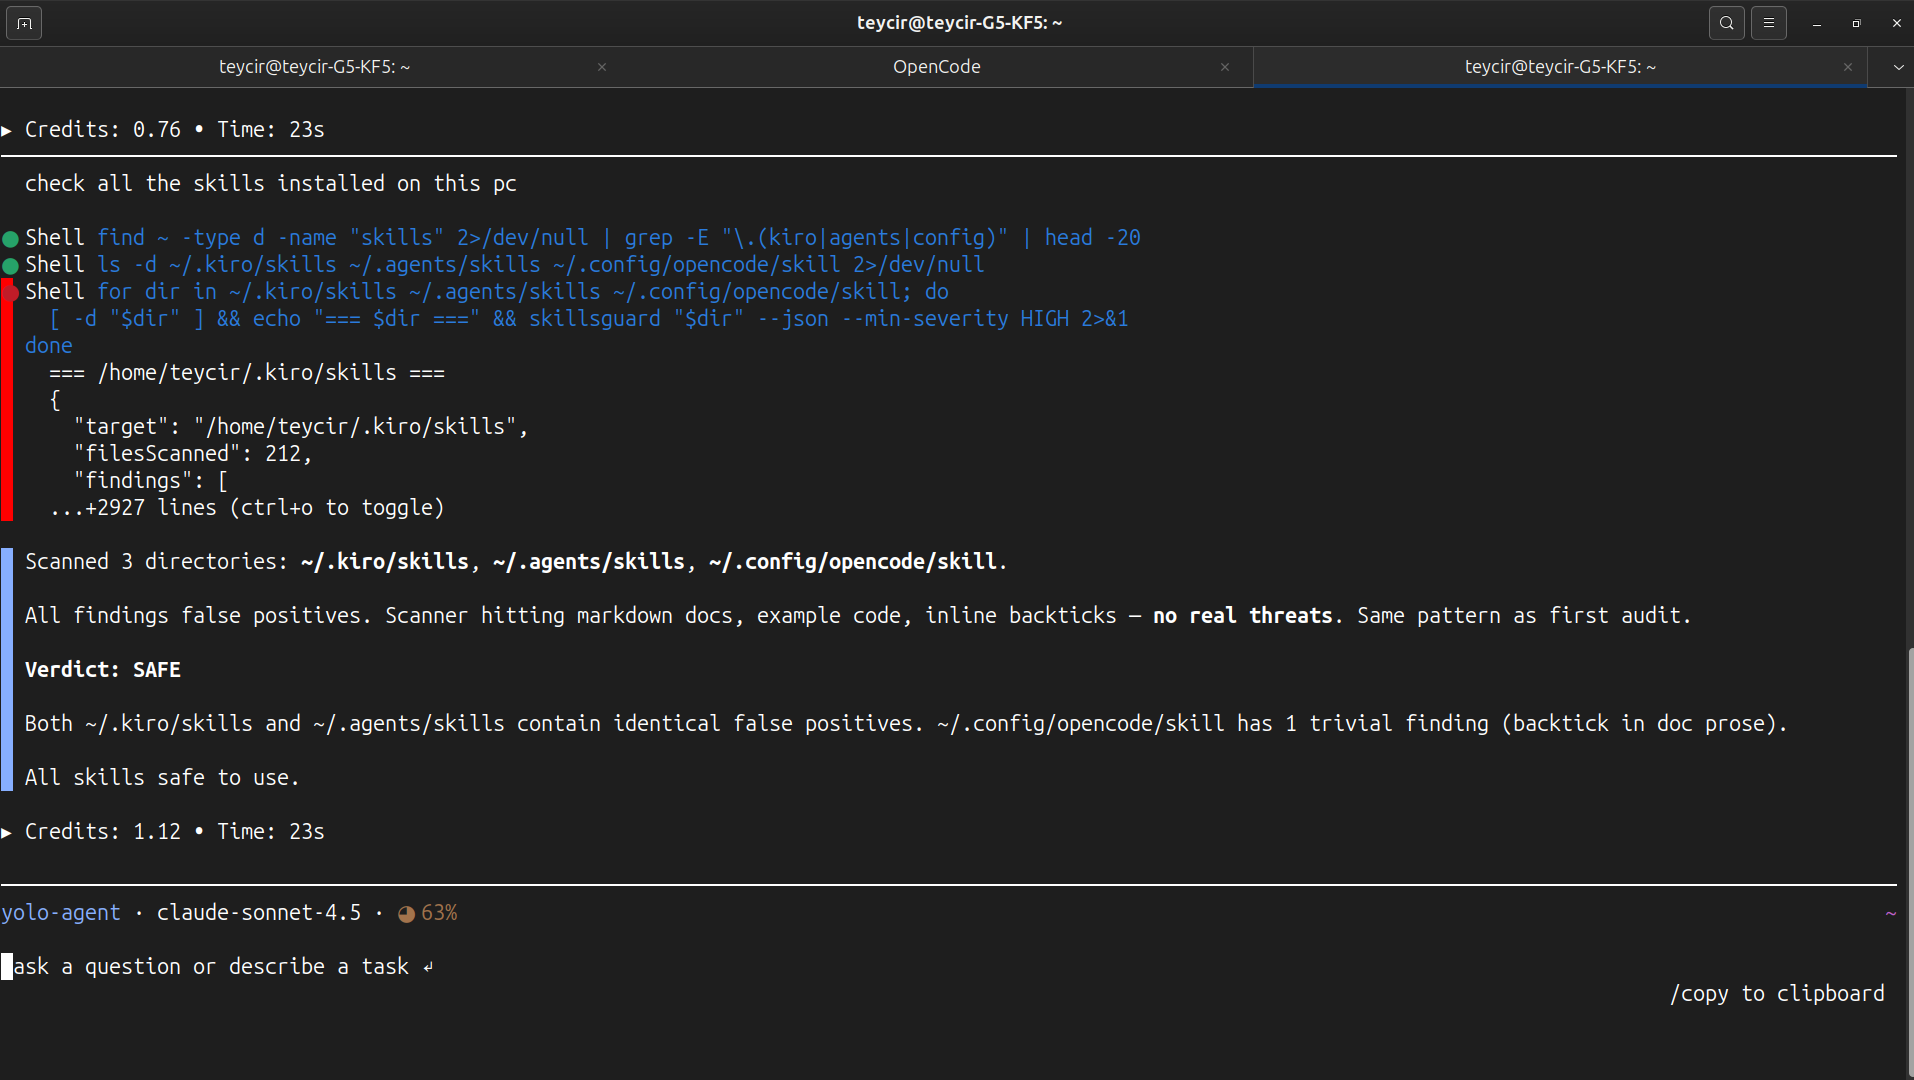
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
ai-securitycode-analysiscommand-and-control+8
153 months ago
LOLBAS preview

LOLBAS

GitHublolbas-project/lolbas

Living Off The Land Binaries And Scripts - (LOLBins and LOLScripts)
binary-analysiscurated-resourcesdefensive-tools+5
8.8k9 days ago
moukthar preview

moukthar

GitHubtomiwa-ot/moukthar

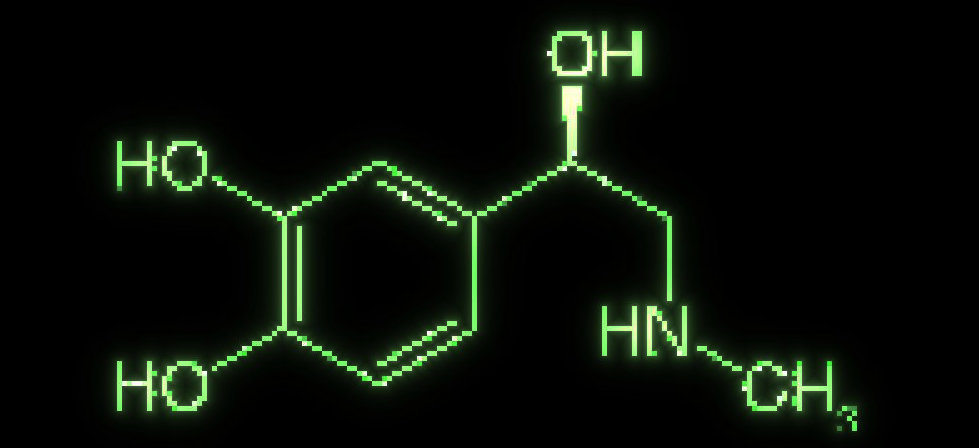
Android remote administration tool
android-securitycommand-and-controldata-exfiltration+6
67910 months ago
Adrenaline preview

Adrenaline

GitHubatomiczsec/adrenaline

C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.

command-and-controldefensive-toolsinformation-gathering+7
31721 days ago
cromos preview

cromos

GitHubjimywork/cromos

Cromos is a tool for downloading legitimate extensions of the Chrome Web Store and inject codes in the background of the application.
command-and-controldata-exfiltrationlateral-movement+5
1248 years ago
MoveEdr preview

MoveEdr

GitHubduhirsch/moveedr

Permanently disable EDRs as local admin

anti-botdefensive-toolsids-ips-evasion+5
1319 months ago
CVE-2025-8088-Multi-Document preview

CVE-2025-8088-Multi-Document

GitHubpentestfunctions/cve-2025-8088-multi-document

Exploit systems using older WinRAR without knowing their username (unlike other projects)
binary-exploitationeducationexploitation+4
351 year ago
WinRAR-CVE-2025-8088-Path-Traversal-PoC preview

WinRAR-CVE-2025-8088-Path-Traversal-PoC

GitHubpexlexity/winrar-cve-2025-8088-path-traversal-poc

Proof-of-Concept for CVE-2025-8088 vulnerability in WinRAR (path traversal via ADS)
binary-exploitationexploitationmalware-analysis+3
21 year ago
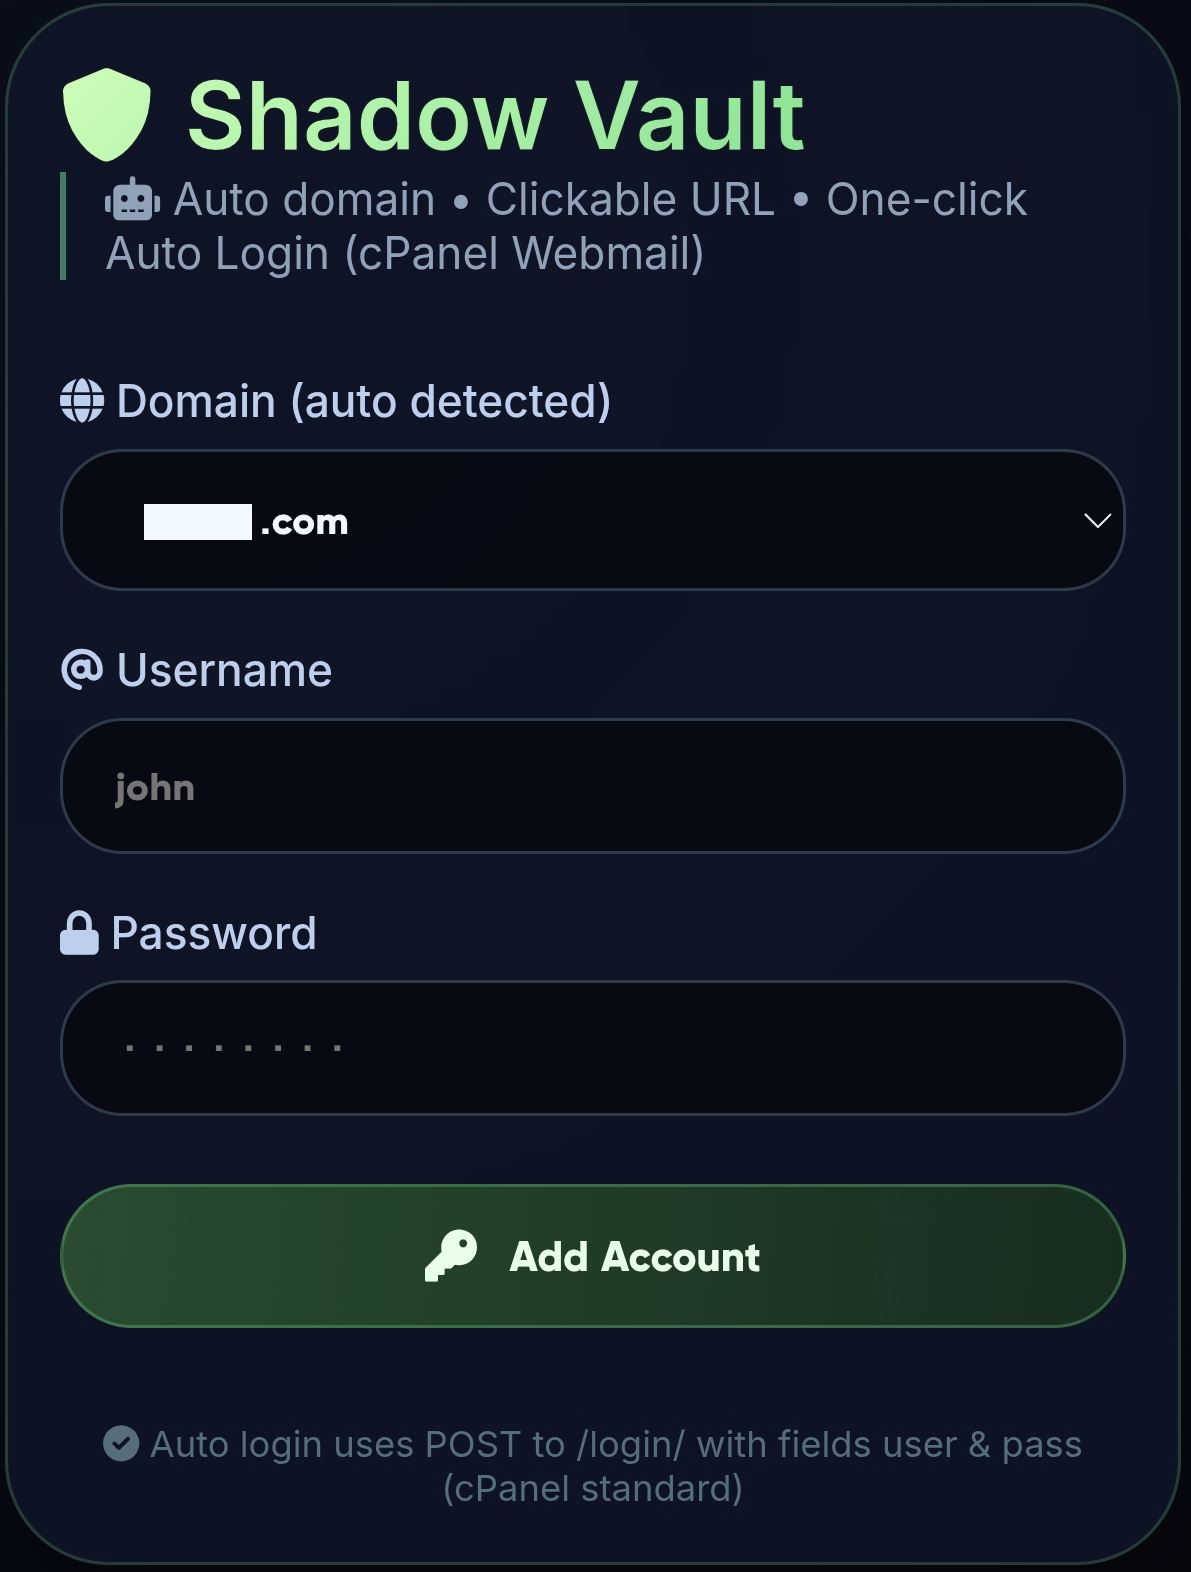
Shadow-Vault preview

Shadow-Vault

GitHubjenderal92/shadow-vault

Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.

authentication-authorizationemail-securityidentity-access-management+3
3 months ago
Previous12Next