
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
257 results
RATel preview

RATel

GitHubfrenchcisco/ratel

RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
command-and-controlencryption-decryption-toolspayload-generation+6
277
5 years ago
RevShell preview

RevShell

GitHubdragon56yt/revshell

A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…

command-and-controldata-exfiltrationeducation+8
24 months ago
Powershell-C2 preview

Powershell-C2

GitHubenigma0x3/powershell-c2

PowerShell-based command and control framework using website-hosted payloads for persistent remote access and post-exploitation on Windows systems.
command-and-controlpayload-generationpenetration-testing+3
5012 years ago
shepard preview

shepard

GitHubd3adzo/shepard

In progress persistent download/upload/execution tool using Windows BITS.
command-and-controldata-exfiltrationpersistence-mechanisms+3
415 years ago
THM-Tempest preview

THM-Tempest

GitHubczabatta/thm-tempest

TryHackMe SOC Level 1 — Follina CVE-2022-30190, Nim C2, Chisel, PrintSpoofer, backdoor accounts

command-and-controlctfdigital-forensics+9
3 months ago
Arduino-Netcat-Backdoor preview

Arduino-Netcat-Backdoor

GitHubdavidkowalk/arduino-netcat-backdoor

*Proof of concept* Attacks a Windows machine running Windows 7 or later, creating a persistent Backdoor.
command-and-controlexploitationhardware-hacking+7
56 years ago
Metamorph preview

Metamorph

GitHubsynacktiv/metamorph

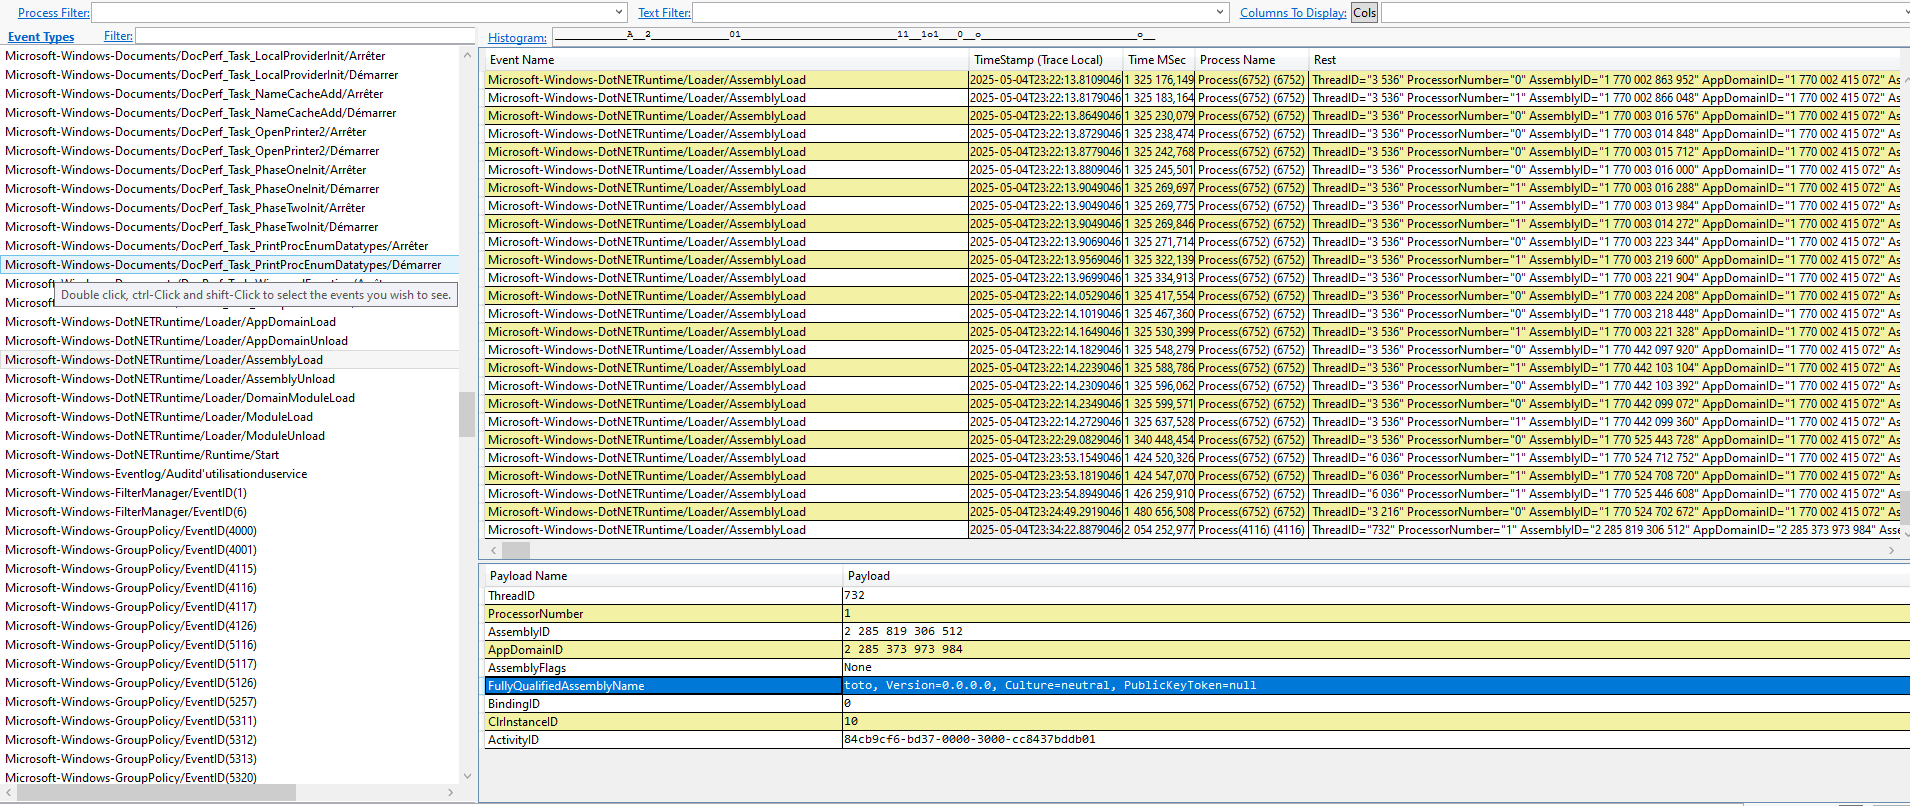
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
defensive-toolsincident-responseinformation-gathering+3
84 months ago
ToRat preview
Archived

ToRat

GitHubluantak/torat

ToRat is a Remote Administation tool written in Go using Tor as a transport mechanism and RPC for communication

command-and-controleducationpayload-generation+6
1.0k3 years ago
impacket preview

impacket

GitHubfortra/impacket

Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
authenticationcommand-and-controldatabase-security+17
16.1k4 days ago
CVE-2025-56799 preview

CVE-2025-56799

GitHubshinycolumn/cve-2025-56799

OS Command Injection Vulnerability via Cache Clearing Scheduler in Reolink Desktop Application
binary-exploitationexploitationmalware-analysis+3
111 months ago
malvinci preview

malvinci

GitHubgsoffmarket/malvinci

This simple but powerful script will introduce a new type of malware that will turn off the firewall, start an HTTP server, forward its port through…
command-and-controldata-exfiltrationpayload-development+3
592 years ago
Windows-Python-RAT preview

Windows-Python-RAT

GitHubthe404hacking/windows-python-rat

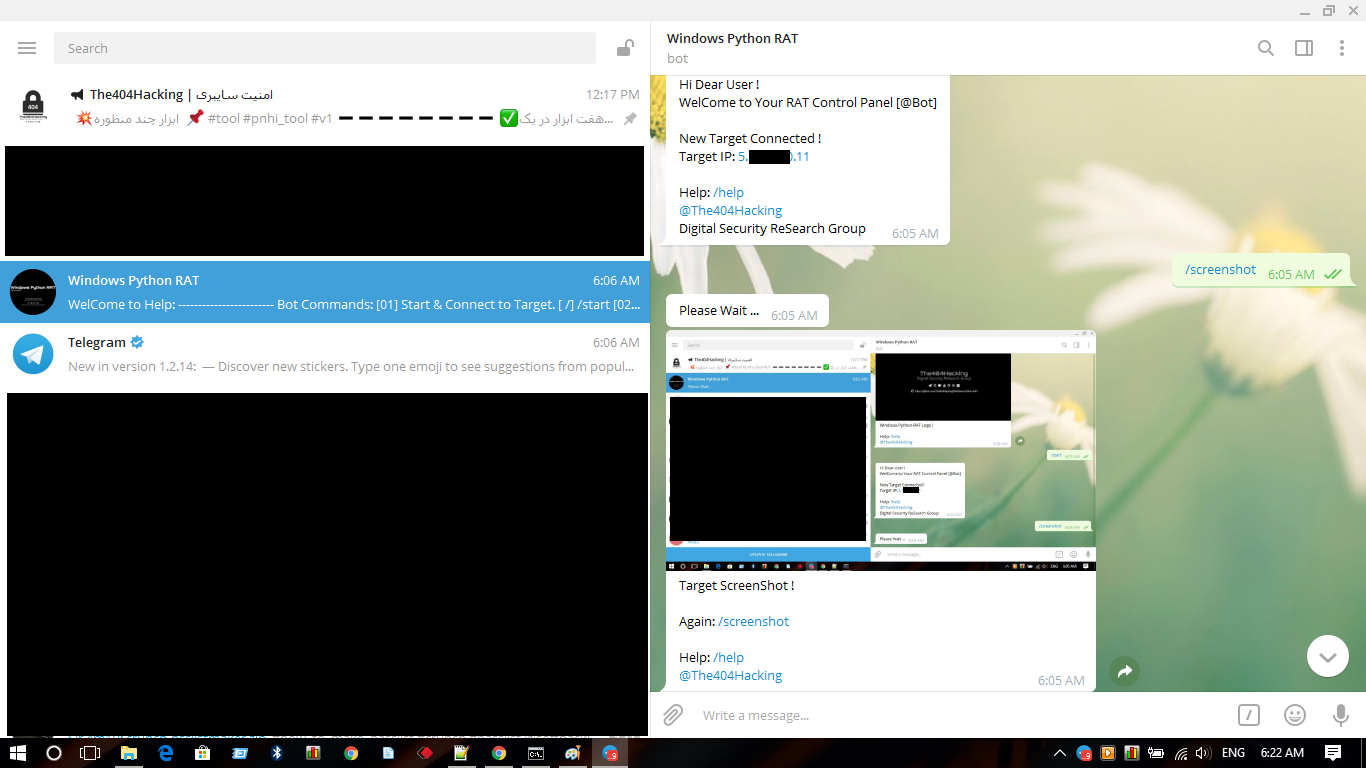
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
api-securitycommand-and-controlpayload-development+3
1186 years ago
paradoxiaRAT preview

paradoxiaRAT

GitHubquantumcore/paradoxiarat

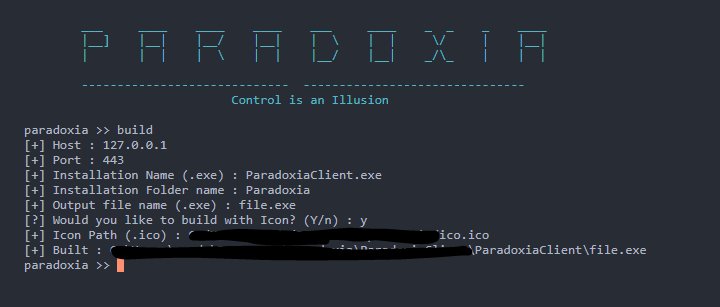
ParadoxiaRat : Native Windows Remote access Tool.
command-and-controlpassword-crackingpenetration-testing+4
8313 years ago
RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis preview

RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis

GitHubkaandemir993/redline-stealer-c2-defender-bypass-payload-analysis

"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…

command-and-controldata-exfiltrationmalware-analysis+4
11 month ago
RedbloodC2 preview

RedbloodC2

GitHubkira2040k/redbloodc2

Node.js command-and-control server with FUD payload generation, encrypted communication, session management, and modules for data exfiltration and…
command-and-controldata-exfiltrationencryption-decryption-tools+5
293 years ago
RAT-via-Telegram preview
Archived

RAT-via-Telegram

GitHubmvrozanti/rat-via-telegram

Windows Remote Administration Tool via Telegram
command-and-controldata-exfiltrationpassword-cracking+6
7127 years ago
FsquirtCPLPoC preview

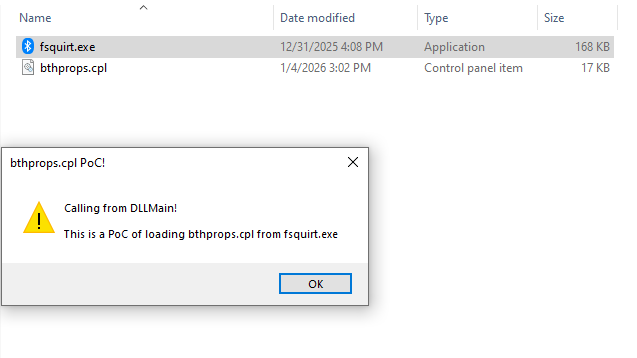
FsquirtCPLPoC

GitHubmhaskar/fsquirtcplpoc

PoC for generating bthprops.cpl module designed to be loaded by Fsquirt.exe LOLBin

binary-exploitationcommand-and-controlexploitation+5
1219 months ago
cromos preview

cromos

GitHubjimywork/cromos

Cromos is a tool for downloading legitimate extensions of the Chrome Web Store and inject codes in the background of the application.

command-and-controldata-exfiltrationlateral-movement+5
1248 years ago
Previous12…15Next