
Sinister
 pushpenderindia/sinister
Sinister is Windows/Linux Keylogger Generator which sends key-logs via email with other juicy target info
data-exfiltrationinformation-gatheringpassword-cracking+5
467
pushpenderindia/sinisterSinister is Windows/Linux Keylogger Generator which sends key-logs via email with other juicy target info
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
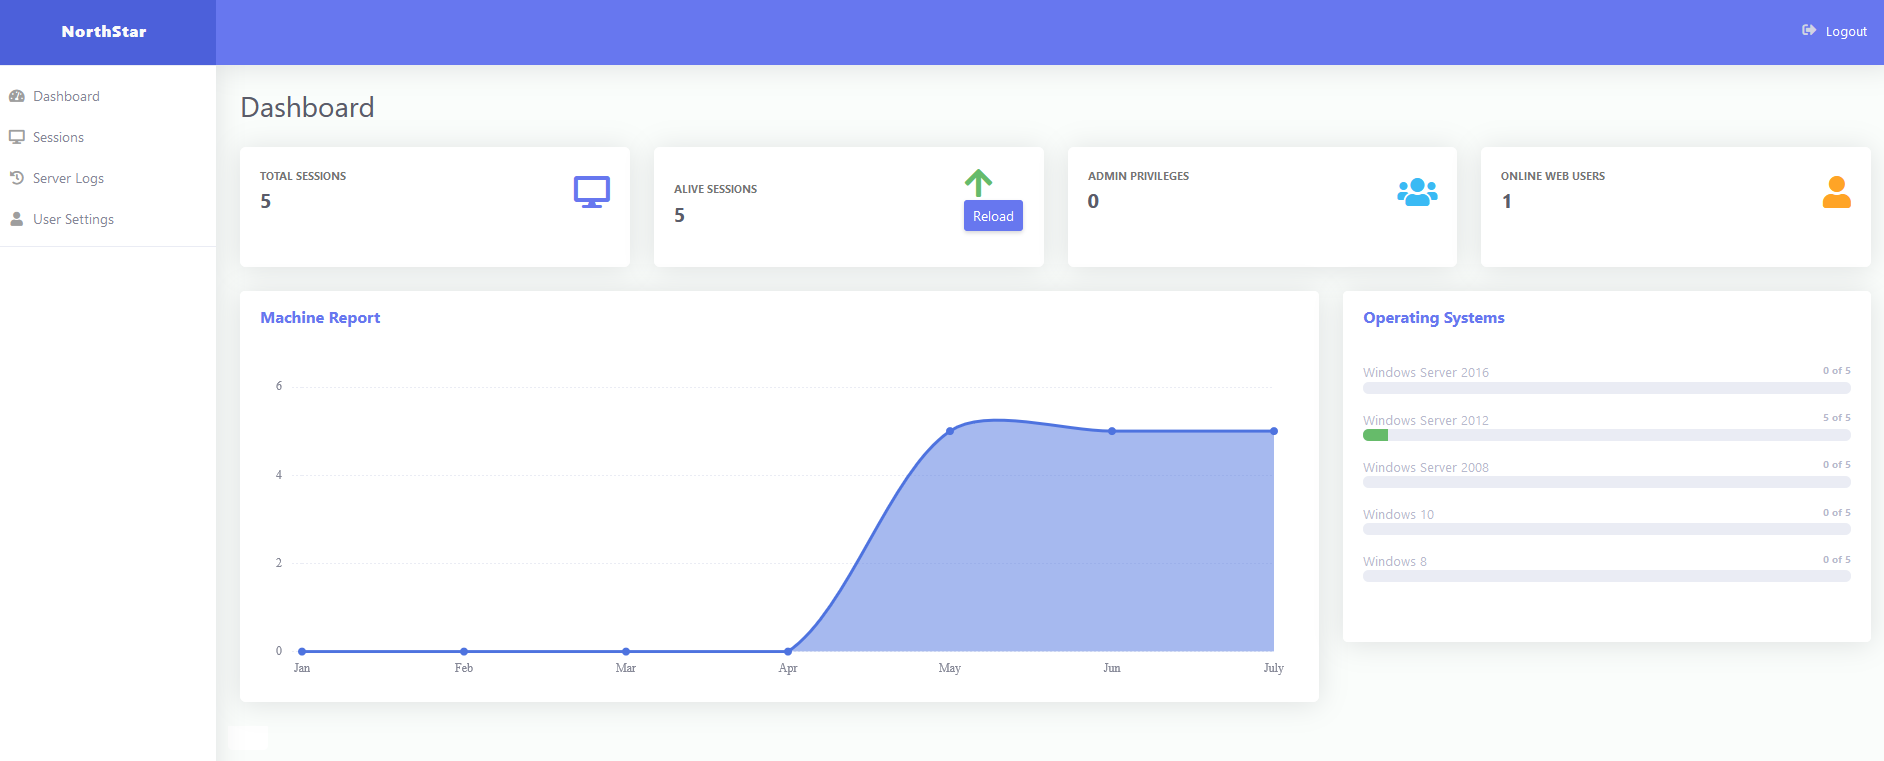 eng1ndes/northstarc2
Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…
 ignitetechnologies/mssql-pentest-cheatsheet
Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
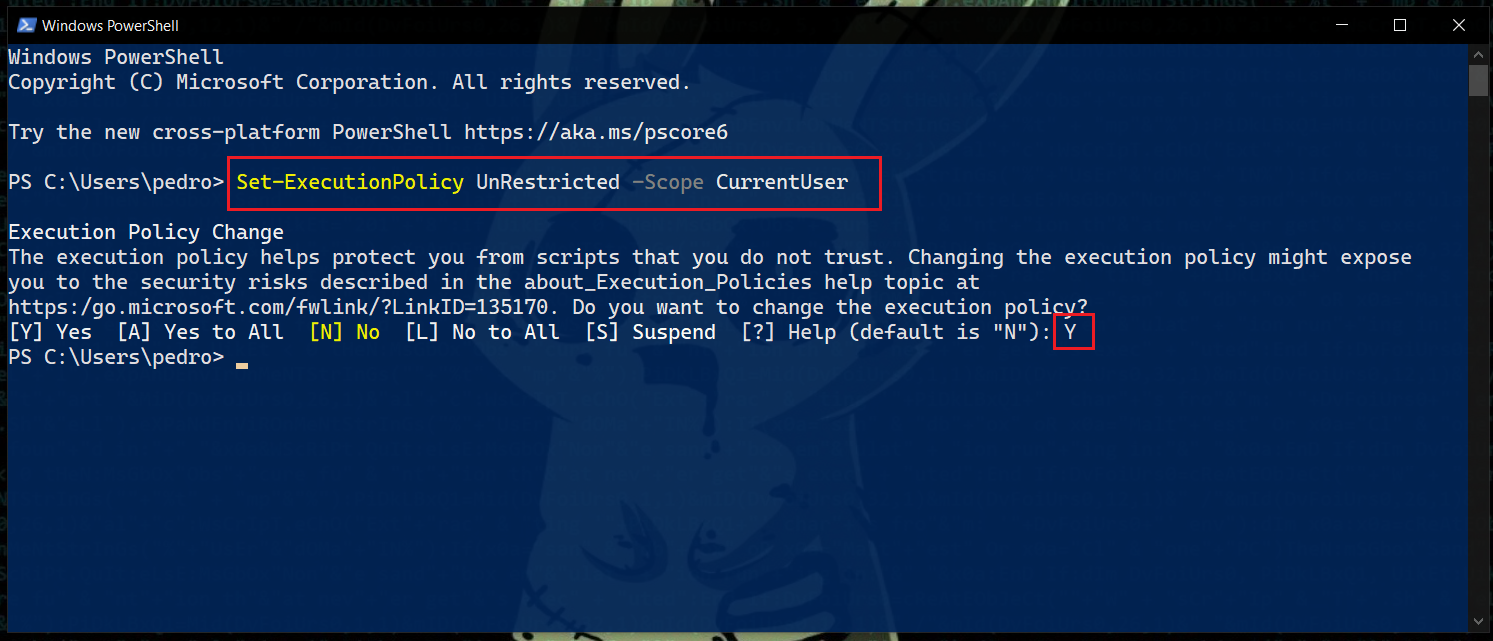 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
 logangoins/cable
.NET post-exploitation toolkit for Active Directory reconnaissance and exploitation
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
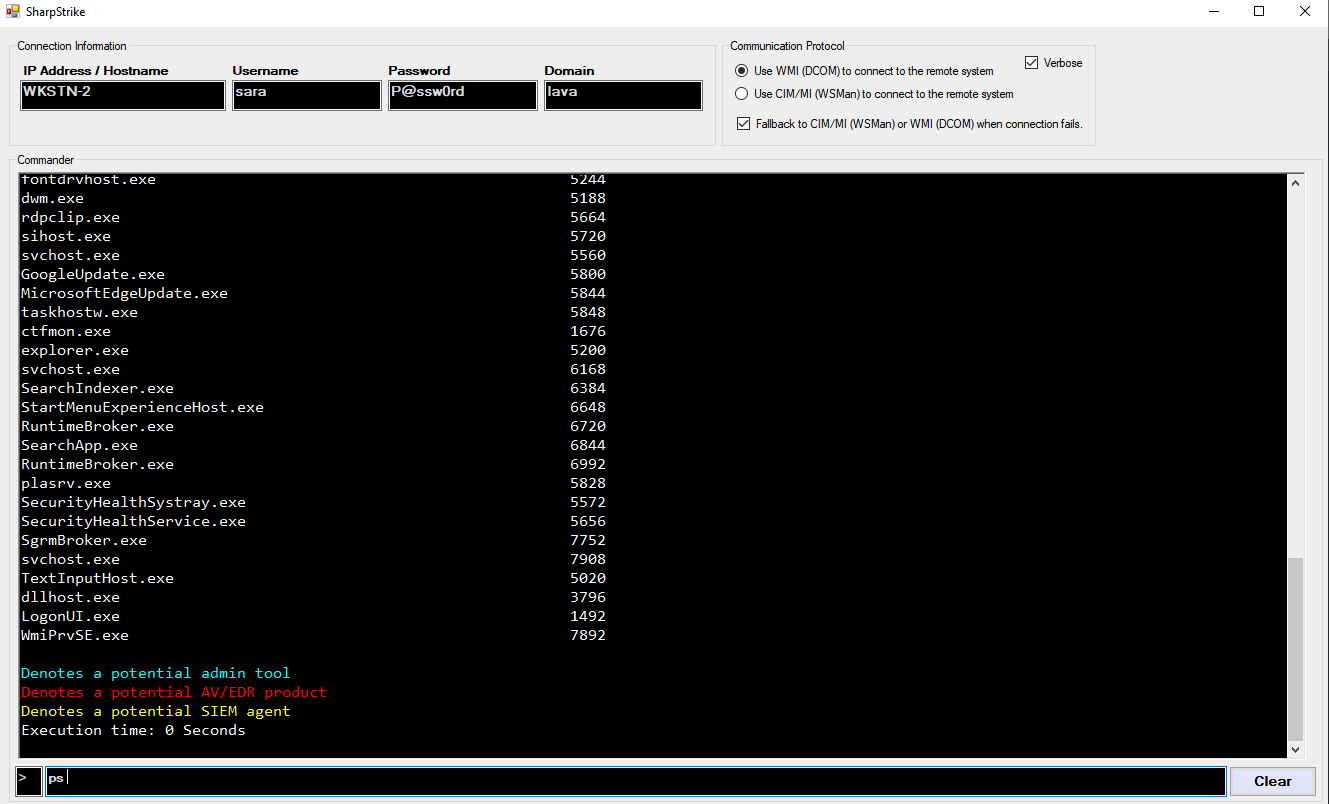 iomoath/sharpstrike
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.
 h4wkst3r/adokit
Modular attack toolkit exploiting Azure DevOps REST API for reconnaissance, privilege escalation, and persistence using stolen cookies or PATs.
 h4wkst3r/scmkit
Source Code Management Attack Toolkit
 zerodaylab/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 dviros/rat-via-telegram
Windows Remote Post Breach Tool via Telegram
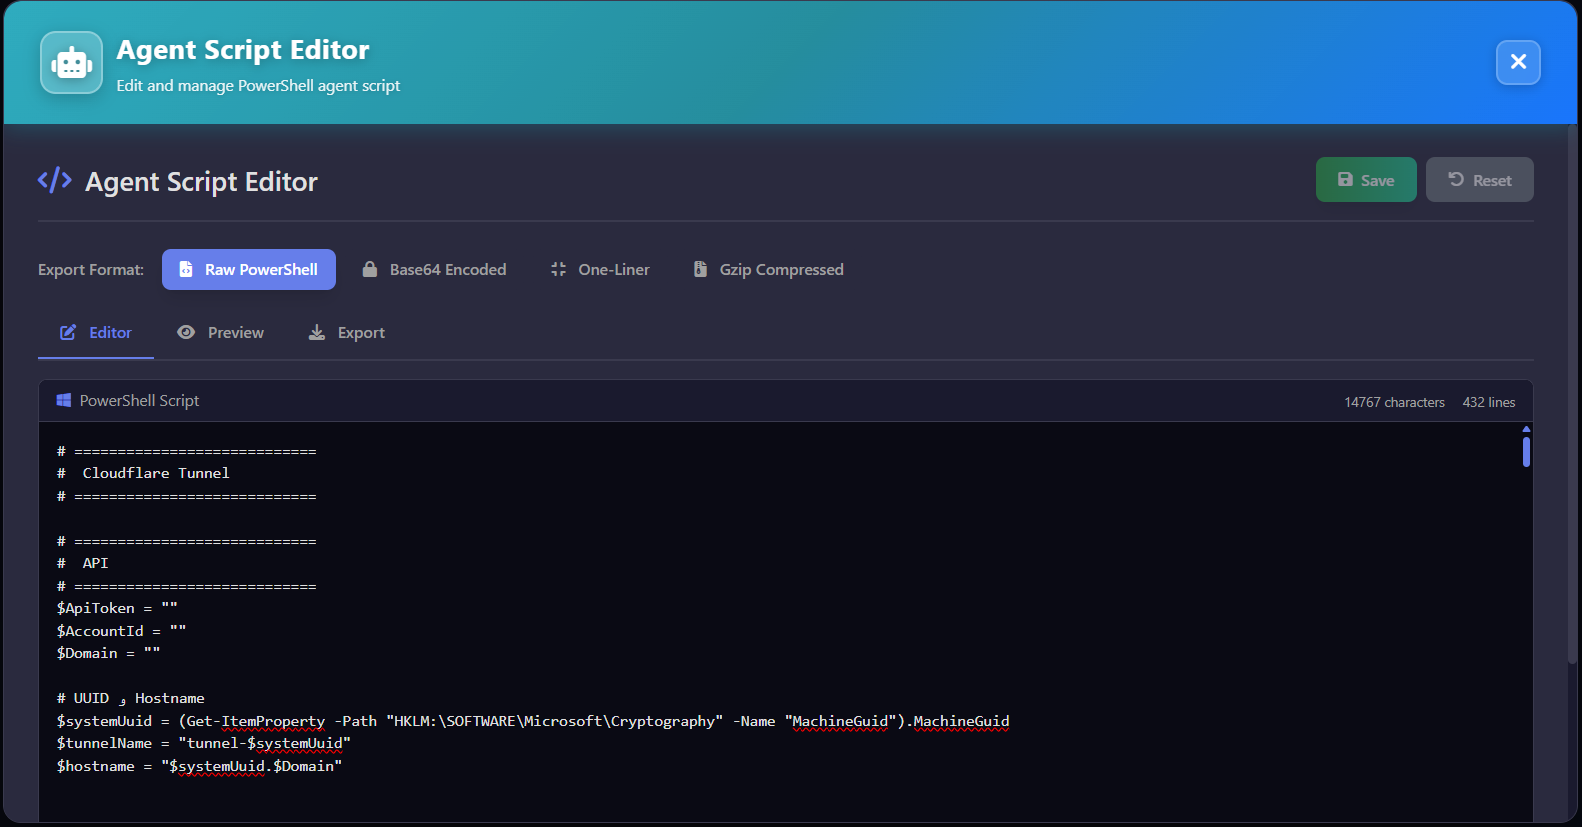 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
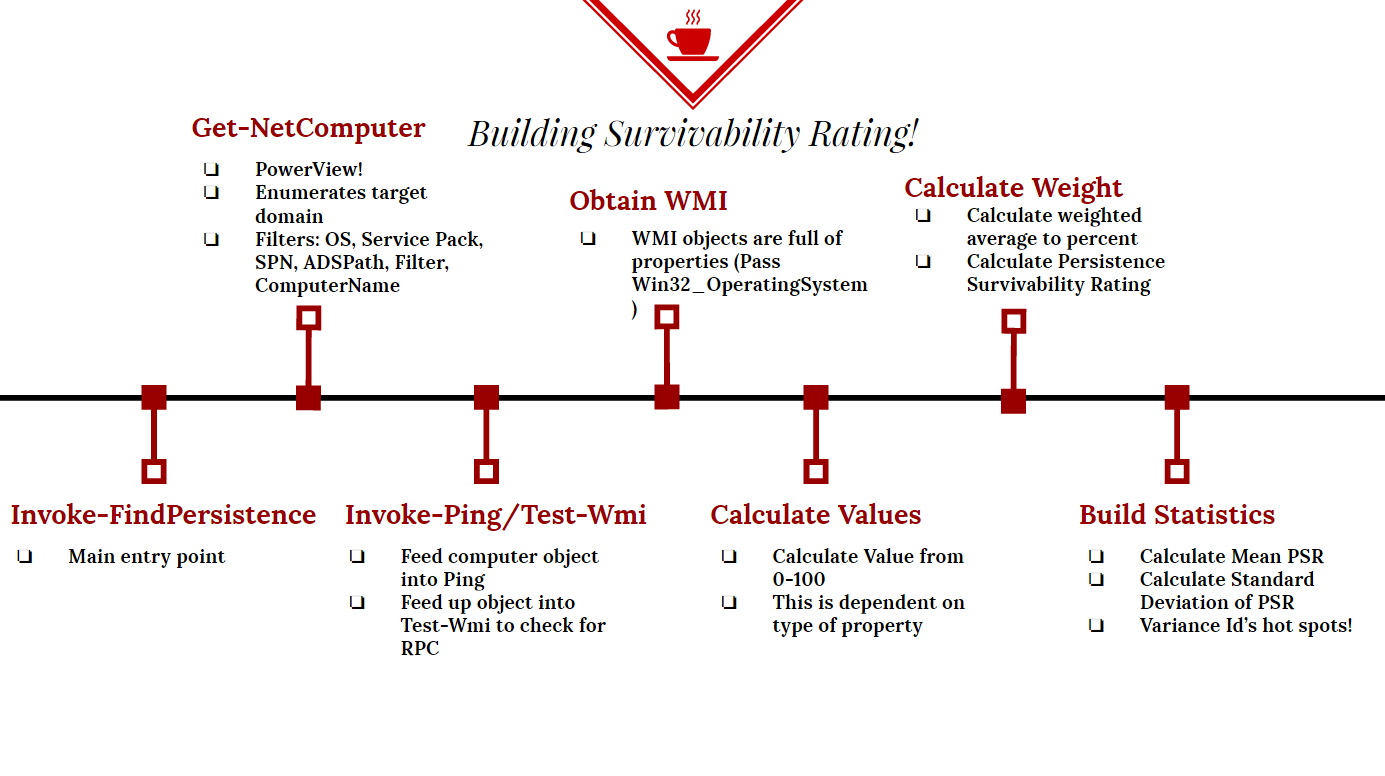 killswitch-gui/persistence-survivability
Powershell Persistence Locator
 lithium876/controll_remote_access_trojan
Created a VERY SIMPLE remote access Trojan that will establish administrative control over any windows machine it compromises.
 qazeer/farsightad
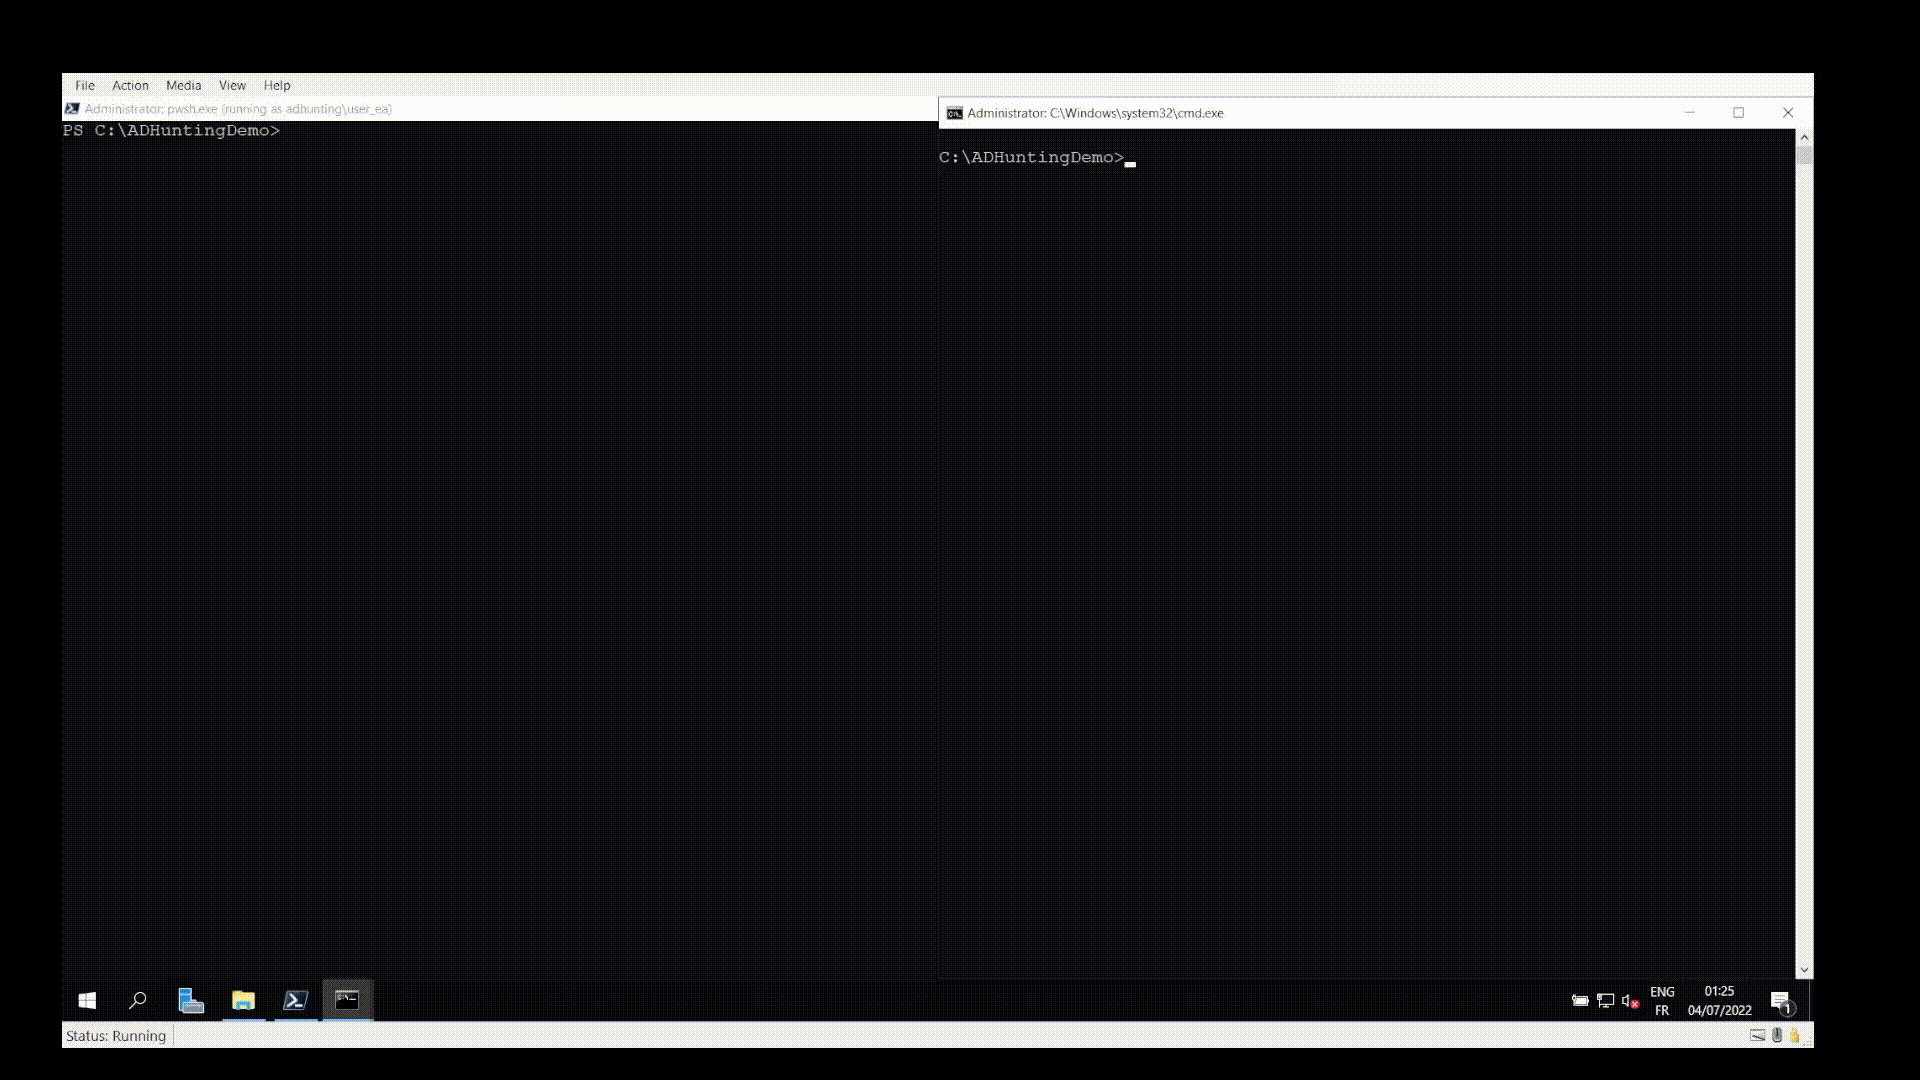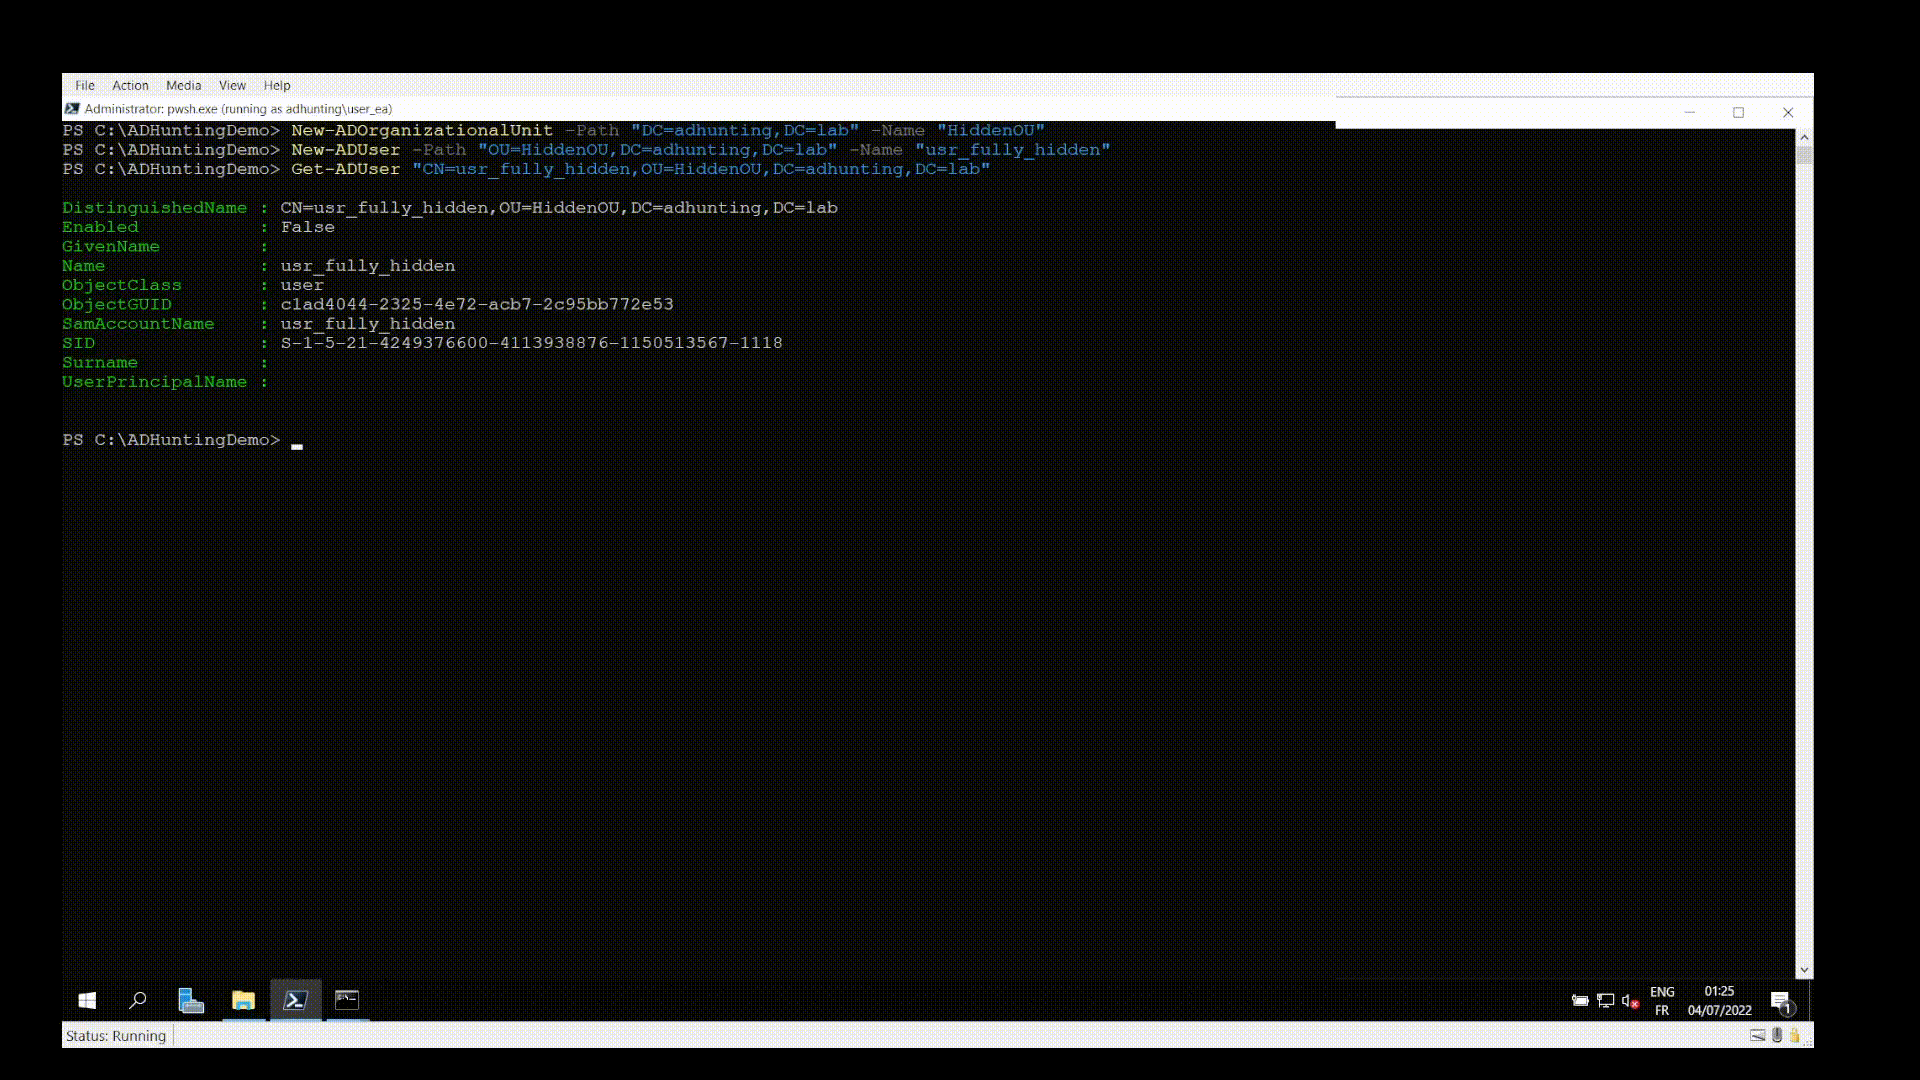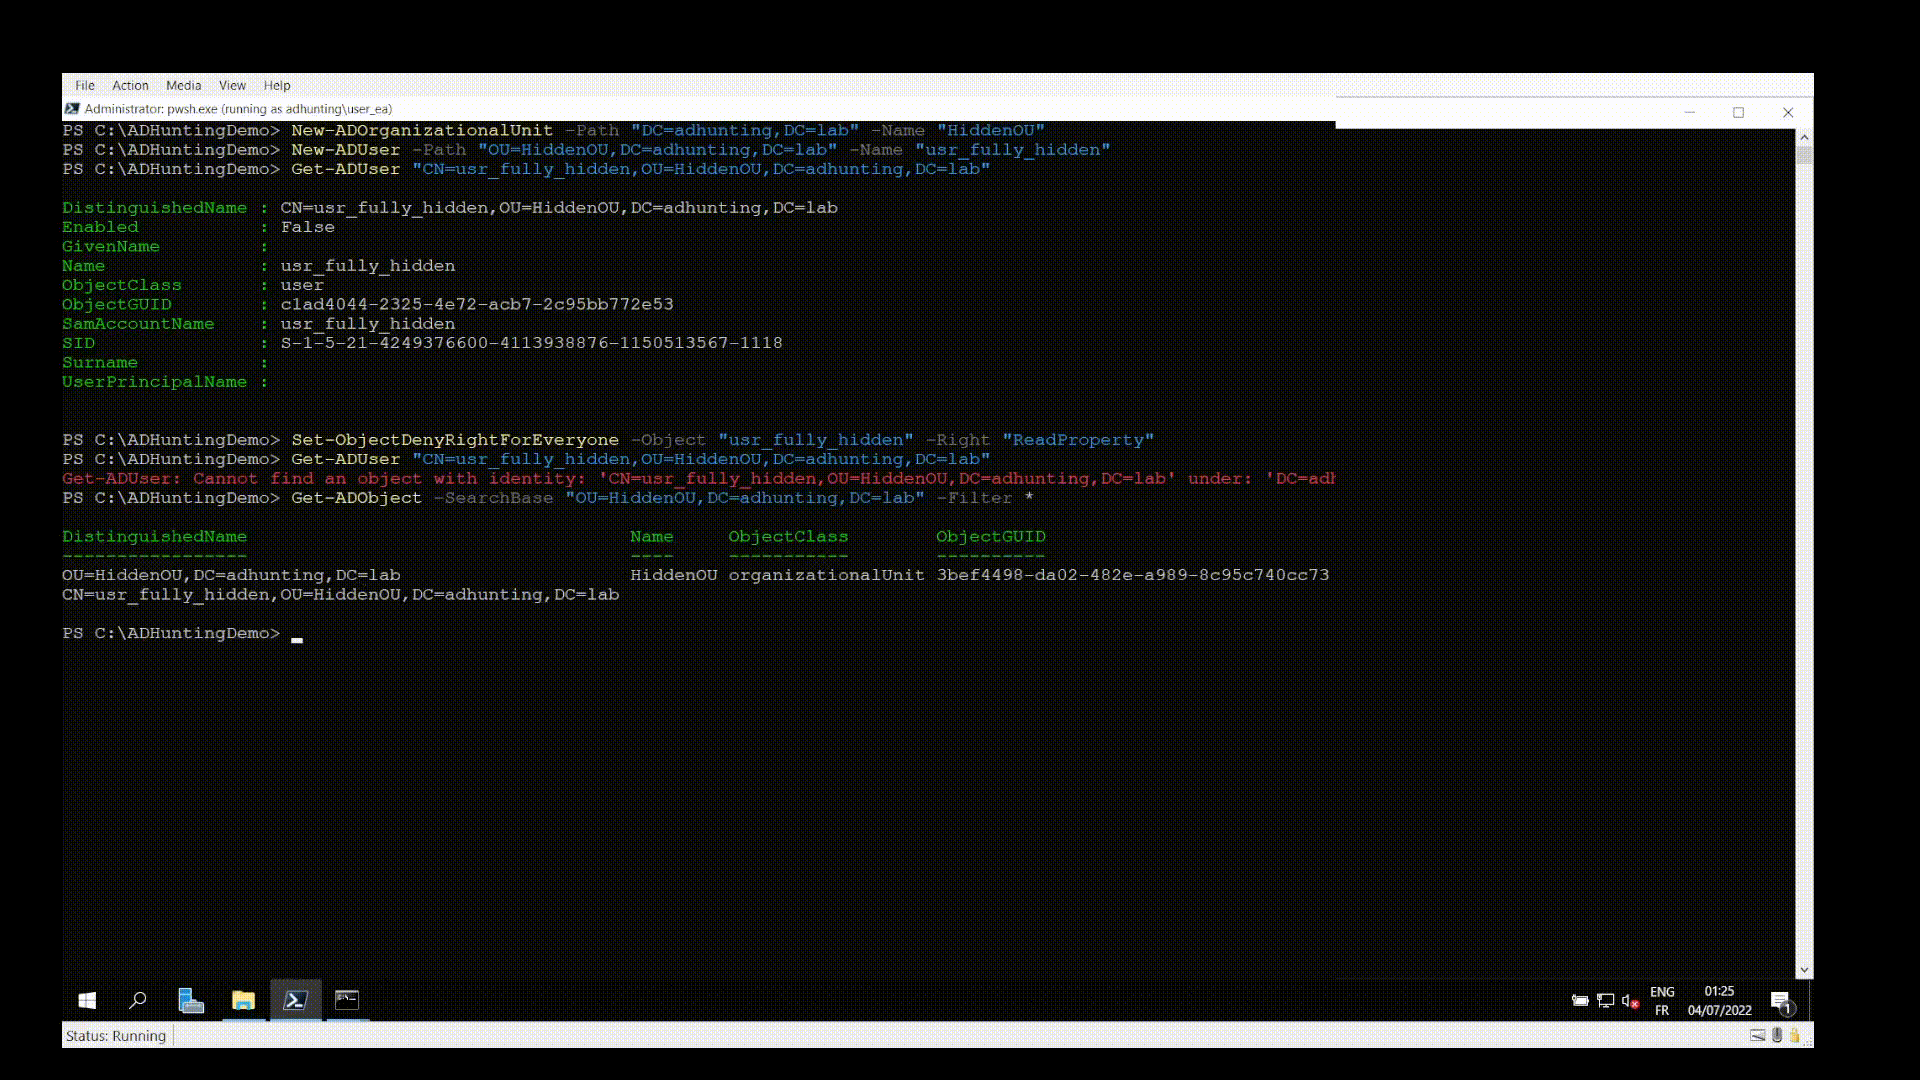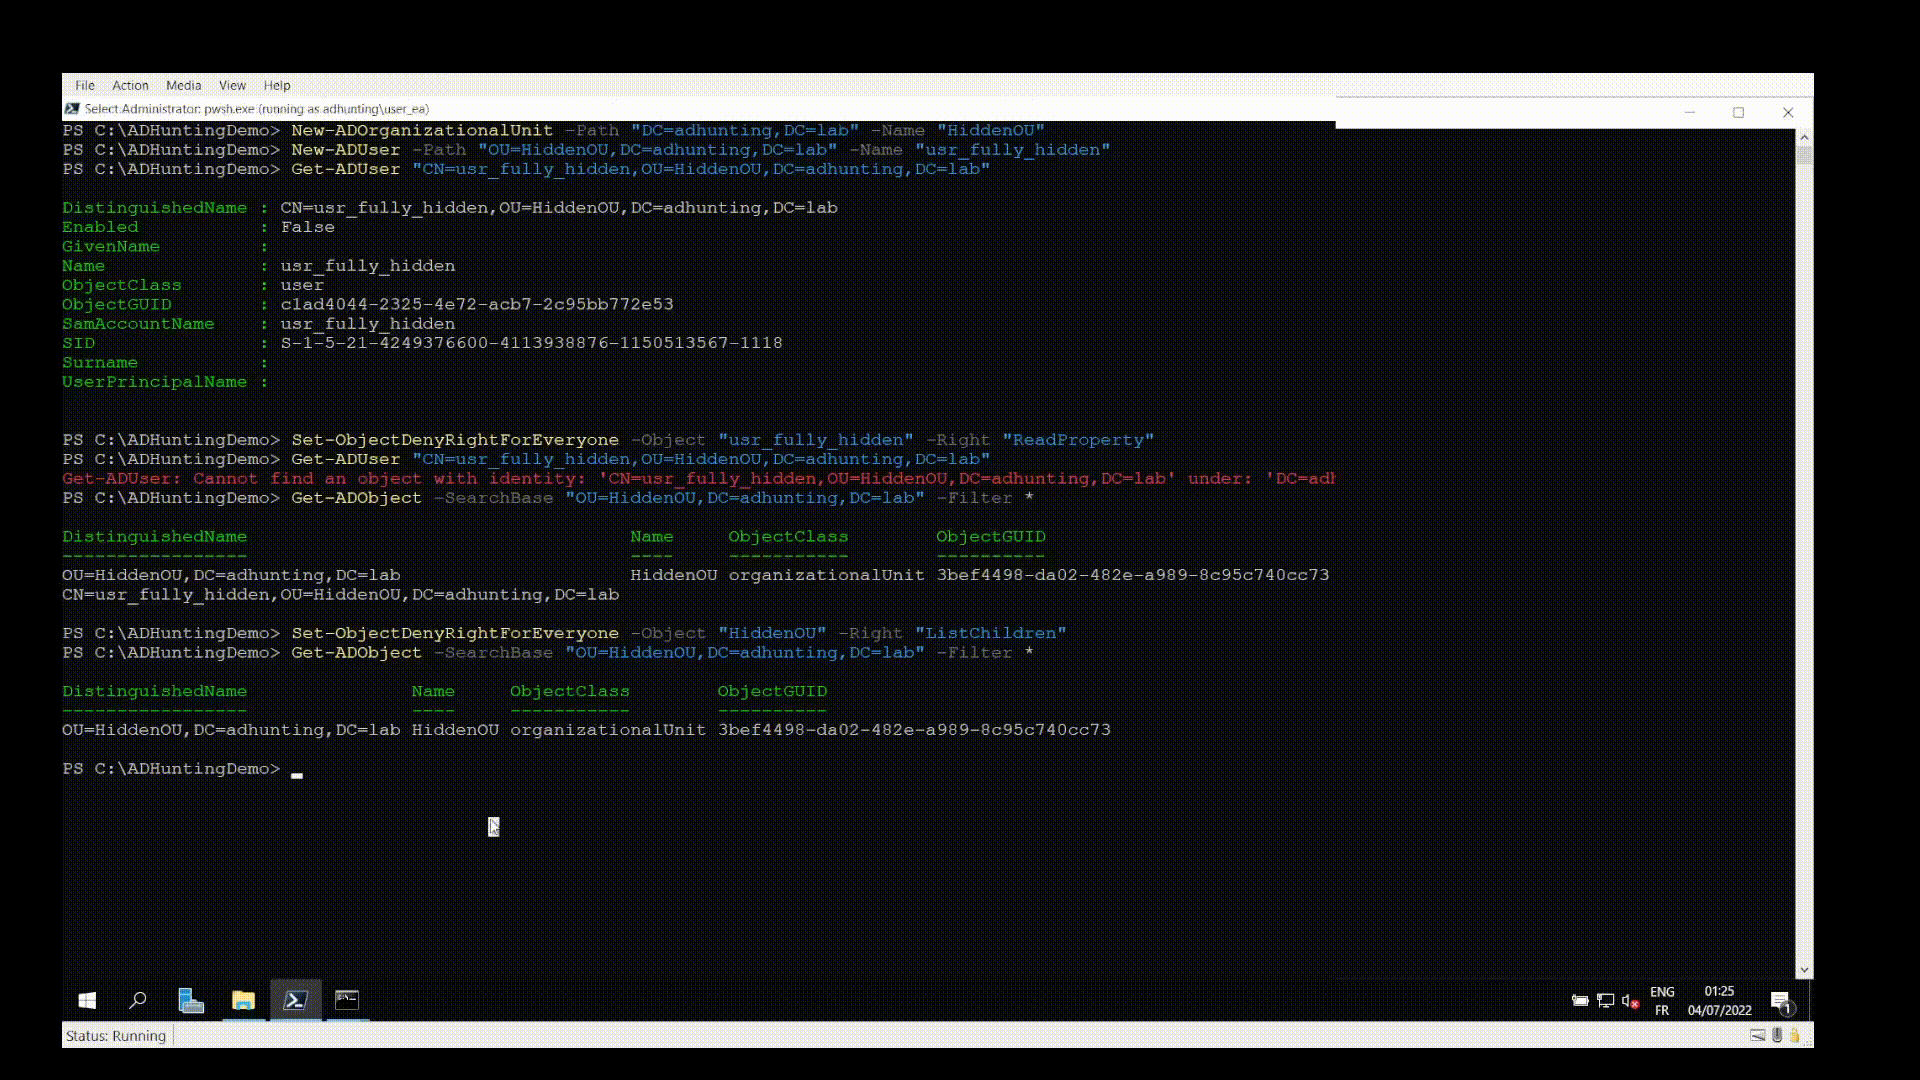
PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…
 1d8/spybrowse
Code developed to steal certain browser config files (history, preferences, etc)