
PersistBOF
 n4kedturtle/persistbof
A BOF to automate common persistence tasks for red teamers
payload-generationpersistence-mechanismspost-exploitation+2
2973 years ago
n4kedturtle/persistbofA BOF to automate common persistence tasks for red teamers
 aldisakti2/cve-2025-8088-builder-winrar-tool
CVE-2025-8088-BUILDER
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler

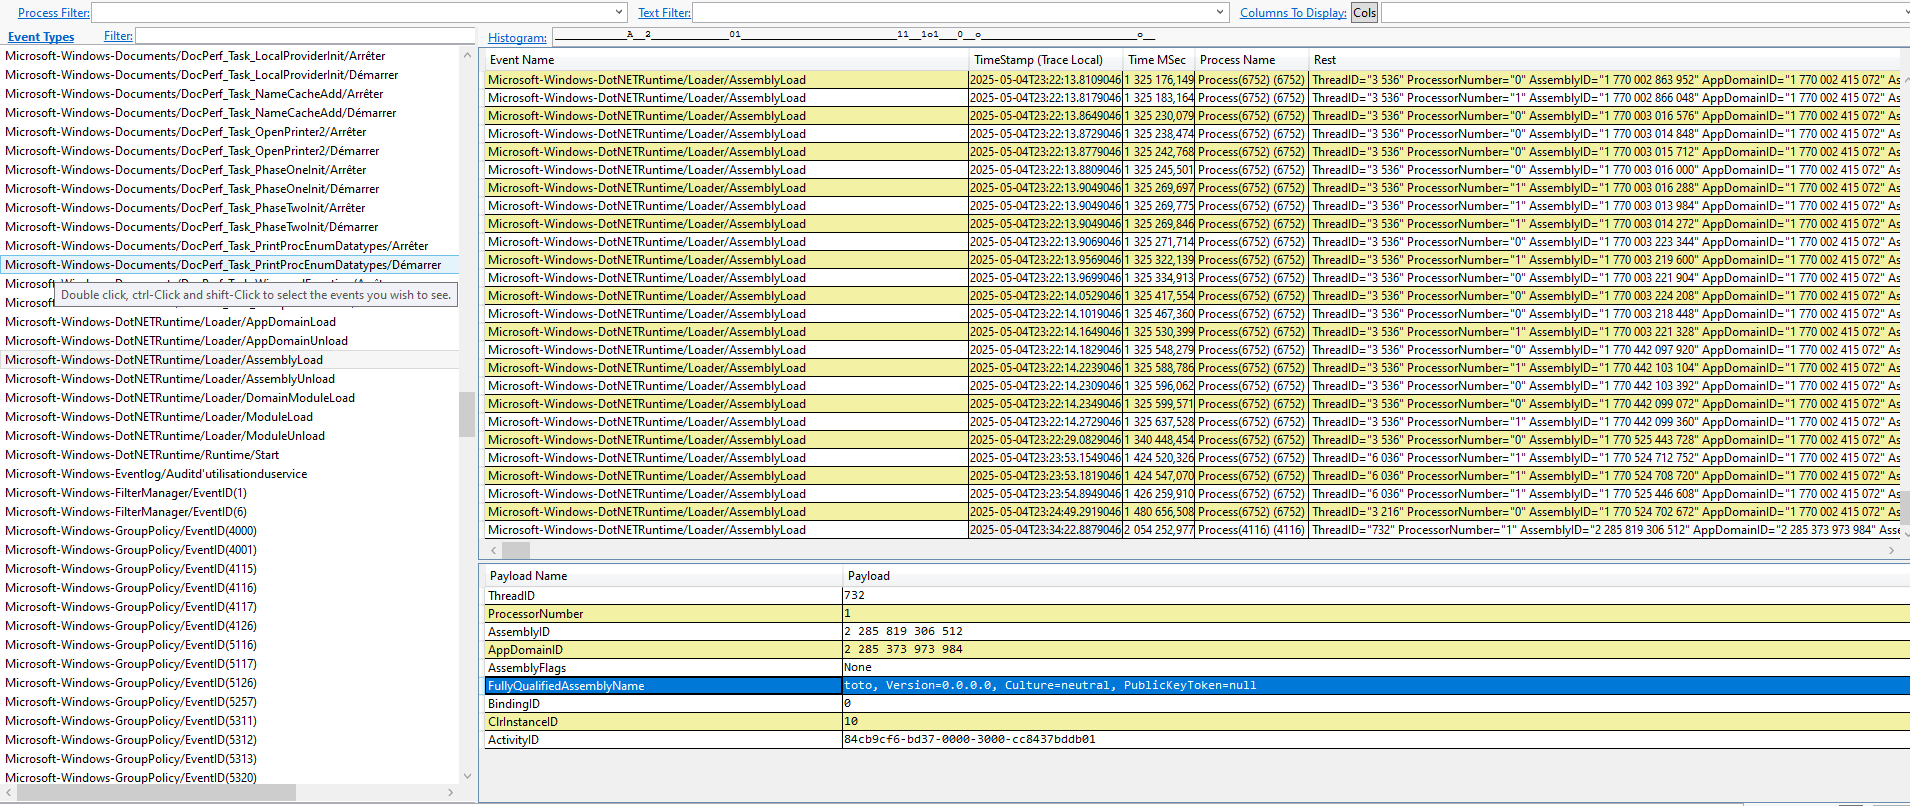 synacktiv/metamorph
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
 luantak/torat
ToRat is a Remote Administation tool written in Go using Tor as a transport mechanism and RPC for communication
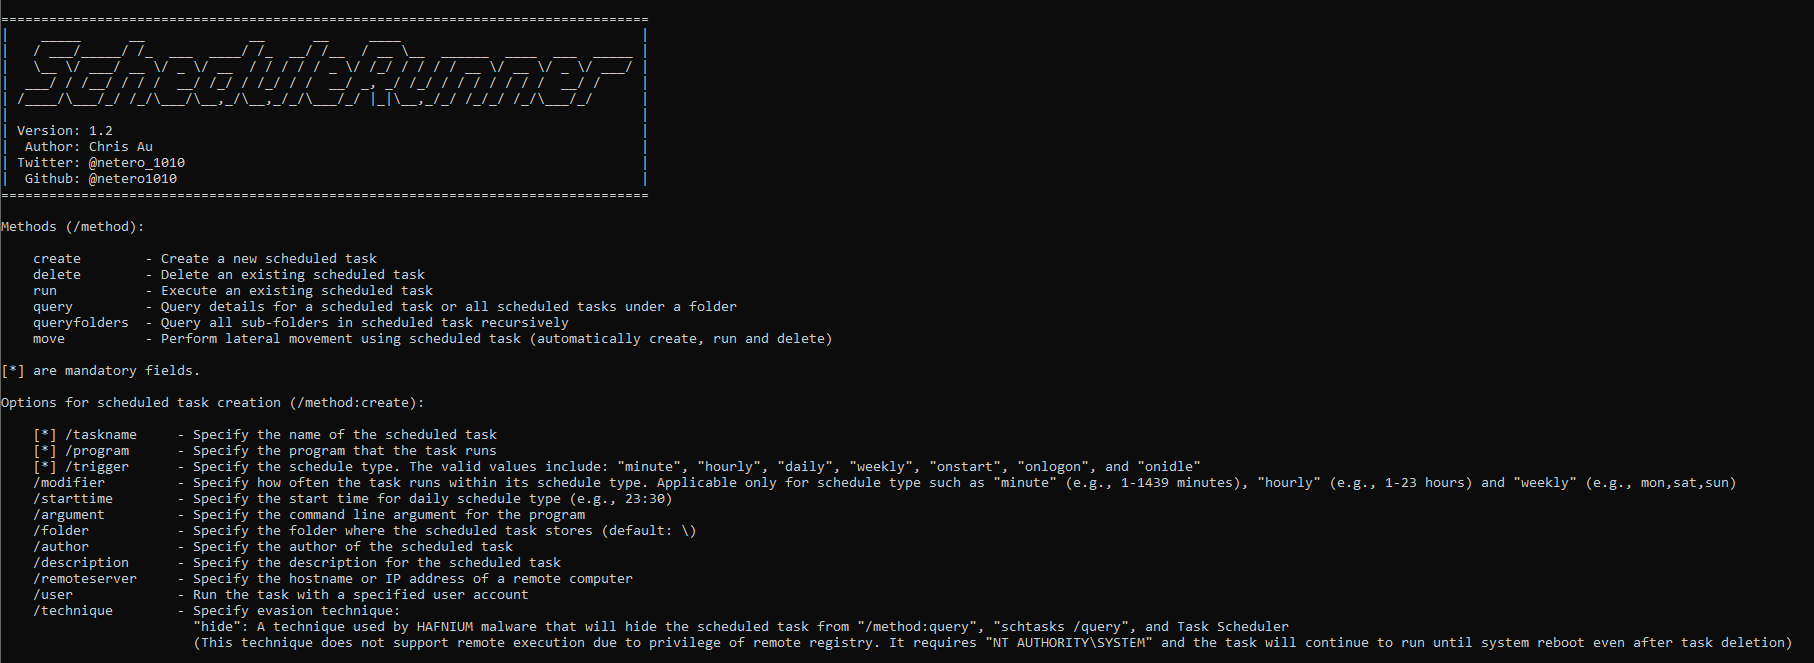 netero1010/schedulerunner
A C# tool with more flexibility to customize scheduled task for both persistence and lateral movement in red team operation
 nccgroup/gitpwnd
GitPwnd is a network penetration tool that lets you use a git repo for command and control of compromised machines
 viralmaniar/phirautee
A proof of concept crypto virus to spread user awareness about attacks and implications of ransomwares. Phirautee is written purely using PowerShell…
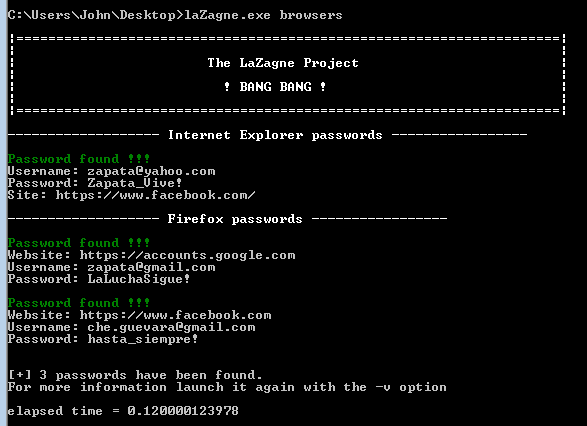 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 nickvourd/com-hunter
Windows COM hijacking persistence tool with search, classic, Task Scheduler, and TreatAs modes. Available as .NET executable and Cobalt Strike BOF…
 gmh5225/dse-patcher
Windows tool that disables Driver Signature Enforcement by patching kernel variables, allowing unsigned drivers to load for testing and research.
 sobri3195/pegasus-gram
Python-based keylogger and surveillance tool with Telegram C2, capturing keystrokes, screenshots, webcam, audio, clipboard, and system activity for…
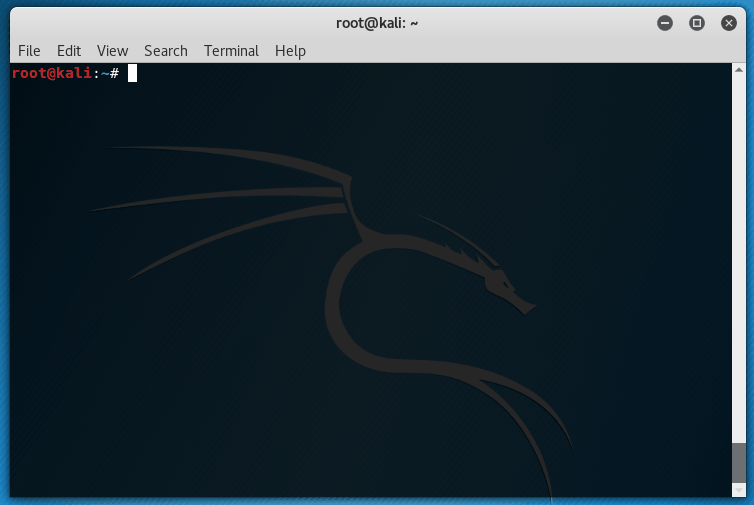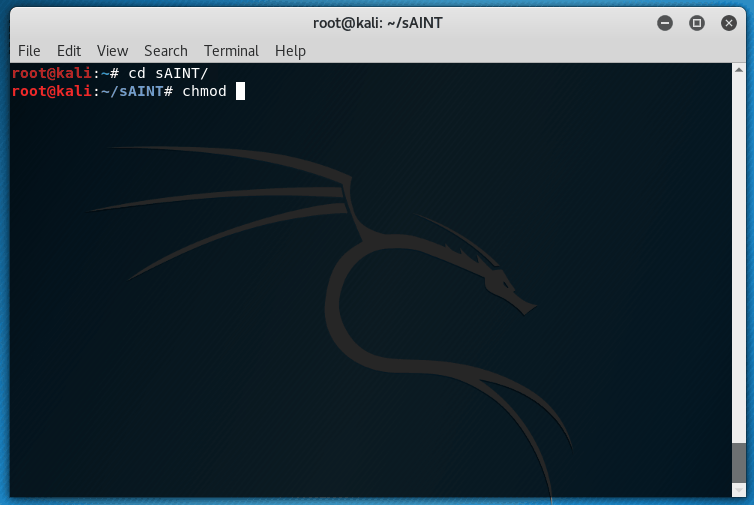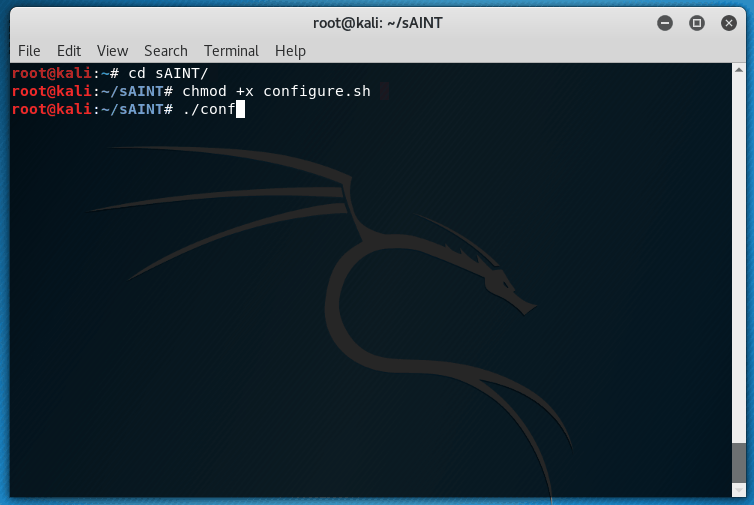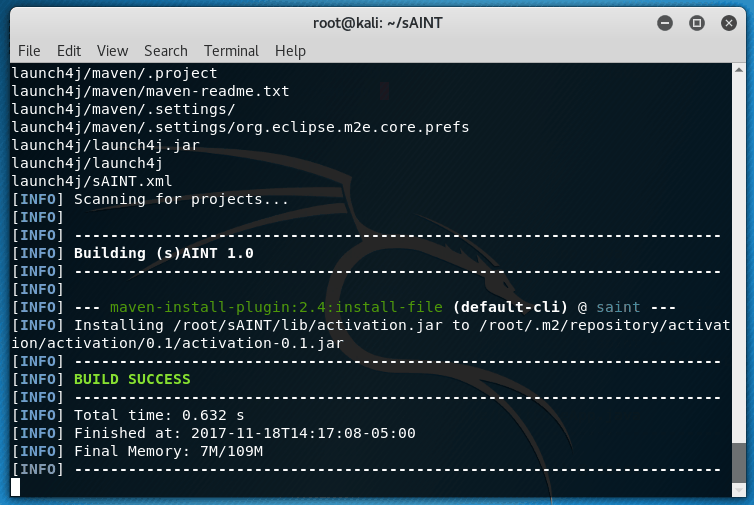 tiagorlampert/saint
👁️ (s)AINT is a Spyware Generator for Windows systems written in Java. [Discontinued]
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 mvelazc0/purplesharp
PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…