

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
69 results
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

adversarial-attackcommand-and-controldata-exfiltration+16
5.2k
1 month ago
emp3r0r preview

emp3r0r

GitHubjm33-m0/emp3r0r

Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…

anti-botcommand-and-controlids-ips-evasion+10
1.7k1 day ago
Heroinn preview

Heroinn

GitHubb23r0/heroinn

A cross platform C2/post-exploitation framework.
command-and-controldata-exfiltrationlateral-movement+8
7129 days ago
neurax preview

neurax

GitHubredcode-labs/neurax

A framework for constructing self-spreading binaries

command-and-controlexploitationlateral-movement+7
1.0k2 years ago
AdStrike preview

AdStrike

GitHubcapture0x/adstrike

AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
ai-securitycommand-and-controlexploitation+7
40819 days ago
venom preview

venom

GitHubboku7/venom

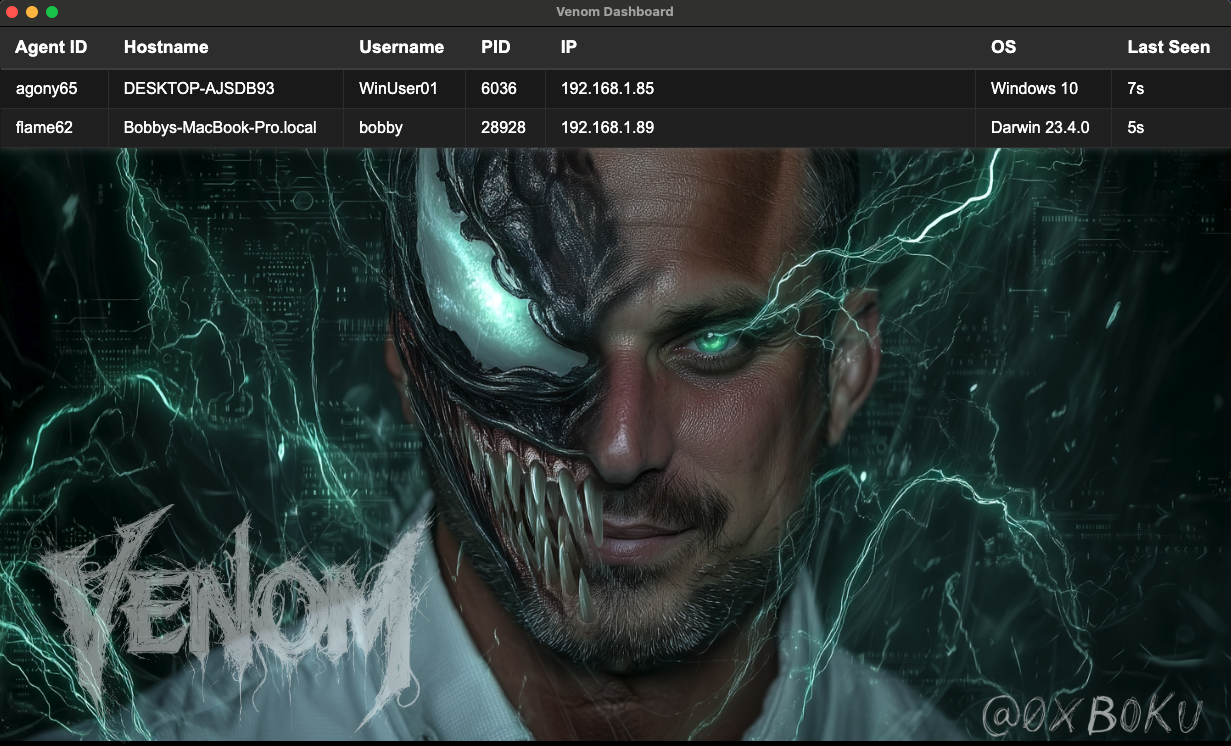
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
command-and-controlencryption-decryption-toolslateral-movement+6
4360 years ago
RedGhost preview

RedGhost

GitHubd4rk007/redghost

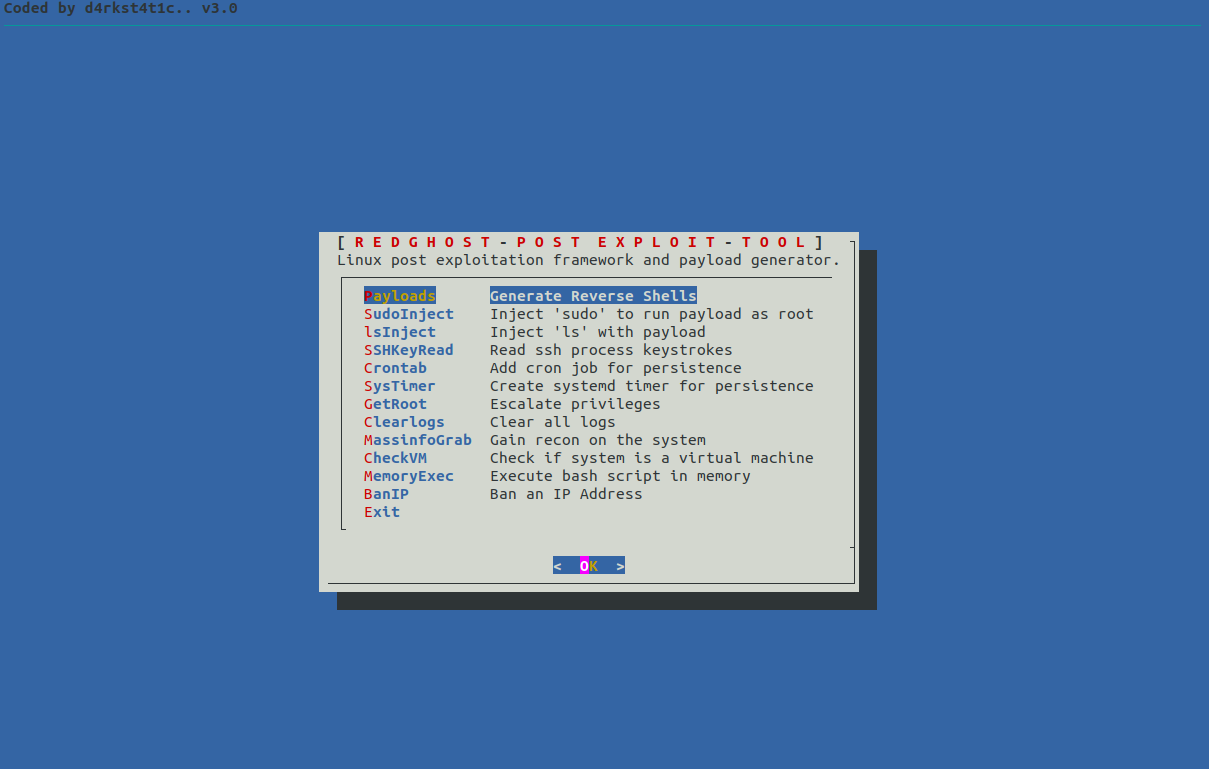
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
command-and-controllateral-movementpayload-generation+5
5425 years ago
conquest preview

conquest

GitHubjakobfriedl/conquest

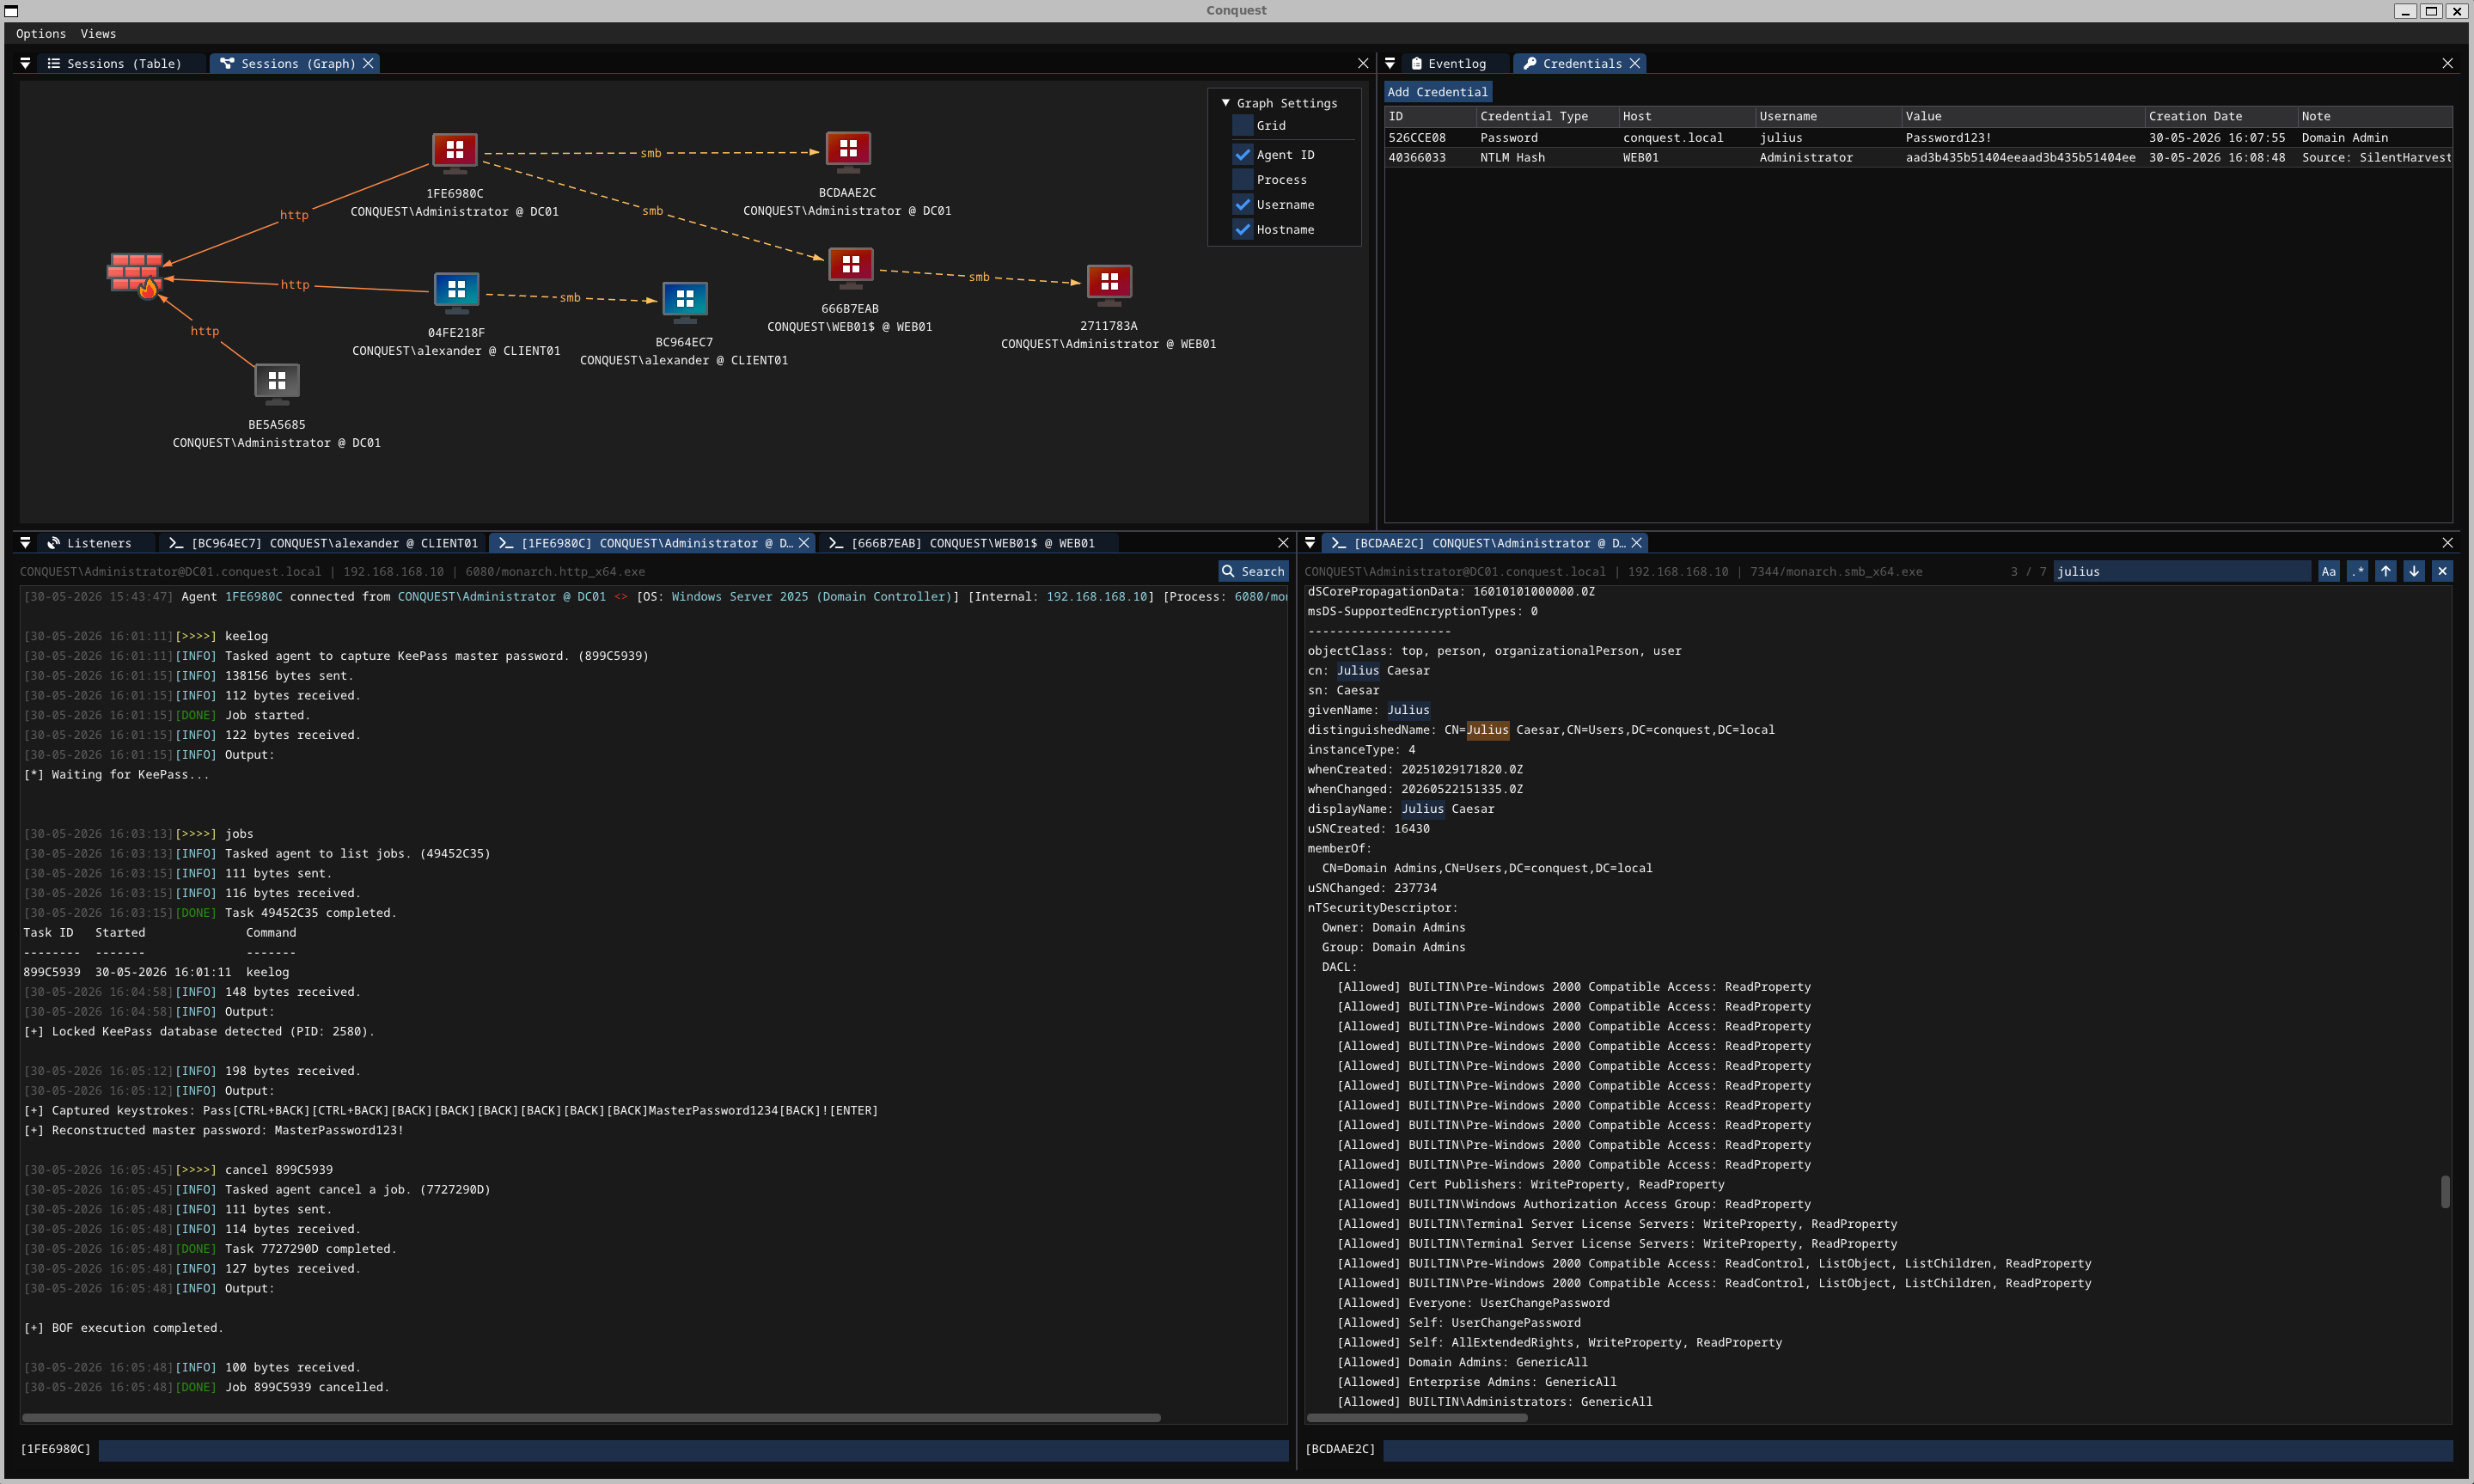
Conquest is a feature-rich and malleable command & control/post-exploitation framework developed in Nim.
command-and-controleducationexploit-frameworks+7
4183 months ago
FudgeC2 preview

FudgeC2

GitHubziconius/fudgec2

FudgeC2 - a command and control framework designed for team collaboration and post-exploitation activities.
command-and-controldata-exfiltrationexploit-frameworks+7
2533 years ago
NorthStarC2 preview

NorthStarC2

GitHubeng1ndes/northstarc2

Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…

command-and-controldata-exfiltrationinformation-gathering+6
2682 years ago
Silverseal preview

Silverseal

GitHubidov31/silverseal

Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
binary-exploitationexploitationmalware-analysis+4
17328 days ago
SharpMemshell preview

SharpMemshell

GitHuba-d-team/sharpmemshell

.NET in-memory webshell (memshell) payloads implemented via HttpListener and VirtualPath, compatible with the Godzilla 4.01 post-exploitation…
command-and-controldefensive-toolspayload-development+5
3004 years ago
PersistAssist preview

PersistAssist

GitHubredsiege/persistassist

Fully modular persistence framework
command-and-controlexploitationlateral-movement+7
2603 years ago
PowerSploit preview

PowerSploit

GitHubzerodaylab/powersploit

PowerSploit - A PowerShell Post-Exploitation Framework
command-and-controldata-exfiltrationexploit-frameworks+7
2394 years ago
stratum-c2 preview

stratum-c2

GitHublame-projects/stratum-c2

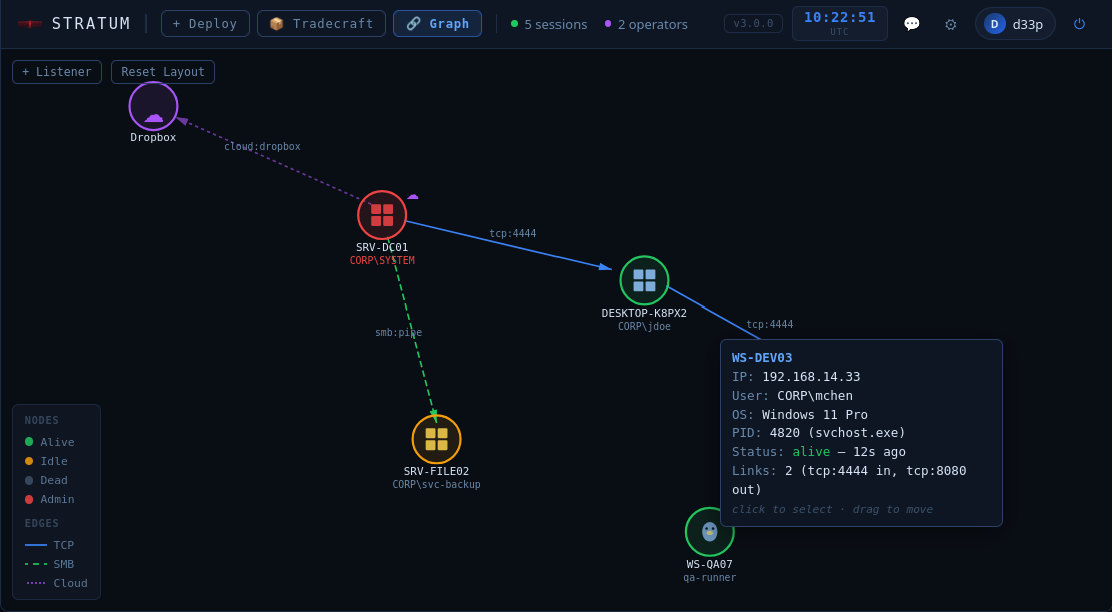
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting

cloud-securitycommand-and-controlencryption-decryption-tools+6
5014 days ago
TornadoC2 preview

TornadoC2

GitHubkamalx06/tornadoc2

Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
command-and-controlcryptographyids-ips-evasion+9
342 days ago
Phoenix-Framework preview

Phoenix-Framework

GitHubxm0kht4r/phoenix-framework

Post-exploitation framework that abuses trusted sites like Telegram and Discord for C2.

command-and-controldata-exfiltrationpayload-development+5
716 months ago
TornadoRevC2 preview

TornadoRevC2

GitHubkamalx06/tornadorevc2

Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…

command-and-controlinformation-gatheringlateral-movement+8
3929 days ago
Previous1234Next