

Silverseal
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
binary-exploitationexploitationmalware-analysis+4
172
idov31/silversealLinux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 mrexodia/titanhide
Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
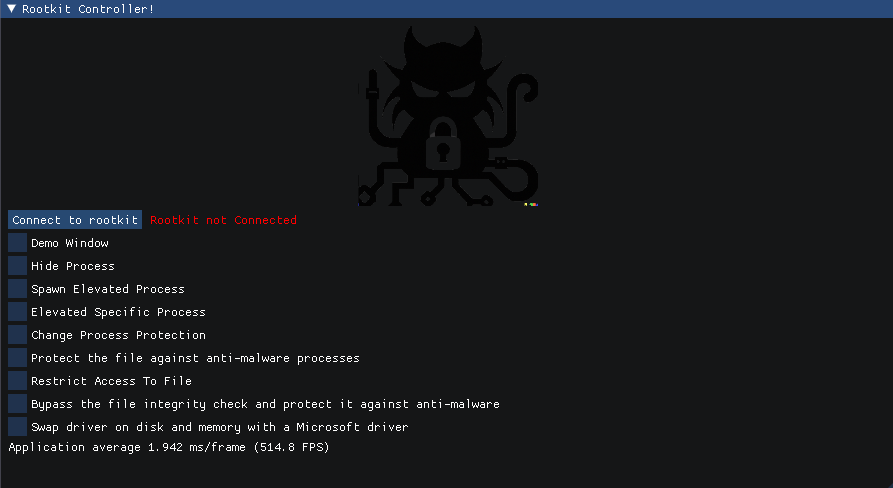 zeromemoryex/chaos-rootkit
Now You See Me, Now You Don't
 daem0nc0re/vectorkernel
PoCs for Kernelmode rootkit techniques research.
 gmh5225/evilkaspersky
Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
 gmh5225/kprocterminator
Windows kernel driver designed for terminating specific processes on a system
 gmh5225/dse-patcher
Windows tool that disables Driver Signature Enforcement by patching kernel variables, allowing unsigned drivers to load for testing and research.
 gmh5225/kli-ex
Extended kernel lazy importer for Windows drivers that resolves APIs at runtime with encrypted, cached import names to hide kernel function usage…
 gmh5225/driver-hide-file
choose and hide windows files/path from kernel space using this driver
 gmh5225/driver-kaldereta
Unsigned Kernel Mode Driver that does memory modifications
 jkornev/hidden
Windows driver with usermode interface which can hide processes, file-system and registry objects, protect processes and etc
 gmh5225/driver-hidekernelthread-iocancelirp
Windows kernel driver technique that hides kernel threads by abusing IoCancelIrp and IRP cancel routines, with detection methods for identifying…
 xaff-xaff/cronos-rootkit
Cronos is Windows 10/11 x64 ring 0 rootkit. Cronos is able to hide processes, protect and elevate them with token manipulation.
 darthton/hyperbone
Minimalistic VT-x hypervisor for Windows x64 providing syscall, MSR, IDT, and kernel inline hooks plus EPT-based page substitution and TLB splitting.
 ustayready/casperstager
PoC for persisting .NET payloads in Windows Notification Facility (WNF) state names using low-level Windows Kernel API calls.
 alex3434/wmi-static-spoofer
Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking