
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
45 results
CVE-2026-69414 preview

CVE-2026-69414

GitHubmaxprog-svg/cve-2026-69414

Python proof-of-concept exploit for CVE-2026-69414, a type-confusion elevation of privilege in the Microsoft Malware Protection Engine, with AMSI/ETW…

exploitationids-ips-evasionpayload-development+4
26 days ago
claude-code-backdoor-check preview

claude-code-backdoor-check

GitHubhappyhackingspace/claude-code-backdoor-check

Read-only scanner for the backdoored Claude Code 2.1.313 extension (Cursor marketplace, Oct 2026): SSH key, persistence, reverse tunnel. macOS +…
defensive-toolsdigital-forensicsincident-response+4
16 days ago
AndroRAT preview

AndroRAT

GitHubkarma9874/androrat

A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side

android-securitycommand-and-controldata-exfiltration+7
5.3k2 years ago
Overthrone preview

Overthrone

GitHubkarmanya03/overthrone

All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
command-and-controlexploit-frameworksinformation-gathering+8
3113 days ago
veneficus-implant-public preview

veneficus-implant-public

GitHubabraxas/veneficus-implant-public

Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…

command-and-controldata-exfiltrationexploitation+9
2 months ago
TornadoRevC2 preview

TornadoRevC2

GitHubkamalx06/tornadorevc2

Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…

command-and-controlinformation-gatheringlateral-movement+8
3929 days ago
Driver-kaldereta preview

Driver-kaldereta

GitHubgmh5225/driver-kaldereta

Unsigned Kernel Mode Driver that does memory modifications
binary-exploitationdebuggersdynamic-analysis-sandboxing+8
114 years ago
Windows-Defender-Security-Auditor-CVE-2026-50656- preview

Windows-Defender-Security-Auditor-CVE-2026-50656-

GitHubeh-amish/windows-defender-security-auditor-cve-2026-50656-

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
configuration-auditingdefensive-toolsincident-response+8
12 months ago
PowerSploit preview

PowerSploit

GitHubzerodaylab/powersploit

PowerSploit - A PowerShell Post-Exploitation Framework
command-and-controldata-exfiltrationexploit-frameworks+7
2394 years ago
wmiexec-Pro preview

wmiexec-Pro

GitHubxiaolichan/wmiexec-pro

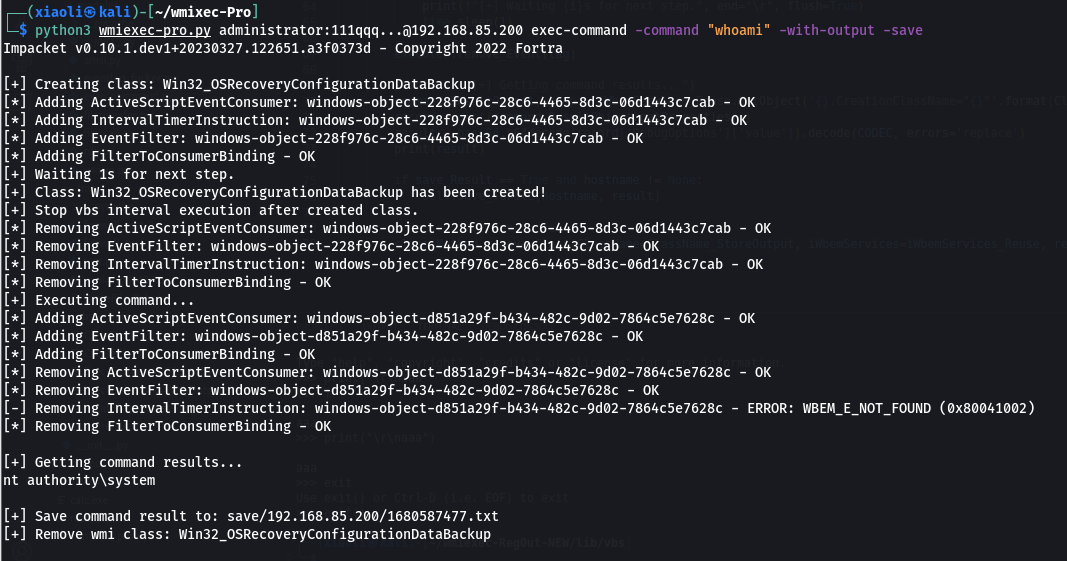
New generation of wmiexec.py
information-gatheringlateral-movementpenetration-testing+5
1.3k7 months ago
GraphSpy preview

GraphSpy

GitHubredbyte1337/graphspy

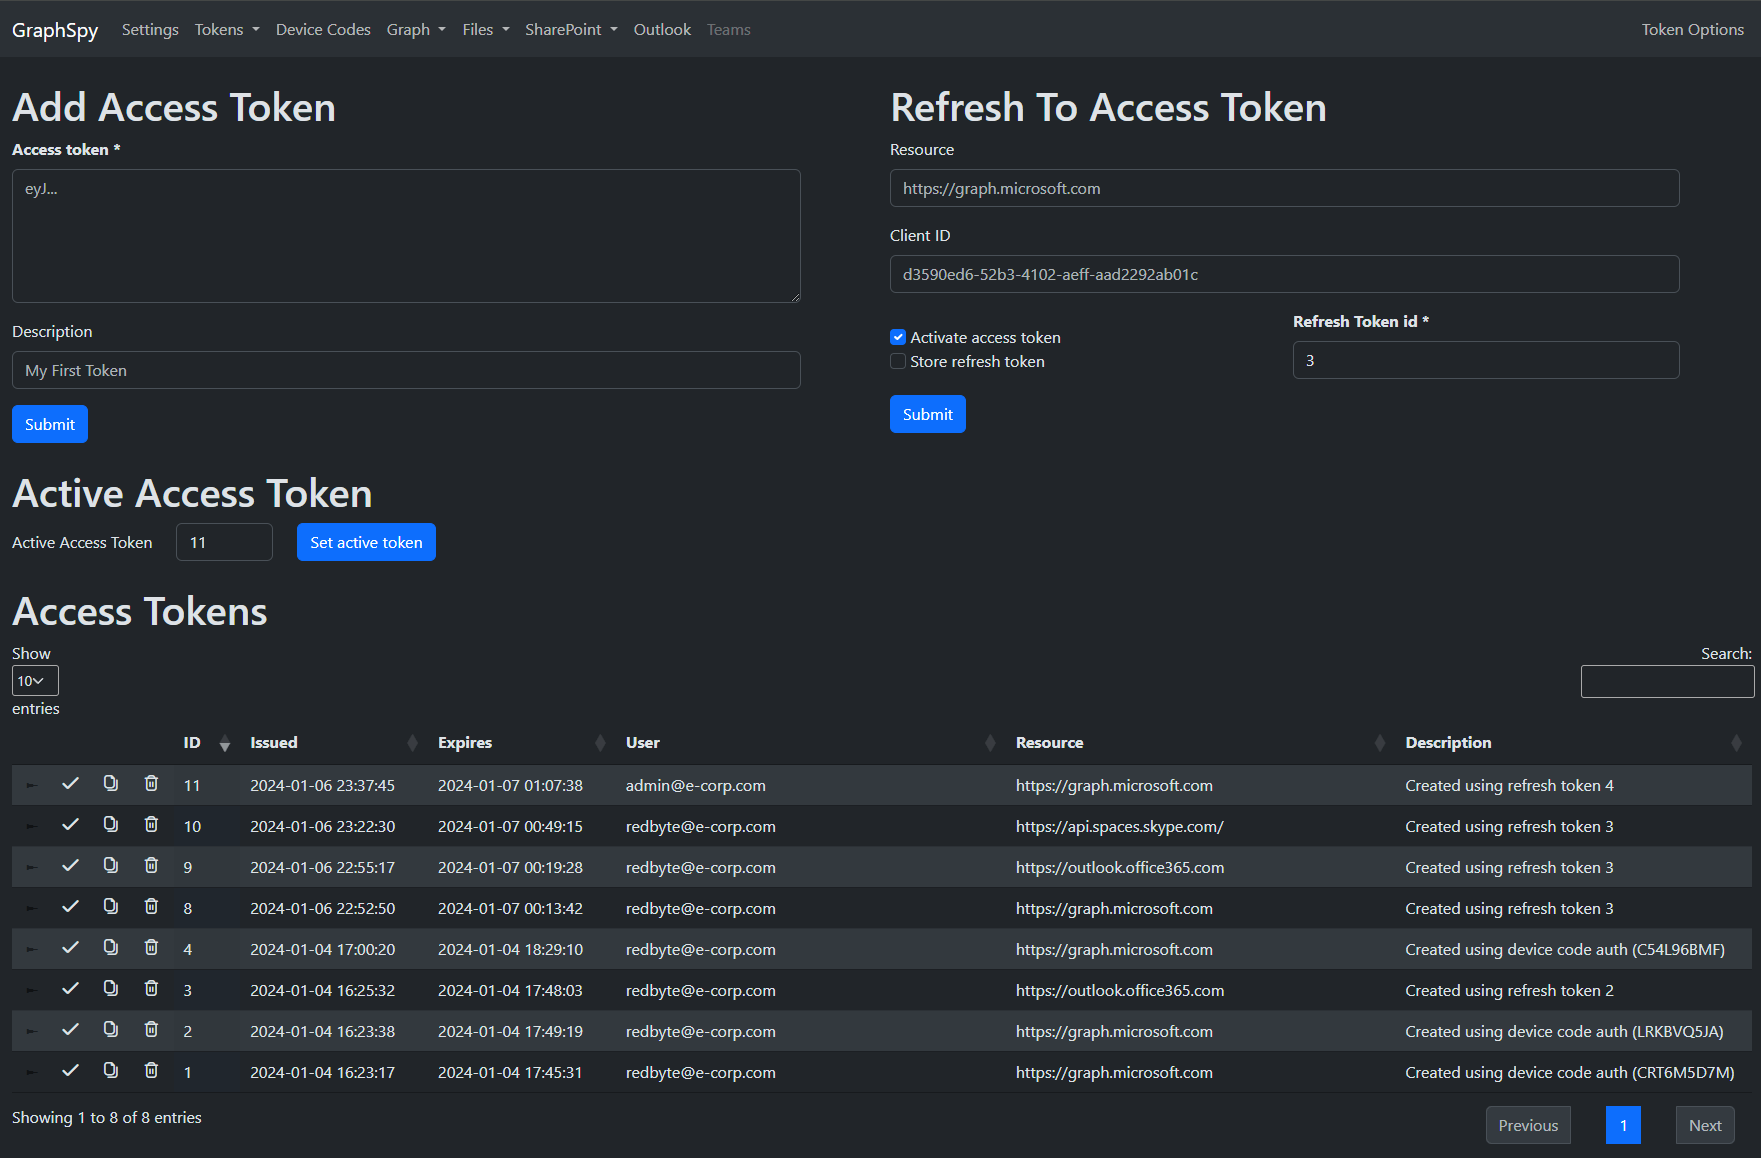
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
authenticationcloud-securitydata-exfiltration+6
1.4k2 months ago
badsuccessor preview

badsuccessor

GitHubcybrly/badsuccessor

Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
adversarial-attackexploitationinformation-gathering+7
12214 days ago
ncentral-compromise-ioc-triage preview

ncentral-compromise-ioc-triage

GitHubcreamyg31337/ncentral-compromise-ioc-triage

Read-only N-able N-central CVE-2026-18556/CVE-2026-18577 post-exploitation IoC hunter for Windows endpoints

defensive-toolsdigital-forensicsincident-response+4
3 months ago
Active-Directory-Exploitation-Cheat-Sheet preview

Active-Directory-Exploitation-Cheat-Sheet

GitHubintegration-it/active-directory-exploitation-cheat-sheet

A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
curated-resourcesdata-exfiltrationeducation+6
2.8k5 years ago
Metamorph preview

Metamorph

GitHubsynacktiv/metamorph

A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
defensive-toolsincident-responseinformation-gathering+3
85 months ago
sqlwinds preview

sqlwinds

GitHubblue0x1/sqlwinds

SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
configuration-auditingdatabase-securitydata-exfiltration+7
1 year ago
Flowise-CVE-2026-58057-exploit preview

Flowise-CVE-2026-58057-exploit

GitHubcerberusmrxi/flowise-cve-2026-58057-exploit

Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…

command-and-controlexploitationinformation-gathering+7
13 months ago
IIS-Backdoor preview

IIS-Backdoor

GitHubnu11secur1ty/iis-backdoor

Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…

command-and-controlexploitationids-ips-evasion+4
346 years ago
Previous123Next