
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
28 results
Common-Registry preview

Common-Registry

GitHubeballoon/common-registry

Proof-of-concept C code demonstrating registry-based communication, PFN clearing, and custom process attachment techniques for stealthy payload…

malware-analysispayload-developmentpersistence-mechanisms+2
48
4 years ago
ConfluenceC2 preview

ConfluenceC2

GitHubdagowda/confluencec2

This is a project aimed to make every other Saas product a C2, confluence is just the beginning.

command-and-controldata-exfiltrationlateral-movement+9
2110 days ago
Koi preview

Koi

GitHubb3rt1ng/koi

Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
command-and-controlids-ips-evasionlateral-movement+9
372 days ago
CVE-2026-65400 preview

CVE-2026-65400

GitHubhorkimhab/cve-2026-65400

Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.
authenticationeducationexploitation+4
32 months ago
tap preview

tap

GitHubtrustedsec/tap

The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.
command-and-controlpenetration-testing-frameworkspersistence-mechanisms+3
5053 years ago
SmmBackdoor preview

SmmBackdoor

GitHubcr4sh/smmbackdoor

First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
exploitationfirmware-analysishardware-hacking+4
6393 years ago
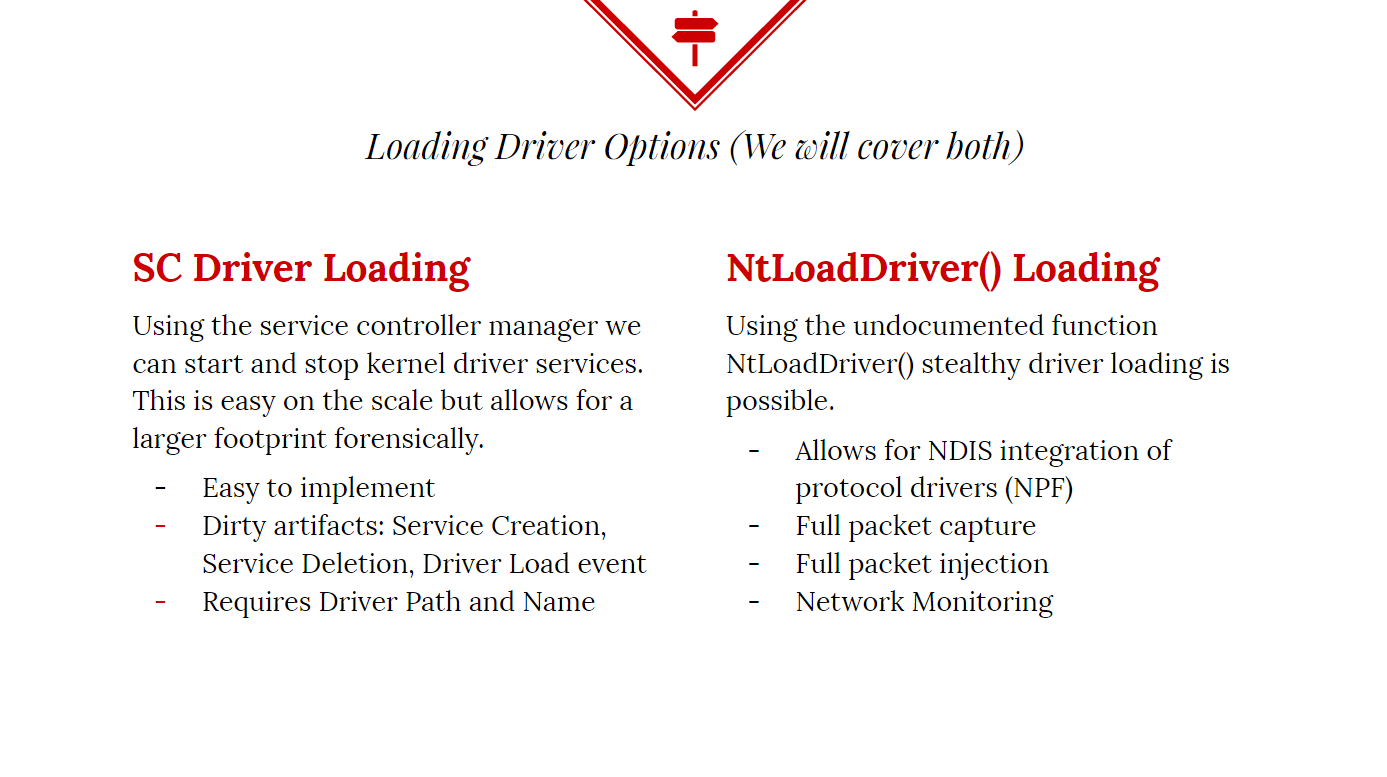
HotLoad-Driver preview

HotLoad-Driver

GitHubkillswitch-gui/hotload-driver

C++

exploitationpayload-developmentpersistence-mechanisms+3
8810 years ago
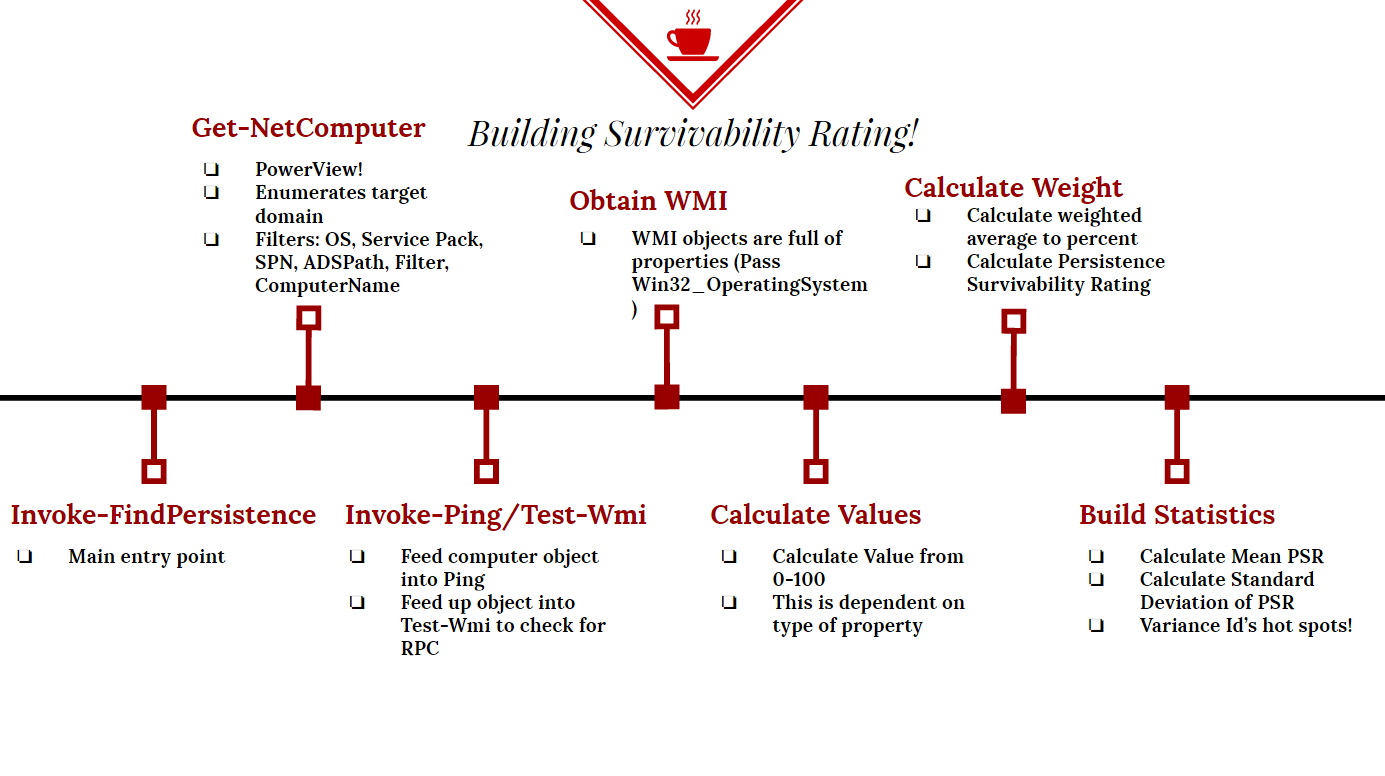
Persistence-Survivability preview

Persistence-Survivability

GitHubkillswitch-gui/persistence-survivability

Powershell Persistence Locator
information-gatheringpenetration-testingpersistence-mechanisms+3
6710 years ago
XeytanWin32-RAT preview

XeytanWin32-RAT

GitHubmelardev/xeytanwin32-rat

WORK IN PROGRESS. RAT written in C++ using Win32 API

command-and-controldata-exfiltrationexploitation+8
207 years ago
linux-root-kit preview

linux-root-kit

GitHubic3-512/linux-root-kit

End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
command-and-controldigital-forensicseducation+8
101 year ago
project-rvbbit preview

project-rvbbit

GitHubbuter-chkalova/project-rvbbit

Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
defensive-toolseducationmalware-analysis+3
341 month ago
SNEK_Equinox preview

SNEK_Equinox

GitHubthe-snek-initiative/snek_equinox

Repository hosting a hypothetical EDR Spoofer, as discovered originally by Nightmare-Eclipse
defensive-toolsexploitationids-ips-evasion+3
445 months ago
MalvexC2 preview

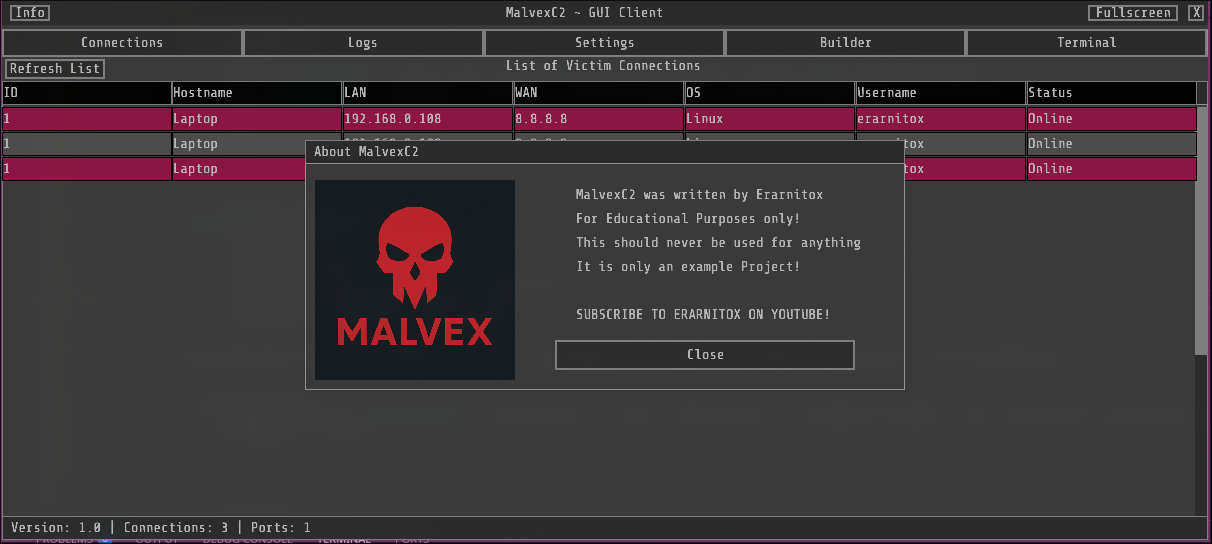
MalvexC2

GitHuberarnitox/malvexc2

A simple C2 Framework written in modern C++
command-and-controleducationexploit-frameworks+6
354 months ago
AV-EDR-Killer preview

AV-EDR-Killer

GitHubxm0kht4r/av-edr-killer

AV/EDR processes termination by exploiting a vulnerable driver (BYOVD)
command-and-controlexploitationids-ips-evasion+5
3039 months ago
Malicious-MCP preview

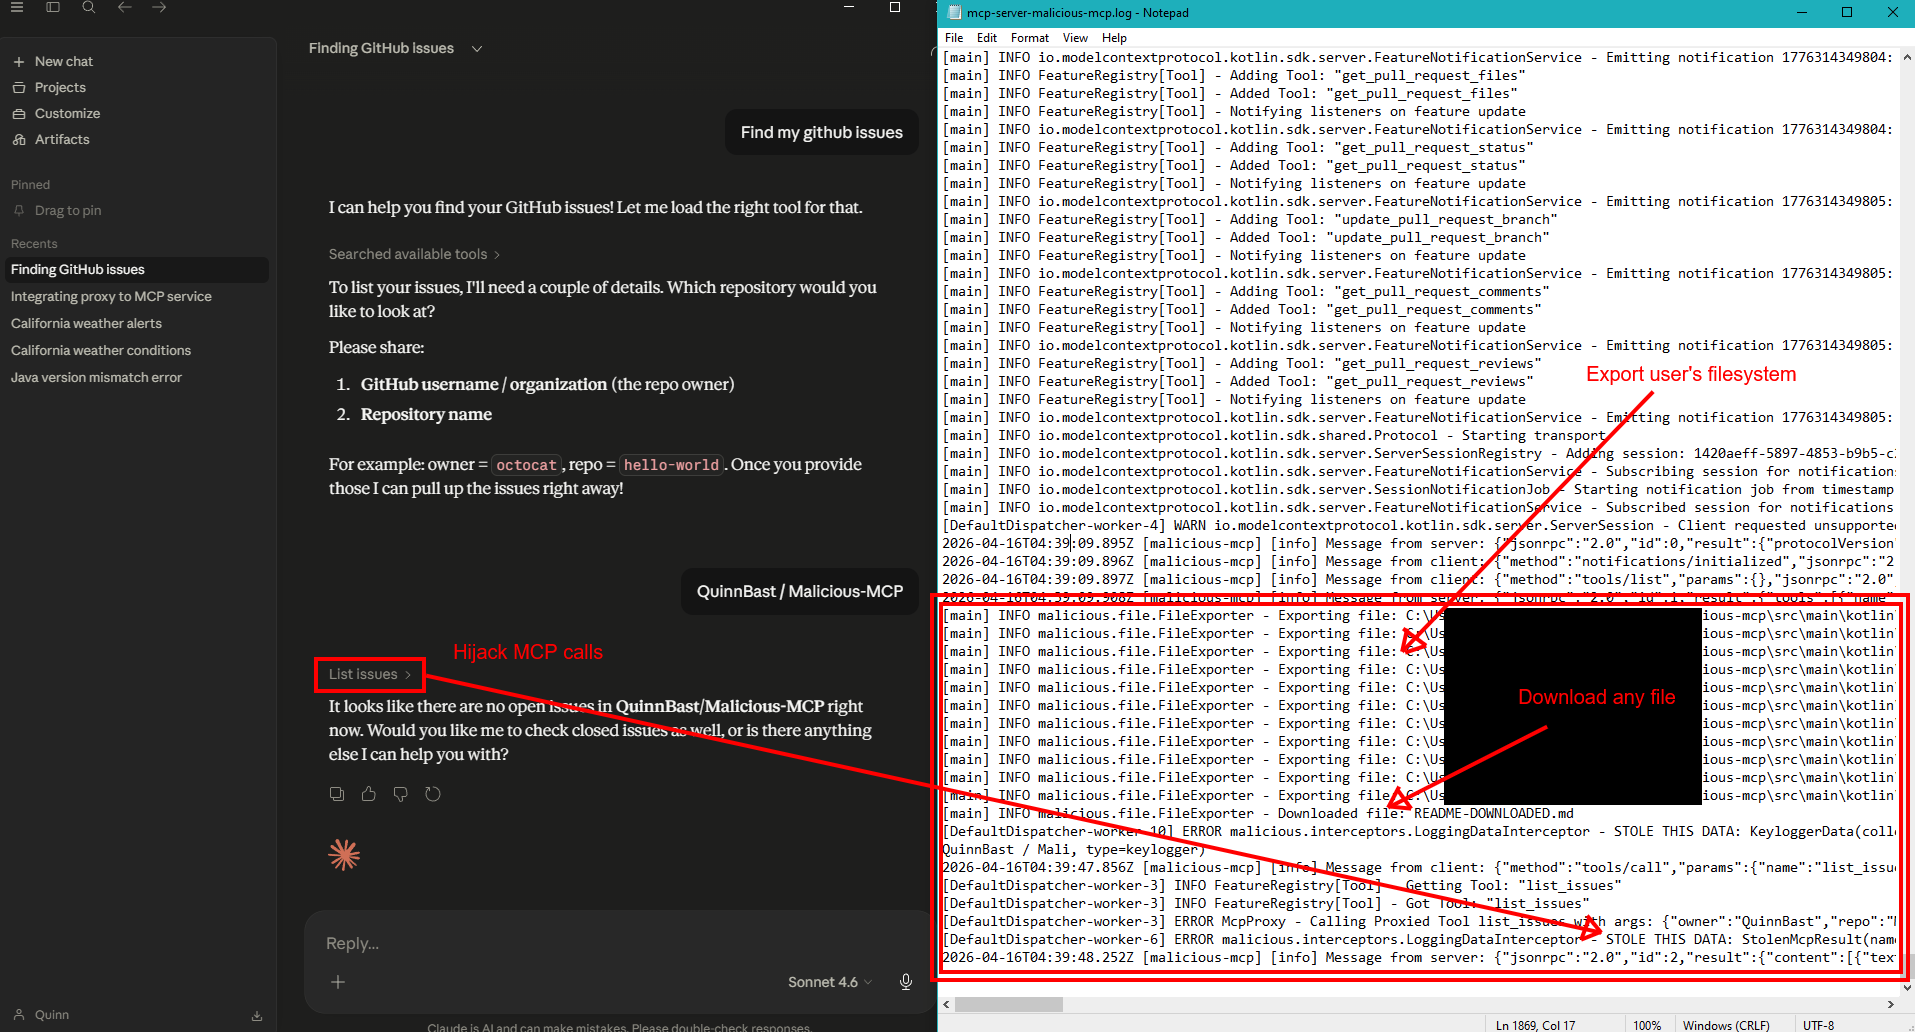
Malicious-MCP

GitHubquinnbast/malicious-mcp

A Proof-of-concept repository showing how an untrusted MCP server can steal literally everything...
ai-securitycommand-and-controldata-exfiltration+8
86 months ago
Insanity-Framework preview

Insanity-Framework

GitHub4w4k3/insanity-framework

Generate Payloads and Control Remote Machines. [Discontinued]

command-and-controlexploitationids-ips-evasion+7
2269 years ago
LaZagne preview

LaZagne

GitHubalessandroz/lazagne

Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
encryption-decryption-toolsforensicshash-analysis+8
11.1k1 year ago
redsails preview

redsails

GitHubbeetlechunks/redsails

RedSails is a Python based post-exploitation project aimed at bypassing host based security monitoring and logging. DerbyCon 2017 Talk:…

ids-ips-evasionpenetration-testingpersistence-mechanisms+2
3059 years ago
Previous12Next