

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
262 results
ConfluenceC2 preview

ConfluenceC2

GitHubdagowda/confluencec2

This is a project aimed to make every other Saas product a C2, confluence is just the beginning.
command-and-controldata-exfiltrationlateral-movement+9
13
6 days ago
3snake preview

3snake

GitHubblendin/3snake

Tool for extracting information from newly spawned processes

data-exfiltrationmemory-forensicspassword-attacks+4
7911 year ago
aws-pentest preview

aws-pentest

GitHubcapture0x/aws-pentest

Automated AWS security assessment CLI with 30 modules covering IAM privilege escalation, S3 exposure, compute, network, logging and misconfiguration…

cloud-infrastructure-securitycloud-securityconfiguration-auditing+9
365 months ago
TornadoC2 preview

TornadoC2

GitHubkamalx06/tornadoc2

Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…

command-and-controlcryptographyids-ips-evasion+9
3410 days ago
AdStrike preview

AdStrike

GitHubcapture0x/adstrike

AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
ai-securitycommand-and-controlexploitation+7
3889 days ago
InjectSetConsole preview

InjectSetConsole

GitHubtwosevenonet/injectsetconsole

Proof of Concept for Process Code Injection Without Using WriteProcessMemory

command-and-controlexploitationids-ips-evasion+7
1591 month ago
Overthrone preview

Overthrone

GitHubkarmanya03/overthrone

All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
command-and-controlexploit-frameworksinformation-gathering+8
314 days ago
glimmer preview

glimmer

GitHublinnemanlabs/glimmer

Adversary emulation and C2 framework for security research
command-and-controlcryptographydata-exfiltration+8
55 months ago
veneficus-implant-public preview

veneficus-implant-public

GitHubabraxas/veneficus-implant-public

Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…
command-and-controldata-exfiltrationexploitation+9
1 month ago
veneficus preview

veneficus

GitHubabraxas/veneficus

Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.

command-and-controldata-exfiltrationids-ips-evasion+8
21 month ago
lockjaw preview

lockjaw

GitHubg13net/lockjaw

Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
command-and-controldns-analysisexploit-frameworks+9
3327 days ago
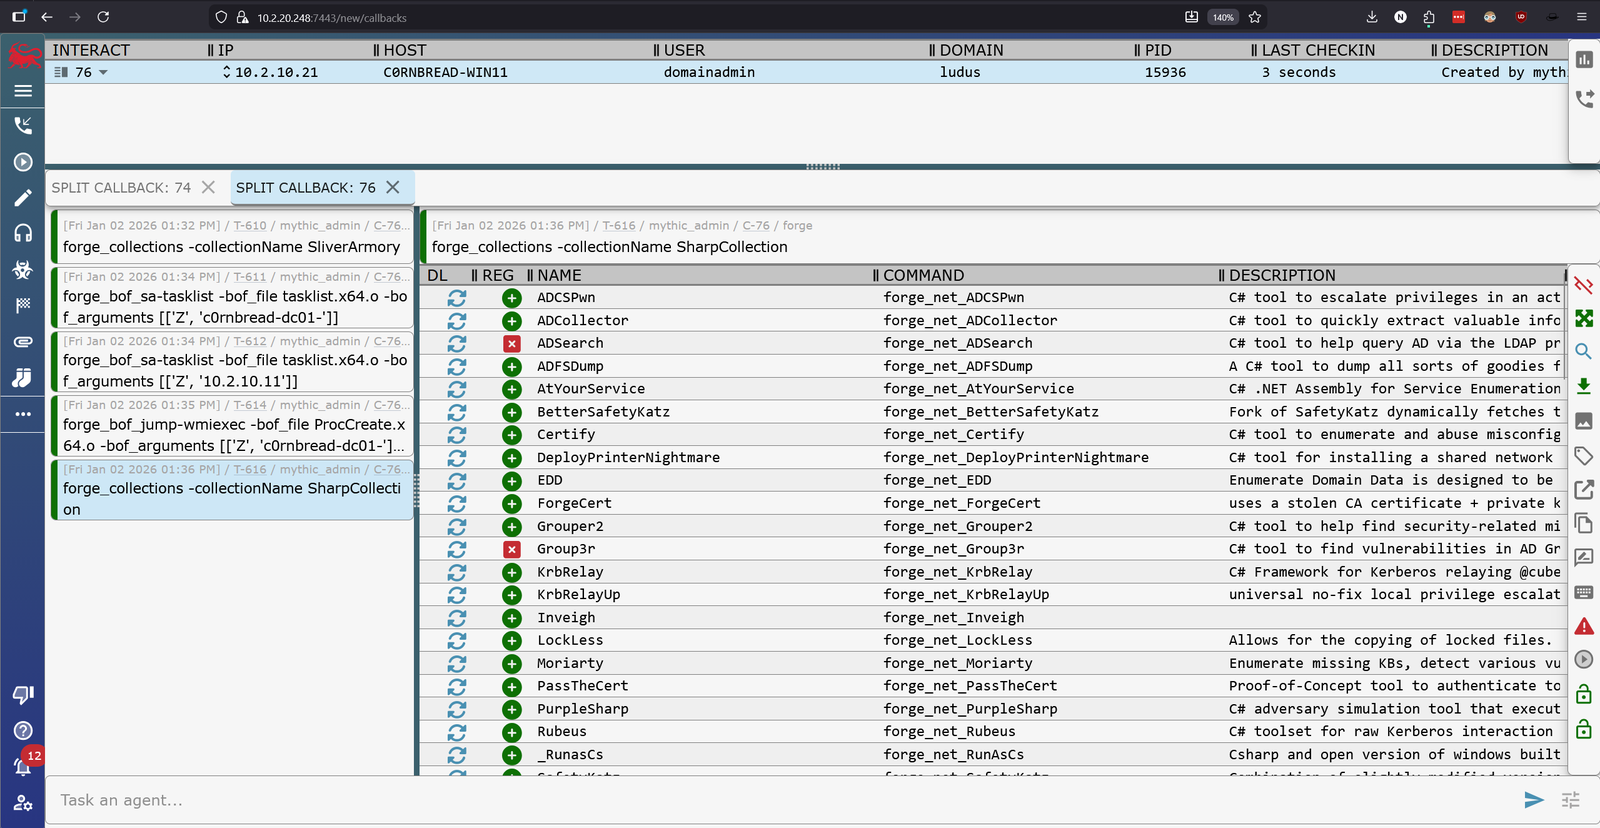
Xenon preview

Xenon

GitHubmythicagents/xenon

A Mythic agent for Windows written in C
command-and-controldata-exfiltrationdefensive-tools+9
1872 months ago
FUD-C2-Framework preview

FUD-C2-Framework

GitHubx3r0day/fud-c2-framework

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.

command-and-controlencryption-decryption-toolsids-ips-evasion+9
75 months ago
Koi preview

Koi

GitHubb3rt1ng/koi

Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
command-and-controlids-ips-evasionlateral-movement+9
377 days ago
ICALL-GADGET preview

ICALL-GADGET

GitHubgmh5225/icall-gadget

Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking

binary-exploitationexploitationids-ips-evasion+5
12 years ago
CVE-2026-65660-Poc preview

CVE-2026-65660-Poc

GitHubshadowforge-cyber/cve-2026-65660-poc

Malicious Register Directive Code Injection Exploit
command-and-controldata-exfiltrationexploitation+8
11 month ago
Kestra-cve-2026-53576 preview

Kestra-cve-2026-53576

GitHubatlasvector/kestra-cve-2026-53576

End-to-end reproduction and cross-layer detection of CVE-2026-53576, the unauthenticated RCE in Kestra - taken past the base PoC to show how a common…

container-securityexploitationincident-response+8
1 month ago
RC4Decryption preview

RC4Decryption

GitHubweedhashpeddler/rc4decryption

Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…

binary-analysiscryptographydefensive-tools+6
371 month ago
Previous12…15Next