
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
15 results
PPLRunner preview

PPLRunner

GitHubpathtofile/pplrunner

Builds an ELAM driver and service that launches a signed child process as an Anti-Malware Protected Process-Light (PPL) on Windows, for security…
defensive-toolsexploitationmalware-analysis+4
185
4 years ago
TLPE preview

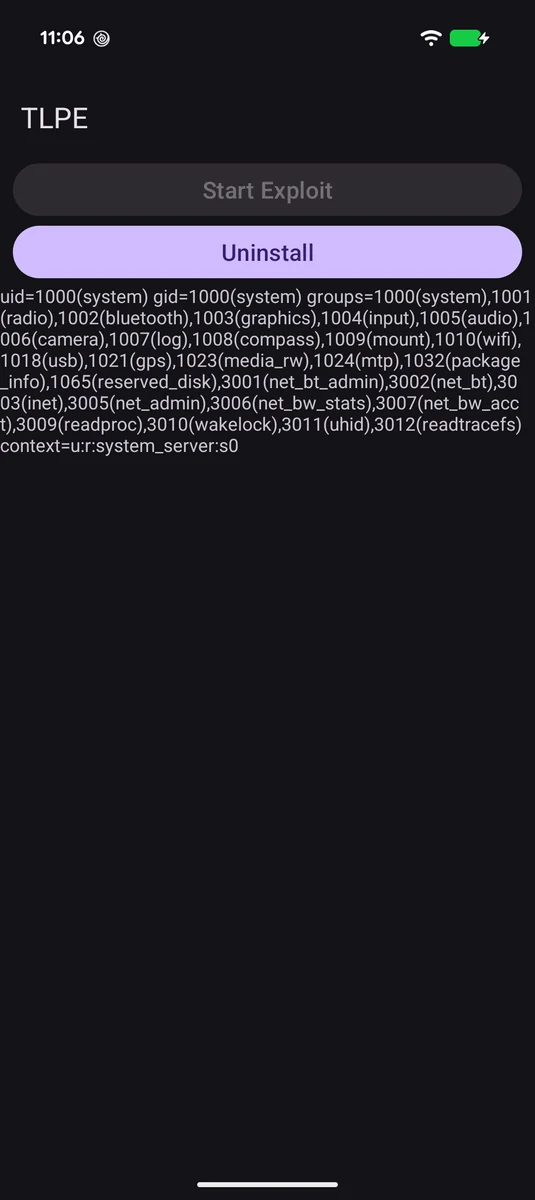
TLPE

GitHubsupersonic/tlpe

CVE-2026-49881, using insecure context creation in Android 17's Telecom service to execute arbitrary code as UID 1000 system_server from an…
android-securitybinary-exploitationexploitation+4
1081 month ago
CdpSvcLPE preview

CdpSvcLPE

GitHubsailay1996/cdpsvclpe

Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
exploitationpayload-developmentpenetration-testing+3
2564 years ago
NoFaxGiven preview

NoFaxGiven

GitHubhackerhouse-opensource/nofaxgiven

Code Execution & Persistence in NETWORK SERVICE FAX Service

exploitationpayload-developmentpersistence-mechanisms+3
379 months ago
poisontap preview

poisontap

GitHubsamyk/poisontap

Exploits locked/password protected computers over USB, drops persistent WebSocket-based backdoor, exposes internal router, and siphons cookies using…
authenticationcommand-and-controldata-exfiltration+7
6.5k7 years ago
CcmMessagingBackdoor preview

CcmMessagingBackdoor

GitHubsynacktiv/ccmmessagingbackdoor

Proof-of-concept backdoor for SCCM Management Point using rogue COM service for persistent remote command execution as SYSTEM.
command-and-controlpayload-developmentpersistence-mechanisms+3
191 year ago
shadow-workers preview

shadow-workers

GitHubshadow-workers/shadow-workers

Shadow Workers is a free and open source C2 and proxy designed for penetration testers to help in the exploitation of XSS and malicious Service…

command-and-controlpenetration-testingpersistence-mechanisms+2
2453 years ago
DriverJack preview

DriverJack

GitHubklezvirus/driverjack

Hijacking valid driver services to load arbitrary (signed) drivers abusing native symbolic links and NT paths

exploitationids-ips-evasionlateral-movement+5
3672 years ago
CVE-2024-31771 preview

CVE-2024-31771

GitHubrestdone/cve-2024-31771

Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…
binary-exploitationexploitationlateral-movement+4
2 years ago
EDRChoker preview

EDRChoker

GitHubtwosevenonet/edrchoker

A tool uses the QoS Policy (Pacer.sys) to throttle Endpoint Detection and Response (EDR) agents from connecting to the server.
defensive-toolsids-ips-evasionpersistence-mechanisms+3
3034 months ago
AirBorne-PoC preview

AirBorne-PoC

GitHubekomssavior/airborne-poc

poc for CVE-2025-24252 & CVE-2025-24132
binary-exploitationcommand-and-controlexploitation+6
16410 months ago
Awesome-RedTeam-Cheatsheet preview

Awesome-RedTeam-Cheatsheet

GitHubristbs/awesome-redteam-cheatsheet

Red Team Cheatsheet in constant expansion.
curated-resourceseducationlateral-movement+4
1.3k3 years ago
SharpEventPersist preview

SharpEventPersist

GitHubimprosec/sharpeventpersist

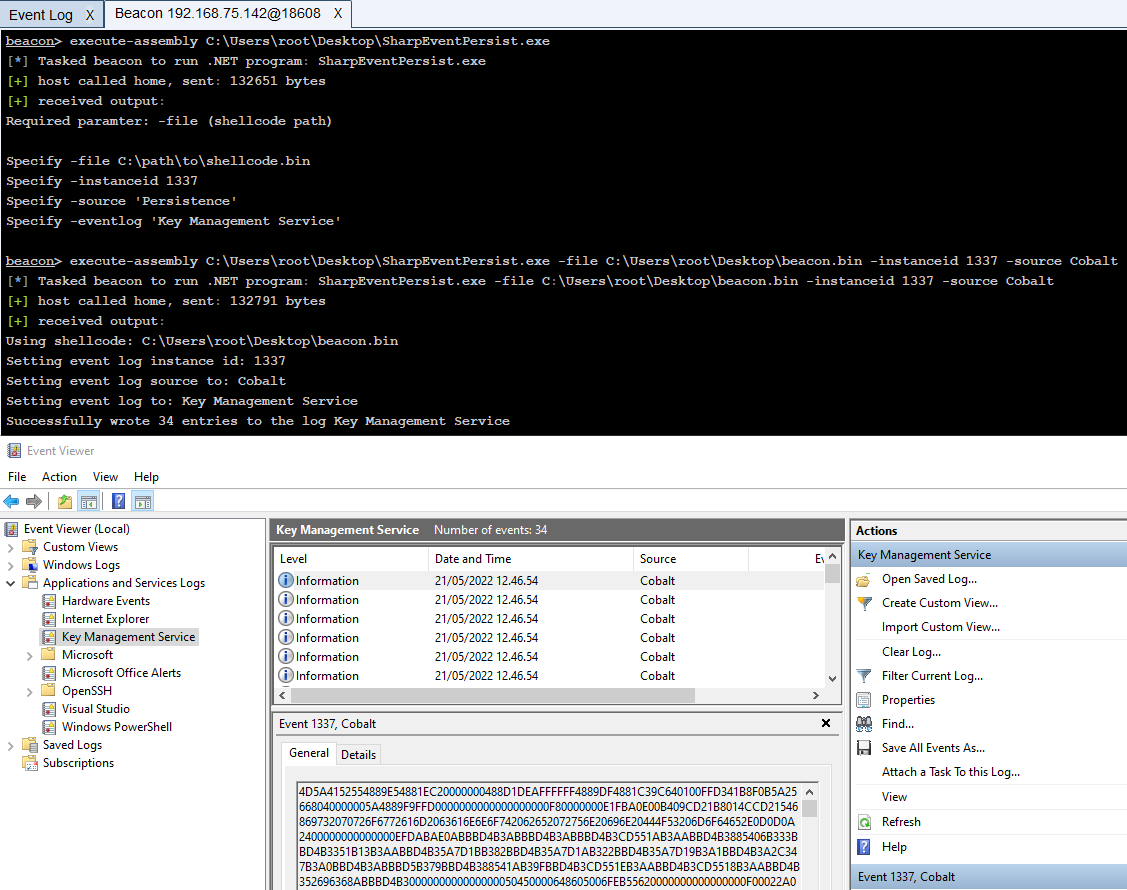
Persistence by writing/reading shellcode from Event Log
payload-generationpersistence-mechanismspost-exploitation+1
3764 years ago
BrainDamage preview
Archived

BrainDamage

GitHubmehulj94/braindamage

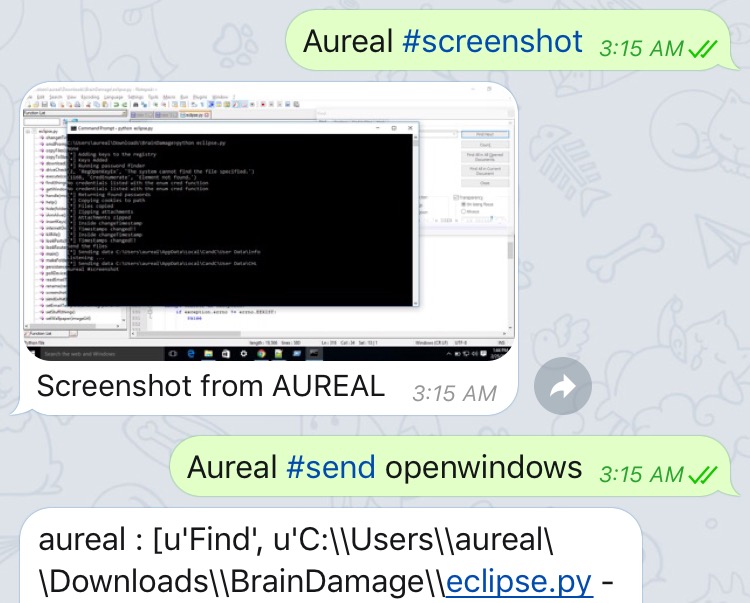
Remote administration service which uses twitter as a command and control server
command-and-controldata-exfiltrationinformation-gathering+5
7145 years ago
illusion-rs preview
Archived

illusion-rs

GitHubmemn0ps/illusion-rs

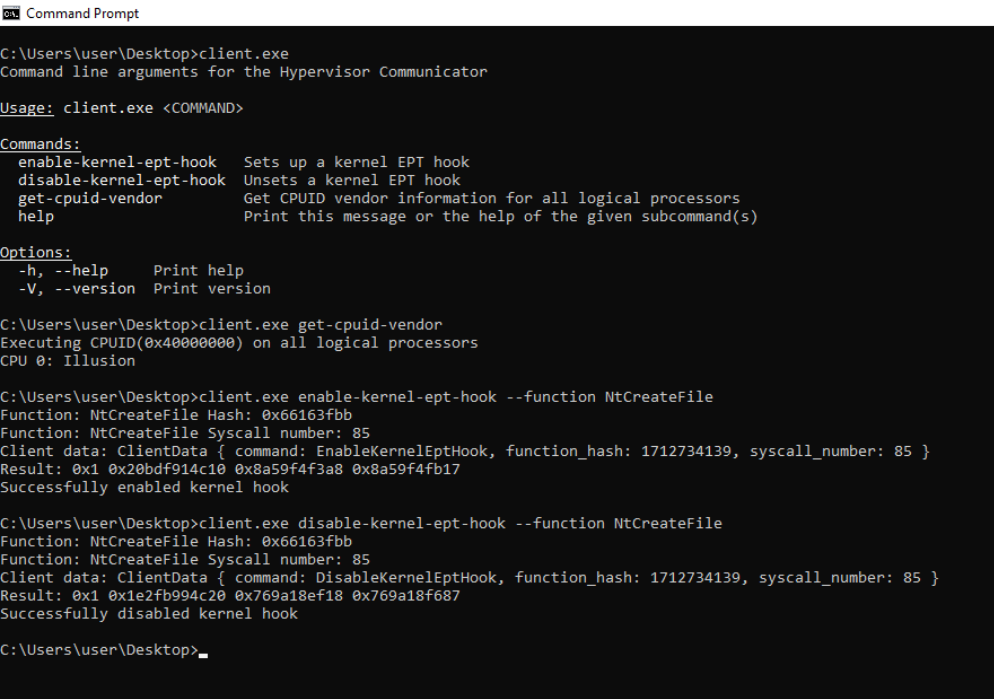
Rusty Hypervisor - Windows UEFI Blue Pill Type-1 Hypervisor in Rust (Codename: Illusion)

binary-analysisdefensive-toolshardware-security+7
4145 months ago