
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
25 results
BEAR-C2 preview

BEAR-C2

GitHubs3n4t0r-0x0/bear-c2

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
679
3 days ago
CVE-2026-65643-PoC-Toolkit preview

CVE-2026-65643-PoC-Toolkit

GitHubtc4dy/cve-2026-65643-poc-toolkit

Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
command-and-controlexploitationpayload-development+7
1220 days ago
Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis preview

Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis

GitHubkaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis

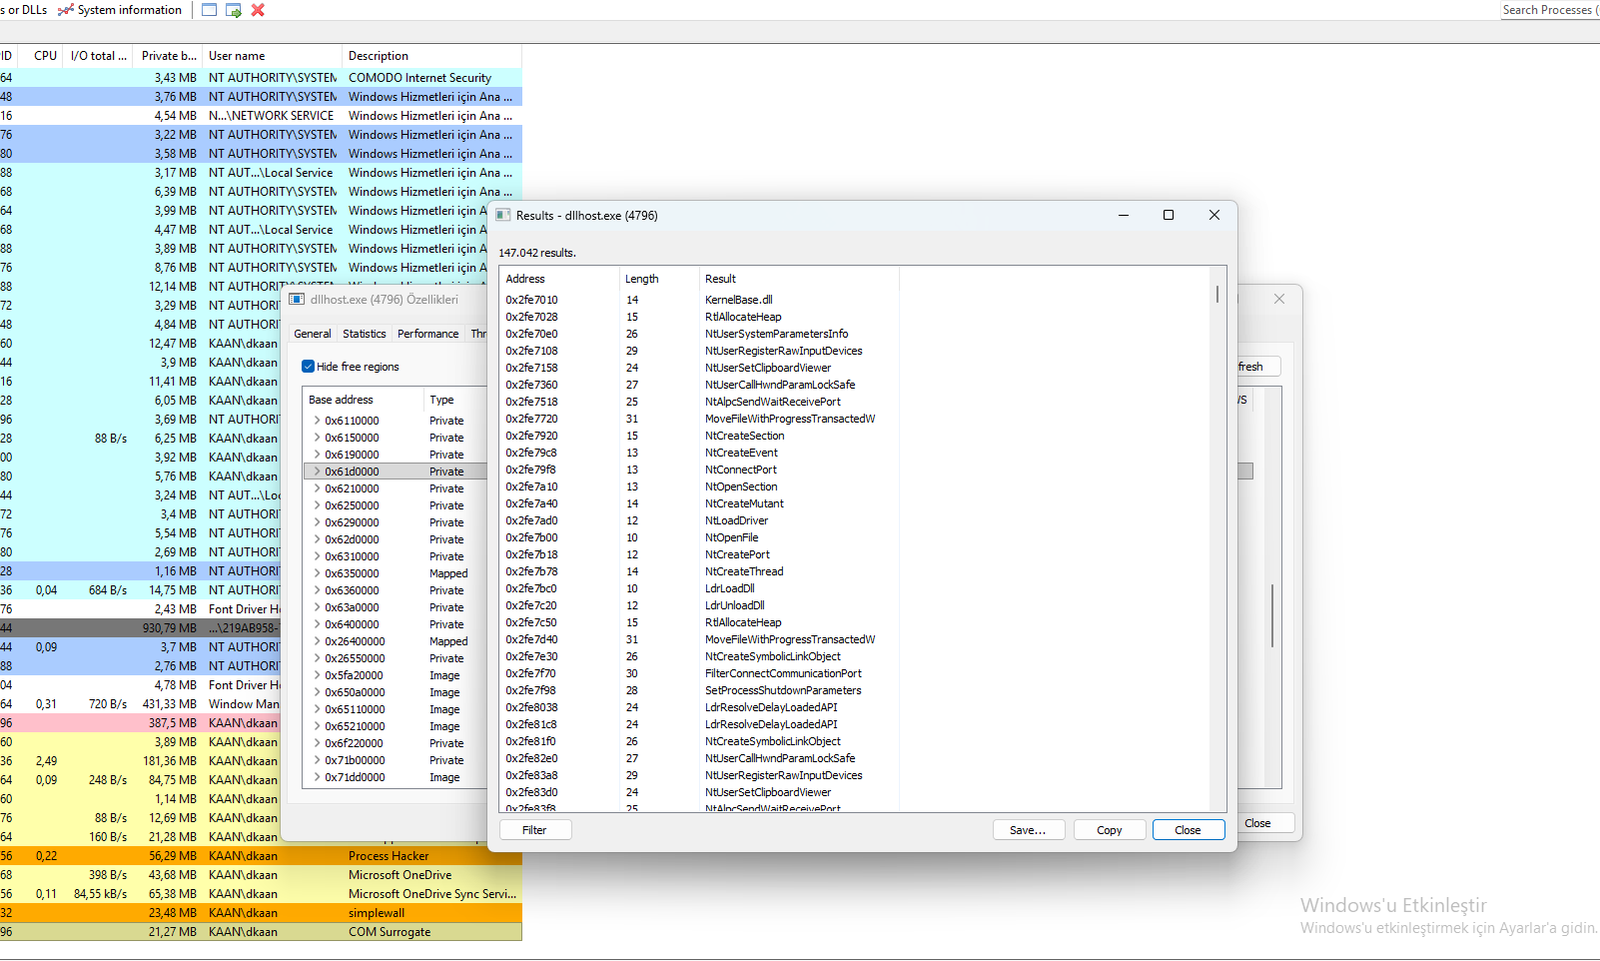
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

binary-analysiscommand-and-controldata-exfiltration+4
1023 days ago
stratum-c2 preview

stratum-c2

GitHublame-projects/stratum-c2

Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
cloud-securitycommand-and-controlencryption-decryption-tools+6
4215 days ago
Windows-Defender-Security-Auditor-CVE-2026-50656- preview

Windows-Defender-Security-Auditor-CVE-2026-50656-

GitHubeh-amish/windows-defender-security-auditor-cve-2026-50656-

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
configuration-auditingdefensive-toolsincident-response+8
1 month ago
RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis preview

RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis

GitHubkaandemir993/redline-stealer-c2-defender-bypass-payload-analysis

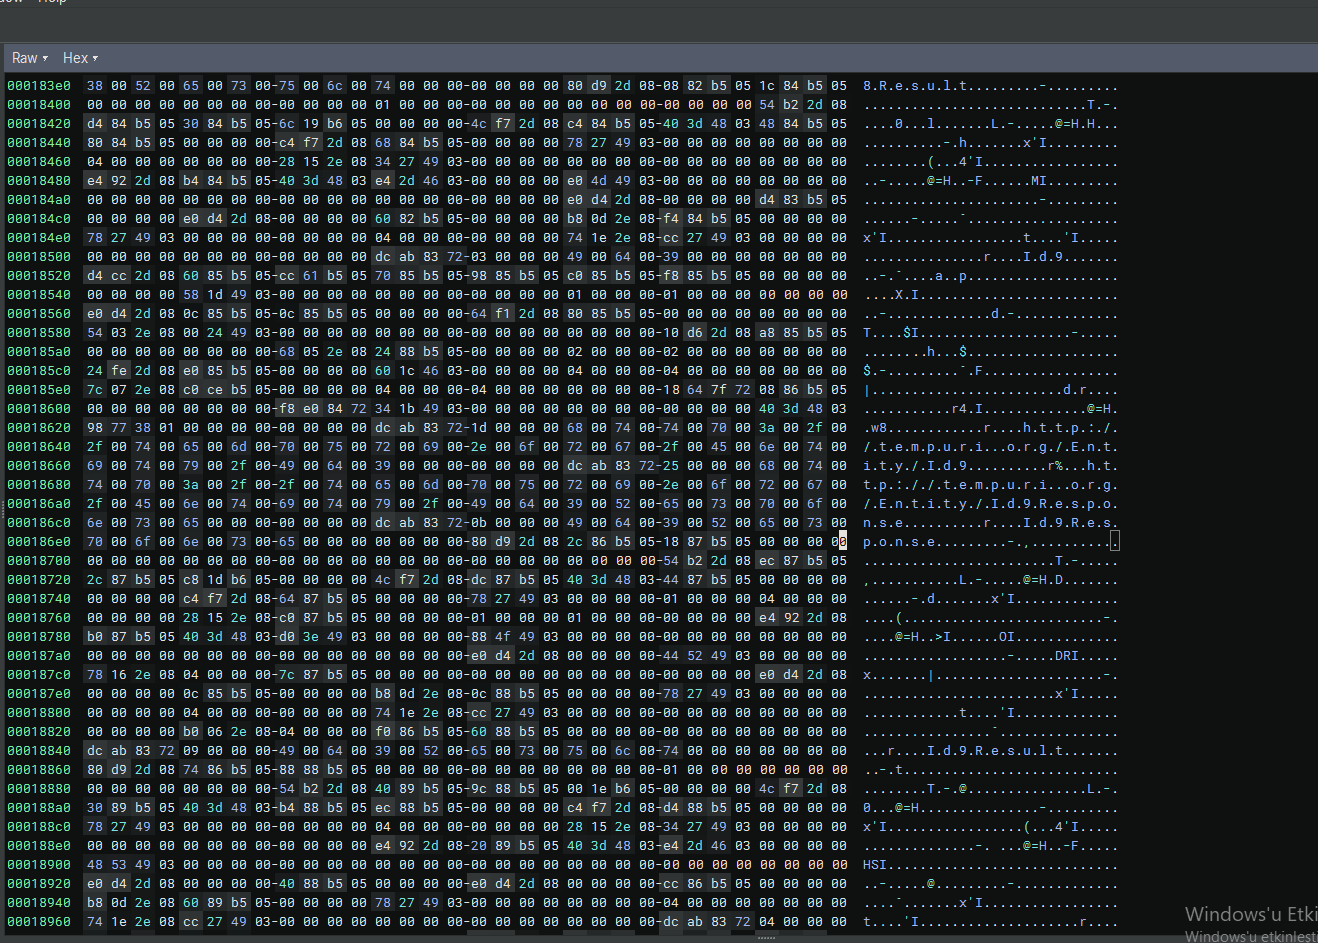
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
command-and-controldata-exfiltrationmalware-analysis+4
11 month ago
BOF_Collection preview

BOF_Collection

GitHubrvrsh3ll/bof_collection

Various Cobalt Strike BOFs
command-and-controlinformation-gatheringpersistence-mechanisms+4
7863 years ago
badsuccessor preview

badsuccessor

GitHubcybrly/badsuccessor

Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…

adversarial-attackexploitationinformation-gathering+7
1211 year ago
Active-Directory-Exploitation-Cheat-Sheet preview

Active-Directory-Exploitation-Cheat-Sheet

GitHubintegration-it/active-directory-exploitation-cheat-sheet

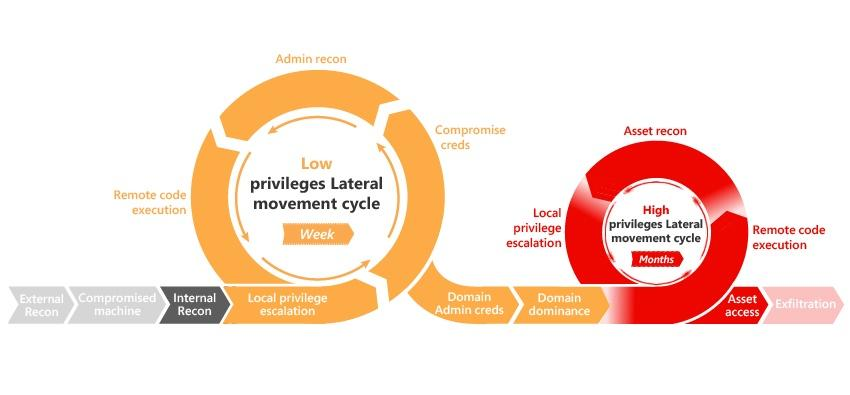
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
curated-resourcesdata-exfiltrationeducation+6
2.8k5 years ago
Shadow-Vault preview

Shadow-Vault

GitHubjenderal92/shadow-vault

Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.
authentication-authorizationemail-securityidentity-access-management+3
3 months ago
AD-Attack-Defense preview

AD-Attack-Defense

GitHubinfosecn1nja/ad-attack-defense

Attack and defend active directory using modern post exploitation adversary tradecraft activity

curated-resourcesdefensive-toolseducation+7
4.9k1 year ago
LSTAR-EN preview

LSTAR-EN

GitHubmoscowchill/lstar-en

LSTAR - CobaltStrike Translated to EN
command-and-controlexploitationids-ips-evasion+9
233 years ago
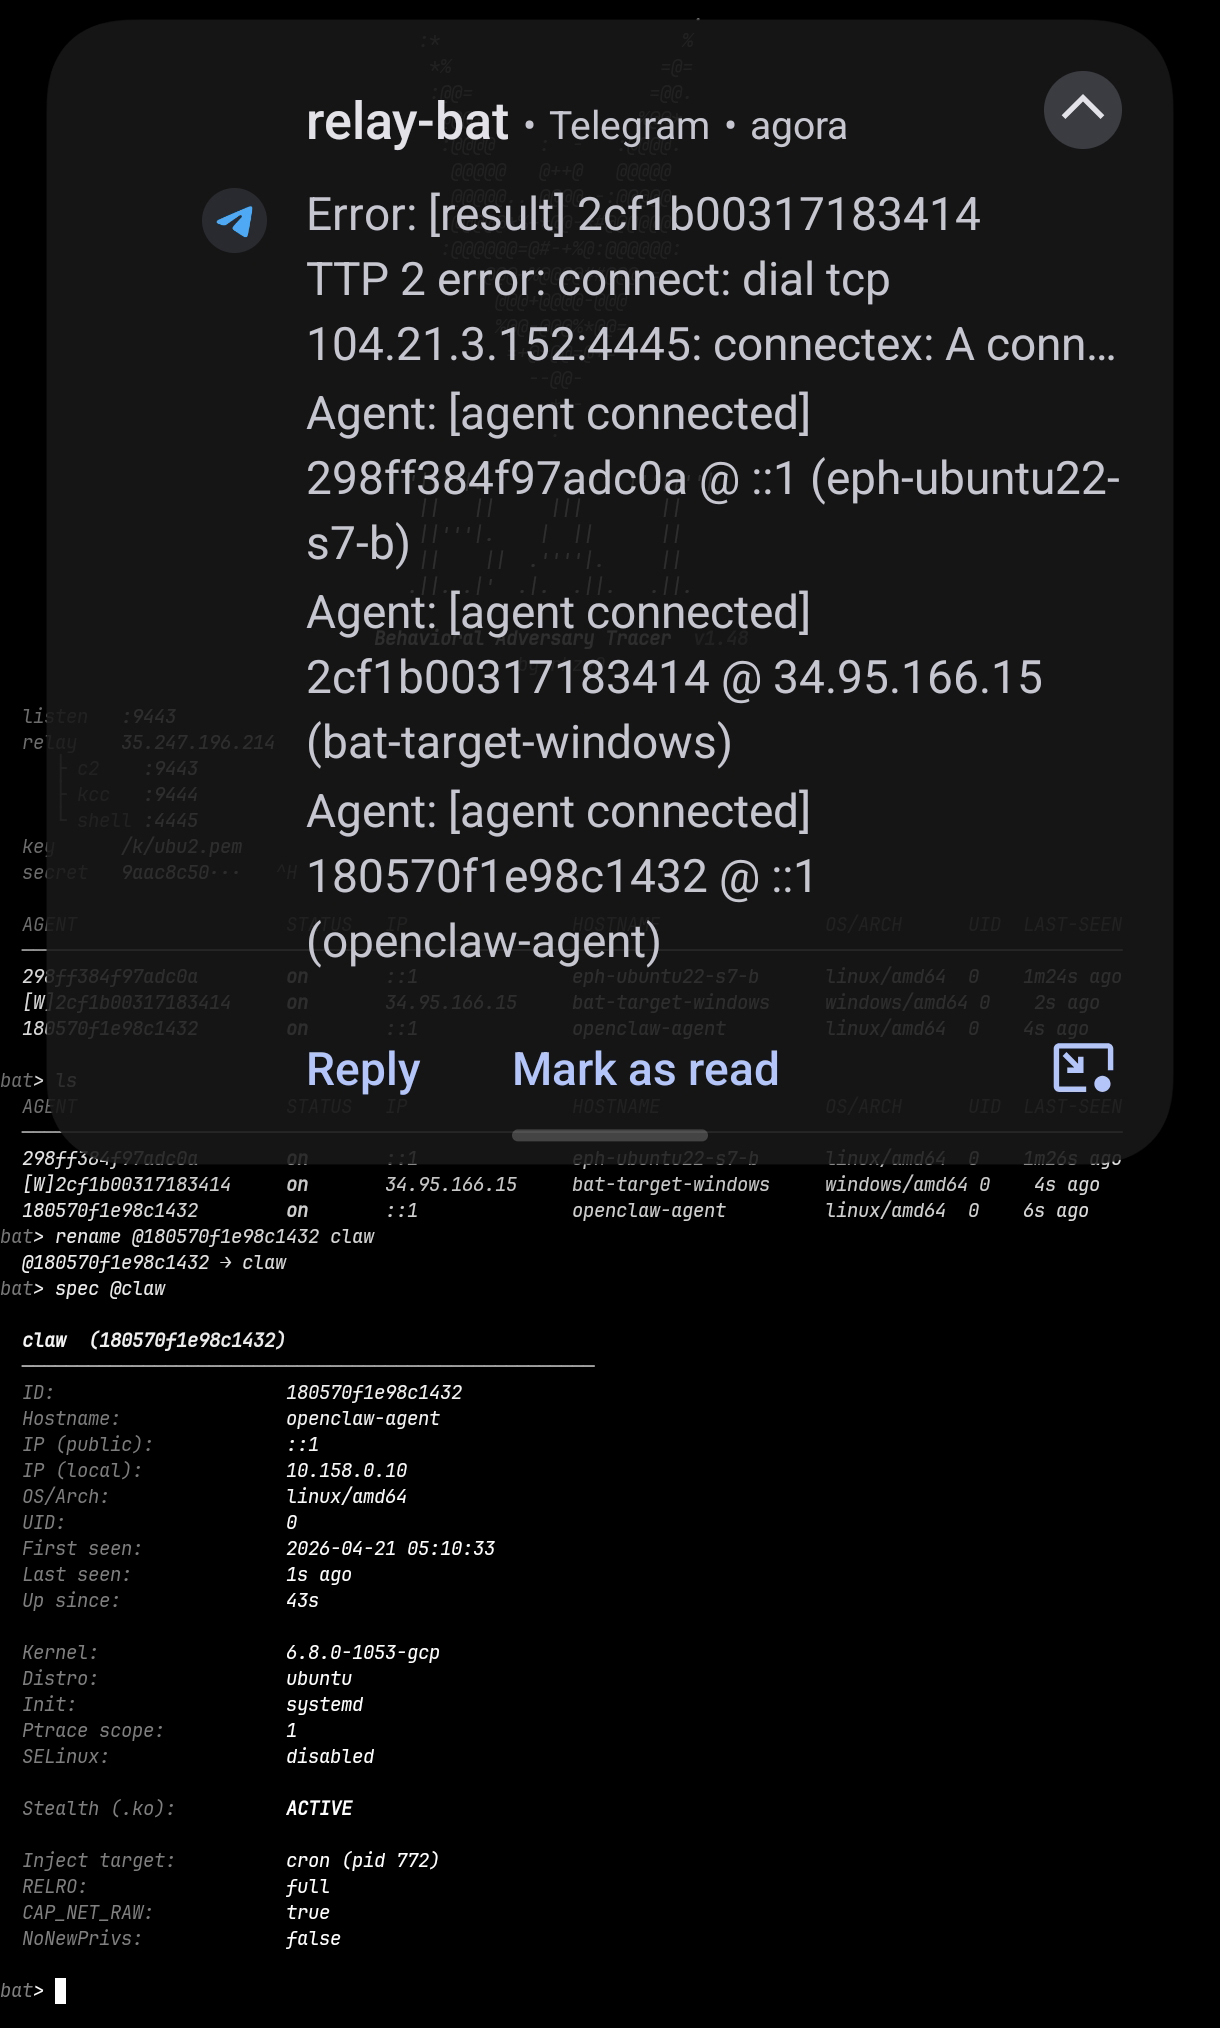
bat preview

bat

GitHubrhzv0/bat

Full-spectrum Linux adversary simulation platform with kernel-level stealth, C2 beaconing, privilege escalation, credential harvesting, lateral…

command-and-controldata-exfiltrationlateral-movement+5
364 months ago
wasmforge preview

wasmforge

GitHubpraetorian-inc/wasmforge

WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.

binary-analysiscommand-and-controlexploit-frameworks+9
1313 months ago
mimikatz-missing-manual preview

mimikatz-missing-manual

GitHubdarkoperator/mimikatz-missing-manual

Comprehensive self-paced manual on Windows identity, Kerberos, and PKI internals, covering credential dumping, ticket forgery, domain persistence,…
authenticationcryptographyeducation+6
4657 months ago
JS-Tap preview

JS-Tap

GitHubhoodoer/js-tap

JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…

command-and-controldata-exfiltrationinformation-gathering+8
4772 months ago
DLLPasswordFilterImplant preview

DLLPasswordFilterImplant

GitHubgosecure/dllpasswordfilterimplant

DLL Password Filter Implant with Exfiltration Capabilities
data-exfiltrationpenetration-testingpersistence-mechanisms+2
1366 years ago
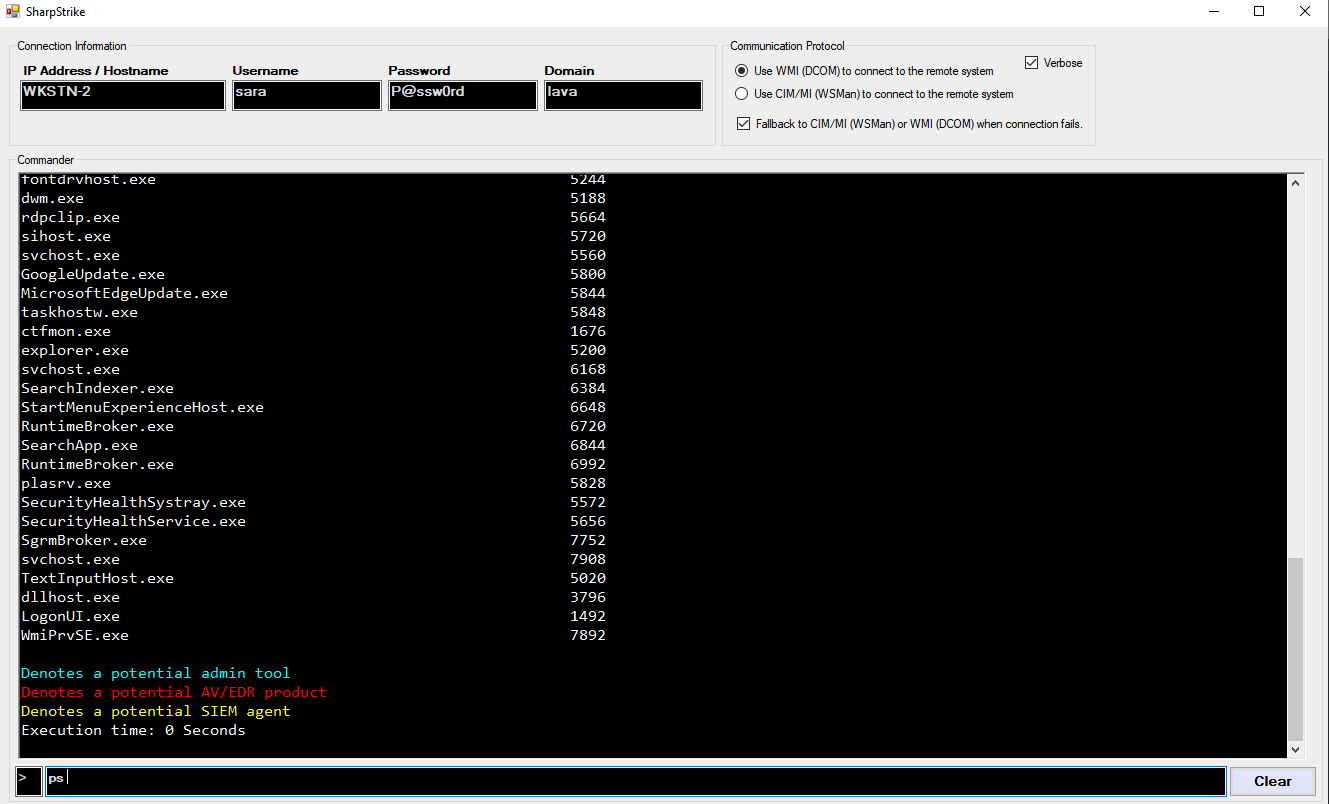
SharpStrike preview

SharpStrike

GitHubiomoath/sharpstrike

A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.

command-and-controldata-exfiltrationinformation-gathering+6
1985 years ago
Previous12Next