
SharpMemshell
 a-d-team/sharpmemshell
.NET in-memory webshell (memshell) payloads implemented via HttpListener and VirtualPath, compatible with the Godzilla 4.01 post-exploitation…
command-and-controldefensive-toolspayload-development+5
300
a-d-team/sharpmemshell.NET in-memory webshell (memshell) payloads implemented via HttpListener and VirtualPath, compatible with the Godzilla 4.01 post-exploitation…
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 linnemanlabs/glimmer
Adversary emulation and C2 framework for security research
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
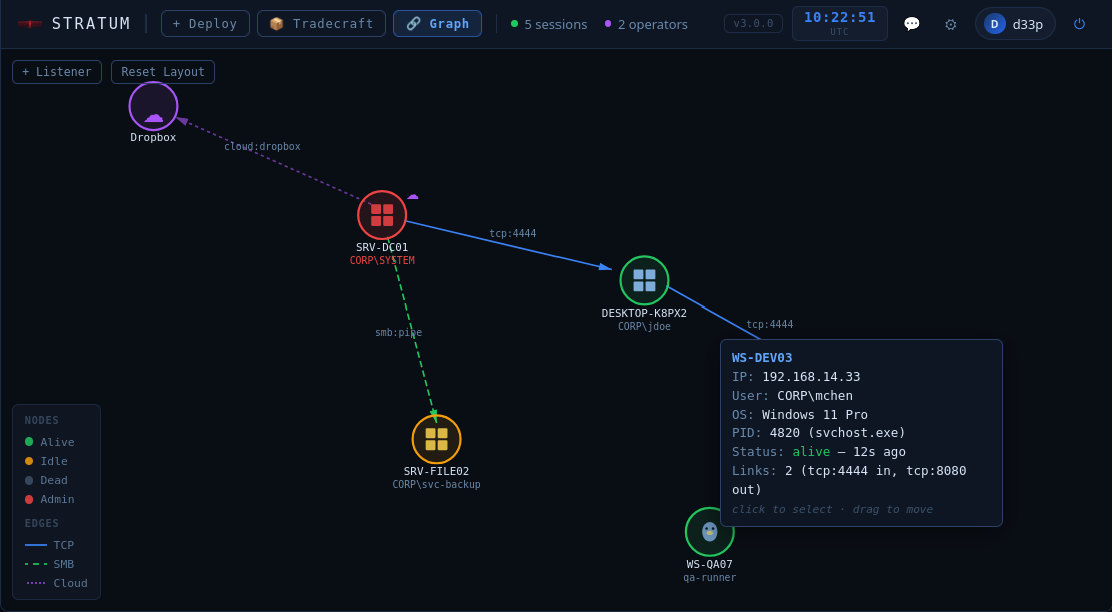 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 epsilonpoint88-glitch/epsilonpoint-
Modular exploit framework targeting CVE-2026-23550 in WordPress, featuring mass exploitation, obfuscation, post-exploitation, and Docker-based C2…
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 zerodaylab/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 b23r0/heroinn
A cross platform C2/post-exploitation framework.